❌

Reading view

Man Covers Car in Special Wrap That Breaks Flock Cameras’ Electronic Brains

In light of plummeting public support for its widespread automatic license plate readers, surveillance company Flock has lost dozens of contracts with cities across the US.

The company even drew up plans to use the dashcams installed in Uber and Lyft drivers’ cars to spy on other vehicles, as 404 Media reported this week.

Citizens are increasingly disgusted by the company’s presence on public streets, opting to hack down the cameras, blind them, or sabotage them in other creative ways.

“His project, which he calls noRecognition, allows people to escape the automatic detection and algorithmic surveillance used across the U.S. and beyond.” https://t.co/OIQNOt9B0a @TechCrunch

— Christina Ayiotis, Esq., CRM, CIPP/E, AIGP (@christinayiotis) August 10, 2026

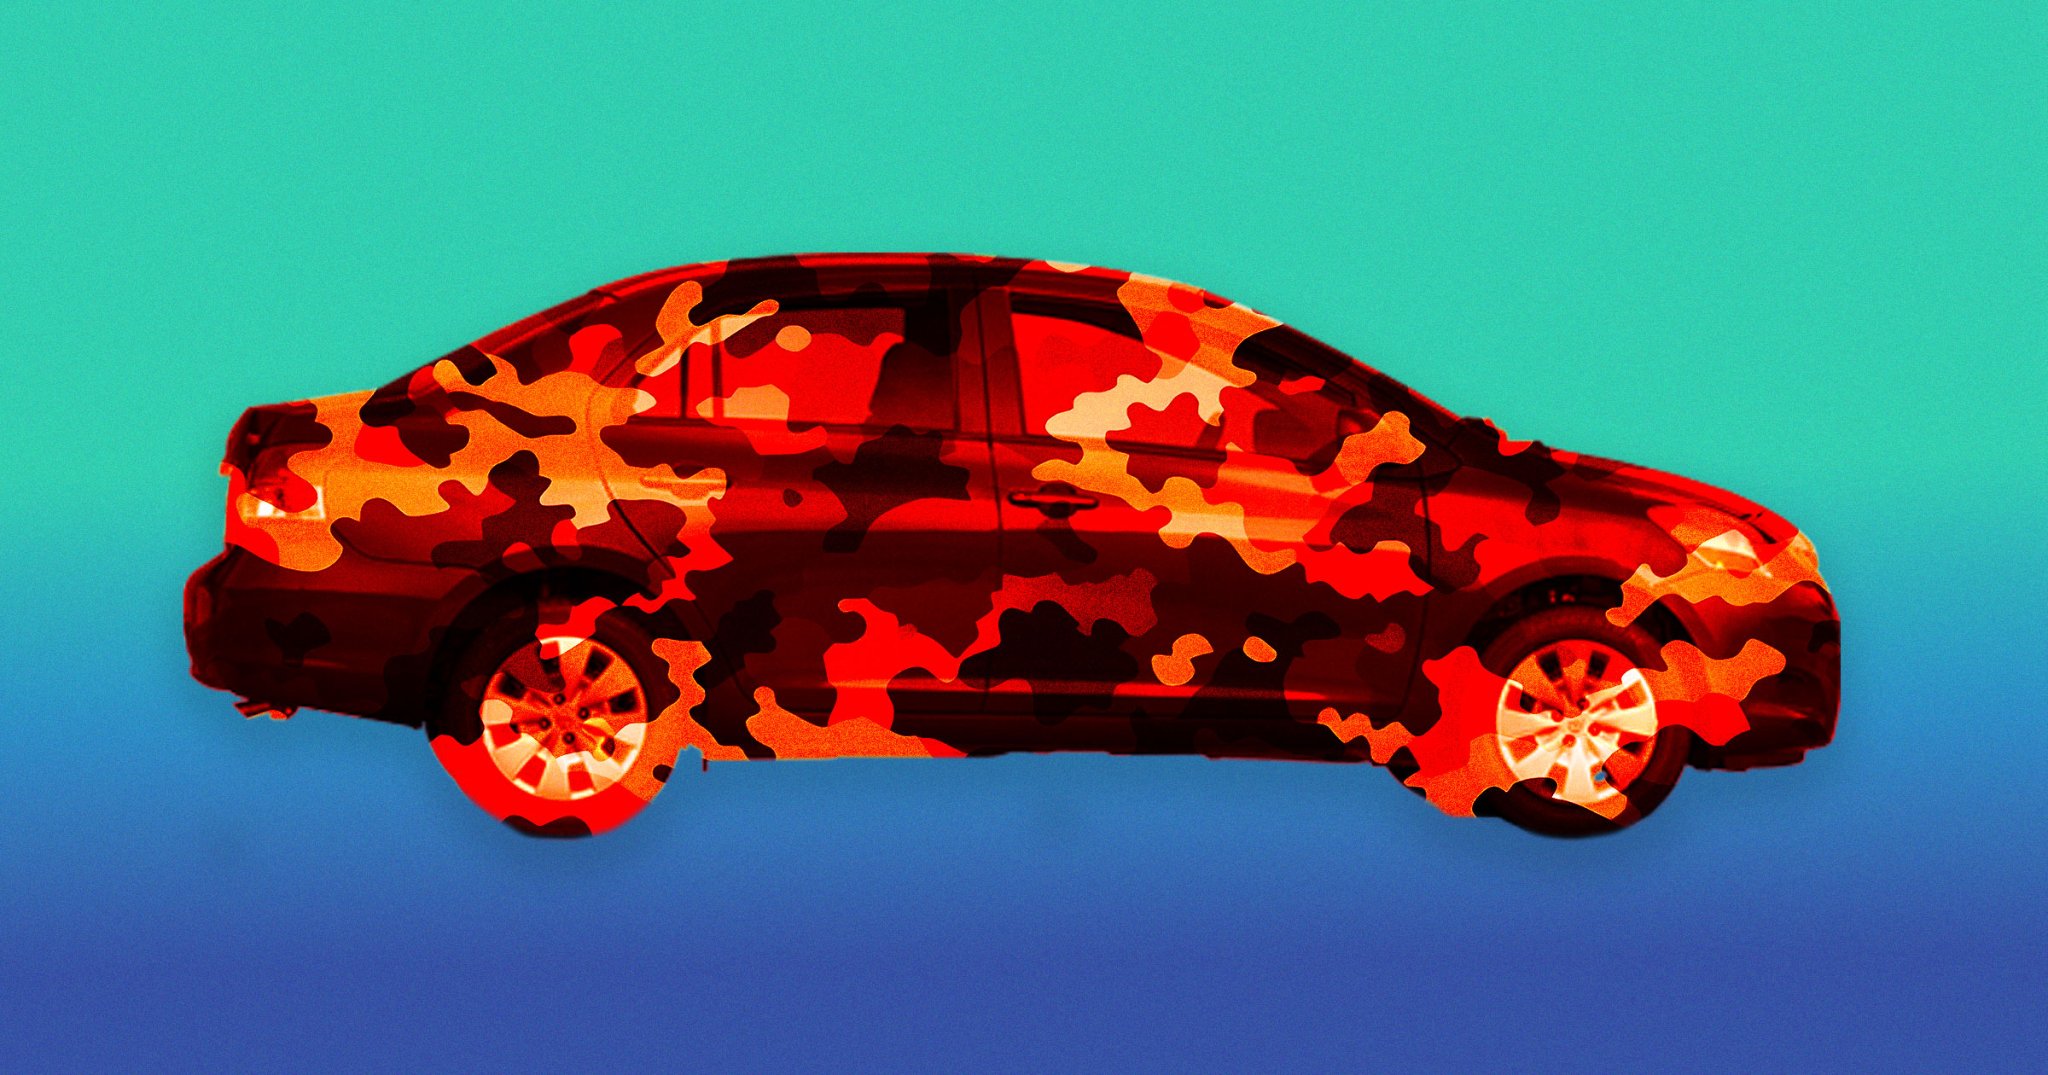
And according to cybersecurity researcher Bill Swearingen, there may be other creative ways to befuddle Flock’s spy cams. He devised with a special computer-generated pattern which, once stretched out across the vehicle in the form of a wrap, will result it in not being flagged as a car by Flock’s cameras.

During this year’s Def Con cybersecurity conference in Las Vegas, Swearingen showed off a 2009 Toyota Yaris wrapped in vinyl featuring the logo of automotive publication Donut Media (which is owned by Futurism‘s parent company Recurrent Ventures.)

Despite the car looking a bit chaotic — albeit still very much like a small passenger vehicle to the human eye — “we proved it was effective,” Swearingen told TechCrunch. The Yaris successfully defeated surveillance detection at Def Con during the pattern’s first public test.

“Privacy is a fundamental right,” he added, aiming to give people a way to “opt out of being tracked.”

To come up with the pattern, he used a reinforcement learning model that trained itself on patterns that evade detection. The model got to the point of being able to confuse all 11 open source detection algorithms he tested, per TechCrunch, in addition to Flock’s license plate readers and even Axon’s body-worn cameras used by police departments.

As part of his noRecognition crowdsourcing campaign, Swearingen has also come up with T-shirts and hoodies that feature algorithmic detection-busting patterns. He hopes to eventually put pattern-printed skins for entire cars on sale as well.

The effort is part of a much broader trend of companies offering up garments that incorporate “adversarial patterns,” which can exploit weaknesses in computer vision systems.

One thing is clear: as outrage over Flock’s heavy presence across the country grows, people are looking for any way to foil the tech — especially if it looks cool.

More on Flock: Flock’s Secret Surveillance Plan Will Make You Gasp

The post Man Covers Car in Special Wrap That Breaks Flock Cameras’ Electronic Brains appeared first on Futurism.
  •  

OpenAI extends 'Daybreak' security project and reveals new cyber model — but for approved users only

  • OpenAI expands Daybreak with Blue and Red tiers for defensive cyber work
  • New GPT‑5.6‑Cyber model offers high compliance for authorized vulnerability research
  • Access remains restricted due to dual‑use risks and reduced safeguard operation

OpenAI has announced two new tiers for its Daybreak dedicated cybersecurity project, each offering a different model with different levels of compliance. It also used the opportunity to introduce a new security-focused AI model, as well.

Hackers and criminals are increasingly abusing AI to improve and speed up the creation of phishing emails and malicious code, and with the introduction of AI agents, they’ve also used it to automate entire attack processes. The AI community responded by placing strong guardrails, making sure their models do not comply with requests to build malware, or hack other companies.

These guardrails ended up being a two-edged sword, because as they slowed down attackers, they also slowed down the defenders.

What is Daybreak?

To give the cybersecurity community the upper edge, companies like OpenAI started creating dedicated cybersecurity initiatives that provide a vetted list of companies state-of-the-art models, free of guardrails. The company also provided them with pre-trained AI agents, as well as access to a pool of shared knowledge.

Initially launched in June 2026, Daybreak originally included GPT.5-5-Cyber (a model optimized for security work), Codex Security (an agent that can analyze codebases, identify vulnerabilities, validate findings, and help develop patches), Patch the Planet (an initiative with Trail of Bits to find and fix vulnerabilities in open-source software), Daybreak Cyber Partner Program (lets approved cybersecurity companies such as Cloudflare or Cisco integrate OpenAI's cyber capabilities into their own products and services), and Trusted Access for Cyber (the governance/access system for organizations doing authorized cybersecurity work with these capabilities).

Now, OpenAI has expanded Daybreak with two access tiers, Daybreak Blue, and Daybreak Red.

The company says Daybreak Blue is “the recommended starting point for most defenders, supporting vulnerability discovery, secure code review, malware analysis, incident response, and patch validation. Companies opting for this tier can expect access to frontier general-purpose models, including GPT‑5.6 Sol, whose safeguards have been tailored to authorized defensive security work.

Daybreak Red, on the other hand, provides access to OpenAI’s “purpose-trained cybersecurity models for authorized vulnerability research, exploit validation, and security testing.” This tier offers the brand new GPT‑5.6‑Cyber, built on GPT‑5.6 Sol and trained to improve capabilities on several specialized cybersecurity tasks such as finding zero-day vulnerabilities and developing exploit chains.

This model is also more compliant and less likely to refuse certain higher-risk, dual-use cyber tasks.

Complying with "dangerous" requests

Request compliance is the name of the game here. OpenAI says the new model addresses feedback from security researchers who “encountered persistent refusals with the earlier model.” General-purpose GPT-5.6 Sol, for example, will comply with just 1.5% of the requests usually given by cyber-defenders working on codebase analysis or vulnerability identification. This percentage increases to 2.0% with Daybreak Blue access.

GPT-5.6-Cyber, on the other hand, completes 95.0% of requests, OpenAI says, up from 57.3% of the previous model, GPT-5.5-Cyber. We weren’t able to independently verify these claims, though.

While it doesn’t outright say it, OpenAI considers these models relatively dangerous to use, which is why they’re locked behind the Daybreak Cyber Partner Program. However, the program is now expanding, allowing these companies to embed the models behind their own products, managed services, or cybersecurity engagements, and offer them to clients of their own.

Those who wish to be a part of the program directly can do so by applying to join online now.

“Models running with reduced safeguards carry risks beyond standard model usage, whether from misuse or misalignment. Despite these risks, we believe that democratizing access to frontier intelligence for defenders is crucial to accelerating and automating cyber defense,” OpenAI said.

“Daybreak Blue and Daybreak Red access are available for approved individuals⁠ and organizations conducting authorized work. We control access through identity verification, account security, monitoring, approved-use restrictions, and legal attestations.”

  •  

GitHub already has an EDR. You just have to listen to it

Many of the recent supply-chain attacks could have been caught earlier if defenders looked closely at the telemetry GitHub already provides, researchers said.

At their Black Hat USA 2026 presentation, researchers Yossi Weizman of Microsoft and Mor Weinberger of Echo argued the case, saying, “GitHub can tell you’re being hacked. You’re just not listening.”

The duo described an EDR-style detection approach built from GitHub’s own event stream rather than relying solely on conventional endpoint or network telemetry.

After studying recent supply-chain attacks, including Shai-Hulud, Trivy, and Megalodon, the researchers found that seemingly different incidents repeatedly used the same techniques, from forged commit identities and poisoned tags to workflow abuse, OpenID Connect (OIDC) theft, and attempts to erase evidence.

They said they turned those recurring techniques into behavioral detections, combining GitHub webhooks, API data, and Git repository inspection to build a historical view of activity.

Their new open-source tool, dubbed “GitHub Threat Detector,” reportedly includes 22 production detection rules and 12 beta rules, with compound detections designed to correlate individually weaker signals into high-confidence alerts.

Everything leaves evidence on GitHub

The central observation in Weizman and Weinberger’s research is that supply-chain attacks often repeat the same patterns even when the targeted projects are unrelated.

A compromised identity, for example, may not be obvious from the commit itself because Git metadata can be forged. An attacker can set the author name, email, timestamp, parent, and other metadata to make a malicious commit appear legitimate.

But GitHub separately records the authenticated user who pushed the commit.

When the commit author does not match the authenticated pusher, defenders have something worth investigating, they explained. Added to this, their analysis revealed that attackers sometimes reuse the same forged identities across multiple victims. Searching GitHub for the same author’s email can therefore help connect seemingly unrelated incidents into a broader campaign.

“Forged identities in the repo which appear in other repos as well-is a strong indication of compromise,” they said.

The research found “forged maintainer’s identity” used across many attacks, including Trivy, tj-actions, Megalodon, TanStack, and Red Hat.

Another detection pitched on the same principle included tracking “Mass tag poisoning.” Mass tag poisoning involves force-moving numerous release tags onto a malicious commit so that workflows using a version such as @v1 execute attacker-controlled code. Researchers recommended adding tracking GitHub tag history through the GitHub API and comparing old and new commit references to catch this out.

OIDC offers another signal. Attackers can modify workflows to generate short-lived identities for cloud or package registries instead of stealing long-lived credentials. Watching for new or modified workflows that enable OIDC token issuance can help, the researchers said.

Correlating weak signals for stronger detection

GitHub Threat Detector follows an EDR-like pipeline: collect activity, enrich it with context, detect suspicious behavior, and then investigate or respond. The signals it ingests include live GitHub webhooks, API events, commits, tags, and Actions activity, while Git inspection provides additional context such as tag provenance.

Additionally, a PostgreSQL-backed activity store keeps the history needed to correlate events over time.

The tool took over 30 detection rules and tested them against 52 attack simulations, including reproduction of Trivy, TanStack, Megalodon, and Bitwarden CLI incidents. A separate “noise lab” helped researchers measure detection prevalence and recall, while tuning rules through allowlisting and severity adjustments.

The system, however, is not without drawbacks. Some of the trade-offs it carries include possibly disabled webhooks, rate-limited APIs, and Git inspection not being real-time.

The article originally appeared on CSO.

  •  

The CEVA Logistics data breach is having major knock-on effects across Europe - here's what we know

  • CEVA Logistics hack disrupted European warehouses and exposed some customer data
  • Retailers and Valve reported compromised delivery information and service delays
  • Clients warned of targeted scams while awaiting fuller incident details from CEVA

CEVA Logistics, one of the biggest shipping and logistics companies in the world, has suffered a major cyberattack, the effects of which are trickling down to many of its clients.

The details of the hack itself, however, are not yet publicly available and what little information is out there came from the affected clients themselves.

CEVA has not yet issued an official statement, or filed a report with the regulators, but confirmed to TechCrunch that the attack most likely started on July 29, 2026, and affected at least eight warehouses across Europe.

Technical details missing, affected customers step forward

CEVA Logistics is a global logistics and supply-chain company and a wholly owned subsidiary of CMA CGM, a French shipping giant. It provides freight forwarding, contract logistics, warehousing and transportation services to thousands of customers, including major companies in the consumer and retail, automotive, industrial and aerospace sectors.

The company operates in more than 170 countries around the world and last year it generated $18.3 billion in gross revenue, so it is a major player and a key target for attackers.

The details about the incident itself are scarce right now. We don’t know how the crooks broke in (via a successful social engineering attack, or by abusing a software vulnerability, for example), how much data they stole, or if they demanded a ransom payment in exchange for deleting the stolen goods. From one of the victims, though, we have learned that some data was most likely compromised.

When the effects of a cyberattack spill into the physical realm (as is the case here with eight affected warehouses) we can speculate the attack was either ransomware, or disruptive malware. Companies shut down parts of their IT infrastructure only when there is no other way to clear an infection or remove malicious outsiders.

In the meantime, a small number of CEVA’s customers confirmed suffering an attack and losing sensitive data.

Among them is Bol, a Dutch online retail company, which said the incident affected two systems used for processing orders from one of its fulfillment

“No bol systems were affected,” it said. “However, data of customers whose orders were processed via this location may have been viewed or copied.”

Bol also said restoring operations at one of CEVA’s locations was taking longer than anticipated. As a result, the assortment stored at the affected location was taken offline, and the products were unavailable for sale. Also, Bol is currently unable to receive goods from suppliers and sales partners at that location.

A similar announcement was given by De Bijenkorf, another Dutch luxury retailer, who said that order processing, returns, and refunds, might take longer, but stressed that its stores remained open. It also said that some customer data may have been compromised, including names, contact details, online orders data and, in some cases, VAT numbers. Payment information, bank account numbers (IBANs), credit card information, usernames, or passwords, were not compromised, it was confirmed.

Valve steps forward

Retail giants aside, PC gaming powerhouse Valve also notified its customers about the incident. It said CEVA ships Steam hardware to its European customers and as such, receives specific delivery-related information from Steam.

This information, which CEVA retains for up to 90 days after the order, was most likely compromised. It includes names, street addresses, phone numbers, email addresses, and the type and price of ordered products.

Valve warned its customers to expect fake messages, either via email, SMS, or phone, that might mention recent hardware orders.

“They may quote your address back to you to prove they're genuine. They may ask you to confirm a delivery, pay a small customs or redelivery fee, or sign in somewhere to “verify” your order. Treat all of them as fake,” Valve warned. The company also stressed that customer accounts are safe and that users need not do anything to secure them.

Other details are missing, not just for the general public, but for the affected CEVA clients, as well. Valve said it was “pressing” the company for the full scope of what was taken and how, and added that it is notifying the relevant authorities, as well.

A spokesperson of the Dutch data protection authority, Mark Schenkel, told TechCrunch the agency so far received 10 incident reports. Given the size of CEVA, it’s safe to assume there will be others.

  •  

New Pass-ta-key attack reveals all the things we didn't know about passkeys

Last week a researcher outlined what he said was a “novel attack surface” in passkeys, the new authentication paradigm that offers a more secure alternative over password-based methods. In fact, the attacks demonstrated in the post are neither novel nor unique to passkeys. This distinction is important because the research has generated confusion among end users and security professionals as they assess whether this new mechanism is truly safe to use.

The attack is called Pass-ta-key—a blending of the word passkey with the phrase “pass the key” and a nod to a plate of pasta. Arie Olshtein, a researcher at security firm Palo Alto Networks, described in a post last week how Pass-ta-key could obtain all passkeys stored in the Google Password Manager app (GPM) for Windows when it’s running on a machine infected with malware.

This came as a surprise to many people because they believed passkeys are stored exclusively in the trusted platform manager (TPM), the locked-down enclave in a hardened silicon chip that’s reserved for storing cryptographic keys and other highly sensitive information on Windows machines. If passkeys are stored in the TPM, then how was Pass-ta-key able to extract the entire set of passkeys stored by the app, they wanted to know?

Read full article

Comments

© Aurich Lawson | Getty Images

  •  

New Pass-ta-key attack reveals all the things we didn't know about passkeys

Last week, a researcher outlined what he said was a “novel attack surface” in passkeys, the new authentication paradigm that offers a more secure alternative to password-based methods. In fact, the attacks demonstrated in the post are neither novel nor unique to passkeys. This distinction is important because the research has generated confusion among end users and security professionals as they assess whether this new mechanism is truly safe to use.

The attack is called Pass-ta-key—a blending of the word passkey with the phrase “pass the key” and a nod to a plate of pasta. Arie Olshtein, a researcher at security firm Palo Alto Networks, described in a post last week how Pass-ta-key could obtain all passkeys stored in the Google Password Manager app (GPM) for Windows when it’s running on a machine infected with malware.

This came as a surprise to many people because they believed passkeys are stored exclusively in the trusted platform manager (TPM), the locked-down enclave in a hardened silicon chip that’s reserved for storing cryptographic keys and other highly sensitive information on Windows machines. If passkeys are stored in the TPM, then how was Pass-ta-key able to extract the entire set of passkeys stored by the app, they wanted to know.

Read full article

Comments

© Aurich Lawson | Getty Images

  •  

AI finds so many Windows flaws, Microsoft can’t keep up. Should you worry?

Be careful what you wish for. That’s what Microsoft found out recently when it discovered that AI — rather than making Windows more secure by helping the company close security holes — could help hackers find flaws faster than Microsoft can fix them.

It’s put Microsoft in a serious bind. Should the company devote a potentially massive amount of resources to fix every AI-unearthed security issue as fast as it can? Or should it rush to close the most important ones, and clean up the minor ones later at much less cost?

What the company decides could have tremendous implications. For years, Microsoft has faced criticism from many in the US government because of how often its technologies have been hacked, potentially putting the nation’s security at risk. Some members of Congress have suggested the government curtail contracts with Microsoft until the company proves it can provide more safety. Billions of dollars in federal contracts could be pulled.

To get a better insight into what could happen, let’s look at AI’s newfound prodigious ability to find security holes and bugs.

AI-fueled security mavens Mythos and Project Glasswing

Microsoft’s AI-related security problems are an outgrowth of the launch of Anthropic’s Mythos AI model, designed to handle cybersecurity and biology research. One of its goals is to uncover security vulnerabilities as quickly as possible, so that software companies and cybersecurity companies can fix them before hackers find the holes.

Anthropic’s early tests found that Mythos was spectacularly successful in finding Windows security flaws. “Within 31 minutes, Mythos generated its first proof-of-concept exploit for a Windows kernel vulnerability,” Axios reported in June.

Anthropic noted that its testing of Mythos “reveals a stark fact: AI models have reached a level of coding capability where they can surpass all but the most skilled humans at finding and exploiting software vulnerabilities.

“Mythos Preview has already found thousands of high-severity vulnerabilities, including some in every major operating system and web browser. Given the rate of AI progress, it will not be long before such capabilities proliferate, potentially beyond actors who are committed to deploying them safely. The fallout — for economies, public safety, and national security — could be severe.”

As a result, Anthropic decided to launch a security project it calls Project Glasswing, which it describes as “an urgent attempt to put these capabilities to work for defensive purposes.”

Many companies beyond Anthropic are part of the effort, including Microsoft, Google, Amazon, Nvidia, Apple and others. In theory, it’s a great idea. Find and fix vulnerabilities before hackers can, and everyone is safer. What could go wrong? 

Plenty, as it turns out. Access to Mythos is available to anyone, and Mythos has been finding security holes and bugs far faster than companies — particularly Microsoft — can patch them. As Pro Publica reported in late July, ‘Microsoft is struggling to fix them fast enough.” 

Too little, too late?

For now, Microsoft is only patching the most dangerous bugs and holes. And, according to Pro Public, “internal records indicate that Microsoft plans to eventually address ‘moderate’-severity flaws uncovered by Mythos. The documents made no mention of ‘low’-severity bugs.”

That’s fairly typical of the triage many companies use when deciding how much effort to put into plugging holes. But some experts believe that in the Age of AI, that’s a dangerous way to handle security. 

Vinh Nguyen, former chief AI officer and chief data scientist at the US National Security Agency and now a senior technical adviser to Anthropic and senior fellow for AI at the Council on Foreign Relations, is particularly concerned that the approach is outdated. He told Pro Publica: “The problem now is that you can chain four low-level flaws, and that can equal a high severity. If you’re Microsoft, the current triage strategy may be underpricing risks.” 

It’s already proving difficult for Microsoft to keep up with patching bugs and security holes since Mythos’ launch. July’s Patch Tuesday release fixed the most bugs in Microsoft’s history – 622 of them. Things will only get harder from here. 

The dangers for Microsoft

Microsoft is already in the doghouse for how it’s handled security. A year ago, in one of the worst attacks on Microsoft technologies, Sharepoint was hacked. Tens of thousands of servers were hit, including not just thousands of businesses, but many important government agencies as well.    

The National Institutes of Health (NIH) and the National Nuclear Security Administration (NNSA), which is in charge of the nation’s nuclear security, were among the victims. So were the Department of Homeland Security (DHS), the Cybersecurity and Infrastructure Security Agency, the Transportation Security Administration, Customs and Border Protection, and the Federal Emergency Management Agency, among many others. 

Even before then, some members in Congress were threatening to pull Microsoft contracts if it didn’t improve security. At one point Sens. Eric Schmitt (R-MO) and Ron Wyden (D-OR) sent a threatening letter to the Pentagon requesting it not increase its use of Microsoft products.

“We write with serious concern that the Department of Defense (DoD) is doubling down on a failed strategy of increasing its dependence on Microsoft at a time when Congress and the administration are reviewing concerning cybersecurity lapses that led to a massive hack of senior US officials’ communications,” the letter said, in part.

Nothing happened as a result of the hack or the letter. But that could change in a heartbeat if there’s another big attach. It seems inevitable that hackers will start taking advantage of how quickly Mythos discovers security holes and bugs, especially if Microsoft doesn’t fix them all. 

The next big hack, powered by AI, could prove very dangerous — not just for businesses and governments, but for Microsoft as well.

  •  

Japanese authorities use new tool to identify initial torrent uploaders — anti-piracy group says it identified seeder on popular anime torrenting website without torrent swarm monitoring

Recently, the Kyoto Prefectural Police caught one of the initial-seeders of the well-known Japanese torrent website Nyaa. Masakazu Ono, 56, from Sagamihara in the Kamigawa Prefecture, was arrested after a multi-year investigation. While this news is straightforward by itself, the interesting bit is that CODA, the Japanese anti-piracy entity that performed the initial cyber-investigation, identified Ono allegedly without joining or monitoring BitTorrent swarm traffic, with the help of the Japan Hacker Association (JHA).

CODA's description of only having "[analyzed] how data moves through torrent sites, such as index sites and tracker sites" is vague and can be parsed in a number of ways. The distinction between indexer and tracker is relevant: while an indexer is a user-visible list of torrents (usually a website), the tracker is the background service that software like qBittorrent actually connects to, and it lists everyone who's currently active in that torrent, whether sharing, downloading, or both.

Our hypothesis is that CODA kept close tabs on the Nyaa trackers to see which IP address (in this case, Ono's) consistently appeared as the first person to offer up a 100% complete set of data for a show, a theory that would fit with how long the operation took. JHA's founder, Takayuki Sugiura, was the first to decrypt the Winny P2P protocol in 2004 to find original uploader sources, and the methods used weren't too different from the aforementioned theory. It's also possible that Ono wasn't using a VPN but was logged into Nyaa, or activity at another website's cookies or CDN logs was used to establish a link to his activity at Nyaa, and from thereon, to the tracker.

An initial-seeder is someone who is the first to offer up data for others to download — in this case, shows and movies. The show that reportedly got Ono nailed was Midnight Taxi, a 2026 Japanese drama produced by NHK and WOWOW. However, the police apparently had been tracking him for quite a while and claimed that he had uploaded close to a thousand NHK recordings over the investigation's span.

The process started in 2021 when CODA first launched its Cross-Border Enforcement Project, aiming to identify Nyaa's uploaders. During three years, with the help of JHA, CODA seemingly collected enough information to get the Kyoto police involved in 2024. Three "secondary uploaders" from "reach sites" were charged in 2025, likely meaning regular users participating in the torrents, who got there through link aggregator sites. Fast-forward to a couple of weeks ago, and Masakazu Ono was formally arrested with specific charges.

The most common techniques used by law enforcement agencies are creating a tracker honeypot or participating in the torrent swarm themselves in a bid to identify who's sharing files. However, Nyaa's list of trackers is small and comprises well-known, trusted servers, so together with CODA's wording, it's unlikely this was the method used. Furthermore, Japanese law generally frowns on non-targeted data monitoring, meaning that techniques like Deep Packet Inspection (DPI) and traffic volume monitoring likely weren't used, at least until such time as Ono was identified.

  •  

Meet Snowflake Volunteer: Tor's Android app that lets you help people bypass censorship

  • Tor unveils Snowflake Volunteer as a standalone Android app
  • The app lets users share their open internet connection
  • It is the result of a collaboration between Tor and Bloco

The team behind the censorship-resistant Tor Browser has unveiled Snowflake Volunteer — a standalone Android app that lets you help people living in restricted countries bypass internet censorship.

Developed in collaboration with Portuguese Android studio Bloco, the app expands on Snowflake's capabilities. That's Tor’s pluggable transport, which allows people on censored networks to connect to the Tor network via volunteer-operated proxies, making their connection appear as normal traffic.

Since its official launch in April, Tor reported that the app saw an increase from about 1,300 unique proxy IP addresses per day in May to 1,700 per day in June, marking a 29% increase in one month. That represents a win for raising public awareness and expanding its volunteer-led community.

Altruistic digital privacy

Tor Browser is a free-to-use, privacy-focused network that routes Internet traffic through a series of secure computers run by volunteers in different countries — the "layers of an onion" —to prevent snoopers from identifying you personally as the one visiting sensitive sites.

Just like the best VPNs, Tor is all about protecting your privacy online. However, its system only works if people around the world volunteer to run the access points.

Tor bridges, like Snowflake, allow digital users living in safer countries to make their private connections available by turning their phones and computers into proxies, making it appear that they are making video or audio calls. A system that has been widely used as an alternative to VPNs in countries under censorship, including Iran.

It uses the "domain fronting" technique to establish a connection with one of the thousands of Snowflake proxies managed by volunteers. For users subject to censorship, if their Snowflake proxy is blocked, the broker will automatically find a new one.

🚨 New app alert! Android app called Snowflake Volunteer for those willing to help people reach the Tor network and circumvent censorship from their mobile devices. It was built open-source by Bloco, an Android app studio from Portugal. ❄️👉https://t.co/Ueltb49AqwAugust 3, 2026

What Snowflake actually needs is more volunteers' proxies that can serve as disguised access points to the Tor network. Perfectly addressing this need, the Snowflake Volunteer app was created specifically to allow people with less technical experience to easily become these proxies and contribute to the network's continued expansion.

Indeed, until now, the option was available for Android on Orbot, Tor's main Android app, or via browser extensions, a desktop command-line tool, and manual access to Tor's Kindness mode to facilitate the process.

The new app widely simplifies the experience. Users can simply install the app from F-Droid and Google Play (or build it from the source code) and let it run in the background to have their device become part of the Tor bridge. They can also restrict its use to networks with unlimited data, and set a limit on the number of people who can connect at the same time.

Once enabled, the app automatically connects with users seeking a Snowflake proxy and helps route their connection through the Tor network, making it easier and more rewarding to help others online, as people can see the impact of their actions.

Tor vs VPNs?

Is it wise to use a VPN with Tor? Unfortunately, there is no universally accepted answer.

Tor's official stance for most users is not to use a virtual private network (VPN) to avoid the risk of exposing identifying information. However, if you’re an experienced user who understands the technical aspects of VPNs and Tor routing, you could safely opt for more complex configurations.

Others, however, argue we should all use VPNs: particularly in countries with high levels of censorship, some believe it’s better to use VPNs, as they mix better into normal traffic and arouse less suspicion.

Unfortunately, though, this approach fails where VPNs are subject to restrictions or made illegal — further proof that, when it’s about digital security, there might be no one-size-fits-all solution.

  •  

'It's Stalin's dream' — Quote of the day by software pioneer Richard Stallman on the tracking capabilities of cell phones

The programmer Richard Stallman is not a household name, but his work has been instrumental in building the software industry, as has his long-term campaign for free software. He's also been a huge advocate for privacy in the digital age, and has railed against the rise of cell phones for that reason.

Who needs phones anyway?

Stallman first disclosed his views on cell phones in an interview with Network World, during a time in which smartphones were exploding in popularity.

Quote of the day

This article is part of TechRadar Pro's QOTD project to provide an insight into the minds of the brightest and most recognized figures in the technology industry today and in years gone by. Read the full series here.

During this interview, Stallman indicated his long-held belief that the portable phones that many millions use would be the perfect tool that authoritarian forces could exploit and use to track the movements of populations.

He also advocated for free software, which you would expect from the founder of the Free Software Foundation (FSF), which he established in 1985. This was backed by the creation of the GNU project – a free software, mass collaboration movement to give users freedom of choice to use and develop software for their devices.

The legacy of free software

Despite his reluctance to ever use a cell phone, one of Stallman's achievements – which he himself acknowledged in the interview – was the third-party version of the Android mobile OS, from which all proprietary software was stripped out.

He pointed to new systems like Replicant, an alternative version of Android, that can run on certain devices without additional proprietary software. The catch is that this only works with older and outdated handsets, like the Samsung Galaxy S3 or the Galaxy Note 2.

  •  
❌