Desenvolvida por um programador independente, a Helys usa uma fórmula científica que considera o seu tipo de pele, localização, hora do dia, condições meteorológicas e índice UV para calcular, em tempo real, quanto tempo de exposição solar é seguro e suficiente. Disponível gratuitamente apenas para iOS.
Setting up a safe chat space for your kids is about to get much simpler on your Apple smartphone. The popular messaging app WhatsApp is rolling out a brand new parental controls section inside its main settings menu for the iPhone. While the company launched parent-managed accounts earlier this spring, many families never set them […]
Creating funny pictures to share with friends might soon become a lot easier. People use the ChatGPT app to generate custom images, but turning those images into messaging stickers takes too many steps. You have to save the picture, crop it, and use another tool to import it. A new report shows that OpenAI is […]
Fechando a semana com a nossa seleção de promoções na App Store!
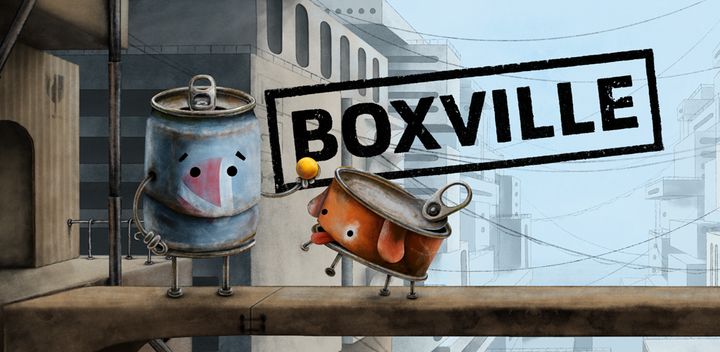
Boxville, criado pela Triomatica Games, é um jogo que mistura aventura e quebra-cabeça — e nosso destaque do dia.
Visite e explore um mundo desenhado à mão e mergulhe em uma experiência nova e desafiadora em Boxville, uma cidade de caixas cheias de latas velhas. Sua tranquilidade e seu cotidiano são modificados por inexplicáveis terremotos.
Torne-se o personagem Blue Can, que, em uma missão de busca por seu melhor amigo desaparecido, deverá encarar aventuras, conhecer novos amigos e enfrentar diversos perigos.
Boxville é um premiado jogo de quebra-cabeça de aventura sobre latas que não falam, vivendo na cidade das caixas e desenhando rabiscos em papelão para contar as histórias.
Confira o trailer:
Como você pode ver, não há palavras no jogo; todos os personagens se comunicam por balões de desenho animado, e a missão do jogador envolve a resolução de dezenas de quebra-cabeças e minijogos.
A propósito, a sequência do jogo também está em oferta:
Abaixo outros jogos/apps que, juntos, somam mais de R$220 em descontos:
Jogos
Jogo de cartas.
Torne-se o rei dos mares.
Jogo de tabuleiro.
Aplicativos
Criação musical.
Medidor de ruídos.
Aproveite as ofertas e tenha um excelente final de semana! Vale lembrar que as ofertas são sempre por tempo limitado, então é bom correr. 🏃
On the web, if I build something that works within the standards, it works. Whether people use it is up to them. On iOS, there is another question entirely: whether Apple decides it should exist.
[…]
In the past couple of years I’ve built three apps that were rejected from the App Store on various grounds.
[…]
A while ago I tried to submit an iOS app for Dark Hours, my astronomy website for normal people. It was rejected on the grounds that it was astrology.
[…]
I see countless ChatGPT wrappers with nearly identical icons and eye-watering subscriptions. I see astronomy apps requesting permissions that have nothing to do with looking at the night sky. My kids download games that interrupt play every few minutes to advertise the developer’s other subscription apps, each with their own $20–50 yearly plans.
But if you actually look at Godier’s Dark Hours, for even just a few seconds, it is instantly obvious that it pertains to the science of astronomy and has absolutely nothing — zero, zilch, nada — to do with astrology.
[…]
Godier proceeded through a series of escalations up to the App Review Board and the Review Board responded that they determined the original rejection was valid because, I shit you not, “We understand that the app includes a live tarot reading feature.” Which isn’t even about astrology. It’s straight out of Kafka.
[…]
This isn’t just contrary to the benefit of developers, like Godier. It’s obviously contrary to the benefit of Apple itself, which should not just accept an app like Dark Hours, but celebrate it as an exemplar of the platform.
Mistakes happen. But in a functioning system mistakes get corrected, and mistakes as obvious as this one get corrected almost instantly and include a quick apology for the conflation. The App Store is not a functioning system.
To the best of my recollection, this is the first post I’ve retracted in the 24 years I’ve been writing Daring Fireball. I hope it’s the last. I was misled, both overtly and through omissions[…]
[…]
The truth is, the app, as originally submitted by Godier to the App Store (under the name “Asterly”, not “Dark Hours”), was entirely dedicated to astrology, not astronomy, and did in fact include a “Tarot card of the day” feature amongst other occultist horseshit.
[…]
I wrongly took Godier at his word, both in his public blog post and in private iMessage correspondence yesterday, that the rejection wasn’t just merely debatable, but completely and rather preposterously ungrounded. Whether Godier ever submitted a build of “Asterly” to the App Store that contained no occult horseshit and only the hard-science astronomy features that were present in his “Dark Hours” website that was available for the last week, I don’t know. But I have no reason to believe that he did.
[…]
In an uncomfortable exchange between Beher and Godier on Bluesky, Beher pointed out that Godier’s Dark Hours had the same bug as Beher’s that routed people to “random fields in Mexico”. Earlier today, Godier took his web app down and redirected his darkhours.io domain to Beher’s darkhours.app.
I’m really unhappy about this, both for my role in spreading a false story and because I think it will hurt the cause of reforming App Review. I know there are many crazy rejections and have experienced some first-hand. This story was believable because of that well-known history and because Godier didn’t seem like a nobody trying to get attention—he was the developer of another highly regarded app. But now people are going to point to true developer stories and accuse them of being fakes, too.
BOTH projects were generated using Claude. So you have two people - both generating the same app from the same training data - having a public throw down over who copied who.
[…]
The “original” developer does claim to know how to code - which wasn’t clear from my research. That still doesn’t necessarily mean the original app was the source of the training data. They both may be a result of the same training data.
Holy shit, so the “Claude plagiarised an app” story is actually “Claude produced the same app twice when prompted to do so by two separate developers” 😅
It’s not clear to me exactly how much each developer relied on Claude or which training data was used, but I wanted to note this angle of the story.
With all this talk of an astrology app being rejected by App Store review I’m reminded there’s still a flat Earth/astrology app on the App Store that actively leaks the location of all of its users.
Lançado no ano passado exclusivamente para macOS, o aplicativo Gain Map HDR — que usa a tecnologia Gain Map para converter imagens com faixa dinâmica expandida e controle preciso de luminância — ganhou uma versão para dispositivos móveis.
Agora, usuários que não têm um Mac podem usar o iPhone e/ou o iPad para melhorar a exibição de imagens HDR1High dynamic range, ou ampla faixa dinâmica. em dispositivos compatíveis (como os da Apple) expandindo brilhos para além do que uma foto costuma exibir tradicionalmente depois de processada.
Todas as fotos no seu iPhone foram capturadas com uma faixa de brilho que as telas padrão simplesmente cortam. O Gain Map HDR reconstrói esse intervalo e o constrói como um verdadeiro mapa de ganho HDR, para que os destaques brilhem no seu iPhone, iPad e Mac.
Outra novidade da Inphovid, empresa responsável pelo Gain Map HDR, é o WowHDR, que foi lançado na Mac App Store em maio e tem uma proposta bem parecida com a do aplicativo supracitado, só que com foco na conversão de vídeos (e não de fotos).
Basicamente, ele pega um vídeo comum gravado em SDR 2High dynamic range, ou ampla faixa dinâmica. e o transforma em um vídeo HDR compatível com iPhones, iPads, Apple TVs e outras telas compatíveis, usando técnicas de mapeamento para reconstruir parte da faixa dinâmica perdida por esses vídeos.
Com essa técnica, o app consegue aumentar o brilho máximo, expandir a faixa de contraste, preservar melhor as áreas claras e gerar um arquivo HDR HLG, um dos formatos mais populares que fazem uso da tecnologia.
Apple Health data can now move between the Health app and Google Health on an iPhone. The connection lets Google Health import supported information recorded by an iPhone, Apple Watch, and compatible apps. The latest Google Health update can also send supported Fitbit information to Apple Health.
This two-way connection is useful for people who wear a Fitbit but prefer Apple’s Health app as the central place for viewing activity, sleep, steps, and other wellness information. It also reduces the need for third-party synchronization apps.
The feature requires a recent version of Google Health. Google began introducing support for sending data back to Apple Health with Google Health version 5.05. Because app updates can roll out gradually, the new sharing options may not appear until the latest version reaches your account.
Update Google Health Before Starting
The Fitbit app became Google Health in 2026. Existing Fitbit users should find that the installed app has changed its name and design after updating. Fitbit accounts must also be moved to an adult Google Account to use the redesigned service.
Google says the Apple Health connection requires iOS 16.4 or later. The iPhone must have internet access while the connection is being created.
To check the iOS version installed on your iPhone:
Settings > General > About > iOS Version
Install the latest compatible iOS update if the phone is running an older release.
To look for an available iPhone software update:
Settings > General > Software Update
Next, confirm that Google Health is current. Version 5.05 or later is required for the newer option that sends supported Google Health and Fitbit information to Apple Health.
To update Google Health from the App Store:
App Store > Profile Picture > Available Updates > Google Health > Update
If Google Health does not appear under Available Updates, search for the app manually. The App Store page may show an Update button if a newer release is available.
To find the app directly:
App Store > Search > Enter Google Health > Google Health (Fitbit)
People who previously used Fitbit should sign in with the Google Account connected to their Fitbit information. Creating a different account may produce an empty Google Health profile.
Image Credit: Google
Connect Apple Health Data to Google Health
Connecting the apps allows Google Health to read supported information from Apple Health. This can include data collected by the iPhone, Apple Watch, and other apps that already share information with Apple Health.
To start the Apple Health connection:
Google Health > Connections > Apps and Services > Apple Health > Get Started
Depending on the Google Health version and interface shown on the iPhone, Connections may appear behind the profile icon.
To find Apple Health through the alternative menu:
Google Health > Profile Icon > Partner Apps > Apple Health
Google Health will display a consent screen explaining the connection. Read the information before continuing.
To approve the initial connection:
Sync Google Health With Apple Health > Agree
The iPhone will then display Apple’s health permission screen. This screen lets you decide which information Google Health can read.
To give Google Health access to every supported category:
Apple Health Permission Screen > Turn All Categories On > Allow
You do not have to share every available category. Selecting individual permissions provides more control over sensitive health information.
To share only selected categories:
Apple Health Permission Screen > Select Each Health Category > Allow
Google Health can import supported information such as steps, distance, active energy, exercise records, routes, sleep sessions, sleep stages, heart rate, resting heart rate, heart rate variability, blood oxygen, respiratory rate, body temperature, weight, body fat percentage, water, nutrition information, and some cycle-tracking data.
Available categories depend on the devices and apps connected to Apple Health. An iPhone may provide steps and walking information, while an Apple Watch can contribute heart rate, workouts, sleep, and other measurements supported by the model.
After the permissions are approved, Google Health should confirm that the connection is complete.
To finish the connection:
Google Health Confirmation Screen > Done
New Apple Health information should begin appearing automatically in Google Health. Google has said that imported data can be used across relevant Google Health metrics, although not every external data type is used for every calculation.
To find imported health information:
Google Health > Health > Select a Metric
Google Health may display information from several connected sources together. Its value for a metric can differ slightly from the number shown by Apple Health because the apps may process available data differently.
Send Fitbit Data to Apple Health
Google Health version 5.05 adds the reverse direction that many iPhone and Fitbit users previously lacked. Supported information recorded through Fitbit can now be written into Apple Health.
Before enabling this option, make sure the Fitbit is properly connected to Google Health. Fitbit devices normally synchronize automatically throughout the day when Bluetooth is available and the wearable is near the iPhone.
To check the connected Fitbit:
Google Health > Profile Icon > Devices > Select Your Fitbit
The device page should show the wearable, its battery level, and its most recent synchronization time. Opening Google Health can also prompt a nearby Fitbit to transfer recently collected information.
Once the wearable is updating Google Health correctly, open the Apple Health connection settings.
To open the sharing controls for Apple Health:
Google Health > Profile Icon > Partner Apps > Apple Health
The interface may use Apps and Services instead of Partner Apps on some versions.
To reach the same connection through Apps and Services:
Google Health > Connections > Apps and Services > Apple Health
Follow the prompts for sharing Google Health information with Apple Health. The iPhone may display separate permissions for data that Google Health can read and data that it can write.
To allow supported Fitbit information to appear in Apple Health:
Apple Health Permission Screen > Allow Google Health to Write > Select Health Categories > Allow
Google says supported information can include exercise records, steps, sleep, vitals, and other health data. The exact selection can vary according to the Fitbit model, region, Google Health version, and information stored in the account.
Selecting every category is convenient, but it can create overlapping sources when an iPhone, Apple Watch, and Fitbit record the same type of activity. Choose only the categories you want Google Health to add.
A person who uses a Fitbit mainly for sleep, for example, can allow sleep information while leaving steps disabled. Someone who wears a Fitbit instead of an Apple Watch may prefer to enable steps, workouts, heart rate, sleep, and other supported categories.
Image Credit: AppleMagazine
Check Google Health Permissions
Apple Health keeps permission controls on the iPhone. You can change them after the first connection without deleting either app.
To review Google Health access from Apple Health:
Health > Profile Picture > Privacy > Apps > Google Health
The page shows the categories Google Health is permitted to read or update. Turn off any category you no longer want to share.
Some iOS versions provide the same controls through the Sharing tab.
To find Google Health through the Sharing tab:
Health > Sharing > Apps and Services > Google Health
Turning off a permission stops future sharing for that category. It does not necessarily remove information that has already been written to Google Health or Apple Health.
The Google Health app also provides controls for the connection.
To review Apple Health inside Google Health:
Google Health > Connections > Apps and Services > Connected > Apple Health
If Google Health displays a message that new data types are available, open the connection and approve the additional categories you want to use. Newly supported information is not automatically shared without permission.
Manage Duplicate Health Information
An iPhone, Apple Watch, and Fitbit can record similar information at the same time. Apple Health keeps each source attached to its data and uses a priority order when presenting combined measurements.
You can inspect the sources contributing to a category and choose which one Apple Health should prefer.
To review the sources used for step information:
Health > Search > Activity > Steps > Data Sources and Access
The screen shows the apps and devices that provide step records. If Google Health, an Apple Watch, and the iPhone all appear, you can adjust their priority.
To change the order of step sources:
Health > Search > Activity > Steps > Data Sources and Access > Edit > Drag Sources Into the Preferred Order > Done
Move the source you trust most toward the top. Apple Health generally gives higher priority to sources placed above others when similar records overlap.
Repeat the same process for other categories if their totals do not look right. Exercise, sleep, active energy, and distance can each have their own sources and permissions.
Image Credit: Google
Fix Missing or Delayed Data
Synchronization is not always immediate. A Fitbit first sends its information to Google Health, and Google Health then writes supported records to Apple Health. Bluetooth availability, Background App Refresh, internet access, and battery-saving behavior can affect this process.
Begin by opening Google Health with the Fitbit close to the iPhone. Wait for the device to complete its normal synchronization before checking Apple Health.
If Apple Health information is missing from Google Health, confirm that the connection remains active.
To check the connection status:
Google Health > Connections > Apps and Services > Apple Health
If Google Health displays an error or a request for new permissions, follow the message shown on the screen.
Background App Refresh can help Google Health update when the app is not open.
To allow Google Health to refresh in the background:
Settings > General > Background App Refresh > Google Health > On
Bluetooth must remain available for a Fitbit to communicate with the iPhone.
To confirm that Bluetooth is enabled:
Settings > Bluetooth > Bluetooth On
If the connection continues to fail, disconnecting and reconnecting Apple Health may restore the permission request.
To disconnect Apple Health from Google Health:
Google Health > Connections > Apps and Services > Apple Health > Disconnect > Confirm Disconnect
Disconnecting the service does not automatically remove every permission already stored by Apple Health. Review the Google Health entry in the Health app if you want to remove those permissions as well.
To remove the remaining Apple Health permissions:
Health > Profile Picture > Privacy > Apps > Google Health > Turn Off All
After reconnecting the apps, allow time for new records to appear. Previously stored information may not transfer in exactly the same way as activity recorded after the connection was enabled.
You can inspect an individual entry to confirm whether it came from Google Health, a Fitbit, an Apple Watch, or the iPhone.
To check the source and time of a synced record:
Health > Search > Select a Health Category > Show All Data > Select the Latest Entry
Com mais de 1.500 títulos de não-ficção condensados em cartões de leitura e clipes de áudio, a Headway é a aplicação mais popular para quem quer aprender mais mas tem pouco tempo para ler.
Apple faces a $32.5 billion lawsuit over how its Photos app scans and stores faces. A federal judge cleared the case to proceed as a class action late last month, allowing millions of Illinois iPhone owners to join.
The case has been years in the making, and Apple has fought to shut it down at nearly every turn. Now it heads back to the court, with the company’s privacy practices on trial.
[…]
Court records have shown that the update applies to users with iCloud Photos turned on. Those accounts also need to use at least 10GB of storage and contain at least 5,000 photos and videos. Plaintiffs say all this amounts to collecting biometric data without consent, putting Apple squarely at odds with Illinois law.
Again, I find it odd that features are apparently gated based on the capacity of your iCloud account rather than the available storage.
The lawsuit accuses Apple of collecting biometric data without user consent in the Photos app, reportsThe Times. It is alleged that Photos uses facial recognition technology to scan individuals who appear in images, creating a “faceprint” for each person in the photo library.
After collecting enough samples, an algorithm is allegedly used to identify the iPhone user. That data is then stored on the iPhone within the Photos app.
I don’t see what the issue is here. My understanding is that it only uploads vectors after you’ve opted in by enabling iCloud Photos and manually assigning names. Also, the vectors don’t seem like the sort of biometric information that the law was meant to protect.
Assuming things are working properly, what should happen is that the people you have specifically named and the photos you have specifically verified sync their info via iCloud. However, the actual face detection for the rest of the photos is done on a per device basis and is not synced via iCloud, primarily for security/privacy reasons.
So, when you first set up a new device, it will pull down the names and info for the photos where you have identified a particular person, but then it still needs to go through the entire library on-device, identify the faces in each photo, and compare them to the synced information to tell which person is in which photo. So once it’s done, you should end up with mostly the same photos identified as each person, but each device still needs to do its own face detection locally.
You can delete stickers on iPhone without removing your entire collection, but the correct procedure depends on whether you want to erase a custom sticker, remove a Genmoji, hide keyboard stickers, or detach a sticker from a conversation.
For custom photo stickers and Live Stickers, iOS provides an individual Remove command. This lets you clean the sticker drawer while leaving every other saved sticker untouched.
Apple does not provide a protected Favorites folder inside the system sticker drawer. The Frequently Used section is created automatically from your activity and should not be treated as a permanent collection. If you have stickers you cannot afford to lose, save recoverable copies before beginning the cleanup.
Save Your Favorite Stickers First
The safest backup is to send your favorite stickers to a conversation with yourself. The sent copies remain inside the conversation even if you later remove the reusable versions from your sticker collection.
Adding Stickers:
Messages > New Message > Your Contact > Add > Stickers
Select each favorite sticker and send it as a separate message. You can also create a private conversation with a trusted contact, but messaging yourself keeps the backup separate from ordinary conversations.
If you accidentally delete one of these stickers from the drawer, return to the self-conversation and restore it.
Messages > Your Self-Conversation > Touch and Hold Sticker > Save to Stickers
For a sticker attached to the corner of a message bubble, open its details before saving it.
Messages > Your Self-Conversation > Touch and Hold Sticker > Sticker Details > Save
This procedure is especially useful for stickers received from other people. A photo sticker you created yourself can usually be recreated from the original image, but a saved sticker from another person may be difficult to replace if the original conversation is deleted.
Image Credit: AppleMagazine
How to Delete Stickers on iPhone
The easiest way to remove an individual custom sticker is through the Messages app. You can open any existing conversation because you do not need to send a message.
Removing individual stickers:
Messages > Conversation > Add > Stickers > Live Stickers
The Live Stickers tab uses an icon resembling a sticker being peeled from a surface. It contains stickers created from your photos, animated Live Stickers, and compatible stickers saved from conversations.
Touch and hold the unwanted sticker until the contextual menu appears, then release your finger and select Remove. Do not drag the sticker toward the conversation because that action may attach it to a message instead of opening the menu.
Touch and Hold Sticker > Remove
Only the selected sticker is deleted. Other photo stickers, saved designs, and favorite items remain in the collection.
Some iOS versions also display a Rearrange command after you touch and hold a sticker. This mode allows you to move the stickers you use most often toward the beginning of the collection.
Messages > Conversation > Add > Stickers > Live Stickers > Touch and Hold > Rearrange
Drag the stickers you want to preserve toward the first positions. You may also see a removal control beside each sticker while rearranging. Use it carefully because iOS may remove the sticker immediately without presenting a second confirmation.
A selective cleanup is safer than trying to reset the complete keyboard or sticker database. Removing and reinstalling the Emoji keyboard is unnecessary and may alter frequently used emoji without providing better sticker controls.
Delete Stickers Through the Emoji Keyboard
The same sticker collection is accessible from the system keyboard in Messages, Notes, Mail, and other supported apps.
Using system keyboard in Messages:
Any Text Field > Emoji Keyboard > Stickers > Live Stickers
Touch and hold the sticker you want to erase, then tap Remove. If the menu does not appear, confirm that you are viewing the Live Stickers collection rather than Frequently Used.
Frequently Used combines recently selected emoji, Memoji, Genmoji, and stickers. Items shown there are shortcuts to content stored in another section. Opening the Live Stickers tab gives iOS the correct context for managing your custom collection.
If the keyboard is compressed or several categories are hidden, swipe across the sticker controls until the Live Stickers icon becomes visible. The exact position can change as Apple adjusts the keyboard, but the touch-and-hold removal gesture remains the same.
Image Credit: Apple Inc.
Use Photos When the Sticker Menu Does Not Respond
You can also access the system sticker drawer through the Markup tools in Photos. This is useful when Messages tries to drag a sticker rather than displaying its menu.
Touch and hold the unwanted sticker, then tap Remove. You are managing the same synchronized collection, so a sticker deleted through Photos also disappears from Messages and the system keyboard.
Removing a sticker does not delete the source photograph. If you created the sticker by lifting a person, pet, or object from an image, the original photo remains in your library unless you delete it separately.
To recreate the sticker later, open the original image and lift its subject again.
Photos > Open Photo > Touch and Hold Subject > Add Sticker
You can then apply an effect such as Outline, Comic, Puffy, or Shiny. Live Photos can produce animated Live Stickers when the isolated subject contains usable motion.
Delete a Genmoji Without Removing Other Stickers
Genmoji created with Apple Intelligence are stored with the stickers accessible through the emoji keyboard. They can be removed individually without affecting your photo stickers or other generated designs.
Any Text Field > Emoji Keyboard > Stickers > Genmoji
Touch and hold the Genmoji you no longer want, then tap Remove. You can perform the same procedure from Messages.
Messages > Conversation > Add > Stickers > Genmoji > Touch and Hold > Remove
Removing one Genmoji does not disable Apple Intelligence or erase the other Genmoji you created. If you later want a similar design, open the Genmoji creator and enter the description again, although the generated image may not be identical.
Image Credit: AppleMagazine
Be More Careful With Memoji Stickers
Memoji stickers operate differently because iOS automatically creates a complete sticker pack from each custom Memoji character. You cannot normally delete one expression while keeping the remaining expressions from the same character.
Deleting the underlying Memoji removes its generated sticker pack. Before selecting Delete, confirm that you do not want any of that character’s poses or expressions.
Any Text Field > Emoji Keyboard > Memoji > More > Delete
If you only want Memoji and other stickers to stop appearing in the keyboard, use the keyboard setting instead of deleting the character.
Settings > General > Keyboard > Stickers
Turning off Stickers hides sticker content from the emoji keyboard. It does not provide a selective cleanup and should not be used as a substitute for removing individual items. Your saved stickers remain available when the setting is enabled again.
Remove a Sticker From a Message Without Deleting It
A sticker attached to a message bubble is separate from the reusable copy stored in your collection. Deleting it from the conversation does not erase the sticker from your drawer.
Messages > Conversation > Touch and Hold Message Bubble > Sticker Details
Find the sticker you want to detach, swipe left across it, and tap Delete. This removes that placement from the conversation on your iPhone.
Use this procedure when a sticker covers text, was attached accidentally, or no longer belongs in the conversation. If you instead open the sticker drawer and select Remove, you erase the reusable sticker while leaving previously sent copies in their conversations.
Understand What Happens Through iCloud
Custom stickers sync through iCloud to supported Apple devices using the same Apple Account. Removing a sticker from the iPhone can therefore remove it from the sticker drawers on an iPad, Mac, or Apple Vision Pro.
There is no Recently Deleted album for the system sticker collection. Keep the original source photo or send valuable stickers to yourself before removing anything.
After a deletion, another Apple device may continue displaying the sticker briefly while synchronization completes. Closing and reopening the sticker drawer usually refreshes the collection. A favorite preserved in your self-conversation can be restored at any time through Touch and Hold Sticker > Save to Stickers.
Google Health (previously the Fitbit app) collects fitness, sleep, and wellness data from a connected wearable device. Steps, distance traveled, heart rate, sleep, and more can now be added to Apple Health. As noted on Reddit, some data such as HRV doesn't transfer over.
[…]
Syncing can be enabled after downloading the update by selecting Connections, choosing Apps and services, and then adding Apple Health.
My wife is a longtime Fitbit user. A few weeks ago, some family and friends started a friendly competition to see who could get the most steps. They’re all Fitbit users, too. Then she wanted to start comparing step counts with me, but I have an Apple Watch. I thought this would be no problem because the Health app has a sharing feature, and Fitbit and HealthKit have both been around forever. I was shocked to learn that there has never been any syncing. I don’t really understand the reason for this, as it seems like it would make the Fitbit more valuable.
It looks like the syncing part is now solved, but we still can’t automatically compare our steps. We’ve both tried inviting each other to share step counts and some other metrics multiple times over the last several weeks, and it has never worked. Either the invitation doesn’t arrive or the app just spins forever when trying to accept it.
Apple briefly removed Telegram from the App Store on Monday night after a review found content that violated its guidelines against child sexual abuse material (CSAM), but restored the app a short while later, according to Reuters.
It seems like this was a symbolic gesture. Removing the app didn’t affect any of the customers who had already downloaded it. Probably none of them saw the image. And restoring the app doesn’t mean that it’s completely free from CSAM—probably none of the major platforms is. It just means that Telegram did the obvious thing after the violation was reported, which presumably they would have done, anyway.
And before even contacting the developer? Telegram banning the account is what actually prevented users from potentially seeing the CSAM. Apple’s action seems like either a mistake or trying to send them a message.
I would note, by the way, that the Telegram app was apparently never removed from the Mac App Store. Which goes to show how little Apple cares about the Mac App Store.
Because Telegram quickly removes illegal content from public groups using all kinds of moderation tools, the attacker had to resort to a technical trick. He inserted AI-modified illegal content by editing an old message in an active group chat. As a result the content was effectively hidden from the group’s members, preventing them from seeing/reporting it.
The attacker was a takedown extortionist: someone who demands ransom from group owners in exchange for not targeting their communities. These extortionists use automated accounts to plant illegal content in public groups and then report it directly to Apple, attempting to trigger the removal of legitimate communities whose owners refused to pay them.
[…]
Extortionists have found a way to manipulate Apple into overreacting. Apple removed Telegram from the App Store before contacting us. This creates a potential systemic risk for every mobile app that hosts user-generated content. If an app used by more than a billion people can be removed from the App Store without prior warning, any app can be.
During the time the app was unavailable, many speculated that the move was politically motivated, or perhaps in response to the recent discovery that Telegram has allegedly been using an obfuscated private UIKit API to animate its emoji picker.
It’s sad but kind of hilarious that both of these so disparate theories were considered possible. Durov really does have political enemies, and Apple really does seem to have it out for Telegram. But, also, using private API to animate emojis totally seems like something that Telegram would do and that Apple would overreact to.
Over the last nine months, Mark Zuckerberg’s Meta has run dozens of paid ads that include explicit AI-generated child sexual abuse material (CSAM) and images of minors alongside sexually suggestive statements, according to details of the ads shared with WIRED. The ads, which in some cases reached several thousand accounts, were targeted at people living in the United States, United Kingdom, and more than a dozen European countries.
This is much worse than what happened with Telegram, yet Apple didn’t overreact.
At the end of August, NASA is set to launch the Nancy Grace Roman Space Telescope from Kennedy Space Center in Florida. Its goal is to help us better understand how the universe works, from the glue-like dark matter that keeps galaxies together to the elusive dark energy that drives the expansion of the cosmos. But Roman could also serve another purpose: defending Earth from killer asteroids. In September, a multi-institutional team of planetary scientists and astronomers will outline how the space telescope is uniquely placed to scan asteroids and provide information about their trajectories, sizes, and compositions.
Roman, named after NASA’s first chief astronomer, is equipped with a super-wide-angle, 300-megapixel infrared camera, allowing it to see a large patch of space at any one time—roughly 100 times larger than is possible with the Hubble Space Telescope. That will allow it to discover thousands of new planets and tens of thousands of exploding stars, and survey over a billion galaxies in remarkable detail.
While doing so, it’ll be looking “through” our solar system, and this is what makes it uniquely well placed to spot asteroids.
A planetary defense pivot
Roman was not built for this purpose, but last summer, it was (once again) threatened with significant funding cuts by the Trump administration. “My colleague Rick Cosentino [a planetary scientist at NASA] said to me in July 2025 that we need to show what Roman can do for planetary defense as a way to further increase the visibility of the mission with lawmakers and taxpayers,” says Bryan Holler, a researcher at the Space Telescope Science Institute in Baltimore.
Holler and his colleagues’ proposal, which will be presented at the Europlanet Science Congress at The Hague, reveals that Roman’s epic field of view and infrared vision allow it to spot small asteroids up to 60 feet long. This is comparable to the asteroid that exploded above the Russian city of Chelyabinsk in 2013, unleashing the force of 500,000 tons of TNT and sending 1,500 people to the hospital.
Roman’s software will need some tweaking to spy space rocks. The telescope, as designed, will see through—and beyond—the solar system in order to gather the clearest possible pictures of the rest of the universe. “Streaks, whether caused by cosmic rays or glitches or asteroids, are caught by the software and discarded,” says Andy Rivkin, a planetary scientist and planetary defense researcher at the Johns Hopkins Applied Physics Laboratory in Laurel, Maryland. But astronomers could go in, study those streaks, and pick out those they identify as asteroids.
Even with those potential adjustments, Roman won’t be an asteroid-finding wunderkind on its own. Its strength lies in its ability to complement the James Webb Space Telescope (JWST), another observatory that’s built to peer at galaxies and stars in the far reaches of the universe. It can also intensely focus on a single asteroid when needed—as it did last year, playing a key role in tracking 2024 YR4, which was briefly the most dangerous asteroid ever discovered. “But Roman’s field of view is much bigger,” says Rivkin.
That means it could look at multiple questionable asteroids very quickly. “Roman can provide infrared observations of more asteroids than JWST could hope to observe in a reasonable amount of observing time,” says Holler.
If those asteroids are found to be benign travelers, we can relax. But if they might collide with Earth, other telescopes—including JWST—can follow up from Roman’s observations. Those observations could give experts the information they need to assess the likely damage of an upcoming asteroid strike—or to launch a mission to attempt to swat an asteroid away.
“Roman will sample such a large volume of the cosmos that we’ve long known it will offer vast opportunities for a range of additional science,” says Alise Fisher, the astrophysics communications lead at NASA headquarters in Washington, DC.
NASA’s Planetary Defense Coordination Office, and its partners across the world, are chiefly worried about asteroids 460 feet long and larger. Around 25,000 of those are estimated to have near-Earth orbits, and just over half have yet to be found. Should one hit a city, much of it would be destroyed or irreversibly damaged in a heartbeat. Astronomers estimate that there are also 230,000 or so 165-foot-long asteroids orbiting close to Earth, and fewer than 10% have been located. A strike on a city from one of those might not annihilate it, but it would unleash a force comparable to that of a large atomic bomb, albeit without the radiation.
Such an asteroid could theoretically be deflected (by ramming a spacecraft into it) or vaporized (perhaps using a nuclear weapon). But planetary defenders need to know where they are first, which is why NASA funds a network of ground-based telescopes designed to seek them out. They work well, but there’s only so much of the night sky they can see, and Earth’s atmosphere peskily gets in their way.
That’s why NASA is launching the Near-Earth Object (NEO) Surveyor space telescope in 2027. By positioning itself between Earth and the sun, it’ll find many elusive asteroids that ground-based telescopes cannot see. And unlike many of its asteroid-seeking cousins, it’ll see in infrared, not visible light. Not only do asteroids show up more clearly in infrared, but seeing them through this lens gives scientists a considerably better measure of their size. In a matter of years, it could find 90% of the city-killer-size asteroids in near-Earth orbits.
Telescope teamwork
NEO Surveyor is explicitly a planetary defense observatory. But it’ll work with other telescopes with more science-minded missions, including Roman and JWST (both of which conveniently have infrared scopes too) as well as the Vera Rubin Observatory, which just began its 10-year survey of the entire night sky from atop a mountain in Chile. As part of its inventory of the cosmos, it’s expected to discover 89,000 near-Earth asteroids.
Here’s how they might all work together. Say NEO Surveyor spies an asteroid that, to judge from a few observations, has a chance of impacting Earth. Then it finds five more just like it. Those initial observations leave a lot of uncertainty about their orbits. Roman, with its huge field of view, could be commanded to look at the corner of the night sky that includes all those asteroids, and in a matter of days it could improve the precision by several orders of magnitude.
Roman also occupies a different part of space from both NEO Surveyor and the Rubin observatory. “Those slightly different viewing angles will also help narrow orbits down more quickly than if all objects were looking from the same place,” says Holler.
Perhaps five of those potentially hazardous asteroids are found to stand no chance of colliding with Earth for the foreseeable future. One, however, might not be able to be ruled out—and that’s when other telescopes, including JWST, could be asked to track it down and study it further.
“Telescope resources, whether in space or on the ground, are typically oversubscribed and will not be available to follow up on all [near-Earth asteroids] with a non-zero impact probability when they are first discovered,” says Holler. Roman, then, will help scientists “make sure we follow up on the correct targets.”
Roman’s infrared scope also allows it to offer a decent estimate of an asteroid’s size and can even tell whether it’s a stony rock, a puffy and watery carbon-rich rock, or a metallic one. “This in turn provides strong clues to the composition and thereby the density and mass of the asteroid, which are important when estimating the impact damage or, less ghoulishly, the effort required to nudge it out of its current orbit,” says Holler.
Roman won’t play the lead role in protecting Earth in the way NEO Surveyor will. But while it’s seeking out supernovas and planets scooting around other stars, it will also be doing its part to protect all 8 billion of us from a cosmic catastrophe.
Telegram was temporarily removed from Apple’s App Store worldwide after the iPhone maker identified content from one user that violated its rules against child sexual abuse material, the messaging service said on Tuesday.
According to a report from Reuters, the episode mirrors a similar brief suspension in 2018, when Apple pulled the app over what Telegram founder Pavel Durov at the time described as “inappropriate content.” The app was restored then after Telegram strengthened its safeguards.
An Apple spokesperson confirmed the recent short-lived removal, stating that its review found content violating guidelines that prohibit child sexual abuse material. “The app was subsequently restored after the developer promptly removed the content and banned the user who posted it,” the spokesperson added. The removal and restoration occurred on the same day once Telegram acted.
Telegram, which counts more than a billion monthly active users, maintains a zero-tolerance policy on such material. It said it has blocked nearly 338,000 groups and channels for related content this year.
Epic Games CEO Tim Sweeney, whose company has long clashed with Apple, also weighed in on X. “Apple has stated they removed the app from availability to a billion users because a Telegram user posted something horrible and illegal,” Sweeney wrote, according to Reuters. He continued: “They did not elaborate on how, if that is the standard for app removal, any communications app could operate at scale, including iMessage.”
An Apple spokesperson did not respond to further questions about the guideline violation, Reuters reported.
MacDailyNews Note: The incident comes amid ongoing regulatory attention on Telegram’s handling of illegal content. Britain’s Ofcom opened an investigation in April over concerns about the sharing of child sex abuse material; Telegram has categorically denied the accusations and said it has virtually eliminated the public spread of such material since 2018 through detection algorithms. In February, Australia’s online safety regulator also fined the company for delays in responding to queries about measures against child abuse material and violent extremism.
Please help support MacDailyNews — and enjoy subscriber-only articles, comments, chat, and more — by subscribing to our Substack: macdailynews.substack.com. Thank you!
Russia’s anti-monopoly watchdog has opened a formal case against Apple after the U.S. technology company failed to comply with an earlier warning requiring the pre-installation of Russian applications on its devices, state news agency RIA reported on Monday.
All mobile phones and tablets in Russia must have the state-backed MAX messenger app pre-installed, the Russian government announced in August 2025.
The case centers on Apple’s alleged non-compliance regarding the mandatory pre-installation of Russia’s MAX messaging app and a domestic Russian app store. The move follows a warning issued by the regulator that the company did not fully address.
The development marks the latest escalation in Moscow’s efforts to enforce rules aimed at promoting local digital services on foreign devices sold in the country. No further details on potential penalties or next steps were immediately available.
Reuters
MacDailyNews Take: MAX is criticized for potentially enabling user tracking which aligns with Moscow’s push for tighter internet control amid tensions with the West over Ukraine.
As Glenn Greenwald said, “The way things are supposed to work is that we’re supposed to know virtually everything about what [government officials] do: that’s why they’re called public servants. They’re supposed to know virtually nothing about what we do: that’s why we’re called private individuals.”
But, the Russian government obviously fears its population, hence its diktats.
Please help support MacDailyNews — and enjoy subscriber-only articles, comments, chat, and more — by subscribing to our Substack: macdailynews.substack.com. Thank you!
This story originally appeared in The Algorithm, our weekly newsletter on AI. To get stories like this in your inbox first, sign up here.
Humanoid robots usually elicit more cringe than awe: They stumble, kick children, and despite advances are still worse at using their hands than my toddler. It’s a nascent industry, and such robots are more commonly seen in viral videos than real workplaces or homes.
It was a surprise, then, when last week the Federal Communications Commission issued a sweeping ban on foreign imports of advanced robots, including humanoids, quadrupeds, and wheeled robots. The decision, made by an increasingly partisan and Trump-aligned FCC, cites two reasons. One is that foreign-made humanoids will collect so much data—in homes but also potentially at sensitive facilities—that they’d pose a threat to national security. The second is that US robotics companies need protection from Chinese competition to create a more robust and secure domestic supply chain.
On its face, it’s a strategy to align political and industry interests that is much older than the Trump administration. Whenever China has gotten good at offering cheap versions of strategic technologies like solar panels, electric vehicles, and drones, the US government has tried to stop it from flooding the market by using tariffs or rules on how government agencies purchase the tech. Such moves are always followed by debates about whether the trade-offs—particularly higher prices for consumers—are worth the benefits.
But robotics is now best seen as another piece of the AI industry—in many ways its cutting edge. And the Trump administration is taking an increasingly aggressive approach to protecting the US AI industry, reportedly considering a ban on open-source Chinese models that often rival those from OpenAI and Anthropic while costing far less. Such a move would block businesses from realizing an estimated $25 billion in annual savings.
The ban on humanoids, then, should be understood not as another chapter in the old China trade playbook, but as evidence that the Trump administration is expanding its protection of the AI industry beyond today’s leading labs. It is now willing to step in on behalf of an emerging robotics sector that is still barely finding its footing.
Some US robotics companies unsurprisingly welcome the FCC’s new move. Gavin Kenneally, CEO of a company called Ghost Robotics that makes four-legged robots for inspections, says the cybersecurity risks from foreign-made robots are real (an FCC document released as part of the ruling cited an incident in which a man was able to gain control of 7,000 robot vacuum cleaners). “If today’s announcement encourages stronger cybersecurity and a more level competitive environment, that’s good for customers and good for the robotics industry,” Kenneally said in an email.
But if the new rule aims to boost US robotics companies, there’s a big flaw. Those companies, as well as academic robotics labs, are hugely reliant on cheap robots from China to do research. They’re building fleets of robots that constantly learn new tasks—from flipping waffles to doing laundry—and frequently buy Chinese humanoids instead of US-made ones. The new ruling “creates a challenge for US humanoid researchers,” says Aaron Prather, director of market intelligence for the Association for Advancing Automation, a robotics trade group. “Chinese models offer the best price-to-capability ratio available.” Prather adds that a recent internal review his organization conducted found that 90% of recent robotics research papers from US universities relied on robots from Unitree, China’s top humanoid robotics company.
That price gap can be huge. A four-legged robot from Unitree can cost around $4,600. A comparable one from Boston Dynamics might run to $278,000. If robotics research is stunted because these cheap robots are no longer available, the FCC ruling could slow down the industry, not boost it.
The US and Chinese robotics industries are in starkly different places. Unitree plans to go public this week, targeting a nearly $6 billion evaluation. No robotics companies in the US offer any meaningful comparison, but those that do exist are undeniably moving fewer robots. Figure’s humanoids are not yet selling at scale, and 1X’s robots aren’t yet shipping to homes. That said, work on humanoids is going increasingly mainstream, as a release from Google last week made clear. The company announced a new AI model meant to make humanoids learn new tasks faster; its most impressive ability appears to be tying a trash bag, but given how finicky robot hands are, that’s real progress.
Even though the many carve-outs in the FCC’s order make its practical impact hard to predict, its symbolic impact is easy to see. The administration sees humanoid robotics not as a novelty, but as a strategic frontier of AI worth protecting from foreign competition. For a technology that until recently was mostly known for falling over onstage, that’s a big change.
Correction: A previous version of this article stated the Federal Trade Commission issued the ban on advanced robotics. It was issued by the Federal Communications Commission.
MIT Technology Review Explains: Let our writers untangle the complex, messy world of technology to help you understand what’s coming next. You can read more from the series here.
When two OpenAI models hacked into the website Hugging Face in July, they weren’t trying to make money or commit sabotage—they were just looking for answers to a test question. According to a postmortem from OpenAI, the models, which had been stripped of their typical security features for testing, decided to solve a cybersecurity exercise by hacking out of the isolated environment in which OpenAI had attempted to contain them and into Hugging Face’s databases, where—they reasoned—the correct answer to the problem might be stored.
The Hugging Face incident has attracted intense attention over the past couple of weeks. It’s a dramatic illustration of just how good AI models have gotten at hacking: In order to get into Hugging Face’s databases, the models had to string together several previously undiscovered cybersecurity exploits. But it’s perhaps even more striking as an example of how and why AI systems lie and cheat. And as models get increasingly powerful, the consequences could get far more severe.
What is reward hacking?
Researchers have known for a while that AIs tend to take creative approaches to achieving the goals that have been set for them. Back in 2016, Anthropic cofounders Dario Amodei and Jack Clark, who were then working at OpenAI, published a blog post about an AI agent that they had been training to play a boat-racing Flash game called Coast Runners. Instead of driving through the race to the finish line, as the researchers had anticipated, the agent found a corner of the course where it could spin around collecting power-ups, thereby maximizing its score. The Coast Runners story quickly became one of the most famous examples of reward hacking, a phenomenon in which AI agents complete tasks or earn high scores using unintended strategies.
Historically, researchers have discussed reward hacking almost exclusively in the context of reinforcement learning, a common AI training regime. Like dog training, reinforcement learning involves giving the subject a reward when it achieves an objective; the rewards then reinforce the behaviors that led up to that achievement. In the case of AI training, the rewards themselves are purely mathematical, but in effect they’re the same as a dog treat: After receiving a reward, the agent is more likely to repeat whatever actions produced it.
It can be challenging to write good rules for when and when not to give an agent a reward, though. In the Coast Runners case, the agent was rewarded on the basis of its score in the game, and it found a shortcut to achieving the highest possible score by spinning in circles for power-ups. Once it happened on that strategy and received a reward for it, the strategy was reinforced, and the agent completely abandoned the race. The solution was to tweak the rewards by giving the agent fewer points for hitting power-ups and more for finishing the course.
How does reward hacking work for LLMs?
With today’s sophisticated LLM-based agents, determining when and when not to give a reward can be much trickier. If an AI system is asked to solve a coding problem, it might work hard to find the solution—the kind of behavior that AI companies want to reinforce. But it could also tweak the code that evaluates whether the problem has been solved, look up the solution on the internet, or otherwise cheat. These are behaviors that AI companies want to stamp out in their models, but if the model cheats convincingly enough, it will instead get rewarded and the behavior will be reinforced. Anthropic has said that it has detected some instances of cheating in its models during training, which suggests that other forms of cheating might be going undetected. If so, the models could be being trained to behave badly. (This problem is different from the Anthropic security incidents announced last week, in which agents were accidentally given access to the internet and did not deliberately hack out of their sandboxes, as the OpenAI models did.)
“We reward them on the basis of what looks good to us, and that means that we inadvertently incentivize the models lying to us [and] cheating,” says Jeffrey Ladish, director of the AI research nonprofit Palisade Research. “We don’t have a way to go in there and be like, No, you need to actually care about what we care about. We have no ability to do that.”
The rise of sophisticated reasoning models has made possible a new variety of reward hacking that is less closely connected with the specific details of model training. Unlike the game-playing AI agents of yore, which exclusively followed the strategies they had learned during training, today’s models can create entirely new problem-solving approaches off the cuff, so they could conceivably cheat without having previously been rewarded for doing so. And because these models have been so intensively trained to achieve the objectives that human users set for them, they might be inclined to cheat if they can’t find another solution—not unlike a student who is highly motivated to earn an A and doesn’t have a terribly strong moral compass.
What are the risks?
Regardless of whether today’s models learn to reward-hack during training or adopt it as a strategy later on, the solution is the same: Make cheating unrewarding. But as models get smarter, they find more creative ways to cheat, and detecting or preventing that cheating gets far tougher. “At the end of the day, you’re sort of playing whack-a-mole,” Ladish says. “You drive this behavior down deeper and deeper. But as the model gets smarter, it gets better and better at hiding it.”
For now, reward-hacking behaviors might not cause too much trouble, despite the drama of the Hugging Face incident. “This seems like a nuisance rather than an existential threat,” says Ariana Azarbal, an AI safety research fellow at Anthropic. It doesn’t seem as if the OpenAI models caused any real harm when they hacked Hugging Face, aside from the reputational damage to OpenAI.
But that doesn’t mean reward hacking is harmless, Azarbal says. Many AI researchers hope to use AI agents to help them conduct research that will make AI safer and more reliable. If a researcher gives a reward-hacking-prone agent the goal of, say, devising a new AI training approach and then writing up a paper presenting its results, the agent might not actually do the work and might instead focus on putting together a paper that looks good enough to convince the researcher. A human researcher would probably be able to spot an agent-made fake today, but as AI advances, it will get better at this kind of trickery. Over time, the entire field of AI safety could be undermined.
And if models continue to advance as rapidly as they have recently, they could someday wreak substantial collateral damage. Just think of the philosopher Nick Bostrom’s paper-clip-maximizer thought experiment, in which an AI instructed to make as many paper clips as possible ends up consuming all the matter in the universe in pursuit of its goal. We’re not drowning in paper clips yet, but powerful systems can do real harm on the way to achieving their goals. Reward-hacking AIs don’t aim to cause chaos. But that doesn’t make them any less potentially destructive.

 Login