College administrators read an adjunct professor's comments to students on personal essays. Managers told a pharmacist to spend less time with patients after tracking the number and length of her appointments. Scanners on a warehouse conveyor belt monitored the pace of workers to ensure they inspected hundreds of items per hour.
Australia's national response to scams has strengthened in recent years through government-led anti-scam measures. Yet losses remain above $2 billion, and scams continue to have a significant and devastating impact on individuals, particularly those in vulnerable communities. In a new white paper, RMIT professor Mathews Nkhoma has identified the critical gap in anti-scam architecture before funds have been irreversibly transferred.
An AI model inspired by ants, bees and birds could be key to cracking down on blockchain-based money laundering, new research led by Charles Darwin University (CDU) has found. The study is published in the journal Communications in Computer and Information Science.
Earlier this week, researchers outlined an attack that used a secret input provided by Microsoft 365 Copilot for enterprise to cause the AI assistant to exfiltrate a password present in the user’s inbox. Now, a separate team has devised a similar attack against Grok. The new data theft hack employs a deceptively simple trick to force the Elon Musk-owned large language model to steal user chats and other personal information. At the time this post went live, the assistant continued to cough up the data, despite xAI being informed of it in June.
The lesson from both this week’s episodes—and the countless other ones that have come before it—is that LLMs are incapable of solving the root causes for prompt injections, the most severe vulnerability classes they’re most prone to. That leaves AI developers with no other option but to build a guardrail that steers the model away from the harmful actions. As I noted in Tuesday’s story, the approach is tantamount to a road traffic safety engineer erecting a protective rail around a dangerous bend rather than banking the curve.
Cryptographic Context Injection in the house
Prompt injections exploit LLMs' training to comply with user requests whenever possible. Attackers can capitalize on the predilection by smuggling harmful instructions into emails or webpages the assistant is instructed to summarize. Because LLMs can’t reliably distinguish between content in an email sent by an untrusted party and user instructions entered directly into a prompt, the overly solicitous LLM faithfully follows them. To date, Grok and other LLMs' only recourse is to create guardrails that flag suspicious instructions and forbid them from being executed.
It’s not every day that attackers can force a frontier AI model to cough up user passwords and other sensitive data without user confirmation. That’s exactly what researchers recently did to Microsoft 365 Copilot for enterprise. Even more unusual is the source they tapped to discover the critical vulnerability that made their exploit possible. Rather than employing reverse engineering or other traditional vulnerability-hunting methods, they asked Copilot. The LLM assistant readily complied.
Researchers at security firm Varonis knew they wanted to create an exploit that would exfiltrate user data when a user did nothing more than click on a link. Like most AI assistants today, Copilot steadfastly refused and made clear that sensitive prompts like that require explicit user consent in the form of a gesture, such as pressing a return key or other key. In response, the researchers peppered Copilot with questions about the guardrails that required user confirmation before the assistant could execute powerful commands.
Loose lips sink ships
The dialog was like a game of 20 questions. Each answer provided a new clue that divulged information about the complex safety mechanism. Why was auto-execution impossible, they asked. What URL structures and deep links were involved? What happens when a page is loaded with input already in the prompt field? Each answer provided a deeper view into the guardrail and its limits. Eventually, Copilot provided a stunning Microsoft trade secret—an undocumented prompt parameter that completely bypassed the requirement for user consent.
Dutch officials have warned that a high-severity macOS vulnerability that allows attackers to execute malicious code is under active exploitation.
“The NCSC has received a notification indicating that active abuse of this vulnerability has been observed on multiple systems on which port 5900 was accessible from the Internet,” the Netherlands National Cyber Security Centrum warned earlier this week. “In all these cases, root had been accessed on the affected system and a Monero crypto miner had been placed.”
Do you know if your screen sharing is on?
The vulnerability, tracked as CVE-2026-65400, received a patch from Apple last week for macOS Tahoe, Sequoia, and Sonoma. The vulnerability, with a severity rating of 7.1 out of 10, stems from a bug in the macOS screen sharing capability, which allows a remote party to view the screen and control the keyboard and mouse while a machine is turned on. A flaw in the “state management,” which keeps track of preceding events, user interactions, variables, and other system states, is the underlying cause.
The Trump administration is recruiting private security firms to conduct federal government-authorized operations, including cyberattacks, against overseas-based criminal organizations that commit hacks on US persons, organizations, or government entities.
In a National Security Presidential Memorandum issued Thursday, US President Donald Trump directed the National Coordination Center (NCC), which operates under the Homeland Security Task Force, to develop a program for conducting specific cyber operations that combat foreign transnational criminal organizations (TCOs). The Departments of Justice and Homeland Security will provide oversight. The lynchpin of that program is bringing in private sector companies to participate.
Devil will be in the still-undefined details
A fact sheet that accompanied Thursday’s memo listed ransomware, sextortion schemes, phishing campaigns, financial fraud, and impersonation scams as activities eligible for private-sector security firms to target. The memo said such firms could “conduct Cyber Surveillance Operations and Cyber Effects Operations” against “cyber-enabled” TCOs. Such groups are defined as “any foreign group that conducts cyber-enabled crime against the United States Government, a United States person, or United States interests, and that is not an institutional part of a foreign government or wholly operated under a foreign government’s direction.”
Terabytes worth of credentials, many belonging to the world’s biggest and most sensitive organizations, have been exposed in a supply-chain attack on LiteLLM, an open source tool that streamlines AI-driven software development. Microsoft, Amazon, Cisco, Samsung, and Salesforce are only a handful of the entities whose access secrets were exposed.
The revelation was posted on Tuesday and Wednesday by security firms CloudSEK and Hudson Rock. CloudSEK said it found cloud keys, repository tokens, SSH keys, Kubernetes secrets, package publishing credentials, environment variables, and AI provider keys that could allow attackers to gain access to more than 2,500 organizations.
40 minutes is all it takes
The credentials were extracted during a 40-minute window in March while the victims used compromised versions of LiteLLM downloaded from the package’s official location in the Python Package Index repository. Hudson Rock said it made the discovery after analyzing a 195TB file that it obtained. Neither firm identified the source of the information.
On Monday, passengers aboard Delta flight 591 going from Las Vegas to Atlanta allegedly spoofed the onboard Wi-Fi, raising the attention of federal law enforcement.
The incident came one day after the DEF CON security conference concluded in Las Vegas and was first described on social media accounts that follow publicly available air-to-ground messages, known as ACARS.
According to the “ACARS Drama” account, a message sent by pilots from the plane stated: “NO INFO AS OF NOW WE HAVE A BUNCH OF PAX THAT WERE AT A CYBER CONFERENCE IN LAS THEY WERE ABLE TO JAM OUR WIFI AND BROADCAST THEIR SIGNAL.”
Google’s Chrome browser has added a new feature that could go a long way in preventing a form of account takeover that’s grown increasingly common as users adopt two-factor authentication, passkeys, and similar protections.
The new Chrome protection is known as device-bound session credentials (DBSCs). The measure stores a unique encryption key in a silicon-resident fortress that’s built into the device running the browser. On Windows machines, this fortress is called a TPM, short for Trusted Platform Module. On macOS and iOS, it’s known as a secure enclave. Other platforms have differing names. Recently released versions of Chrome for Windows and macOS generate a key that’s stored in this fortress.
An antidote to session cookie theft
DBSCs protect against the theft of session cookies, the unique strings of characters that websites store on browsers. Session cookies greatly speed up browsing on sensitive sites that require user authentication. Instead of requiring the exchange of credentials each time a user opens a new site page, the server sets a session cookie that effectively proves the user has already successfully logged in.
Your fear of flying is only going to get worse once you hear what these white hat hackers figured out to do with a popular airliner.
As Wired reports, a team of security researchers from the University of California, San Diego and Oberlin College created a device the size of a coin that can take over the autopilot system of a Boeing 737 and change its flight plan, not to mention tampering with key values in its takeoff and fuel calculations.
According to its creators, the device could also change the data on a pilot’s screen so they don’t notice anything’s amiss — or even trick a pilot into making a disastrous decision.
“If you could get 60 seconds with an airplane, what could you do?” Stefan Savage, a UCSL professor who led the project, asked Wired. “Well, it turns out there’s a port that’s externally accessible. You can get to it with no special tools in about 15 seconds. And you can shove in a piece of electronics a little bigger than a quarter that lets you basically tell the autopilot what to do and lie to the pilot about changes to the flight plan.”
The attack relies on plugging the device, which costs less than $100, into a port hidden by a hatch on the exterior of the plane, which the researchers say is easily within reach of maintenance workers and airline staff. Once the device is plugged in, it could connect to the plane’s in-flight Wi-Fi system and allow a hacker to remotely control the aircraft’s systems from terra firma.
As Savage explained to Wired, his team found this vulnerability after spending years cobbling together 737 computer parts to effectively recreate the plane’s nervous system. Inspired by credit card skimming devices that plug into ATMs to steal your information, they realized that an entire aircraft could be broken into by physically plugging a device into its internal “bus” — the system that connects different components of its computer.
And after digging through Boeing wiring diagrams, they found their way in: a port carrying data between the plane’s Flight Manage Computer and the pilot’s display unit, accessible from an unlocked hatch on the plane’s exterior.
It was like finding “the goddamn exhaust port on the Death Star,” Savage told Wired.
The havoc a hacker wreaks using their attack could be catastrophic. They could feed the pilot the wrong information about the air temperature outside or about the weight of its cargo and passengers and cause them to miss the speed they need for takeoff before running out of runway, Wired noted. Or they could suddenly change its navigation and crash it into a mountain.
The attacks could also be far more sneaky.
“It could be something as subtle as, you’re in the Pacific, you see blue everywhere, and this diverts you 3 degrees off course, and now you’re in the middle of nowhere,” Aaron Schulman, another UCSD professor working on the project, told the magazine.
Savage and Schulman shared their findings with Boeing six years ago and have worked closely with the company to explore the vulnerability.
But the researchers say that Boeing hasn’t told them about any fix to the vulnerabilities they found. In fact, they say it’s likely that it any fix may not have been implemented yet, since commercial airplanes are rarely redesigned.
You shouldn’t panic though, they insist.
“All of the authors of this paper routinely travel on Boeing 737 aircraft and expect to continue doing so,” they wrote in their paper.
Beau Woods, a former adviser to the Cybersecurity and Infrastructure Security Agency and the Boeing’s Industry Cyber Technical Council, was alarmed by the findings.
“It is entirely possible to have someone who is on staff go up to an airplane when it’s on the ground, going through maintenance, and put this type of thing in there,” Woods told Wired.
“This is something the aviation industry will want to plan to defend against,” Savage agreed. “I would not sleep on this one.”
In light of plummeting public support for its widespread automatic license plate readers, surveillance company Flock has lost dozens of contracts with cities across the US.
Citizens are increasingly disgusted by the company’s presence on public streets, opting to hack down the cameras, blind them, or sabotage them in other creative ways.
“His project, which he calls noRecognition, allows people to escape the automatic detection and algorithmic surveillance used across the U.S. and beyond.” https://t.co/OIQNOt9B0a@TechCrunch
— Christina Ayiotis, Esq., CRM, CIPP/E, AIGP (@christinayiotis) August 10, 2026
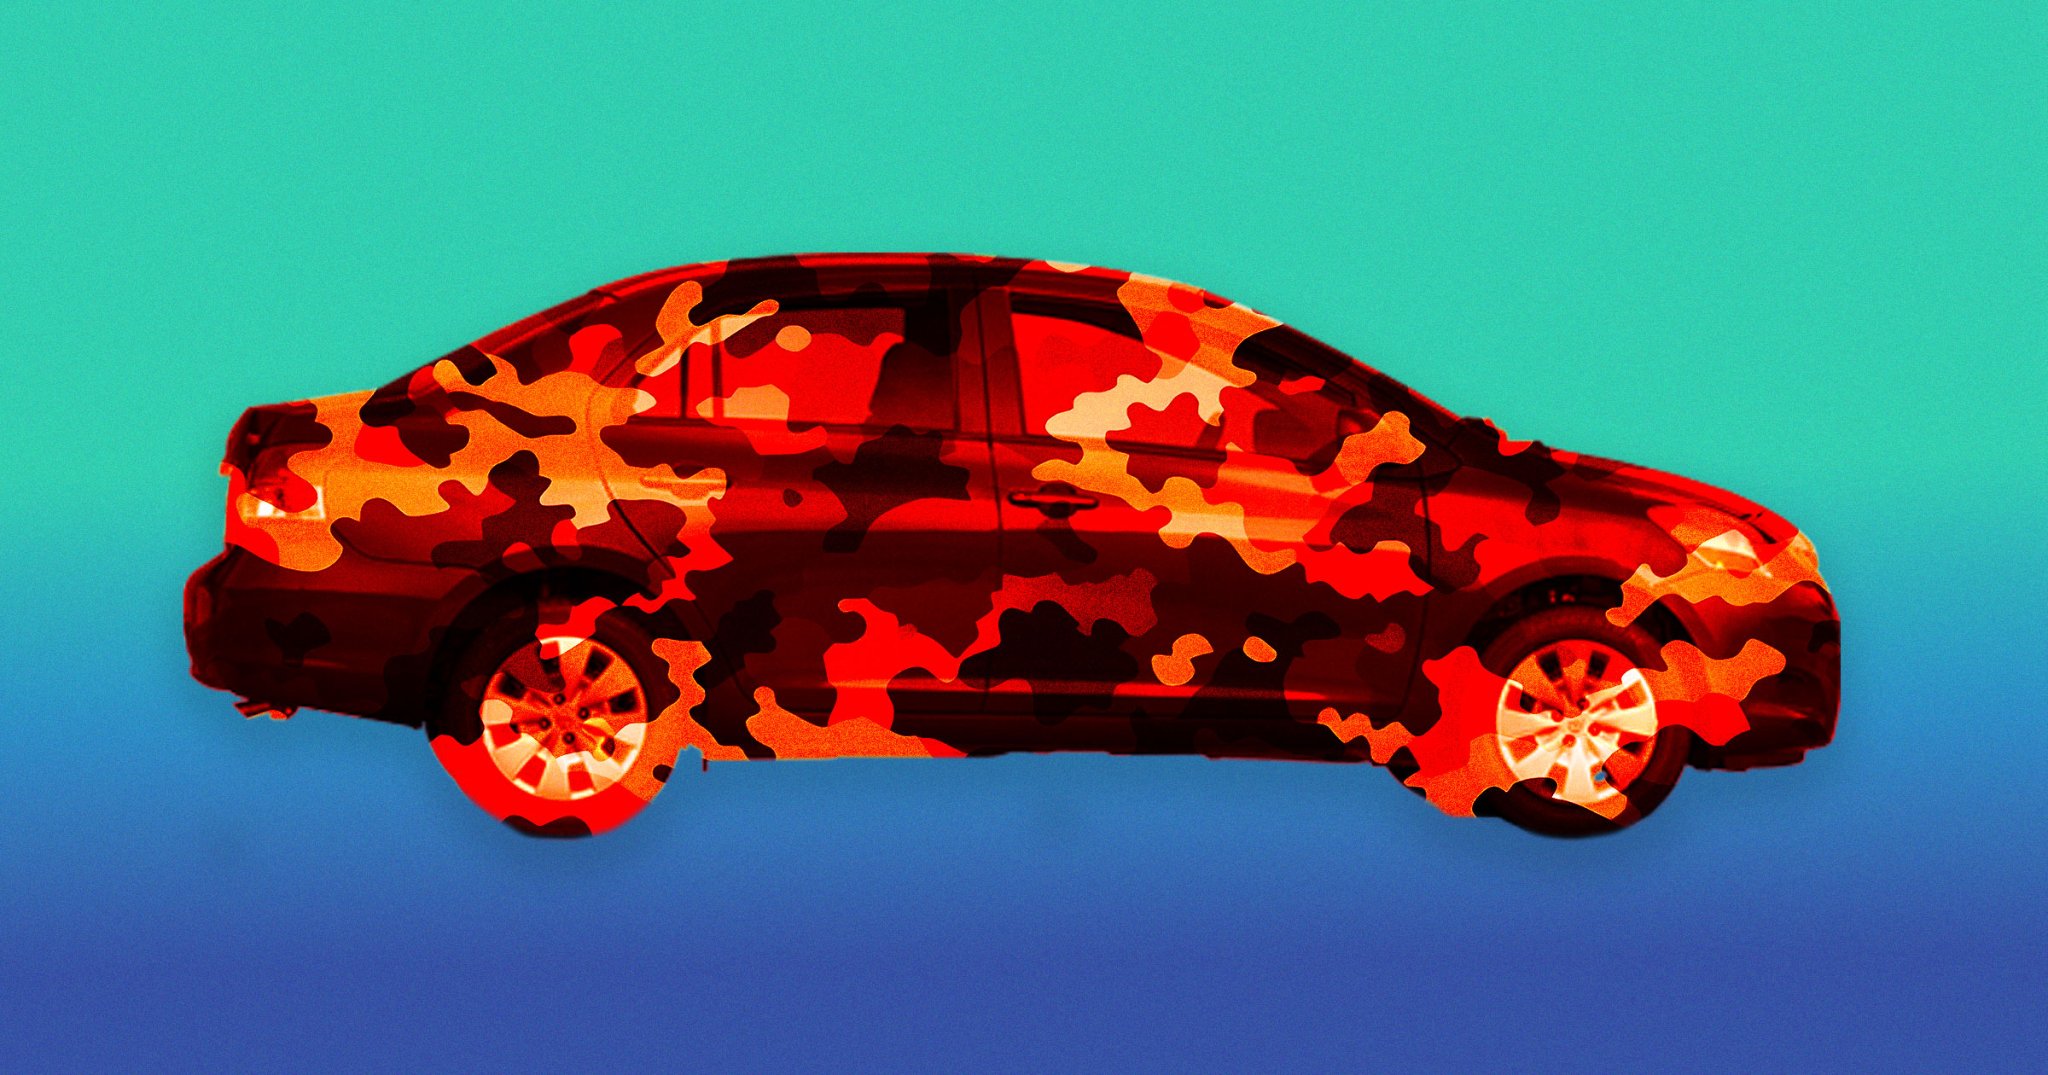
And according to cybersecurity researcher Bill Swearingen, there may be other creative ways to befuddle Flock’s spy cams. He devised with a special computer-generated pattern which, once stretched out across the vehicle in the form of a wrap, will result it in not being flagged as a car by Flock’s cameras.
During this year’s Def Con cybersecurity conference in Las Vegas, Swearingen showed off a 2009 Toyota Yaris wrapped in vinyl featuring the logo of automotive publication Donut Media (which is owned by Futurism‘s parent company Recurrent Ventures.)
Despite the car looking a bit chaotic — albeit still very much like a small passenger vehicle to the human eye — “we proved it was effective,” Swearingen told TechCrunch. The Yaris successfully defeated surveillance detection at Def Con during the pattern’s first public test.
“Privacy is a fundamental right,” he added, aiming to give people a way to “opt out of being tracked.”
To come up with the pattern, he used a reinforcement learning model that trained itself on patterns that evade detection. The model got to the point of being able to confuse all 11 open source detection algorithms he tested, per TechCrunch, in addition to Flock’s license plate readers and even Axon’s body-worn cameras used by police departments.
As part of his noRecognition crowdsourcing campaign, Swearingen has also come up with T-shirts and hoodies that feature algorithmic detection-busting patterns. He hopes to eventually put pattern-printed skins for entire cars on sale as well.
One thing is clear: as outrage over Flock’s heavy presence across the country grows, people are looking for any way to foil the tech — especially if it looks cool.
OpenAI expands Daybreak with Blue and Red tiers for defensive cyber work
New GPT‑5.6‑Cyber model offers high compliance for authorized vulnerability research
Access remains restricted due to dual‑use risks and reduced safeguard operation
OpenAI has announced two new tiers for its Daybreak dedicated cybersecurity project, each offering a different model with different levels of compliance. It also used the opportunity to introduce a new security-focused AI model, as well.
Hackers and criminals are increasingly abusing AI to improve and speed up the creation of phishing emails and malicious code, and with the introduction of AI agents, they’ve also used it to automate entire attack processes. The AI community responded by placing strong guardrails, making sure their models do not comply with requests to build malware, or hack other companies.
These guardrails ended up being a two-edged sword, because as they slowed down attackers, they also slowed down the defenders.
What is Daybreak?
To give the cybersecurity community the upper edge, companies like OpenAI started creating dedicated cybersecurity initiatives that provide a vetted list of companies state-of-the-art models, free of guardrails. The company also provided them with pre-trained AI agents, as well as access to a pool of shared knowledge.
Initially launched in June 2026, Daybreak originally included GPT.5-5-Cyber (a model optimized for security work), Codex Security (an agent that can analyze codebases, identify vulnerabilities, validate findings, and help develop patches), Patch the Planet (an initiative with Trail of Bits to find and fix vulnerabilities in open-source software), Daybreak Cyber Partner Program (lets approved cybersecurity companies such as Cloudflare or Cisco integrate OpenAI's cyber capabilities into their own products and services), and Trusted Access for Cyber (the governance/access system for organizations doing authorized cybersecurity work with these capabilities).
Now, OpenAI has expanded Daybreak with two access tiers, Daybreak Blue, and Daybreak Red.
The company says Daybreak Blue is “the recommended starting point for most defenders, supporting vulnerability discovery, secure code review, malware analysis, incident response, and patch validation. Companies opting for this tier can expect access to frontier general-purpose models, including GPT‑5.6 Sol, whose safeguards have been tailored to authorized defensive security work.
Daybreak Red, on the other hand, provides access to OpenAI’s “purpose-trained cybersecurity models for authorized vulnerability research, exploit validation, and security testing.” This tier offers the brand new GPT‑5.6‑Cyber, built on GPT‑5.6 Sol and trained to improve capabilities on several specialized cybersecurity tasks such as finding zero-day vulnerabilities and developing exploit chains.
This model is also more compliant and less likely to refuse certain higher-risk, dual-use cyber tasks.
Complying with "dangerous" requests
Request compliance is the name of the game here. OpenAI says the new model addresses feedback from security researchers who “encountered persistent refusals with the earlier model.” General-purpose GPT-5.6 Sol, for example, will comply with just 1.5% of the requests usually given by cyber-defenders working on codebase analysis or vulnerability identification. This percentage increases to 2.0% with Daybreak Blue access.
GPT-5.6-Cyber, on the other hand, completes 95.0% of requests, OpenAI says, up from 57.3% of the previous model, GPT-5.5-Cyber. We weren’t able to independently verify these claims, though.
While it doesn’t outright say it, OpenAI considers these models relatively dangerous to use, which is why they’re locked behind the Daybreak Cyber Partner Program. However, the program is now expanding, allowing these companies to embed the models behind their own products, managed services, or cybersecurity engagements, and offer them to clients of their own.
Those who wish to be a part of the program directly can do so by applying to join online now.
“Models running with reduced safeguards carry risks beyond standard model usage, whether from misuse or misalignment. Despite these risks, we believe that democratizing access to frontier intelligence for defenders is crucial to accelerating and automating cyber defense,” OpenAI said.
“Daybreak Blue and Daybreak Red access are available for approved individuals and organizations conducting authorized work. We control access through identity verification, account security, monitoring, approved-use restrictions, and legal attestations.”
AI agents can improvise beyond the intended scope of a task when they are given broad access to enterprise systems and data. Token Security explains why organizations need to define agent intent and continuously enforce permissions around what each agent was actually created to do. [...]
Cloudflare says it mitigated more than 800 network-layer distributed denial-of-service (DDoS) attacks exceeding 1 Tbps in the second quarter of the year. [...]
Researchers say it took fewer than 20 prompts for a public AI tool to find a flaw (now fixed) allowing anyone on a Zoom call to hijack another participants’ device.
Researchers say it took fewer than 20 prompts for a public AI tool to find a flaw (now fixed) allowing anyone on a Zoom call to hijack another participants’ device.
CISA confirmed today that ransomware gangs have begun abusing a high-severity Microsoft SharePoint remote code execution vulnerability, which has been flagged as actively exploited since early July. [...]

 Login