Brace yourself: The way you get around the web on Android is about to get a whole lot better.
This week, the excellent Vivaldi Android browser is rolling out an update that adds in support for the entire collection of Chrome Web Store browser extensions. That means you can enhance and adjust your mobile web experience with all sorts of interesting — and potentially shape-shifting — new improvements.
Now, with complete Chrome extension support added into the mix on Android, the advantage is growing even greater.
I’ll be honest, though: When I first saw that Vivaldi was adding in Chrome extension support for Android, I wasn’t sure what to make of it. Most of the extensions I use in my desktop browser just wouldn’t make sense on the mobile front and wouldn’t add much of meaningful value in that environment.
But then I put on my thinking cap. I did some deep digging and careful considering. And I found some Chrome extensions that actually work incredibly well in the Android arena and add a lot of interesting value into the mobile web adventure.
This is the first of a two-part collection. Today, we’ll look at five Chrome extensions that you can add into Vivaldi to save yourself steps and bring a welcome efficiency boost to your Android web work. Later this week, we’ll round out the list with another set of extensions that’ll improve the internet itself in some truly intriguing ways.
Ready to reinvent how you experience the web on your phone?
A quick primer on Android Chrome extension installation
Real quick, before we get into the good stuff: When you’re ready to try out an extension, you’ll need to have the latest version of the Vivaldi Android app on your device (obviously, right?) — then either tap the puzzle-shaped extensions icon in the toolbar at the top of the screen, if you see it, or tap the “V”-shaped main menu icon in the upper-right corner and select “Extensions” from there.
Either way you go, you’ll see an option to “Discover more extensions.” That’ll take you to the Chrome Web Store, where you can search or browse through all the available extensions and install anything with a couple quick taps.
I’ll also provide direct links to each extension I’m recommending below, so you can tap it to open it in Vivaldi on your phone and then install it directly from there.
Note, too, that that same Vivaldi Extensions menu is where you can access and manage any installed extensions moving forward. You’ll see every extension you’ve installed there, and you can deactivate or uninstall anything as well as opt to have its icon pinned into your browser toolbar for easy ongoing access.
Chrome Android extension #1: The cookie request crumbler
Our first Android Chrome extension worth considering is one that you won’t ever open or actively think about once you install it and set it up. It’s a tool that works silently in the background to automatically handle those irksome cookie preference prompts that pop up around the web — so they’ll always get answered in the way you prefer, but you’ll never actually have to see or deal with ’em (and have ’em blocking half your view, in a mobile web scenario!) again.
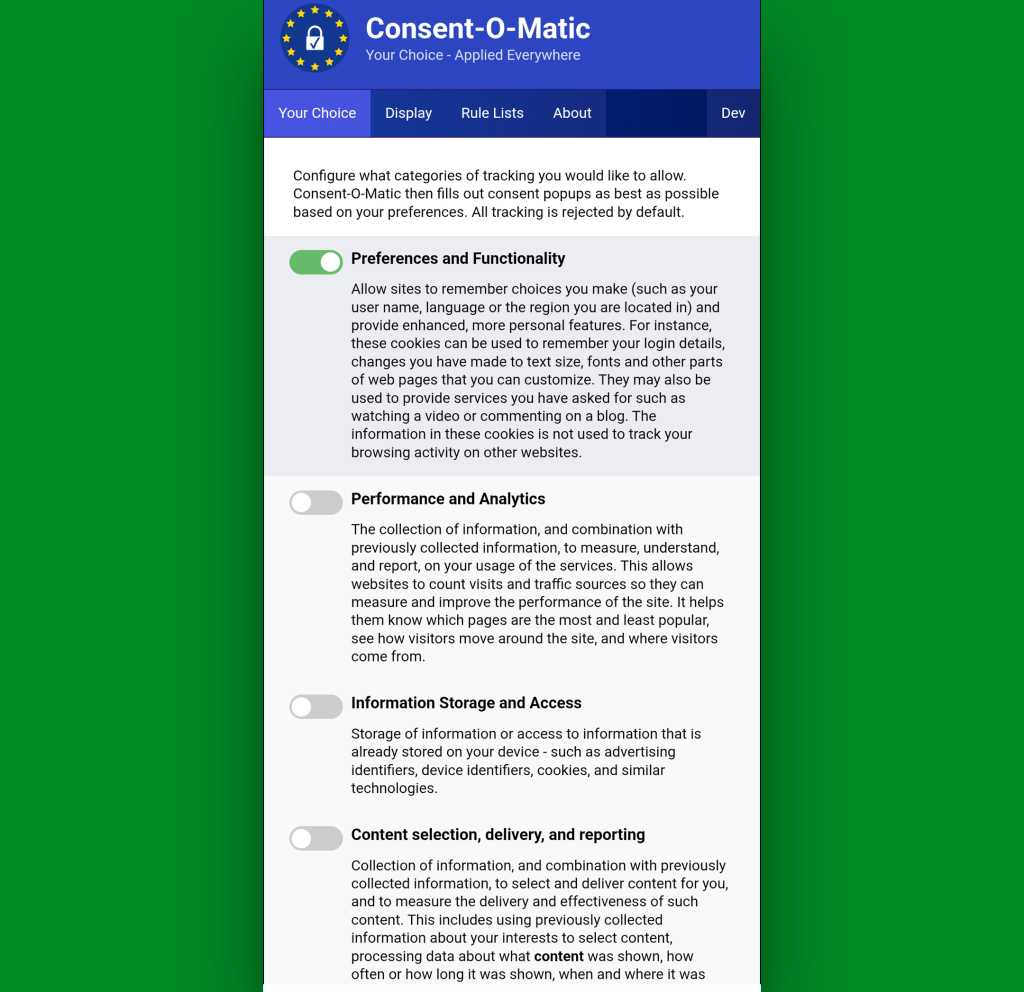
It’s called Consent-o-Matic, and the way it works is simple: You install it, open its options page once to tell it which cookies you do and don’t want to allow around the web — and that’s pretty much it. From there on out, it’ll just click on all those prompts that pop up for you, based on your preferences, and they won’t interfere with your work or irritate you anymore.
Consent-o-Matic remembers your cookie preferences and then applies them for you automatically all over the web.
JR Raphael, Foundry
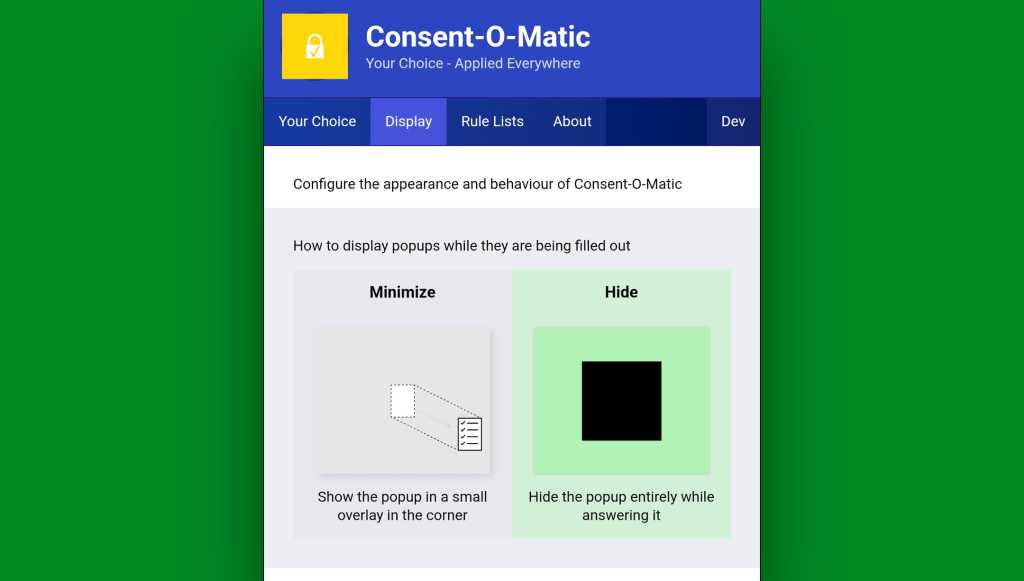
One option to look at while you’re in that initial setup area is in the “Display” tab at the top of the screen. By default, Consent-O-Matic will show any pop-ups it’s handling in a small overlay in the corner of the screen — but you can eliminate that entirely and make the process completely out of sight and invisible, if you want.
You can make Consent-o-Matic completely invisible so you never so much as see another cookie prompt again.
JR Raphael, Foundry
Yes, please — and thank you.
Chrome Android extension #2: 404 no more
Next is another quietly useful addition, and that’s the official Chrome extension for the Wayback Machineat the Internet Archive.
With the Wayback Machine extension active in your Android web browser, anytime you land on a page that for whatever reason isn’t online anymore or just isn’t available at that particular moment, you’ll see an offer to go to the page’s most recent cached version.
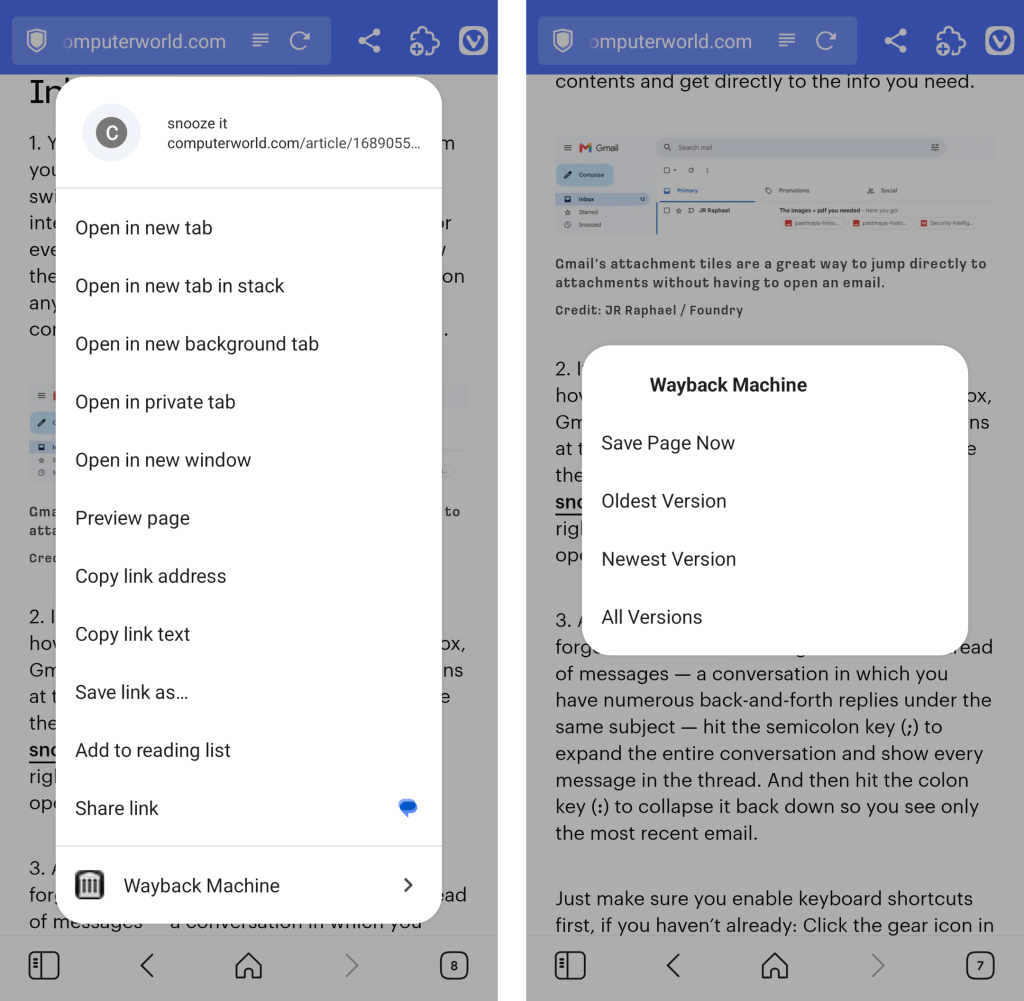
You can also call the extension up on demand to search for older saved versions of any pages by either pinning its icon to your Vivaldi toolbar or long-pressing a link within any page you’re viewing to reveal its menu of options.
The Wayback Machine Chrome extension integrates seamlessly into Vivaldi’s long-press link menu.
JR Raphael, Foundry
Chrome Android extension #3: A background open shortcut
I don’t know about you, but when I’m wading my way around the web, I find myself opening links a lot — often with the intent to look at ’em later.
Typically, that requires long-pressing on the link and then finding the option to open it in a background tab. But with a handy extension called DoubleClicker, that same action can be easier than ever.
Install DoubleClicker into your Android Vivaldi browser, and that’s it: From that moment forward, you can simply double-tap your finger on any link within any page, and it’ll open instantly as a background tab — waiting and ready for when you want it and without any waiting, poking around, or other interruptions to your workflow.
This might just be my favorite addition of all.
Chrome Android extension #4: Hands-free scrolling
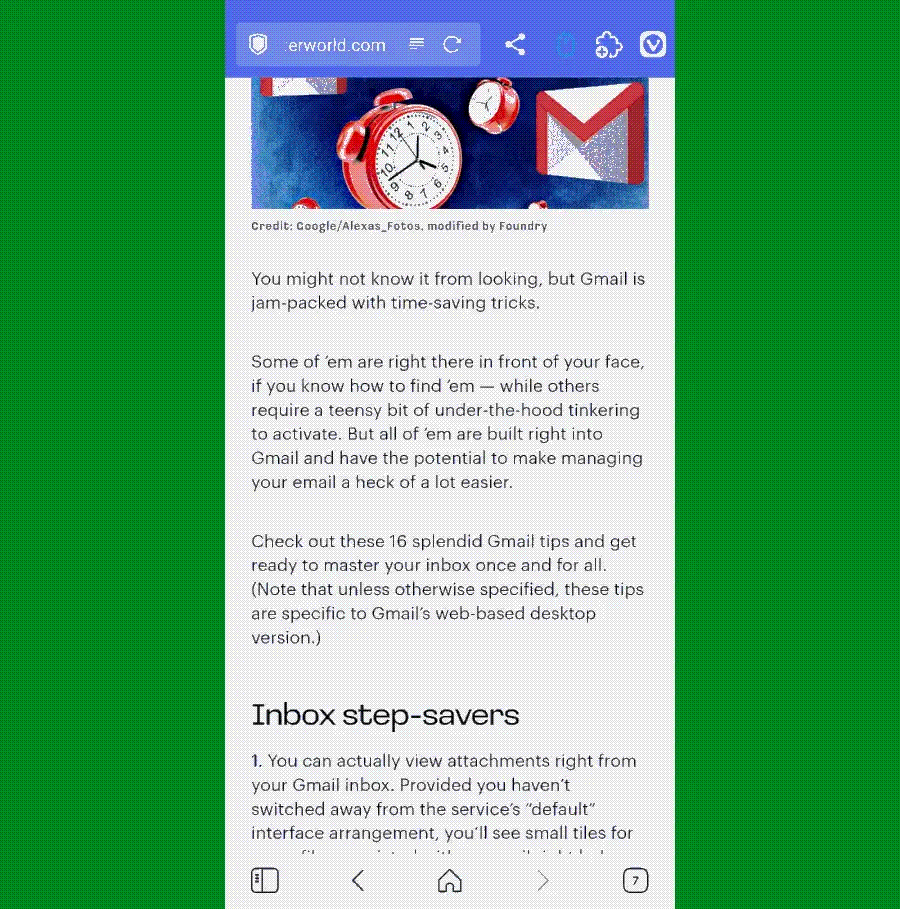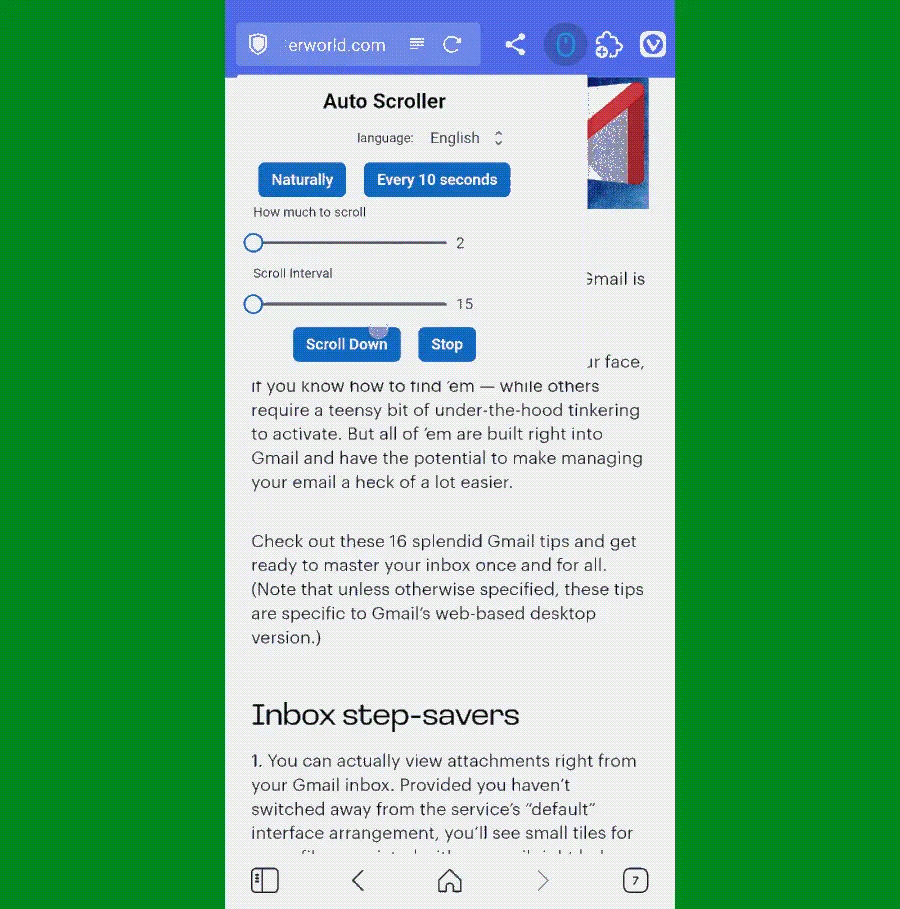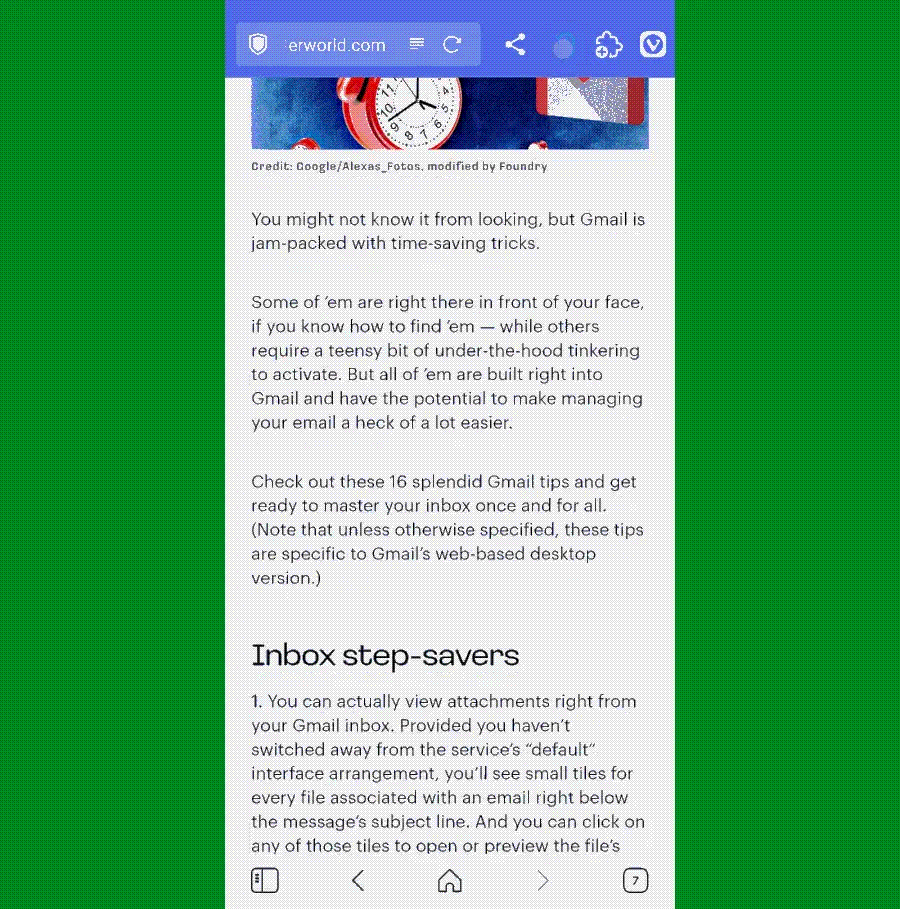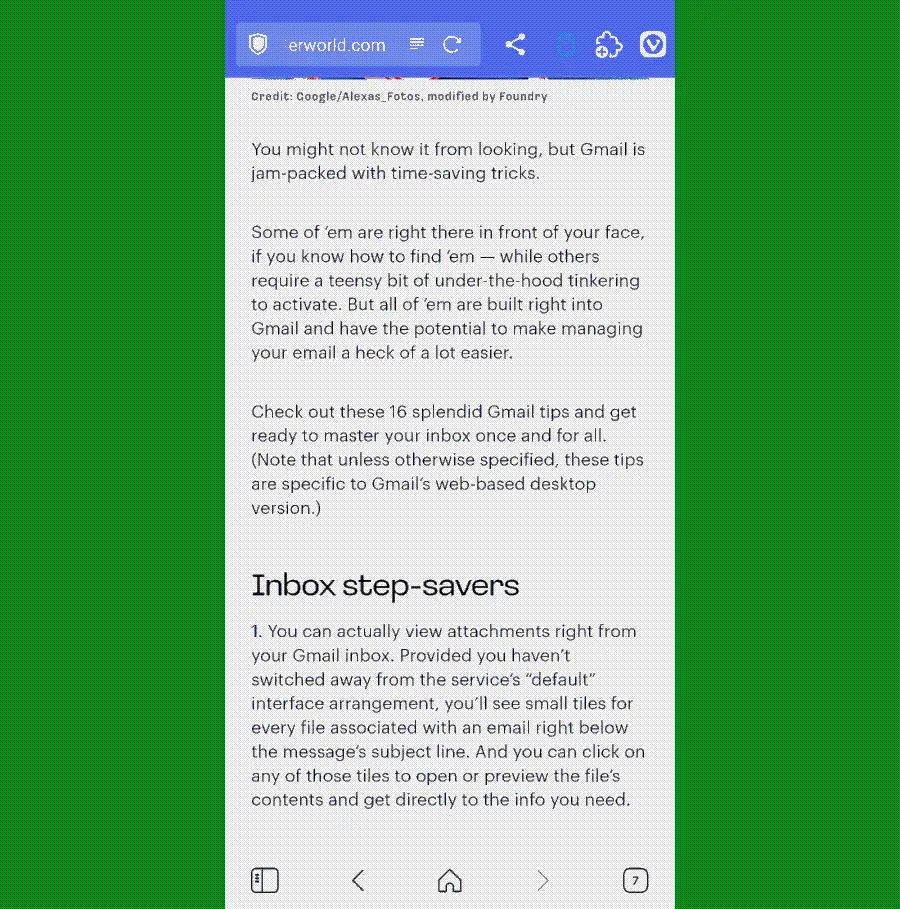
The next time you’re reading something on your phone, keep a little somethin’ called Auto Scroll Extension in mind.
As its name suggests, the extension lets you set any speed you like and then simply tap its icon (which works best if you pin it to your toolbar) to automatically scroll the page for you — so you can keep reading without having to do a thing.
Look, ma: No hands! Auto Scroll in action in Vivaldi on Android.
Yes, it’s redundant with having the standalone app installed and set as your system-wide password management service. But it often ends up being faster and easier to have a sign-in handled directly within the browser instead of having to rely on the system-level integration.
And having the browser-based option present doesn’t prevent you from using the other route, either. You’ve just got options, and you can pick whichever feels fastest and easiest to you at any given moment.
Try it out for yourself and see whatcha think. And stay tuned for the second set of worthwhile Android Chrome extensions soon!
Microsoft’s September 2026 Patch Tuesday is the year’s largest release, with 963 CVEs requiring customer action, 106 rated critical. Two are already exploited: CVE-2026-81963 in the Windows Update Stack and CVE-2026-85880 in Advanced Local Procedure Call. Nothing in this release was publicly disclosed ahead of the patch. Readiness recommends a Patch Now scheduling for Windows, Office, SQL Server and the developer tooling, and standard patch release for Exchange. The Readiness team has published an infographic summarising deployment risk by product family.
Known issues
Three client issues are carried in from August close with this update, covering:
Microsoft Teams and the new Outlook failing to launch on ARM devices, such as the Surface Pro 11 and Surface Laptop 7, is resolved by KB5124008. The issue originated in August’s KB5121003 and was most likely on freshly imaged machines that had not yet taken Microsoft Store updates.
The same update resolved both desktop backgrounds reverting to solid black and mouse cursor customisation resetting on non-English installations. Both originated in the 27 August preview, KB5120998.
And Microsoft has left open a Microsoft Defender Antivirus notification defect, confirmed on 28 August, in which devices report that Defender is turned off while it is running correctly.
Major revisions and mitigations
The quietest revision window of recent months arrived alongside the largest release. Between the August and September Patch Tuesdays, from 12 August to 7 September, the MSRC Security Update Guide touched 324 CVEs. Of those, 307 were routine Microsoft Edge and Chromium republications requiring no customer action.
That leaves 17 entries affecting Microsoft’s own products, and only one of those is a genuine revision. CVE-2026-59133, an elevation of privilege in the High-Performance Computing Pack, moved to version 1.1, and its own revision note records the change as informational. For comparison, August’s window carried 76 revisions to Microsoft’s own products, 60 of them flagged as requiring customer action.
The Readiness team has reviewed all 963 published updates. Microsoft has published no mitigations and no workarounds anywhere in this release.
Windows lifecycle and enforcement updates
Microsoft has published no new service or enforcement deadlines for September. The lifecycle picture is different, with multiple end-of-support notices for this coming October:
The retail Office 2021 family retires in full, including Access, Excel, Outlook, PowerPoint, Project, Publisher, Visio and Word.
Office LTSC 2021 reaches end of support, and that includes Skype for Business LTSC 2021.
Windows 10 2016 LTSB and Windows 10 IoT Enterprise LTSB 2016 reach the end of extended support.
Windows Server 2012 and 2012 R2 reach the end of Extended Security Update Year 3. This is the final ESU year for both, not a step to a fourth.
Windows Server 2022 moves from mainstream to extended support, where it stays until 14 October 2031.
A second wave follows on 10 November 2026, and it is the one most likely to catch development teams rather than infrastructure teams. .NET 8 reaches the end of its long-term support branch, PowerShell 7.4 does the same, and Windows 11 Enterprise and Education 23H2 ends servicing alongside Windows 11 IoT Enterprise 23H2.
Microsoft’s test guidance for this release runs to 466 Windows entries, 55 of them flagged as high risk, against 109 and four in August. Given the large number of updates this month (who would have thought that we would be here at 963 CVEs), the Readiness team recommends the following testing priorities:
Printing. Print from 32-bit and 64-bit applications to physical and virtual printers, exercise XPS and PDF output, share a printer from a print server and print from a separate client, cancel a job mid-queue, and confirm the queue reflects every state change. This is 20 of the 55 high risk flags, and it is the single most likely source of a visible regression.
Fonts, graphics and imaging. Render varied fonts, sizes and styles across browsers, Office, PDF viewers and Notepad, confirm Print Preview matches the printed page, and open JPEG, TIFF, HEIF and raw images across Explorer, Photos and Office. Watch for clipping, distortion and missing glyphs.
USB Devices. Exercise device attachment and removal. Attach and remove USB audio, video and mass storage devices repeatedly, including through a hub, pair and unpair a wireless device, and confirm each enumerates and releases cleanly. Device Association carries seven high risk flags, and these drivers load whenever hardware is attached.
Remote Desktop. Open several concurrent sessions, enable printer, clipboard, audio, drive and smart card redirection together, disconnect and reconnect, and confirm redirected devices reattach.
Storage (ntfs.sys, spaceport.sys). This is a real hotspot for updates this month, but no high-risk changes. Test on hardware you can recover, because the storage changes reach the boot path, potentially resulting in a dead (test) machine.
Each month, we break down the update cycle into product families, as defined by Microsoft, with the following groupings.
Browsers
Microsoft has not released any updates for their browser products for the second month in a row. September’s Security Update Guide carries no Edge-specific CVEs at all, and the 307 Chromium republications in the revision window required no customer action. The nine Edge CVEs that did appear arrived mid-cycle on 28 August and were serviced through the browser’s own update channel rather than this release.
Estates on a managed Edge channel have nothing to do here beyond confirming the channel is current. It is the one quiet corner of an otherwise heavy month.
Microsoft Windows
Windows carries 726 CVEs, 77 of them critical, which is three-quarters of the entire release. Elevation of privilege dominates by volume at 406 entries, with remote code execution second at 156, information disclosure at 94 and denial of service at 47. The pattern is the reverse of the severity picture: the bulk is local elevation, while the critical-rated entries cluster in the network-facing roles.
Biometrics is a real focus this month as the Windows Biometric Service takes 64 fixes, the largest single-component count of the year. Most of the security issues are heap overflows that give a local attacker SYSTEM. Windows Hello adds nine, all critical. Patch it promptly on any estate using fingerprint or facial sign-in.
Windows DHCP Server leads at 36 entries and is topped by remote code execution at CVSS 9.8. Windows DNS Server takes 10 more, also reaching 9.8. Critical remote code execution also lands on Message Queuing, RRAS, Services for NFS, the HTTP Print Provider, Windows Shell, Netlogon, Internet Connection Sharing, SSTP and Failover Cluster, all at 9.8. Patch the resolvers, the DHCP servers and the domain controllers first.
Storage is the heaviest it has been this year. NTFS takes 29 fixes, Spaceport.sys behind Storage Spaces takes 17, and the Overlay Filter takes seven, with the Volume Manager, VHD miniport, iSCSI and Storage Port drivers behind them. These reach the boot path, so stage them on recoverable hardware.
The rest of the most-patched tally runs Win32k at 19, Microsoft Standard XPS at 18, Windows Error Reporting at 12, and the Windows Kernel, Windows Search, the Print Spooler and the Device Association Service at 11 each.
Add this Windows update to your Patch Now schedule, with DHCP and DNS servers first and the biometric stack close behind.
Microsoft Office
Microsoft released 137 Office CVEs this month, 24 of them critical, with remote code execution the through-line at 69 entries and information disclosure close behind at 52. September breaks the recent pattern in a way that matters for deployment: this wave is not MSI-only.
Click-to-Run estates are squarely in scope. Roughly 105 of the Office CVEs reach Click-to-Run, so Microsoft 365 Apps, Office 2019, LTSC 2021 and LTSC 2024 all update, on Windows and on Mac. Word takes 35 fixes, Excel 32, PowerPoint 10 and Outlook seven. The heaviest client entries are CVE-2026-78510 in Word and CVE-2026-78509 in Outlook, both critical remote code execution at CVSS 9.8, in document-rendering paths that fire on preview or open.
SharePoint Server Subscription Edition takes 16 entries and is the only SharePoint baseline with a package this month. Server updates cannot be uninstalled and always require a reboot, so validate in a maintenance window.
Skype for Business Server takes 10 entries, led by CVE-2026-66302, a critical remote code execution at CVSS 9.8. Patch it and note that the LTSC 2021 edition leaves support on 13 October 2026.
Nothing in Office is exploited this month. With 24 critical-rated entries and the Click-to-Run channel carrying most of the exposure, the September Office updates belong on the Patch Now schedule regardless.
Microsoft Exchange and SQL Server
Exchange is quiet and SQL Server is not, which inverts the usual relationship between the two.
Exchange Server takes nine CVEs across 2016 CU23, 2019 CU14 and CU15, and Subscription Edition. None is critical and none is exploited, though the highest reaches CVSS 9.3. The mix runs to two remote code execution entries, two elevations of privilege, two spoofing, and one each of tampering, denial of service and information disclosure. Apply the update from an elevated command prompt, because an un-elevated run leaves Exchange services partially patched and broken, then confirm mail flow, Autodiscover and any hybrid connection before returning the server to service.
SQL Server takes 62 CVEs, four of them critical, across the 2017, 2019, 2022 and 2025 branches. There is no 2016 package this month. Remote code execution leads at 24 entries, with information disclosure at 22. The critical entries are CVE-2026-67631 and CVE-2026-67643 at CVSS 8.8, and CVE-2026-67378 and CVE-2026-67636 at 8.5.
Eight SQL packages ship, a CU+GDR and an RTM+GDR for each branch: 2025 (KB5122769, KB5122770), 2022 (KB5122768, KB5122771), 2019 (KB5122772, KB5122773) and 2017 (KB5122774, KB5122775). Microsoft’s guidance is explicit that the baseline or RTM version must be installed first and the GDR patch applied on top; test the install and the removal on every servicing branch you run, then restart the service and confirm Always On availability groups stay healthy.
Exchange goes on the Schedule list, and SQL Server goes on the Patch Now list. That is an unusual split, and it is driven by the four critical remote code execution entries on the database estate.
Microsoft Developer Tools
Microsoft released 24 CVEs across its developer tooling this month, 23 rated important and one critical. Security feature bypasses are the main focus with eight CVE entries, with remote code execution and information disclosure at four each.
The single critical entry is CVE-2026-34182 at CVSS 9.1, a flaw in CMS AuthEnvelopedData processing that allows forged messages to be accepted. It reaches Visual Studio 2017 through 2022.
The highest-scoring entry in this family is not the critical one. CVE-2026-81376, a Visual Studio Code security feature bypass, reaches CVSS 9.6 while carrying an important rating. It is a useful reminder that severity labels and CVSS scores answer different questions.
Visual Studio Code and its Copilot extensions take 10 entries, mostly security feature bypasses. Update the editor and confirm workspace trust prompts, extension installation and remote sessions behave as configured.
.NET ships SDK updates on all three supported lines, x64 and x86: 8.0.131 and 8.0.425, 9.0.121 and 9.0.318, and 10.0.112 and 10.0.401. Install them, then build and run a representative project to check for regressions. Keep the 10 November date for .NET 8 in view while you are in there.
The .NET Framework ships monthly rollups per operating system: Windows Server 2012 (KB5126147), Server 2012 R2 (KB5126148), Windows 10 1809 (KB5126144), 21H2 (KB5126145), 22H2 (KB5126146) and Server 2022 (KB5126149). One gap worth noting: the 4.7.2 package for Windows 10 1607 is listed as pending and will follow, so estates still on 1607 will not complete their Framework patching this cycle.
Add these to your standard release schedule, behind this month’s Windows, Office and SQL Server priorities. Keep the 10 November date for .NET 8 and PowerShell 7.4 in view while you are in the developer estate, because a patch this month does not extend either branch.
Adobe (and third-party updates)
September is the largest release of the year, and this (crazy, super high) volume is the least interesting thing about it. The 963 CVEs matter less than the 55 entries Microsoft flags as high risk, and those sit in printing and fonts. Adobe shipped two Acrobat builds one digit apart and only the second is a security update (nothing to worry about here). Of the CVEs Microsoft republished, 25 are not Microsoft’s. A version number tells you very little about the work in front of you. So, given my (super-secret knowledge) of how Microsoft operates over the summer, here is my prediction for next month (October). It won’t be as big as this month – but just you wait – November is going to be big. Let’s up those numbers (or not).
Long before Taco Tuesday became part of the pop-culture vernacular, Tuesdays were synonymous with security — and for anyone in the tech world, they still are. Patch Tuesday, as you most likely know, refers to the day each month when Microsoft releases security updates and patches for its software products — everything from Windows to Office to SQL Server, developer tools to browsers.
The practice, which happens on the second Tuesday of the month, was initiated to streamline the patch distribution process and make it easier for users and IT system administrators to manage updates. Like tacos, Patch Tuesday is here to stay.
Patch Tuesday coverage has long been a staple of Computerworld’s commitment to provide critical information to the IT industry. That’s why we’ve gathered together this collection of recent patches, a rolling list we’ll keep updated each month.
In case you missed a recent Patch Tuesday announcement, here are the latest six months of updates.
September Patch Tuesday: 963 CVEs, 2 exploited flaws, 1 message
September’s Patch Tuesday is Microsoft’s biggest of 2026, with 963 CVEs, two exploited flaws and a clear message: prioritize Windows, Office and SQL Server.
Two vulnerabilities are already exploited: CVE-2026-81963 in the Windows Update Stack and CVE-2026-85880 in Advanced Local Procedure Call. Nothing in this release was publicly disclosed ahead of the patch. Readiness recommends a Patch Now scheduling for Windows, Office, SQL Server and the developer tooling, and standard patch release for Exchange.
August’s Patch Tuesday is a monster: 751 fixes, with an exploited Windows flaw
Microsoft’s August 2026 Patch Tuesday closes at 751 CVE entries (across all product families), with 108 rated as critical. One flaw is already exploited, CVE-2026-68820, an elevation of privilege in the Windows WinSock driver (afd.sys). Two more were disclosed but not exploited.
This security-only release earns Patch Now for Windows, Office and Exchange; no SQL Server updates this month. Unfortunately, several critical issues affect server roles: Windows DNS Server carries a cluster of critical RCEs; Windows DHCP Server is the most-populated Microsoft product family at 14 entries. Testing should lead with printing and fonts and the Remote Desktop client, then a WinSock smoke test given the exploited afd.sys flaw.
July’s Patch Tuesday sees an end-of-support collision amidst a massive, record-setting patch wave
Microsoft addressed 722 CVEs this month once the 427 Chromium upstream relays are set aside — roughly three times a normal cycle and one of the largest single months in recent memory. Two vulnerabilities arrive under active exploitation: an elevation of privilege in Active Directory Federation Services (CVE-2026-56155), and an elevation of privilege in SharePoint Server (CVE-2026-56164). A third, a BitLocker security feature bypass (CVE-2026-50661) is publicly disclosed but not yet exploited.
The July 2026 Patch Tuesday earns Patch Now recommendations for Windows, Office, Exchange, and SQL Server. SharePoint has two critical RCEs on top of its exploited zero-day, and Exchange Server returns with a critical on-premises spoofing flaw. Adding to our (dear) administrator’s efforts, SharePoint Server 2016/2019 and SQL Server 2016 all reach end of support today.
Microsoft this month released 206 updates affecting Windows, Office, Exchange Server, and its developer tools — including three Windows vulnerabilities already publicly disclosed. That trio includes an elevation of privilege in the Collaborative Translation Framework (CVE-2026-45586), a denial of service in HTTP.sys (CVE-2026-49160), and a BitLocker security feature bypass (CVE-2026-50507). At the moment, none appear to be under active exploitation, but all three are rated “Exploitation More Likely.”
Even without an exploited zero-day, the June 2026 Patch Tuesday release requires Patch Now recommendations for Windows, Office, and Exchange. The latter is back in the patch picture with a consolidated security update that Microsoft recommends installing “as soon as possible.”
For May, Patch Tuesday means 139 updates — but no zero-days
Microsoft this month released 139 updates affecting Windows, Office, .NET, and SQL Server (though there were no updates for Microsoft Exchange Server). Despite the absence of zero-days, the May Patch Tuesday update still requires Patch Now recommendations for Windows and Office.
The combination of three unauthenticated network RCEs (Netlogon, DNS Client, and SSO Plugin for Jira and Confluence), four Word Preview Pane RCEs, the large TCP/IP vulnerability cluster, and the carry-over BitLocker recovery condition (still active on Windows 10 and Windows Server) warrants an accelerated deployment release schedule.
Microsoft’s Patch Tuesday release for April is a whopper
Windows admins are going to be busy this month, dealing with the largest Patch Tuesday cycle in memory. The April release involves 165 updates and roughly 340 unique CVEs from Microsoft — including two zero-days, one of which is already being actively exploited in the wild.
The Readiness team recommends “Patch Now” schedules for nearly every major product family: Windows, Office (with a zero-day), Microsoft Edge (Chromium), SQL Server, and Microsoft Developer Tools (.NET). April also brings Phase 2 of Microsoft’s Kerberos RC4 hardening with full enforcement set for July. There is a lot to cover, so here’s a useful infographic mapping the deployment risk for each platform.
Microsoft is changing the destination address of two of its most popular services: starting this month, it will redirect M365 and Teams web users to copilot.cloud.microsoft and teams.cloud.microsoft, respectively.
The Teams move is already under way, and Microsoft has now added M365 to the mix. The company announced the changes in two MessageCenter posts: MC1465764 (mirror) and MC1462915 (mirror).
Organizations using these products are advised to update their systems and documentation to ensure continued access. Microsoft has told customers to review configurations on client devices, proxies, firewalls, secure web gateways, or other enterprise network controls to confirm that users can connect to the new addresses. Companies having trouble connecting should ensure that their environment aligns with the recommended network requirements for Microsoft 365 Copilot.
Enterprises that had been blocking the new Copilot address to prevent employees accessing their personal Microsoft accounts can use Microsoft’s TenantRestrictions control to achieve their goals instead, it said.
All redirects should be completed by early October, Microsoft said, advising companies that can’t meet the deadline to contact their account representative for help. Limited exceptions to the Teams redirect are possible until Dec. 31, 2026, but after that no further delays will be possible, it said.
AI note-taking applications are increasingly used by workers to record meetings, generate conversation summaries and suggest post-meeting action items.
Along with the promised productivity benefits — enabling users to focus on meetings rather than actively taking notes — the emergence of these AI tools has raised privacy questions, particularly around obtaining prior consent by meeting participants for their use. Those concerns, in turn, have prompted a spate of lawsuits against software vendors that sell AI notetaking tools.
In some ways, the underlying questions are not new: It’s long been possible to record a phone call with a dictaphone, and laws around surreptitious recording have been around for decades. Yet widespread access to AI notetakers via desktop or smartphone apps means that it’s easier than ever to record a conversation for future reference.
Among the thorny questions arising from the technology’s use: what happens to conversation data sent to a software vendor’s servers for processing? Are the recording and transcript used to train those vendors’ AI models, for example, or create biometric voiceprints? Those practices are among the issues being considered in US courts.
Otter, which claims to have 35 million users, was subject to a class-action complaint in a federal court in California last year. That complaint accused Otter of recording individuals without consent and using their voices to train its speech recognition AI tools. Last month, a judge rejected Otter’s attempt to dismiss the main claims, though the scope of the case was narrowed.
A lawsuit filed against another vendor, Fireflies, in an Illinois court late last year, alleges the company collects and stores biometric voiceprints without user consent, in violation of the Illinois Biometric Information Privacy Act (BIPA). Fireflies claims to have more than 20 million individuals and 1 million organizations as customers.
Earlier this year, a class-action complaint in a Washington court claimed that a live transcription feature in Microsoft’s Teams collaboration application also violates BIPA by collecting biometric data without consent.
None of these cases has yet been resolved, and it’s unclear whether any of the vendors broke the law in the design and delivery of their products and services. But the lawsuits highlight considerations for businesses that allow the use of AI notetakers, both in terms of prior consent for recordings and understanding how conversation data is handled.
More broadly, the lawsuits raise questions about how existing privacy and consent rules apply to new technologies that make it easier to record others, whether through AI note-taking apps, smartglasses, or other recording devices.
Computerworld spoke with Brian McGinnis, partner at law firm Barnes & Thornburg and a founding member and co-chair of the firm’s Data Security and Privacy Law practice group, about the focus of the lawsuits, potential outcomes, and how businesses can deploy AI notetaking apps safely.
Several cases have already been brought against popular AI note-taking apps. What are some of the main commonalities between these? Which laws are the vendors accused of breaching? “The common allegation is that these companies capture communications of people who did not agree to the recording or receive adequate notice. Some of the lawsuits also allege that meeting data is used to train AI models and that consent cannot meaningfully be withdrawn once the data has been processed.
“There are various federal and state claims. You’ve got the Electronic Communications Privacy Act, a federal wiretapping statute. As a general matter, the Electronic Communications Privacy Act permits an interception when one party consents, subject to statutory exceptions and questions about whether the technology constitutes an unlawful interception or third-party eavesdropping. In other words, if you, as the user, provide consent, you can be on a meeting with 20 other people and it’s deemed to be sufficient; you don’t necessarily need to get the consent of other people.
“But California and a minority of other states are what we call ‘two-party consent’ states, meaning each individual on the call has to give consent; it’s not sufficient for you as the person who turns the notetaker on to provide the consent — you also have to get the consent of others that are being recorded. There are state laws around that.
“There’s a law called CIPA, the California Invasion of Privacy Act, that’s being utilized in this context. We see a lot of suits being brought under that law — it’s a wiretapping statute designed for telephone wiretapping that’s now being applied to the internet.”
What about the use of biometric data? “A growing number of states regulate biometric data, with Illinois’ BIPA being particularly prominent because it provides a private right of action. This means an individual can sue a company for violation of the law.
“That law covers biometric information. With an audio recording or recording of ‘dumb’ video that isn’t running any algorithms, you’re not necessarily collecting any biometrics. But when you start identifying people, you’re recording things like faceprints or voiceprints, which are in the definition of biometric information within the statute. Now you’re not only collecting personal information, but also biometric information, which is considered very sensitive and much more highly regulated.
“Then you’ve got the private right of action that goes against it. Part of the argument here is that recordings taken by the AI notetakers can be used to produce some form of biometric information, such as a voiceprint.
“We’ve seen a lot of cases, and a lot of changes in industry as a result of this law. Shutterfly had a famous case about scanning for people’s faces and things like that in Illinois that changed the photo storage and processing industry a little bit.
“A lot of companies stay out of Illinois to avoid this law specifically. But a customer organization might not know exactly who’s in a meeting and where a person is located at the time of the meeting. So, you need to either follow that law and get individual consent, or stay out of states with biometric laws if you want to use some of these tools.
“It’s just a further challenge for these applications if the goal is to be used as much as possible with as little detection as possible.”
What are some of the potential outcomes for these cases? “I think it’d be unlikely to get an outright ban, absent passing some kind of new law that says these tools are per se illegal for use. It’s much more likely the outcome will require some changes and controls over the way that they get used. The clearest case would be some kind of a pop-up notice: ‘Hey, this meeting’s being recorded, here’s who it is, here’s their privacy policy, here’s their terms of service – do you consent to it?’ And getting opt-in consent from anybody who wants to be recorded.
“The notion that only one person in the meeting has to say it’s okay and you can just automatically record everybody else, I think that’s probably at risk, and could potentially be replaced with a standard that requires everybody to consent before it’s considered legal.
“But the newer —and more interesting — wave of these is the Granola case, where part of its marketing is that people aren’t aware that it’s there. The Granola complaint alleges that the product was designed to operate without alerting other participants. It’s possible that kind of activity could result in a decision that would ultimately ban it outright. In other words, that it’s illegal to utilize these tools if you aren’t providing notice to everybody and/or aren’t getting consent from everyone on the call. That’s a possible outcome that we could see.
“To me, that’s interesting when you think beyond AI note-taking and into the broader world, with conversations around, like, Meta Glasses, or any of these kinds of AI wearables. Granola in particular has an Apple Watch app, and there are other wearable or physical devices — there’s one [Plaud Note] that sticks on the back of your phone and is essentially an always-on recording device.
“With these devices, you’re going from an online meeting where you can provide notice and there’s a structure to obtain consent, to walking down the sidewalk and recording people and casual conversations. Maybe it’s somebody you’re having a conversation with, maybe it’s somebody at the table next to you in the coffee shop that you have no relationship with whatsoever — what are the laws around consent and notice in those cases, where there’s no digital interface to put that up in front of people? Do you have to go around with a pad of paper and a pen and get people to sign consent to use these things? Do you have to physically tell them?
“Those are the more interesting conversations that this line of cases is just at the beginning of helping us get some answers on. In other words; how do you get consent? How do you provide notice in a world where we don’t have documents or screens in front of us to easily handle that? Those are interesting questions that the law will have to figure out here.”
These tools are increasingly used in the workplace. How can businesses be sure they deploy the technologies safely? “We’re getting a lot of questions from our clients about this topic, because they’re really unsure and uncertain of how to handle these tools.
“Obviously, there’s a push for broad use of AI within their companies, for productivity increases within their company. People like the tools; they want to be able to use them. But then we also hear a lot of stories about ‘I jumped on a meeting; I didn’t even know it was being recorded, then I got an email afterward with a transcript of it,’ and ‘half of what it recorded wasn’t actually what I said, or it was interpreted incorrectly’ — things like that. So there’s a lot of consternation amongst our clients about the people within their organizations using it.
“I can’t tell clients definitively that they’re legal as they are; there are ways to use this legally and safely that aren’t going to get your organization sued, but you probably have to do some things that are beyond what’s provided ‘out of the box’ by the software providers.
“With Granola, for example, my understanding is that certain notice features may not be enabled by default. You can turn on video or audio watermarking, and you can turn on the notice that pops up in these things, but I think it ships without those features enabled. That puts the responsibility on the individual user to determine and then implement their own legal privacy and legal compliance mechanisms using their settings.
“You really have to play to the most stringent state’s law. I would advise a company that, to decrease your chances of getting in trouble for use of these tools, you need to obtain consent of all parties on the call. You can do that verbally, as well; written is even better.
“Then it’s about having an internal AI note-taking policy. Think of a BYOD policy, which all these companies have, or an AI usage policy — this could be part of that policy, or a standalone policy: ‘Here’s how our organization thinks about these tools: you can only use these approved tools and, if you’re going to use them, you have to turn on these features. You have to get consent from everyone. Here are limits on what you can do with the output of those transcripts or recordings.’
“If you set all that up and do the compliance and governance work, I think you can use these tools and most likely stay on the right side of the law. Certainly, the law doesn’t prevent consenting adults from consenting to the use of these kinds of tools.
“But the further you get away from that written consent standard, the more problematic it becomes. If you just want to go to a notice standard and not obtain actual opt-in consent, or, even worse, if you want to try and do this without anybody knowing, that potentially could get challenged.”
That being said, generative AI can be incredibly useful. The key is simply to frame it as a purpose-specific tool for the right type of limited task as opposed to treating it as the end-all answer for everything, as most tech players seem overly eager to do these days.
Today, I’ve got a new Gemini Android advantage for you to explore — another one that I’ve never seen advertised anywhere but that works brilliantly well and solves a long-standing limitation of our modern mobile gizmos.
It’ll take you all of a minute to master and cost you precisely $0 to pull off. Ready?
This Gemini-provided power-up very much follows the path of thinking about AI as a limited, purpose-specific tool for a narrow task — the exact sort of area where AI excels.
I won’t keep you waiting: Gemini, as I discovered whilst poking around within it recently, is really good at generating unique, custom ringtones and notification sounds based on your personal preferences and specifications.
It almost seems obvious, once you think about it. But I sure hadn’t thought about it up until now — and I suspect most other folks haven’t, either.
The advantage here goes beyond just superficial silliness, too: By creating your own custom ringtones and notification noises, you can know exactly what event your phone is alerting you to within a split second of hearing the associated sound — without having to rely on the same limited and often underwhelming pool of default options that everyone else uses (or, worse yet, having to lean on shady, ad-ridden “ringtone apps” to find mediocre alternatives). That means you’ll know within a heartbeat when your boss or an especially important client is calling or if an incoming call is a random unknown number.
On the notification front, you can create a specific, memorable sound to accompany a new message in an important work-related Slack channel and a different distinctive sound for a high-priority email. They’ll all be sounds that you make and identity with and that no one else in the world uses. That’s pretty powerful.
And creating these custom sounds couldn’t be much easier, either, once you realize it’s possible:
First, just fire up Gemini on your phone (or on any device you’re using) and tell it what you want. So, for instance…
Create a soft, subtle ringtone that’s reminiscent of an old office phone sound.
Create a ringtone that sounds like an 8-bit version of The Final Countdown.
Create a one-second high-pitched notification sound that brings to mind the Super Mario Bros theme song.
Create a short notification sound that mimics the Back to the Future time circuits noise.
Create a notification sound that sounds like a robot saying “ALERT, ALERT!”
The only limit is your imagination. And if you’re not feeling especially imaginative, you can even ask Gemini to give you a list of ideas for distinctive, memorable ringtones or notification sounds based on geeky nostalgia, 80s pop-metal, or whatever it is that tickles your fancy.
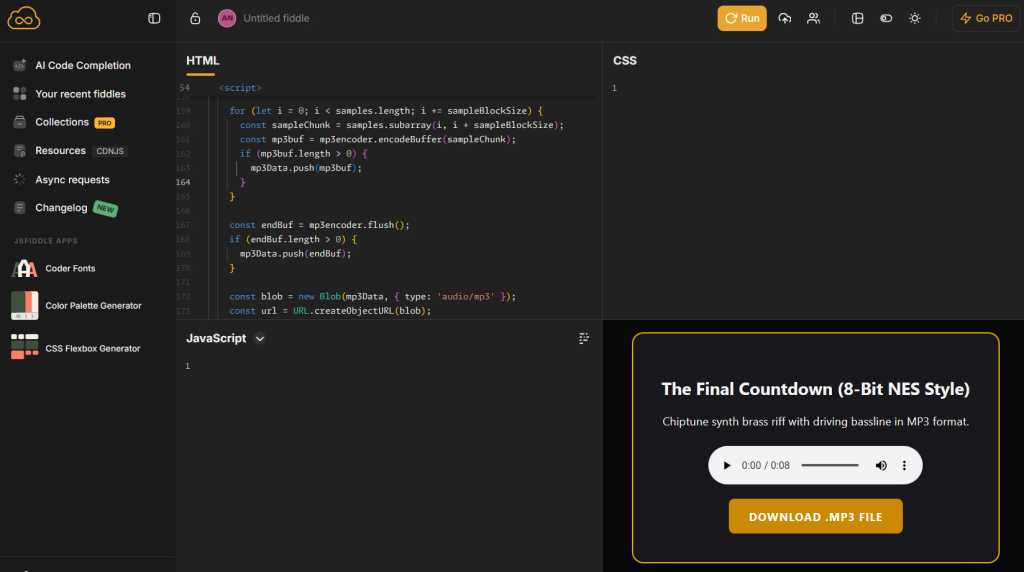
Once you’ve sent a request, Gemini will — somewhat confusingly — spit back a big honkin’ block of HTML code. This is because, for reasons unknown, the system can’t or won’t just provide a sound file directly. Go figure.
Ask, and ye shall receive: Gemini’s ringtone-creating prowess in action.
JR Raphael, Foundry
But from there, it’s just one more quick step to get the file you need: Click or tap the copy icon in the upper-right corner of that code block — the icon that looks kinda like two stacked, rounded rectangles — to copy the entire chunk of code onto your system clipboard.
Then open up your browser and go to the website JSFiddle.net. It’s a well-known, long-standing tool for running code like HTML right in your browser and seeing the result, and it works entirely in the browser and without any downloads or special permissions required.
Tap or click into the “HTML” field, then paste in the code from your clipboard (by long-pressing any open space, on Android, and selecting “Paste” from the menu that appears). Click or tap the “Run” button, and — ta-da: You’ll see a player to listen to your custom Gemini-generated sound and a button to download it.
The JSFiddle website makes it easy to take Gemini’s output and both play and download a sound file from right within your web browser.
JR Raphael, Foundry
Provided you like what you hear, hit the button to download the file, then head into the Sound section of your Android system settings to save it and make it available for applying as any kind of alert or ringtone. The exact steps for doing that will vary from one type of Android device to another, but on a Pixel or another phone that follows Google’s core Android interface, you’ll tap on either “Ringtone” or “Notification,” then tap “My Sounds” and tap the plus icon to import your own custom file from your phone’s local storage.
On a Samsung device, you’ll start the same way but look for the plus icon within the “Ringtone” section of the settings, then tap the “Folders” tab to find your locally downloaded files. Samsung doesn’t make it easy to add in your own custom notification sounds, annoyingly, so what you’ll have to do is open up the Google Files app, find the file you downloaded in your “Downloads” folder, then tap the three-dot icon alongside it to copy it to the folder called “Notifications.” Once the file is in that folder, it should show up as a notification noise option within the Samsung Android settings.
With Gemini as your personal composer, you’ll never be stuck with generic overused sounds again — and you’ll always know exactly what’s happening from the first note of whatever noise you hear.
Swiss authorities have launched a pilot project to determine whether it is possible to replace Microsoft 365 with similar open-source services, RTS reports. This follows a proof-of-concept project in which 172 civil servants tested the German open-source platform openDesk.
According to Matthias Stürmer, a professor at the University of Bern, there are three main reasons for the switch: to reduce dependence on US services, to improve operational reliability, and to reduce costs.
In the first phase, the migration involves 3,000 computers, which corresponds to 7% of Switzerland’s federal workforce. The government has more than 54,000 workstations in operation. The pilot will prioritize employees who have access to highly sensitive data, according to RTS.
A move by the Swiss Armed Forces from Microsoft 365 to openDesk is already underway, with that migration expected to be completed in October, It’s FOSS reports.
Switzerland’s move is part of a larger ‘digital sovereignty’ effort in the European Union that aims to retain local control over data, applications, and infrastructure. In January, lawmakers directed the European Commission to map critical technology dependencies and then develop policies to reduce reliance on foreign providers.
A phishing-as-a-service operation targeting Microsoft 365 users has harvested thousands of session cookies that could be used to hijack authenticated sessions after victims complete multifactor authentication, CloudSEK said.
The cybersecurity firm said in a report that it uncovered the operation, known as BigBear 2.0, in June after gaining access to its administrative panel.
The panel contained 5,137 credential records linked to 461 targeted organizations across more than 40 countries. CloudSEK also reported 4,148 captured session cookies and 1,032 plaintext passwords. The firm said 474 records showed completed logins in which attackers captured the authenticated session created after MFA.
BigBear 2.0 is built on Evilginx2, a framework that places an attacker-controlled reverse proxy between the victim and Microsoft’s legitimate authentication service. The victim signs in through the proxied page and completes MFA as usual. Once Microsoft issues an authenticated session cookie, the phishing infrastructure can intercept it and allow the attacker to reuse the session without completing the authentication process again.
The operation also uses residential proxies selected according to the victim’s country, which can make malicious authentication traffic appear geographically consistent with the user. CloudSEK said this technique can weaken location-based checks used in Conditional Access policies.
Researchers also found custom code designed to disable FIDO2/WebAuthn authentication on the phishing pages, potentially steering users toward weaker, phishable authentication methods.
CloudSEK described BigBear 2.0 as a multi-user service with at least five identified affiliate operators. The company said it observed 42 virtual private server (VPS) nodes over the campaign, with 26 deleted from the panel since late July.
IT services and managed service providers accounted for 151 of the organizations identified by CloudSEK, making them the most heavily represented sector in its data. Such organizations can present especially valuable targets because employees may hold privileged access to customer environments and administrative systems.
Session theft moves into the mainstream
The significance of BigBear 2.0 is not just its ability to capture authenticated sessions after MFA, but the way it packages techniques once associated with more skilled attackers into a service that can be used at scale, said Keith Prabhu, founder and CEO of Confidis.
The underlying technique is not new, said Akshat Tyagi, associate practice leader at HFS Research. “What BigBear 2.0 changes is accessibility and scale,” Tyagi said. “It packages AiTM phishing, residential proxies and automated cookie replay into a service that lowers the expertise needed to run these attacks.”
That shift means enterprises need to think beyond protecting the authentication event itself, he said, because a captured session may give an attacker access to Microsoft 365 without another password or MFA challenge.
Prabhu added that successful MFA should no longer be treated as proof that an account or session remains secure.
Session cookies and access and refresh tokens should be treated as high-value authentication material rather than technical artifacts behind the password, said Sakshi Grover, senior research manager for cybersecurity products and services at IDC Asia Pacific.
OTP, SMS, and push-based MFA should not be relied on as standalone defenses against this type of attack, Tyagi said, because the attacker can allow the legitimate user to complete authentication before stealing the resulting session.
Tyagi said enterprises should enforce phishing-resistant authentication such as FIDO2/WebAuthn passkeys rather than merely making it available alongside weaker alternatives. Prabhu pointed to Windows Hello for Business and certificate-based authentication as additional options, with stronger methods enforced through Conditional Access authentication strengths.
Grover said organizations should also use Continuous Access Evaluation and token protection where Microsoft 365 supports them, but cautioned against treating token protection as a complete solution because coverage varies across platforms, clients and workloads.
The problem is also operational, Grover said. Identity and access tools are not always sufficiently integrated with security operations or SIEM platforms, leaving potentially useful identity signals disconnected from the analysts responsible for detecting attacks.
Password resets are not enough
“Treat the event as an active session compromise, not merely a stolen-password incident,” Prabhu said.
He recommended disabling or containing the affected account, revoking Entra sign-in sessions and refresh tokens, and forcing reauthentication. Incident responders should then examine Microsoft 365 logs for evidence of mailbox access, malicious inbox rules, unusual OAuth consent, newly registered MFA devices, privilege changes, and access to other cloud applications.
Tyagi cautioned that IP location may provide limited reassurance in such investigations because residential proxies can make attacker activity appear geographically consistent with the legitimate user. Responders should instead focus on reconstructing what occurred during the compromised session, he said.
Investigators should also determine whether the stolen session was used to reach other employees, customers, or external contacts, Prabhu added.
Grover said organizations should also include session hijacking in tabletop exercises, testing how identity, security operations, messaging, and cloud teams would coordinate during an authenticated-session compromise. Such exercises can expose gaps that may not emerge in simulations centered on conventional credential theft or ransomware, she said.
You might not know it from looking, but Gmail is jam-packed with time-saving tricks.
Some of ’em are right there in front of your face, if you know how to find ’em — while others require a teensy bit of under-the-hood tinkering to activate. But all of ’em are built right into Gmail and have the potential to make managing your email a heck of a lot easier.
Check out these 16 splendid Gmail tips and get ready to master your inbox once and for all.
(Note that unless otherwise specified, these tips are specific to Gmail’s web-based desktop version.)
Inbox step-savers
1. You can actually view attachments right from your Gmail inbox. Provided you haven’t switched away from the service’s “default” interface arrangement, you’ll see small tiles for every file associated with an email right below the message’s subject line. And you can click on any of those tiles to open or preview the file’s contents and get directly to the info you need.
Gmail’s attachment tiles are a great way to jump directly to attachments without having to open an email.
JR Raphael / Foundry
2. It’s easy to miss, but take note: When you hover your mouse over a message in your inbox, Gmail gives you a series of quick-access actions at the far-right side of the line. You can archive the email, delete it, mark it as read or unread, snooze it, or even RSVP to a meeting request right then and there — without ever having to open the message.
3. A super-useful keyboard shortcut I always forget to use: While viewing a multi-email thread of messages — a conversation in which you have numerous back-and-forth replies under the same subject — hit the semicolon key (;) to expand the entire conversation and show every message in the thread. And then hit the colon key (:) to collapse it back down so you see only the most recent email.
Just make sure you enable keyboard shortcuts first, if you haven’t already: Click the gear icon in the website’s upper-right corner, then click “See all settings” and look for the “Keyboard shortcuts” option midway down the screen that comes up. Select the “Keyboard shortcuts on” setting and then be sure to click the Save Changes button at the bottom of the screen.
4. Some of Gmail’s best keyboard shortcuts are the ones you create yourself. Go back into the website’s settings and this time, click the Advanced tab. See the line labeled “Custom keyboard shortcuts”? Click “Enable” next to that, then click the Save Changes button at the bottom of the screen.
Once Gmail refreshes itself to apply the changes, go back to the Settings area again and look for the newly present Keyboard Shortcuts tab. There, you can adjust any of the default keyboard settings to make them simpler to activate or easier to remember.
One of my favorite adjustments, for instance — and one I rely on constantly — is adding in a second command for the “Go to inbox” shortcut, which is typically gi by default. In Google’s old Inbox service, that shortcut was simplified down to just i, and once you get used to that shorter sequence, you won’t want to go back.
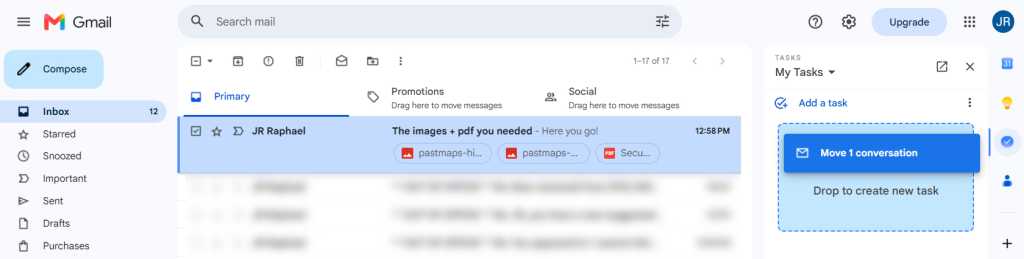
5. The panel at the right of Gmail’s web interface lets you pull up Google Calendar, Google Keep, Google Tasks, or Google Contacts right inside your inbox so you can manage info from each of those apps without having to switch tabs or open anything new. And here’s a handy hidden trick: With Tasks, you can drag messages directly from your inbox into the panel to create new tasks around them.
Creating new tasks from emails is as simple as dragging and dropping, as is being done here with the topmost message.
JR Raphael / Foundry
Unfortunately — and somewhat strangely — the same drag-and-drop behavior isn’t currently possible with Calendar or Keep, nor is it possible for Contacts.
6. Even with a miniature version of Contacts being available inside that handy side panel, you might sometimes want to pull up the fullGoogle Contacts website for its complete set of features. Provided you’ve got Gmail’s keyboard shortcuts enabled now, commit this workaround to memory: Pressing g and then c will open up Contacts in a separate tab, no matter what else you’re doing in your inbox.
Composing shortcuts
Editor’s note: Assuming you’ve enabled keyboard shortcuts (see tip 3), the following keyboard shortcuts work in any browser on any desktop operating system. Mac users, just swap in the ⌘ key for “Ctrl” wherever you see it.
7. Ever like marking messages as unread after you’ve opened ’em? Gmail makes that incredibly easy to do: Anytime you have an email open, look for the envelope icon directly to the right of the trash can in the horizontal row of icons above your message (in the area directly beneath the search bar). That’ll let you mark the message as unread with a single click. Or, for a faster and more powerful one-two punch, just type an underscore (_) while viewing any message. That’ll mark it as unread and zap you back to your main inbox.
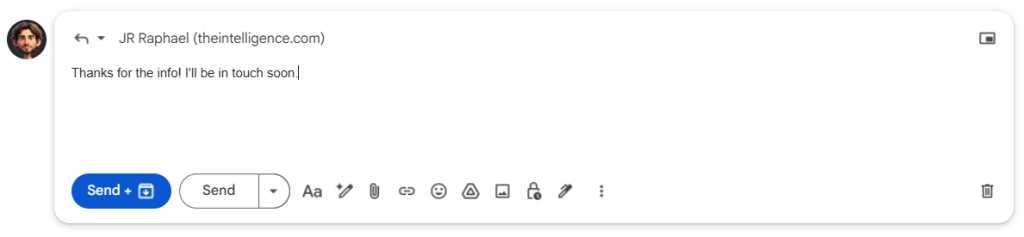
8. Speaking of combining multiple actions into a single command, simplify your inbox organization process by enabling Gmail’s convenient Send & Archive button. It places a second button alongside the regular Send button whenever you’re responding to an existing message, and clicking that button (or, even better yet, hitting Ctrl-Enter on your keyboard) will send your response and archive the thread in one fell swoop.
To enable it, look for the “Send and Archive” option within the General tab of Gmail’s settings. Click “Show ‘Send & Archive’ button in reply,” hit the Save Changes button at the bottom of the screen, and then get ready to save yourself steps the next time you type a reply.
Gmail’s Send & Archive button (the blue one to the left of the regular Send button) turns two steps into one.
JR Raphael / Foundry
9. I don’t know about you, but I frequently start typing an email and then decide against sending it. (Rather fittingly, I started typing out a lengthy explanation of the reasons but then decided against including it.) If the same thing ever happens to you, remember this: Hitting Ctrl-Shift-D while you’re in the Gmail compose tool will close the compose window and discard your draft. And it works whether you’re writing a new email or a reply.
10. Another awesome time-saver: In addition to the obvious Ctrl-B for bold and Ctrl-I for italics email formatting shortcuts, Gmail has hotkeys for doing some advanced forms of text formatting — things that’d otherwise require multiple clicks and much menu-hunting to accomplish.
The ones I use the most:
Ctrl-Shift-8 will add a bulleted list into your email (just like this list!), and Ctrl-Shift-7 will add a numbered one.
Ctrl-Shift-9 will offset text in a blockquote style.
Ctrl-] will indent text, while Ctrl-[ will remove any indentation.
And Ctrl-\ will remove any formatting on your selected text and make it as plain as can be.
11. You’d never know it, but the Gmail compose tool itself can take on various forms, depending on your preferences. Make a mental note of these possibilities and the shortcuts to get to ’em:
To start a new message in the default lower-right-corner-of-the-screen window view, hit c.
To start a new message in a pop-up window totally separate from your main Gmail tab, hit Shift-C. You can do the same thing for a reply by hitting Shift-R while viewing a message thread — or Shift-A for reply-all.
To start a new message in a full-screen compose window within your main Gmail tab, hit c — then click the little arrow icon in the compose tool’s upper-right corner. (You can also hit Shift while clicking that icon to pop the message out into a separate pop-up window form.)
If you’d rather use that full-screen compose window all the time, by default, click the three-dot menu icon in the lower-right corner of the compose tool and look for the “Default to full-screen” option there. (If you ever change your mind, you’ll find the option to disable that preference in that very same spot.)
If for some reason you like the idea of composing a message in a new tab instead of a pop-up window or within the main Gmail tab, just hit d while in your inbox. That’ll do the trick!
To see more keyboard shortcuts, just type ? while viewing any message list within Gmail.
Smarter snoozing
12. Don’t forget to take advantage of Gmail’s super-handy snoozing tool: Instead of letting messages linger in your inbox and pile up to an unmanageable point, use the snooze function to help yourself deal with everything as soon as you see it.
A good rule of thumb to maintain: If you can respond to something in less than a minute, do it. If something doesn’t require any action on your behalf, archive it immediately. And if something requires some sort of action but you don’t have the time to mess with it at that moment, snooze it to a day and time when you will be able to handle it.
You can snooze an email from your inbox by hovering over the message and selecting the clock-shaped Snooze icon, as noted in tip 2. You can also snooze an email while it’s open by clicking the three-dot menu icon to the right of the folder symbol directly above the email and then clicking “Snooze” within the menu that pops up. Or you can simply press b while you’re viewing a message or while you have it selected in your inbox.
Snoozing a message causes it to vanish from your inbox and then reappear at any day and time you choose.
JR Raphael / Foundry
13. Gmail even makes it possible to snooze multiple messages at the same time — in case you see more than one email that needs to be pushed back to the same point. From your inbox, simply click the boxes to the left of any messages you want to include, then click the three-dot menu icon within the row of icons toward the top of the screen and select “Snooze” from there.
14. Need to get back to something you snoozed — or change the day and time at which it’s set to reappear? You can always find all of your snoozed emails in Gmail’s Snoozed section, located beneath the “Inbox” line in the left-hand panel. Once you’re there, just hover over any email and click the clock-shaped icon to change its snooze settings or unsnooze it entirely.
15. You can snooze messages from the Gmail mobile apps, too, though the option is a bit buried. From the inbox view, press and hold a message to select it, then tap the three-dot menu icon at the top of the screen and look for “Snooze” in the list of options that appears. If you’ve already opened the message, tap the three-dot menu icon at the top of that screen; you should see “Snooze” show up as part of the options there as well.
16. Make snoozing even simpler in the Gmail mobile app by assigning it to one of your inbox swipe actions. Just open up the app, tap the three-line menu icon in its upper-left corner, then select “Settings.” On Android, tap “General settings” followed by “Swipe actions”; on iOS, you’ll tap “Inbox customizations” and then “Mail swipe actions.”
All that’s left is to set either your left swipe or right swipe to “Snooze,” and then, you can simply swipe any message in that direction from your inbox to snooze it — no wasted taps or menu diving required. (The Gmail Android app has several other similarly useful hidden features, by the way, most of which aren’t available on iOS.)
With one quick setting adjustment, you can snooze any message from the Gmail mobile app simply by swiping it to the left or the right from your inbox.
JR Raphael / Foundry
And with that, your Gmail time-saving toolbox is officially complete! The next logical step in your inbox improvement adventure is mastering the art of Gmail labels to fight back against email chaos — and I’ve got just the guide to get you started.
This story was originally published in May 2018 and most recently updated in September 2026.
Gmail is filled with hidden features and add-on possibilities, but one of the service’s most powerful organizational tools is sitting right in the heart of its regular settings.
As you may have guessed by now (especially if you read this story’s headline, you clever little cat), I’m talking about filters — Gmail’s long-standing system for automating your inbox with a series of custom-crafted rules. At a glance, filters can seem complicated. They can seem overwhelming. They can even seem unnecessary.
But don’t let yourself be fooled by the feature’s curiously crusty exterior. Gmail filters have the potential to completely reshape your inbox and the way your incoming messages are handled. They can help you keep your email in order with no ongoing thought or effort.
And, unlike Google’s new AI Inbox option (which notably still doesn’t seem to be available for most people as of this writing), filters (a) don’t require your personal messages to be processed by generative AI systems — and (b) give you complete control over exactly how your email is handled instead of forcing you to rely on inherently unreliable technology to figure out what you want for you (and then likely come up short at least some of the time).
Best of all? All it takes is a teensy touch of one-time planning to get Gmail filters set up to your exact specifications and working for you quietly and automatically from that moment onward.
Follow the filter-centric Gmail tips in this guide, and your inbox will be running like a well-oiled (but not too greasy) machine in no time.
Part 1: Figuring out your Gmail filters
Let’s start by thinking through some Gmail filter possibilities to get an idea for the sorts of setups you might want to consider — then, we’ll go step by step through the process of creating them.
With Gmail filters, you could:
Ensure messages from specific high-priority senders always go into your inbox’s Primary tab, where you’re certain to see them
Ensure specific sorts of lower-priority messages — like invoices, reports, or updates from different services you use — automatically get sorted into an out-of-the-way location and never even show up in your inbox
Keep messages from annoying people out of your hair (but still available in case you need to find them) by automatically archiving them as soon as they arrive
Forward messages from a specific address or with a specific phrase in their subjects to other members of your team or family
Instantly respond to messages to or from a specific address with a prewritten template
Label messages sent to a specific variation of your Gmail address (like youraddress+vip@gmail.com) or written with a specific word or phrase in the subject (like “urgent,” “important,” or “hey jerkwad, pay attention to this”) as “VIP” and then receive notifications only for messages with that designation
Mark specific types of messages from yourself as reminders by giving them a bright yellow “REMINDER” label that makes them stand out in your inbox
Get a snickerdoodle delivered to your desk every time your boss emails you
All right, so that last one isn’t really possible (not yet, anyway) — just wanted to make sure you were still paying attention. Everything else in that list, however, is absolutely doable and actually quite easy to set up with Gmail filters.
Got some ideas of your own? Good deal. Time to make ’em happen.
Part 2: Creating your Gmail filters
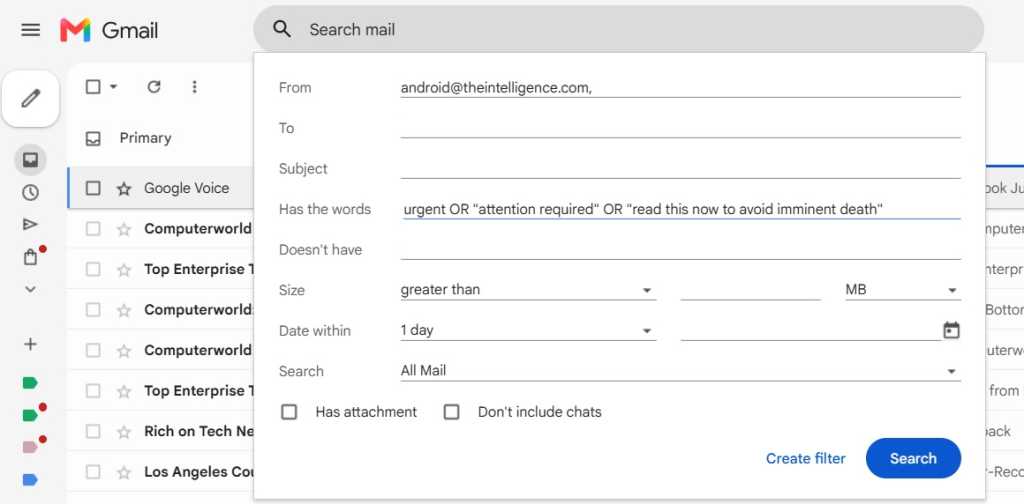
The simplest way to start a new Gmail filter is to click the control panel icon — the symbol showing three horizontal lines stacked on top of each other — within the big search box at the top of the Gmail website. (Filters can’t easily be managed on mobile, unfortunately, so you’ll need to do all of this in a desktop browser.)
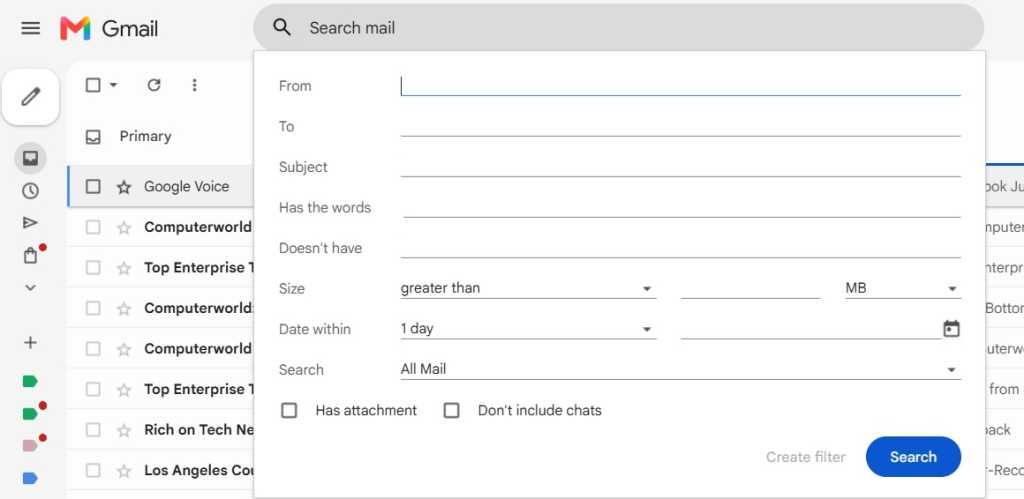
That’ll pull up a form where you can fill in whatever you want to use as the basis for your filtering — a word or phase that might appear within an email’s subject or body, an address from which a message could originate, or any other variable or combination of variables you like.
The form for creating a filter is filled with options for controlling email automation.
JR Raphael / Foundry
Fill in the fields as appropriate, using however many variables you want — even employing quotation marks around multiword terms along with operators like “AND” and “OR” between terms, if you really want to get fancy — and then click “Create filter” at the bottom of the box.
You can use any combination of variables, even employing operators within a single field, to control when your filter will run.
JR Raphael / Foundry
One quick warning: By default, your filter will apply to any and all incoming messages — hence the “All Mail” setting that shows up next to the “Search” option in the filter creation pop-up. If you change that option to “Inbox,” you’re likely to see an error message informing you that the parameters you chose are not recommended and may not work properly. Leave that “Search” option set to “All Mail” — which is probably what you want, anyway — and you’ll steer clear of any errors and allow things to work the way they should.
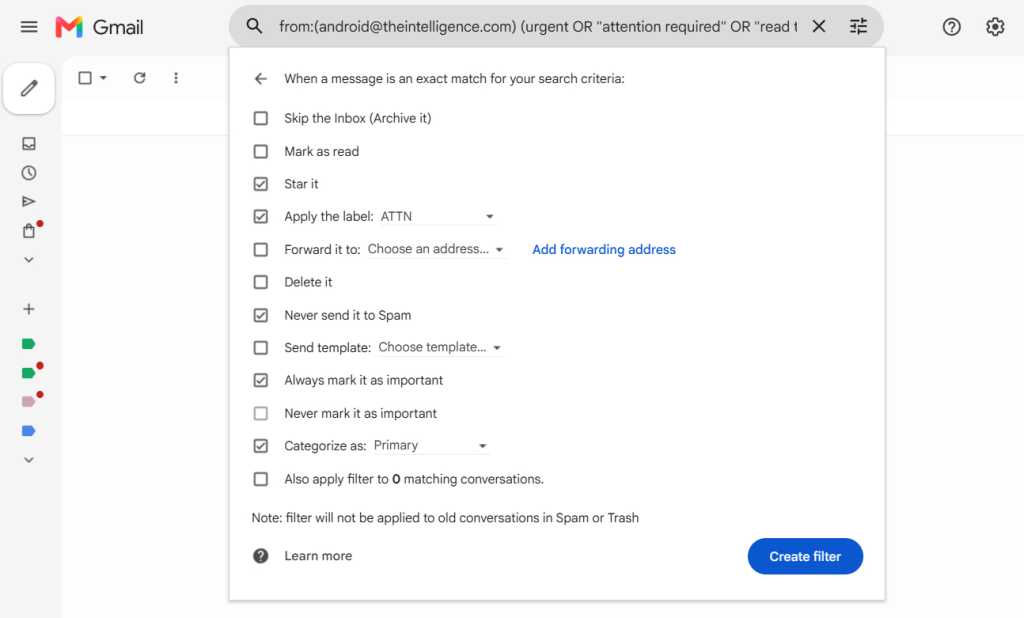
Now it’s time for the fun part — the part where you decide exactly what happens when a message meeting your conditions arrives. You can select any combination of actions from the list and then configure them as needed. You can even tell Gmail to apply your filter retroactively to messages already in your account (as opposed to using it only for new messages that arrive from that point forward) by checking the “Also apply filter to matching conversations” option at the bottom of the box.
Gmail’s filters include a variety of actions that can execute when your conditions are met.
JR Raphael / Foundry
Once you’ve got that finished, click the blue “Create filter” button — and that’s it: Your new Gmail filter is officially in place and active. The next time any message comes in that meets the parameters you outlined, the actions you specified will automatically take place faster than you can say “I embrace Workspace in my workplace cyberspace.”
Part 3: Managing your Gmail filters
Last but not least, make yourself a mental note in case you ever need to adjust your filters in the future: If you want to edit, delete, or even just revisit a filter you created, just click the gear-shaped icon in the upper-right corner of the Gmail website, click “Settings,” then click the “Filters and Blocked Addresses” tab at the top of the settings screen. You’ll see every filter you’ve ever created there and can tweak or remove any of ’em with a couple quick clicks.
Now if only we could find a way to get the filters to deliver those blasted snickerdoodles for us. Hey, Google: Any chance you can make that happen?
This article was originally published in October 2019 and most recently updated in September 2026.
It has taken six months to find a successor to outgoing CEO Shantanu Narayen, who announced in March that he would step back from the CEO role, remaining with the company as chairman.
There had been much speculation that he would be replaced by Adobe’s president of creativity and productivity, David Wadhwani, who was responsible for the digital media business segment that generates around three-quarters of the company’s revenue. Having missed out on the top job, however, he has chosen to leave Adobe, announcing his departure on LinkedIn.
Chakravarthy was responsible for the development of several products, including Adobe CX Enterprise, GenStudio and Brand Visibility, as well as the introduction of CX Enterprise Coworker.
He takes over at a shaky time for Adobe: Its stock price has tumbled dramatically in the past few years as the rise of AI has meant workers can lay out content and manipulate photos without needing Adobe products. Chakravarthy, who will initially work in tandem with Narayen, will have his work cut out for arresting the current decline.
So, you’ve got email, you say? Lots of it? More than you can possibly manage without losing the few metaphorical marbles still sloshing around in that soggy ol’ brain of yours?
I hear ya. In fact, I think we all can relate (even those of us whose brains are, erm, slightly less soggy). And I’m here to tell you: It doesn’t have to be so difficult.
Gmail has a variety of built-in tools for making your messages more manageable. Some of ’em are a little bit different from what you might be accustomed to using in more traditional email clients (here’s lookin’ at you, Outlook) — but if you take the time to figure out how they work, you might just be surprised at how effective they can be.
There’s no better example than Gmail’s label system. It’s a strange concept to wrap your head around at first, especially if you’re used to the more typical folder-based method of inbox organization, but here’s a little secret: Labels actually are folders, in a sense. That, however, is just one small part of their inbox-organizing power.
Think through these nine label-centric possibilities and get ready to see Gmail’s labels in a whole new light.
1. Use Gmail labels like super-folders for categorizing your email
First, the most basic Gmail label mindset to master: You can think of a label like a folder — but with an important twist: Instead of a message being placed into a label, the label is placed onto the message.
That subtle-seeming distinction is actually quite significant. What it means is that a message doesn’t have to be associated with only one label, as is typically the case with folders; rather, you can apply as many labels as you want to any message, and each one ends up acting like a sticker — a label, one might even say! — that sits atop the email along with any other labels you’ve applied.
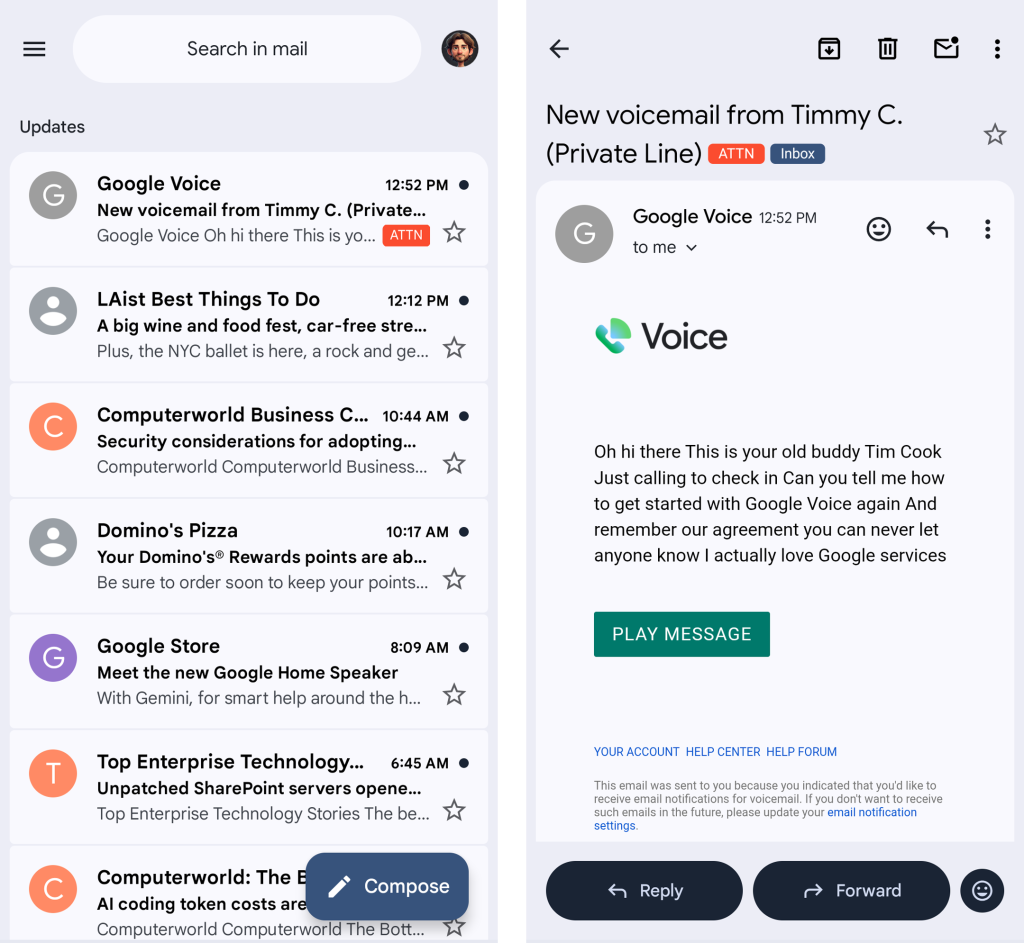
Any labels associated with an email will show up both in your inbox and when viewing the message in full.
JR Raphael / Foundry
So, for instance, if you keep tabs on stats for your company’s website, you might label all incoming emails from Google Analytics as “Web Reports.” But maybe you also have your own personal website for which you receive Analytics updates. You could label the reports from your personal website as “Web Reports,” too, and then add a second label of either “Work” or “Personal” onto every message to create a distinction between the two types.
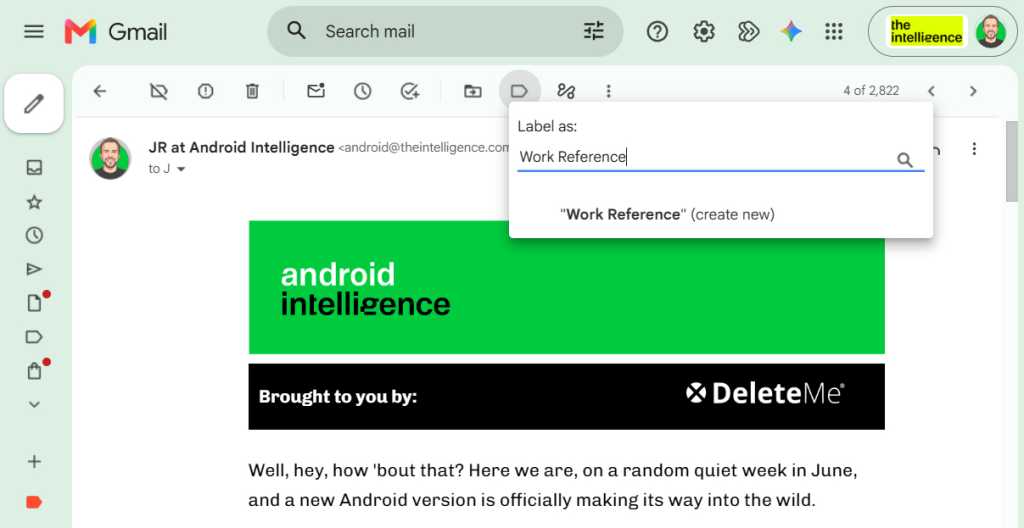
On the Gmail desktop website, the easiest way to create a label is to click the label icon in the toolbar at the top of the screen when you’re viewing a message or when you’ve selected something from a message list — then start typing whatever name you want to use for the label. Once you’re done, simply hit Enter, and Gmail will create the label for you and apply it to the message.
Once you create a new label within Gmail, it’ll always show up as an option in the future.
JR Raphael / Foundry
The next time you click the label command, you’ll see your newly created label as an option.
You can also perform the same action by using the keyboard shortcut L while an email is open or selected, provided you’ve enabled Gmail’s keyboard shortcuts system.
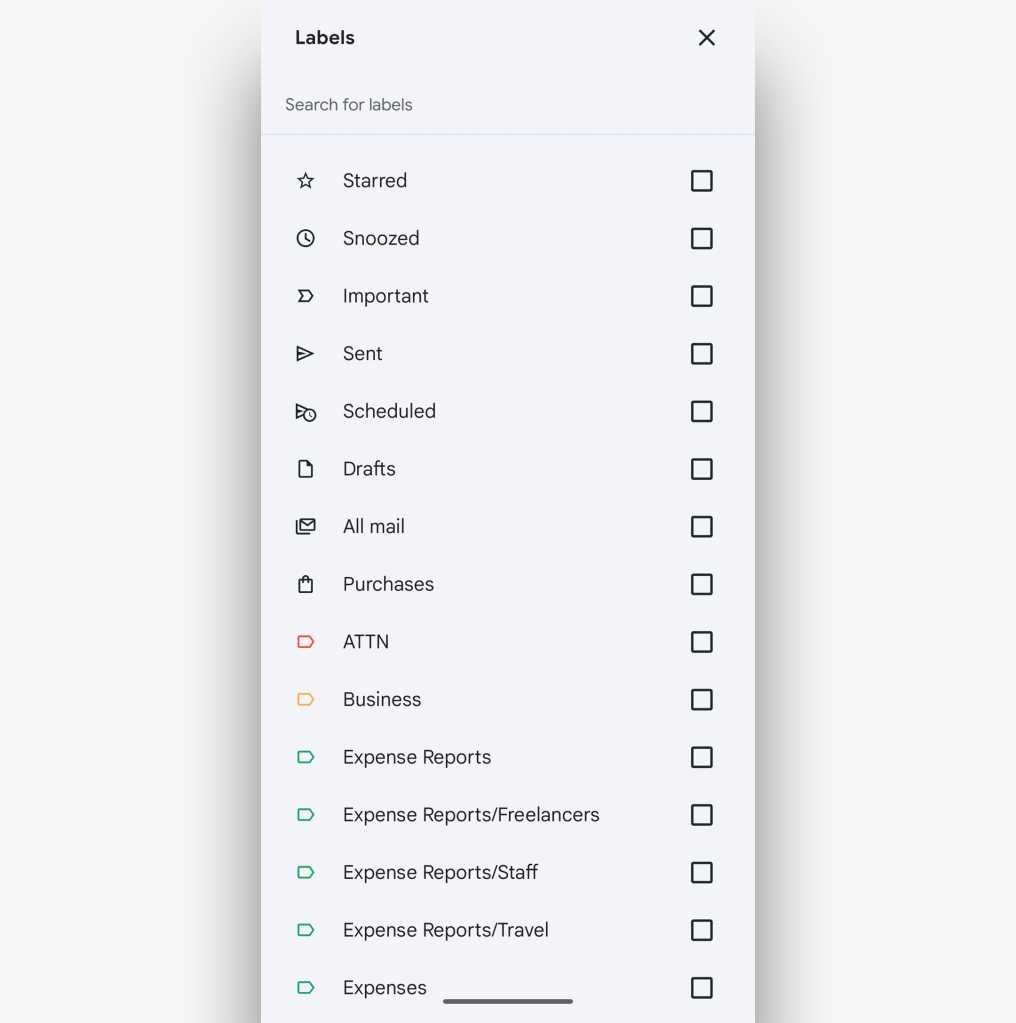
On the mobile front, you can create a new label within the Gmail app for Android or iOS by tapping the three-line menu icon in the upper-left corner of the screen and then looking for the “Create label” option before the list of existing labels (on Android) or the “Create new” option directly after that list. You can apply an existing label onto a message, meanwhile, by looking for the “Label” (on Android) or “Label as” (on iOS) option in the main three-dot menu anytime an email is open or selected.
2. Save yourself a step and label while archiving
Here’s a handy command to remember: If you want to add a label to a message and simultaneously dismiss the message from your inbox, use Gmail’s “Move to” option.
On the desktop website, that’s the icon showing an arrow inside a folder, directly to the left of the regular label icon. On both Android and iOS, you can find the same command within the three-dot menu icon while any email is open or selected. You’ll see a list of options that include your labels; just select the label you want to assign to the message.
Whatever platform you’re using, that’ll handle all the steps for you in one fell swoop. And if you’re a fan of shortcuts like this, by the way, I’ve got a whole story dedicated to time-saving Gmail tips just like ’em.
3. Apply labels while you’re composing an email
Gmail labels aren’t only for incoming messages; you can also proactively apply them to a new message you’re composing and then know that that email and any replies associated with it will remain properly organized and present in all the right places.
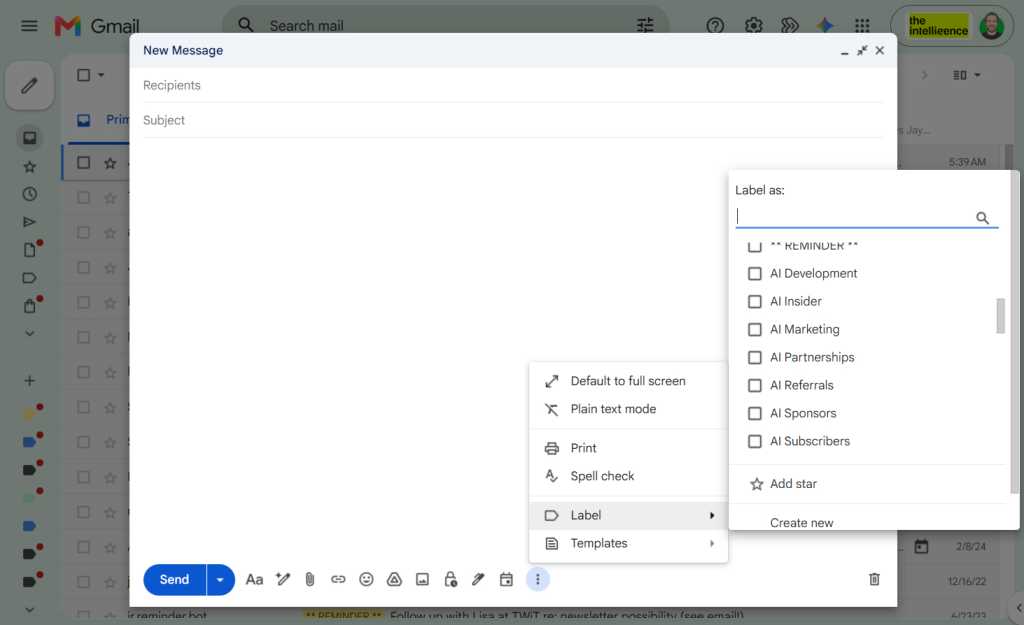
On the Gmail desktop website, all you’ve gotta do is hit the three-dot menu icon in the service’s compose window and look for the “Label” option in the list that appears — then create a new label right then and there or select any existing label to apply it.
You can proactively apply a label while composing a new message.
JR Raphael / Foundry
The mid-composing label-adding option isn’t present in the Gmail mobile apps, unfortunately, but you can accomplish the same thing in a roundabout way by heading into your Sent messages (from the app’s main three-line menu) and then selecting or opening an email to add a label onto it right after you’ve sent it.
4. Organize your label lists
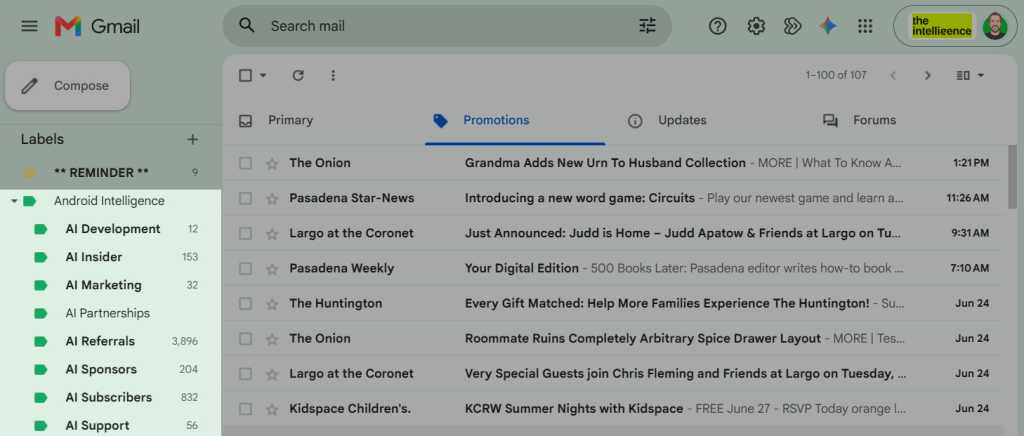
All right, so you’ve got your messages labeled — now what? Well, first, you can always browse through your labels to find something you need. Gmail keeps your list of labels (in alphabetical order) in its left sidebar, on the desktop website. You can collapse or expand that sidebar by clicking the three-line menu icon in the upper-left corner of the screen, and you can click on any label in the list to see all of the messages associated with it.
By default, though, that list is probably quite the unruly mess. So let’s get it organized:
First, if you see a line in the list of labels that says “More,” with a downward-facing arrow alongside it, click it to expand your full list of existing labels.
Now, click the three-dot menu icon next to each one of your labels. (The three-dot icon appears only when you hover over a label.) Assign each label a color, if you’d like; that’ll make it more visually distinctive and give it more or less emphasis (depending on the color you choose) when it appears in your inbox.
In that same three-dot menu, look at the “In label list” section and consider if you want the label to always appear in your label list, to remain permanently hidden beneath that “More” divider, or to appear in the list only when unread messages are present within it. The less unnecessary clutter you have visible, the easier it’ll be to find the labels you actually use often.
Next, look at the “In message list” section and think about whether you want the label to show up as an option when you’re adding a label onto a message. If it isn’t a label you ever actively apply to messages, you might consider hiding it to reduce clutter and increase your efficiency in that area.
On Android or iOS, you can find your labels and browse through any of ’em by looking inside the Gmail app’s main three-line menu. On Android, a third-party app called eLabels can also let you make more advanced label modifications from your phone or tablet — but in general, those sorts of adjustments are most easily managed from the Gmail desktop website.
5. Combine related labels into groups
While we’re getting your labels organized, take a moment to mull over whether any of your labels would make more sense as sublabels within a broader category. Maybe, for instance, you’d have one label called “Expense Reports” and then sublabels within it for “Staff,” “Freelancers,” and “Travel.”
This is an adjustment you’ll absolutely want to make on the Gmail desktop website, where the full selection of label customization commands is readily available. You can find the option to create a sublabel by clicking the three-dot menu icon next to any label name within the site and then selecting “Add sublabel” from the list that appears.
Grouped sublabels are a great way to keep your Gmail labels list tidy.
JR Raphael / Foundry
Just note: Somewhat confusingly, sublabels and parent labels are treated as separate but related entities — so if you were to add a message to “Staff” in our previous example, its label would show up as being “Expense Reports/Staff.” The message wouldn’t, however, show up when you click “Expense Reports” in the left-of-screen label list; it’d appear only when you clicked “Staff” in that same section. If you wanted it to appear within the results for both the parent label and the sublabel, you’d have to add both of them onto the message.
6. Use labels for smarter searches
Gmail’s labels aren’t just for browsing; you can also use them as variables to narrow down a search and make it faster to find a message you need. To include a label as a variable in a search, just click or tap the Gmail search box at the top of the website or mobile app, type label:work (using the name of your actual label name in place of “work,” of course), and then type in any other term or variable you want.
If you were trying to find a travel-related expense report from Tim Cook’s trip to Chicago, for instance, you could type label:travel from:tim@apple.com chicago into the search box. Including the label would narrow down your search considerably — skipping over messages from Tim Cook that might’ve just mentioned Chicago in some other context — and let you get to what you need more efficiently.
You can even narrow down your search further and search for messages that contain multiple specific labels — like label:travel label:work, which would show you a list of all messages that have both of those labels in place.
And on the mobile front, you can make your life easier yet by tapping the “Labels” dropdown within the app’s search area. That’ll let you simply select from a list of available options and save yourself the trouble of manually typing anything in.
In the Gmail mobile apps, you can select from a list of existing labels instead of typing in a search.
JR Raphael / Foundry
Gmail actually treats many of its own built-in message designations as labels, too — so in addition to searching for your own custom labels, you can search for (and in some cases also find within the mobile app dropdown menu) things like:
label:inbox
label:unread
label:promotions
label:social
label:starred
label:muted
Beyond that, you’d never know it, but Google also supports a hidden series of advanced Gmail labels for automatically identifying emails related to areas like travel, purchases, and finance.
And finally, any recent past searches you’ve conducted will show up as suggestions whenever you tap or click in the search box, which makes it especially convenient to revisit any frequently accessed label-related explorations in the future.
7. Let Gmail apply labels for you
Here’s where things really start to get interesting: In addition to manually applying labels to messages as you see fit, you can train Gmail to automatically categorize and process messages for you.
The first step is to think about what factors would make an incoming message fit into a particular label — whether it’s the sender’s email address or domain name, a specific word or phrase in the subject line, or maybe even the address to which the message was sent.
In my own inbox, for example, Gmail applies a red “VIP” label to emails that arrive from editors or other contacts whose messages tend to be timely and important. And it applies a green “Invoices” label to messages that come in from a specific address and with certain subject lines that my accounting software uses for carbon copies of new invoices.
In some cases, like with the “VIP” label, the messages remain in my primary inbox. But in others, they end up moving to less attention-demanding places — like the invoice copies, which skip over my inbox entirely (since I’m keeping them mostly as records and don’t need to be bothered dealing with them every time they come in).
Once you decide what factors should apply to what label — and what else should happen once the label is applied — a Gmail filter is the key to making the magic happen. I outlined the exact steps to setting one up in my separate Gmail filters guide. Go have at it!
8. Let your labels limit your notifications
Last but not least, instead of getting distracting alerts for every new message that lands in your inbox — or going to the opposite extreme and not getting any email notifications whatsoever — use your Gmail labels as a way to control which messages alert you.
You can pick any label that seems notification-worthy and then limit your notifications only to messages with that label attached. You can even set up label-driven notifications to function on your desktop computer and on your mobile device. (Provided you use Android, that is. Sorry, iPhone folks, but Apple’s garden doesn’t allow this level of customization to fly.)
That’s exactly what I do with my aforementioned “VIP” label, in fact. And it’s actually quite easy to set up. I put together a step-by-step guide here.
And with that, my inbox-dwelling comrade, your label education is complete. Go ahead: Label yourself organized. You’ve earned it.
This article was originally published in November 2019 and most recently updated in September 2026.
Bending Spoons has snapped up Airtable to add to its portfolio of software companies, alongside AOL, Evernote, WeTransfer, Brightcove and Vimeo
Airtable made its name as a builder of low/no code database services, aimed particularly at non-technical staff, but is now one of many vendors facing financial difficulties in the face of the SaaS/AIpocalypse. The arrival of AI coding tools, which offer non-technical employees more flexible ways to build business applications, has hit demand for its services.
Bending Spoons bought Airtable in a deal it valued at just $1.285 billion, a far cry from the $11.7 billion Airtable was worth at its peak.
Bending Spoons has built its portfolio by buying once-successful companies like Airtable that have struggled to cope with newer, nimbler competitors or failed to adapt to emerging technologies. Bending Spoons takes these companies, cuts costs and markets them aggressively with the goal of returning them to profitability.
“Airtable is a pioneering brand reshaping how teams organize data and manage critical workflows. We’re committed to investing in Airtable for the long run, and doubling down on its core strength: bringing teams and workflows together in one flexible workspace. We plan to expand what can be done across the full spectrum of work and make Airtable even more valuable to customers at every scale,” said Luca Ferrari, Bending Spoons CEO and co-founder.
We live and work in browsers. It’s where we spend most of our time — and it’s where we waste most of our time as well. Web browsing is slow, inefficient, and full of time-sapping annoyances.
But it needn’t be that way. You can turn your browser into a lean, mean productivity machine. To do it, just follow these tips for Microsoft Edge in Windows 10 or 11. You’ll learn how to switch between home and work profiles, put idle tabs to sleep to speed up your PC, tap into the power of Microsoft’s Copilot AI assistant, and more.
(Note that these tips are written for the most recently updated version of Edge in Windows 11 25H2 and Windows 10 22H2. Things may be slightly different if you use a different Windows version, and not all of these features are available for Edge on macOS or other platforms.)
So let’s get started — time’s a-wasting, and so is your productivity.
1. Switch between work and personal profiles
With remote and hybrid work models now common, many people use the same device for work and personal use. When it comes to using a web browser, that can quickly become problematic.
Mixing work and personal favorites makes it far more difficult to quickly get to important work websites or personal websites. When you’re working, you don’t want to wade through hundreds of links to family photos, vacation destinations, and YouTube videos of cats befriending parrots when you’re just looking for the OSHA website about mine safety regulations. And when you’re off working hours and want to watch a video of a Persian cat nuzzling a cockatiel, a website detailing the GDPs of every country in Europe and Asia is not your primary destination.
Different profiles let you completely segregate your browser use. That doesn’t just mean different favorites. It also means different Collections, different extensions, different passwords, and more.
Each Edge profile is tied to a different Microsoft account. So to use different profiles, you’ll need to create different Microsoft accounts. To create a new Microsoft account in Windows 10 or 11:
Scroll down to the button that says Create an account, click it, and follow the prompts to create a new account.
On the page that appears, click the Sign in button in the middle of the page. On the screen that appears, select the Create one! link, then follow the prompts to create a new account.
You’ve now got two different Microsoft accounts you can use for Edge. When you log into one of those accounts in Windows, that will be the default account that Edge will use when you browse the web.
To switch between the two accounts, you’ll need to add that second account to Edge. To do it:
Click the user profile icon at the top right of Edge. On the small pane that appears, select Set up a new profile, then select either Personal or Work or School.
You’ll be sent to a web page in a new instance of Edge. Click the Sign in button at the far right, then select Sign in to sync data.
On the screens that appear, sign in and confirm that you want to proceed.
Once you’ve done that, you don’t have to log out of your current account and then log into the second account to use it in Edge. Instead, when you want to use the second account, click the user profile icon at the top right of the Edge window. A small pane appears with your current profile at the top. To switch to your other profile, select it in the “Other profiles” section.
To minimize distractions, set up work and personal profiles in Edge.
Preston Gralla / Foundry
You’ll now be sent straight to that profile. When you do that, Edge will open in a new window. So you’ll have both your profiles running simultaneously, each with its own tabs, in two separate windows. (Note that you can set up multiple additional profiles.)
You can also tell Edge which profile to use when you visit certain websites. To do it:
Click the user profile icon in Edge and select Profile settings. (Alternatively, you can click the three-dot icon next to the user profile icon and select Settings > Profiles.)
In the “Profile settings” area, click Profile preferences.
At the bottom of the “Automatic profile switching” section on the page that appears, click Add site next to “Custom site switch.”
On the “Add site” popup, enter a website URL and select the profile you want to switch to for that site.
Should you decide you want to remove a profile, go to Settings > Profiles and scroll to the “More profiles” section. Click the trash can button next to any profile you want to delete. You can always add it again later using the steps above.
2. Get to your most-used sites quickly
Bookmarking and organizing favorites is a great way to manage a large collection of websites, but it’s not that useful if you simply want to get to a frequently used site quickly. Edge has some tricks up its sleeve if you want to get your most-used sites pronto.
Add a site to the new tab page
When you open a new tab in Edge, a page appears that shows you news and other items you might be interested in. It’s easy to pin a site to this page so it’s accessible whenever you open a new tab.
Look toward the top of the page, just underneath the search box. If you don’t see icons for pinned pages (such as for Yahoo, Amazon, your inbox, and so on), click the settings icon on the upper right of the page (it looks like a gear) and turn “Quick links” on.
A row of site icons appears, along with a + icon. Click the + icon and type or paste in the name and URL of the site you want to pin, then click Add. The site will now appear along with the other pinned pages.
Pinning a site keeps it handy on the new tab page.
Preston Gralla / Foundry
You can rename or remove any site pinned to the new tab page by clicking the three-dot icon next to the site icon and selecting Rename or Remove from the menu that appears.
The new tab page is tied to your current profile, so you can set up different pinned sites on the new tab page for each of your profiles.
Pin tabs to the top of Edge
For even faster access to frequently used sites, you can pin them as browser tabs so they appear at the far left of all your other tabs in Edge. When you’re on the site you want to pin as a tab in Edge, right-click its tab and select Pin tab from the menu that appears. The pinned tab will now appear to the left of all your open tabs.
The icon for the pinned tab looks smaller than all of your other tabs, and it will persist even after you shut down and restart Edge. If you have multiple pinned tabs, all of them will appear to the left of any non-pinned tabs.
Like pinned sites on new tab page, your pinned tabs are unique to each Edge profile; they won’t carry over from profile to profile.
Pin sites you often visit to the Windows taskbar
For Windows users, the fastest way to access a frequently used site is to pin it to the Windows taskbar. That means it’s always visible (even when Edge isn’t running), and you can launch it with a single click.
When you’re on the site you want to pin, select the three-dot icon at the top right of the browser window and select More tools > Pin to taskbar. A small screen appears with a text box in it with the name of the site. Use the name provided or type a new name into the text box and click Pin.
3. Create tab groups for more efficient browsing
If you’re like lots of people, you frequently browse with many tabs open, and find yourself wasting time switching to the tab you want because of all of the clutter.
There’s a simple fix: group tabs into categories so you can quickly switch to the tab group that has the tab you want. For example, you might group them into “News,” “Museums,” “Finance,” and so on. Or you could create a tab group for research related to a specific project.
To do it, right-click a tab, select Add tab to new group, and then name the tab group. You can then drag other tabs into the group. You can also assign each tab group a unique color so they’re easy to differentiate at a glance.
Creating tab groups makes it easier to find the tab you want quickly.
Preston Gralla / Foundry
If you’ve already created a group, when you right-click a tab, you’ll see “Add tab to group” rather than “Add tab to new group.” When you click the arrow next to it, you’ll see a list of all your existing groups, so you can easily add it to any of them. You’ll also see “New group,” which will let you create and customize a new group.
Once you’ve created a tab group, you can rename it, change its assigned color, add new tabs to it, ungroup the tabs from it, delete the group and all the tabs in it, and more. Just right-click the name of any group and select an option from the menu that appears.
4. Enlist a Copilot as you browse
Microsoft’s genAI chatbot, Copilot, has become increasingly integrated with Edge, so much so that Microsoft now calls Edge an “AI browser.” At the moment, that’s more hype than fact, but it is true that Edge gets new Copilot features added on a regular basis.
Edge provides a couple of ways to interact with Copilot, one of which is to open the Copilot sidebar to the right of the main browser window. (We’ll go over the other method later in the story.) Click the Copilot icon at the top right of Edge, and the Copilot pane appears. Here’s where you type in prompts for Copilot.
There’s a tremendous amount you can do with Copilot, most of which is beyond the scope of this article. To learn more about what it can do and how to use it, see our story “9 ways to use Copilot right.”
However, here’s one use designed specifically for web browsing: summarizing the contents of the page you’re currently visiting. Depending on the structure and content of the page, Copilot can give a high-level overview of the entire page, provide capsule descriptions of individual articles or sections, and more. You can also ask Copilot to extract specific information from a page, such as all the AI-related information on it, and organize the information into a bulleted digest.
To do all that, open a web page and open the Copilot sidebar. You’ll see a few suggested prompts, one of which should be related to summarizing the page, such as Summarize the main points on this page or Create a summary of this page. Click the prompt, or if you don’t see it, type it into the text box at the bottom of the Copilot pane.
Use Copilot to summarize the content on a web page.
Preston Gralla / Foundry
You can also ask it to summarize the last page you’ve visited. Click the down arrows towards the bottom of the Copilot pane, and you’ll see a listing for the previous page you’ve visited, such as Computerworld.com. Click the text summarize my recent activity on [page] and it will do that for you. Again, if you don’t see that text, type it into the Copilot text box.
The summarization feature, though, still has rough edges, or at least it did when I was writing this article. If you leave the web page you’re currently on and go to a new one, the summary of the old page remains, and there isn’t an immediate way to summarize the new one. To get a summary of the new page, you’ll have to scroll to the bottom of the Copilot pane, click the arrow (it will be facing either up or down, depending on whether you’ve previously clicked it) and click “Create a summary of this page.”
In that section, you can also click listings of your other open tabs and get summaries of any of them.
5. Remove clutter when you launch new tabs
When you create a new tab, the initial page is filled with pinned sites, suggested news stories, widgets, and more. If you find that page distracting, you can change it to a much cleaner, more stripped-down page.
If you haven’t pinned specific sites to the row of icons below the search box (see tip #2 above), you can make Edge’s default icons go away: Click the gear icon on the upper right of the page, and a “Page settings” panel pops up. In the “Quick links & search” section, click the dropdown next to “Quick links” and select Off. That gets rid of the icons for web sites just beneath the search box.
If you have pinned your own preferred sites there, you’ll want to leave quick links enabled, but you can turn the “Show sponsored links” toggle to Off to get rid of ads.
To get rid of the news articles that overwhelm the page, go to the “Show content” area of the panel and move the “Show feed” toggle to Off. Or, if you want to really strip down the page, move the “Show content” toggle to Off. That kills pretty much everything on the page except the weather. If you don’t want to see that either, scroll down a bit more and move the “Weather” toggle to Off.
Going with the stripped-down new tab look in Edge.
Preston Gralla / Foundry
You can also strip out the background graphic for the new tab page by turning off the “Background” toggle. I don’t recommend it, though, because when you do that, you’ll get a gray page with a big Microsoft logo dead center when you launch a new tab.
6. Launch Copilot-centered new tabs
If you’re a frequent Copilot user, you might want to take a different approach to the new tab page.
The Copilot you get in a side pane when you click the Copilot icon at the top right of Edge is a somewhat stripped-down version of Microsoft’s full-blown Copilot app. If you’re looking to use the full-fledged version, there’s a simple way to do it: Tell Edge to open Copilot every time you open a new tab.
To do it, click the three-dot icon to the left of the Copilot icon at the top right of Edge and navigate to Settings > Start, home, and new tab page. In the “New tab page” section, turn on the Copilot new tab page toggle. From then on, every time you open a new tab, you’ll launch a full Copilot screen that’s similar to the standalone Copilot app.
The Copilot new tab page puts Copilot chat front and center.
Preston Gralla / Foundry
You’ll see the usual Copilot prompt box front and center, and beneath that, several prompts Microsoft thinks you might want to use. (Note to Microsoft: I’ve never used one of those suggestions even once. I’d guess few other people have either.)
What’s really new here are the vertical icons running down the left side of the page. Here’s a brief rundown of what each one does:
Open sidebar: Widens the navigation bar and shows a list of your recent chats so you can revisit any of them.
New chat: Start a new chat with Copilot.
Library: Build a library of Copilot-created content such as images, reports, podcasts, documents, and more.
Tasks: Create a Copilot task that automates something you want done, such as sending you a weekly email about a company’s stock price.
Health: Open Copilot Health, a version of Copilot designed specifically for getting health information.
Shopping: Use Copilot as a shopping assistant.
Imagine: Create or edit an image using Copilot.
Experiments: Discover and use new Copilot features that Microsoft is testing but that may or may not be officially launched at some point.
Clicking the Copilot icon at the top of the list of vertical icons returns you to the main Copilot interface you get when you launch a new tab.
As you can see, many of these new Copilot functions are aimed at consumers and unlikely to be useful in a business setting. Still, if you frequently turn to Copilot for help, you might find the Copilot new tab page a good alternative to the standard new tab page.
And note that setting up the Copilot new tab page doesn’t prevent you from browsing or searching the web normally. Just enter the search term or website you want to visit in the address bar at the top of the screen.
7. Put tabs to sleep to conserve system resources and boost battery life
If you’re like most people, you keep multiple tabs open in Edge so you can easily switch among the sites, web apps, and information important to you. It’s a great time-saver.
But it can also be a big memory and processor hog, which can slow down both your browsing and your other computing tasks. It needn’t be that way, though. You can put inactive tabs to “sleep” until you need them, freeing up resources, which will make your PC speedier and make its battery last longer, even when you have multiple tabs open. Microsoft claims that putting inactive tabs to sleep reduces memory use by an average of 32% and CPU use by an average of 37%.
Here’s how to do it:
In Edge, click the three-dot icon on the upper right of the screen and select Settings > System and Performance > Performance.
In the “Memory” section, move the slider to On next to Automatically put tabs to sleep.
To change the length of time it takes to put an inactive tab to sleep, below “Automatically put tabs to sleep” click the drop-down arrow and select a time. Your choice is anywhere from 30 seconds to 12 hours.
Putting tabs to sleep can significantly reduce CPU and memory use.
Preston Gralla / Foundry
To reawaken any tab that’s been put to sleep, simply click on it, and it will resume normal activity.
There’s a chance that some sites might not work properly after they’ve been put to sleep. If that happens to you, you can tell Edge never to put that site to sleep again. To do it, scroll up to the “General” area on the “System and performance / Performance” page of Settings. Click the Add site button next to the “Always keep these sites active” item and paste in the URL of any site you don’t want to sleep.
8. Reduce power use with ‘energy saver’
Browsers can be power hogs, especially if you have multiple tabs open and are playing videos or music in them. That can be a particular problem if you’re using a laptop that isn’t plugged into a power source.
In Edge, the “energy saver” setting reduces the amount of system resources the browser uses, which extends your PC’s battery life. If you enable energy saver, it becomes active when your laptop is unplugged. Microsoft claims energy saver can give you on average an extra 25 minutes of battery life. To use it:
In Edge, click the three-dot icon on the upper right of the screen and select Settings > System and Performance > Performance.
In the “Power” section, make sure the toggle next to “Enable energy saver” is turned on. When you do that, you see two options: “Balanced” and “Maximum savings.”
Select Balanced if you want your laptop to go into a lower-power mode to save battery life when your laptop is unplugged or has a low battery. Select Maximum savings if you know you’re not going to be able to plug your laptop in for some time. Note that in this mode, your video quality may be affected.
There’s also a separate option to use energy saver even if your laptop is plugged in. Use this option if you want to consume less energy when you use your computer. Note that if you use it, you may experience slowdowns when browsing the web.
You can get an extra 25 minutes of battery life with the energy saver setting, Microsoft claims.
Preston Gralla / Foundry
9. View and mark up PDFs
With Edge, there’s no need to launch a separate application when you want to read or mark up a PDF; its built-in PDF app is quite good. With it, you can draw on and highlight sections of the PDF and erase the marks you made as well. So save yourself time and use Edge rather than third-party software.
You don’t need to do anything to read a PDF online. Simply click it, and by default it will launch in Edge’s reader. You’ll find the markup tools, including for drawing, highlighting, and erasing, in a toolbar towards the top of the screen. To open a PDF from your hard disk, when you’re in Edge, press Ctrl-O, then navigate to the PDF and click it.
Edge has a surprisingly useful PDF viewer with markup tools.
Preston Gralla / Foundry
If you prefer to use your own PDF reader, even for PDFs found online, you might be annoyed that every time you click a PDF, it opens in Edge’s PDF reader. You can change that, though, by changing your default PDF reader.
In Windows Settings, select Apps > Default Apps and in the search box at the top of the screen just below “Set a default for a file type or link type,” type in .pdf. After you do that, the listing “Microsoft Edge Microsoft Edge PDF document” appears. Click it, and a screen appears showing you all the applications on your PC that can read PDFs. Select the one you want to use instead of Edge.
10. Turn on Edge’s AI-powered ‘scareware’ blocker
The internet is filled with scammers using sophisticated attacks to steal your data or money. A common one is so-called “scareware,” in which when you visit a website, your PC is suddenly locked into full-screen mode filled with fake malware warnings that claim your computer has been infected and urge you to call a phony tech-support line or allow remote access to your device to supposedly fix the problem.
Once you do that, the scammers steal your data, get you to pay for phony solutions, or embed malware on your system.
To fight that, Edge includes an AI-powered scareware blocker that builds and constantly updates a machine-learning model that detects suspicious behavior and stops the scamware in its tracks.
Typically, the scamware detector is turned on, but there’s a possibility it’s been turned off at some point or was never turned on in the first place. For example, on PCs with only 2GB of RAM or fewer than 5 cores, it’s not turned on by default. Microsoft recommends enabling it on those machines. To do it, in Edge go to Settings >Privacy, search, and services > Security, and in the “Scareware blocker” setting, turn the slider from off to on.
When you do that, make sure that “Block sites detected as scams” and “Share detected scam sites with Microsoft Defender SmartScreen” are turned on as well.
Turn on Edge’s scareware blocker to protect yourself from scams and data theft.
Preston Gralla / Foundry
11. Use Edge’s one-click form filler
How many hours a week do you spend mindlessly filling out web forms — your office or home address, shipping address, email address, and phone number? Wouldn’t it be nice to get that time back?
With autofill, built into Edge, you can. To use it, in Edge go to Settings > Passwords and autofill > Addresses and more. Turn on the toggle next to “Save and autofill addresses.” You can also choose to have Copilot analyze web forms and decide which bits of your information belong in which part of the form.
Microsoft autofill saves information that can be used to fill out forms online.
Preston Gralla / Foundry
From now on, whenever you visit a web form, just click in a text box, and your information will appear in a popup. Select it and the form will fill in. You can go back to Passwords and autofill to change any information you want.
12. Save time with keyboard shortcuts
There’s a good chance you use keyboard shortcuts for some of your office applications, like Word and Excel — and you likely use some for Windows itself.
But when it comes to browsers, many people forgo the keyboard except when absolutely necessary. That’s too bad, because keyboard shortcuts are a big timesaver. So to improve your productivity, check out these keyboard shortcuts for Edge in Windows. (Mac users can generally substitute the Cmd key for Ctrl and the Opt key for Alt.)
An “AI worm” can spread through Microsoft Word documents using Copilot as a vector, a prominent Norwegian AI researcher reported on Tuesday.
The report from Håkon Måløy, later confirmed by Microsoft, said that an attacker can conceal instructions in a document that is later used as source material for Copilot-generated or Copilot-edited Word documents, for example, as input to a financial report. Those malicious instructions could potentially alter figures in the document being created. They then copy themselves into the new document, causing it to become a carrier of the attack when used in another Copilot-assisted workflow.
Måløy noted: “To my knowledge, this is among the first public demonstrations of document-borne AI-worm self-propagation through normal workflows in a mainstream commercial productivity suite.”
Microsoft on Thursday emailed a statement to CSOonline discussing the report’s revelations.
“We have addressed the findings reported by the researcher and thank them for working with us through coordinated vulnerability disclosure. To address this class of risk, we use a defense-in-depth strategy with safeguards that block malicious instructions at multiple points and help keep tasks aligned with users’ requests,” Microsoft said.
“We are continuously strengthening these safeguards as the technology and threat landscape evolve,” it added. “We encourage customers to install the latest updates, use multiple layers of security protection, treat content from unknown sources with caution, and review AI-generated content before using or sharing it.”
Sidesteps defenses
Aman Mahapatra, chief strategy officer for Tribeca Softtech, a New York City-based technology consulting firm, has reviewed the mechanisms used in this vulnerability and says that it is much worse than it might seem, because it will sidestep just about every defensive mechanism enterprises have in place today.
“This is a worm, a self-propagating malware pattern that uses Copilot as the transmission mechanism and legitimate corporate collaboration as the delivery channel. It bypasses every traditional email security control because the document is not malicious on delivery and it becomes malicious when Copilot processes it. That means that it bypasses DLP because the exfiltration happens through the user’s own authenticated Copilot session,” Mahapatra said. “It then bypasses endpoint protection because no code executes, only instructions get followed by an AI service the enterprise has explicitly authorized.”
He also noted that researchers have been warning about this class of attack for two years.
Microsoft’s involvement
Måløy said that he has been working with the Microsoft Security Response Center (MSRC) since March 3 and Microsoft subsequently implemented and distributed multiple small focused mitigations, but the core vulnerability has yet to be fixed.
He said he was hesitant to disclose an active vulnerability, but felt that it was now time to publish.
“My reasoning is that defenders cannot reduce exposure to a risk they are unaware of,” Måløy wrote, “and the propagation mechanism described here affects ordinary document workflows that many organizations already rely on.”
In an email interview, Måløy noted that the tweaks Microsoft has implemented were helpful, nonetheless.
“The coordinated disclosure process showed that mitigations can meaningfully reduce the demonstrated attack surface, making attacks less reliable and limiting their reach, even without completely eliminating the underlying problem,” he said.
Måløy also addressed the resolution that many analysts and consultants suggested, which is to change the nature of LLMs to fully isolate instructions from the data they operate on.
“Separating instructions from data may be part of the solution, but I think the distinction between data and instructions is not always clear in real-world workflows. For example, a user may ask an agent to arrange a business trip, requiring the agent to retrieve an email specifying the approved itinerary and a document containing the booking procedure,” Måløy said.
“My view is that the broader challenge is therefore not simply to prevent systems from interpreting external content as instructions, but to evaluate whether those instructions align with the user’s goals and the context in which the system is operating,” he added.
Problem hard to overstate
Mike Wilkes, enterprise CISO at Aikido Security, said it would be difficult to overstate the potential problems from this situation.
“This is a significant issue because it moves prompt injection from a single compromised interaction into a potentially self-propagating document integrity attack,” he said, noting that it is not a conventional worm that spreads automatically. A user or Copilot workflow must still bring an infected document into the model’s context. “But once that happens, the malicious instructions can reportedly alter business information, conceal themselves inside the resulting Word document and turn a legitimate internal file into the next carrier,” he said.
That, he pointed out, creates “a dangerous enterprise supply chain in which financial reports, contracts, policies and partner documents may inherit malicious behavior while retaining the trust associated with their legitimate authors and Microsoft 365 accounts.”
Not a new issue
The key issue behind this flaw is the fact that genAI tends to struggle with telling the difference between data that a user offers as input and the instructions the AI is to execute.
Flavio Villanustre, CISO for the LexisNexis Risk Solutions Group, observed that the same problem with mixed data and instructions occurred in databases decades ago, and turned into what we know as SQL injection attacks today. But, he noted, a few years later, parametrized binding for the database access layers was developed, which separates instructions, which are handled internally and safely, from data, which can come from untrusted sources. “The same needs to happen with LLMs and other AI,” he said.
Mike Leone, a VP/principal analyst at Moor Insights & Strategy, agreed.
“It’s hard not to chuckle a bit with this one. People have been asking whether data can give orders since SQL injections. We fixed that one by giving the database a way to tell an instruction from a value,” Leone said. “Thirty years later, we’ve built an entire category of software that can’t tell the difference at all.”
Tom Findling, CEO at Conifers.ai, also said he sees the data-vs-instructions issue as the biggest problem.
“Separating data from instructions is still unsolved at the model layer. The labs are making real progress, but not enough to be your only control,” he said, and stressed, “Microsoft doesn’t need to wait for that. It can slow propagation inside Copilot: stop hidden content from being written into new documents, surface hidden text before it’s used, preserve the trust level of what Copilot read and show all AI-generated changes.”
Fix needs industry agreement
However, Frank Dickson, group VP for security at IDC, argued that a fix needs industry agreement.
“A fundamental fix requires the industry to converge on the same architectural change, which isn’t happening anytime soon given the incentives and the fact that the major players are far from besties,” he said, pointing out that Instruction-data separation would need to be baked in at the model or platform level across every major vendor. “None of them are rewarding that work commercially right now, so treat that as a multi-year research problem, not something a CISO should wait on.”
Leone disagreed, arguing that a single vendor can do quite a bit, at least for its own customers.
“Microsoft has said publicly since last year that indirect prompt injection can’t be fully prevented, and I give them credit for saying it out loud rather than pretending otherwise,” Leone said, noting that the industry doesn’t have to move in lockstep. “This attack lives inside one product,” he said. “If Microsoft hardens the Copilot document path, Copilot customers get safer whether or not anyone else moves.”
Dickson added that another critical problem with this vulnerability is that the carrier documents are created by legitimate employees using legitimate tools, “so there’s no obvious point of origin once the payload starts moving; an organization could be laundering corrupted financial figures through its own workflow for weeks before anyone notices.”
Tactics that might help
That said, experts had some specific suggestions for CISOs trying to negate this problem.
IDC’s Dickson said, “the most useful lever right now sits outside the model entirely, in how much untrusted content Copilot is allowed to pull into a session without a human choosing it.” He noted that enterprises can turn Copilot’s auto-discovery behavior off or restrict it, and require humans to explicitly select the documents they feed it. “That alone closes off one of the two ways the attack gets a foothold,” he said.
IDC also suggested a visible diff or redline of anything Copilot changes in a financial or otherwise consequential document, and the requirement for a human to approve the changes. “That’s not a technical fix, it’s a workflow one, and it’s available today,” Dickson said.
He said that IT should also track where content came from and what was touched by an AI system, in metadata that travels with the document. “It doesn’t stop the injection, but it means when something does get through, an organization can actually trace how far it spread instead of discovering a corrupted number three reports later with no way to reconstruct the chain,” he said.
However, one expert, Tyler Reguly, Fortra’s associate director of security R&D, said that he didn’t see this vulnerability having a meaningful impact because it feels like what he called a “laboratory vulnerability.”
Normal enterprise workflows don’t encompass a number of the necessary steps for compromise, he said, pointing out that, if anything, people are trained not to download Word documents. Plus, he noted, looking at the blurred example in the report, the malicious document contained an additional apparently blank page which held the concealed prompts in white text.
“That page is going to send up warning signs for me if someone even managed to convince me to download an external Word document,” he said. So, overall, “this feels like it requires a perfect storm.”
Traveling enterprise employees beware: Think twice before you log onto that oh-so-convenient public Wi-Fi.
Since at least June, threat actors have been compromising “captive” Wi-Fi gateways and other portal appliances at hotels, conference centers, and similar shared venues to hijack users’ Microsoft 365 accounts, according to the ReliaQuest Threat Research team.
Once a threat actor controls a gateway, they can silently redirect a user’s traffic to their own infrastructure and steal their Microsoft 365 credentials without ever touching the user’s device, compromising endpoints, or sending phishing links or malicious attachments.
“The most dangerous element is that it operates at the network gateway, which sits beneath most of the trust assumptions users and devices make,” ReliaQuest told CSO Online. “It’s not necessarily an enterprise breach level event on its own, but it’s a very real risk to individual accounts.”
Exploiting a ‘fundamental trust’
Domain Name System (DNS) poisoning, in which false data is injected to redirect regular web traffic to fraudulent domains, has previously been observed on small office routers, but attackers are now expanding the technique to higher-level targets, the ReliaQuest researchers explained in a blog post.
Attackers likely gain access to the gateways through weak or reused admin credentials in combination with exposed interfaces like Secure Shell (SSH), Simple Network Management Protocol (SNMP), and other web consoles, they pointed out.
Admin access to the gateway is all that malicious actors need, because devices are designed to inherently trust DNS, which translates domain names like login.microsoftonline[.]com into IP addresses to route them. Therefore, a single gateway compromise gives the attacker the ability to redirect traffic for every guest logging into the network, providing IP addresses it controls in response to DNS requests, rather than the legitimate ones, without touching a single endpoint.
“Captive portal appliances sit at the network perimeter for every guest on that network,” the researchers wrote. “Detection is inherently difficult because the attack happens gateway-side, outside the endpoint’s visibility.”
In the campaign tracked by ReliaQuest, four attacker-registered domains, m365-owa[.]com, owa-ms365[.]com, ms365-device[.]com, and ms365-live[.]com, were used for Microsoft-impersonation lures.
The compromised Wi-Fi gateways were discovered across multiple US cities as well as in India and Saudi Arabia, and impacted users were from companies in professional and financial services, legal, retail, health care, and energy, indicating that the method isn’t sector-specific.
“We’ve seen enough SharePoint exfiltration cases to know that a single popped account can cascade into meaningful data loss,” ReliaQuest noted. Meanwhile, for the network operators, there’s a “reputational dimension”; user compromise is a “serious trust and brand problem, regardless of how sophisticated’ the underlying attack is.”
Safe services, DNSSEC not enough
Locking network configurations to a ‘safe’ DNS provider such as Google (8.8.8.8), Cloudflare (1.1.1.1), or the cloud-based OpenDNS isn’t a sufficient tactic, because it doesn’t change the path that queries actually travel over, ReliaQuest contended.
By default, devices send DNS queries as unencrypted protocol traffic, and those packets still have to traverse the hotel’s network to reach Google, Cloudflare, or OpenDNS, the company explained. Since the gateway sits directly in that path, it can inspect, block, or redirect the query before it ever reaches the chosen resolver.
“Specifying a trusted DNS server changes the intended destination, not who controls the road to get there,” ReliaQuest noted.
Further, Domain Name System Security Extensions (DNSSECs), which use digital signatures and public-key cryptography, only “partially” address the problem. DNSSEC provides authentication and integrity for signed domains, which means a validating resolver can detect and reject forged or tampered responses.
“What it does not do is provide confidentiality or availability,” the company said. “It does not encrypt DNS traffic or stop an attacker from intercepting, blocking, or redirecting requests.”
So while DNSSEC can defeat certain response-forgery attacks against signed zones, an on-path gateway can still see queries, drop them, or force fallback behavior. However, this protection layer only helps when domains are actually signed, and then only when the client or resolver performs validation, which “many stub resolvers do not,” according to ReliaQuest.
Full-tunnel VPNs required
To combat the problem, enterprises should require all corporate devices to use a full-tunnel VPN for network connection. Controls should prevent internet access until a tunnel is active, ReliaQuest advised.
This will route all of a device’s traffic, including DNS, through an encrypted connection to a trusted VPN server before it travels anywhere else, the company explained, thus preventing local networks like hotel gateways from seeing or modifying DNS and internet traffic.
“In effect, it takes the untrusted network out of the trust equation,” ReliaQuest noted.
However, full-tunnel configuration is not the default for VPNs, because it comes with “real trade-offs,” the researchers noted: It adds cost, latency, and bandwidth demands, since every packet has to travel through company infrastructure. Thus, forcing all traffic through the corporate backbone is “not always practical” for distributed or bandwidth-heavy workforces.
Enterprises should also enforce conditional access in Entra ID to block device-code authentication flow, which has few legitimate use cases for most users in most environments, ReliaQuest noted.
Additional precautions
The company also advised:
Restricting Proxy Auto-Configuration (PAC) file retrieval to approved internal hosts;
Disabling automatic Web Proxy Auto-Discovery (WPAD) via Group Policy to (this is often enabled by default in Windows);
Deploying encrypted DNS such as DoH or DoT in strict mode as a “complement or alternative” to full-tunnel VPN. This is particularly important for organizations where always-on VPN is not feasible.
Training employees to verify the URL and certificate of any page requesting credentials before entering them, particularly on public Wi-Fi networks.
Prevention is more important than detection here, ReliaQuest pointed out: while in tools like Microsoft Defender for Endpoint, ‘DnsConnectionInspected’ events showing queries to attacker-controlled domains are a primary endpoint-level signal, “by the time those events fire, the redirect has typically already occurred. In other words, endpoint telemetry confirms what happened more than it prevents it.”
This is exactly why methods like encrypted transport, Conditional Access, and WPAD and PAC hardening matter more than detection alone, the researchers emphasized.
The European Commission has fined Google a total of €890 million ($1 billion) for its breaches of the Digital Market Act (DMA).
Just over half the fine — €460 million — was because Google illegally gave preference to its own services in Google Search results.
The remainder was because in the Google Play store for Android apps, the company prevented app developers from leading consumers to alternative, often cheaper, purchase channels. Under the DMA, app developers who distribute their apps via Google Play or Apple’s App Store should be able to inform customers of alternative offers.
Now Google must give third-party services featuring in its results the same treatment as its own services, and allow developers of apps in the Play Store to communicate about offers both in and outside the Play Store, or face further fines.
Healthy software companies typically don’t suddenly eliminate one-fifth of their workforce, but monday.com is doing just that as it bets on flatter teams, AI agents, and customer implementation expertise as the winning combination in the AI era.
Monday.com co-founder and co-CEO Eran Zinman today announced the “very difficult decision” to reduce the AI work platform company’s global workforce by about 20%, or 620 people.
The move has nothing to do with increasing margins or replacing humans with AI, he insisted in his post on LinkedIn; rather, it’s a calculated decision to trim down and hone the company’s focus as AI becomes integral to day-to-day workflows.
“This is not a distress signal; it is a deliberate reset, disclosed with its price attached,” said Sanchit Vir Gogia, chief analyst at Greyhound Research. “The industry has quietly swapped the meaning of productivity, and this filing is the clearest exhibit yet.”
A ‘significant opportunity’ in technology
In a SEC filing this week, monday.com said its restructuring plan reflects the “ongoing transformation of its product, marketing, and go-to-market strategy.” The move is intended to support a “leaner, more focused operating model” as the company continues to invest in its AI-driven strategy.
Zinman noted in his post that the company has shifted to “doing the work with AI and not just managing it,” and is focused on building environments where “people and AI agents [work] together in one workspace.”
In recent months, monday.com has evolved its products, strategy, and the way it serves its customers, and Zinman contended that “the organization we built for our previous chapter is not the organization that fits the new AI era.” Monday.com needs to “execute more decisively,” take on new challenges, and quickly respond to market changes, he said.
“We have never seen such a significant opportunity in software, driven by such exciting technology,” Zinman noted. He emphasized that the reduction is not to replace people with AI, nor to improve margins; the “vast majority” of savings will be reinvested into talent, products, and AI.
The restructuring will result in a “flatter organization” with fewer management layers and smaller, more autonomous teams, and monday.com also has a new go-to-market model, Zinman explained. Customers expect “deeper implementation support” as they deploy AI, and the company will work more closely with customers, increase its on-site presence, create new roles, and “adapt many existing ones.” In its SEC filing, the company said it expects to continue hiring in “key strategic areas” throughout 2026.
Workers will be expected to work better, “not harder,” Zinman noted. He pointed to several past examples where work could have been done in a few days, but instead took many months with “multiple meetings and endless friction.”
“This wasn’t people’s fault and everyone was frustrated by this,” he said. “Our new org changes ownership to allow people to make decisions and move fast.”
A spokesperson for monday.com declined to comment further on the staff reductions.
Monday.com’s key market advantages
Monday.com certainly isn’t struggling; the company expects 19% to 20% year-over-year growth in 2026.
“Companies in that position do not restructure because they must,” Greyhound’s Gogia noted. “They restructure because they have decided to become something else.”
Melody Brue, VP and principal analyst at Moor Insights & Strategy, pointed out that organizational redesign is important for real AI transformation, but while it can signal confidence to the market, it can still be “devastating” to humans.
While the company looks as though it’s trying to do right, that ultimately remains to be seen, she said. “There are often hidden internal bruises that can surface long after layoffs.”
Monday.com’s advantage is in its “structured substrate,” Gogia noted; its boards, permissions and typed workflows give agents something firmer to act on than just documents and chat history. The company highlights its natively built agents that can be configured by any team member, as well as connectors with Claude, Microsoft Copilot, and ChatGPT, and dedicated routes for external agents to authenticate and operate.
“For some time, the sharper enterprise question has been shifting from who has an agent to who owns the governed runtime in which an agent can safely act,” he said. “Structured work is a serious claim on that runtime.”
But parts of monday.com’s agent estate remain in staged release, and its product is ultimately “mid-transition,” Gogia pointed out; its agent builder carried a beta label as recently as March,. Also, the company’s pricing model changed in May to a hybrid model charging for seats as well as mandatory AI credits. And, while its AI-powered no-code builder monday vibe passed $1 million in annual recurring revenue within two and a half months, monday.com has not released subsequent outcomes, usage volumes, or attach rates.
Further, there’s an element of “gravity” with its competitors, he observed. Asana is reorganizing teams around agents, Atlassian is wiring agents into the developer estate, and others are simply bundling them into their offerings: Microsoft is doing so across the productivity stack, and ServiceNow across enterprise operations, each with identity and procurement built in.
“Their pull is strongest exactly where monday.com wants to grow, in the largest accounts, where control-plane depth and administrative reach decide the deal,” said Gogia.
Actions for the near-term
Going forward, buyers should focus on operating risk, not headline risk, Moor’s Brue noted. In practice, that’s continuity of service, roadmap consistency, and strength of enterprise support. Productivity should be valued as better outcomes per unit of organizational effort, not mere activity.
“It should be a measure of how much smoother, faster, and more effective the operating model becomes when AI is built into the work,” said Brue.
Gogia noted that strain surfaces first in customer service, and monday.com’s attention is being redistributed. The company’s annual report disclosed that its focus is now concentrated on the largest accounts, with support for medium-sized clients moved to an AI-first and human-supported model.
During the first month of the transition, buyers should track named account continuity and escalation times, he advised. By the first quarter, keep an eye on whether credit governance and admin controls mature on schedule, and if the roadmap beyond the AI estate keeps pace. By the half-year mark, determine whether promised implementation depth is producing outcomes or “simply more billable engagement.”
Support tiers should be enumerated in writing before renewal, and buyers should contract for “side exits,” Gogia emphasized, with overage pricing fixed in advance, the right to pause consumption, and portability for workflows and agent configuration “if the relationship sours.” Finance should also insist on monthly consumption reporting by capability. Further, integration efforts, partner dependency, and change management should be considered first-class costs of the agent era, “not as afterthoughts to a license.”
“A license was a known cost,” said Gogia. “A meter is a behavior, and behavior is harder to forecast than headcount.”
Building a presentation can take lots of time. There are design choices to figure out: the slide layouts, fonts, theme colors, and so on. You can use a template to skip this hassle, but you still have to paste your text and other content into the slides and edit it all so that the results are visually appealing.
In PowerPoint, Microsoft’s Copilot AI assistant can now automate the heavy lifting of presentation creation. It can generate a first-draft presentation in minutes, then help you edit it. You can also prompt Copilot to help you quickly understand the contents of a presentation and glean insights from it. Use the tips in this guide to save oodles of time as you create and work with presentations.
For business users, it’s more complicated. Organizations with more than 2,000 users must pay for Microsoft 365 Copilot licenses for their users in addition to their regular Microsoft 365 licenses. Users at organizations with fewer than 2,000 users can use Copilot within M365 apps even without the M365 Copilot add-on licenses, but there are limitations in usage, speed, and feature availability.
To see what kind of access you have, log in to Microsoft’s Copilot Chat web hub and look for your name in the lower left corner. If you see “M365 Copilot (Premium)” under your name, you can use Copilot in M365 apps with priority access and advanced features. “M365 Copilot (Basic)” means you can use Copilot in M365 apps with lower-priority access and limited features. If you see “Copilot Chat (Basic)” or nothing below your name, you can’t use Copilot in M365 apps.
(Copilot Chat Basic users do get some Copilot functionality, including the ability to generate presentations, via the Copilot Chat hub. See our Copilot Chat tutorial for details.)
First, let’s quickly go over the notable settings of the Copilot sidebar.
When you have a presentation open in PowerPoint, click the Copilot icon; it may be floating at the lower-right corner of your PowerPoint window or parked at the right end of the Ribbon toolbar. The Copilot sidebar will open along the right of the page. You’ll type your prompts to Copilot inside the chat window in this pane.
The sidebar on the right is where you interact with Copilot in PowerPOint.
Howard Wen / Foundry
Agent mode: By default, Copilot can build a new presentation or make changes to an existing one in the main PowerPoint window. This is known as “agent mode.” To change this so that Copilot can’t take direct action on a presentation (all its responses appear in the sidebar), click the Allow editing button above the chat window and change it to Chat only.
The tips in this guide require that Copilot be in agent mode, so make sure you see Allow editing above the chat window.
Choice of AI model: Behind the scenes, Copilot has access to various genAI models, including different versions of Anthropic Claude and OpenAI GPT. By default, it decides which model to use based on your prompt. You can set it to use a particular model: click Auto at the upper right of the Copilot pane and select a model from the dropdown that opens.
You can choose which AI model you want Copilot to use for a request.
Howard Wen / Foundry
The tips in this guide should work fine on the default Auto setting. But feel free to experiment switching to specific models to see which give you the best results for particular tasks.
For many people, the hardest part of creating a presentation is getting started. What types of information should be included on the slides, and in what order? Copilot can give you a leg up by creating the type of presentation you need, with placeholder data that you can later replace with your own.
Start a new presentation, open the Copilot sidebar, and type your prompt into the chat window. It’s best to provide very specific details in your prompt. The more context or details you provide, the more likely Copilot will generate a presentation template that suits your needs.
A good prompt should contain the slide count, subject, audience, and tone. Example:
Create a 6-slide presentation for a sales meeting focusing on Q1 revenue. The audience is the sales team, so keep the tone professional and focused on the sales data.
Copilot may ask a series of follow-up questions, such as your preferred visual style and desired level of detail. Then it will generate a presentation template.
Copilot generates a presentation with placeholder data and explains its elements.
Howard Wen / Foundry
You can optionally prompt Copilot for revisions, and when you’re happy with the template, swap in your own data.
2. Create a presentation from a document
You can attach a document (such as a Word document, Excel spreadsheet, or PDF) and prompt Copilot to generate a presentation based on its contents. This works best with a structured-format document (such as a business plan, project proposal, or summary report) that contains sections with headings.
Copilot can extract the document’s text and structure to generate the slide content for the new presentation. This can especially be useful for quickly turning a long report into a visually appealing presentation.
In the Copilot pane, click the + icon at the bottom of the chat window. A list of documents that you’ve recently accessed appears. Select the one that you want Copilot to use. Alternatively, click the magnifying glass icon and inside its search box, type a few letters of the filename for the document you want. (Business users with an M365 Copilot license can select up to five files for Copilot to pull from when creating a presentation.)
Attaching a document for Copilot to base a presentation on.
Howard Wen / Foundry
Then in the chat window, you can enter a prompt that’s as simple as “Create a presentation,” although as always, providing more details and context is better. This is especially important for corporate users who reference multiple source files. It’s useful to tell Copilot what data to pull from each document.
Answer any follow-up questions that Copilot asks, and it will then generate the presentation.
Copilot has generated a professional presentation from a social media marketing campaign document.
Howard Wen / Foundry
Note: Your marketing department may have created one or more branded company templates for Copilot to work from. If that’s the case at your organization, simply open the appropriate company template as your first step. Then you can upload docs and type a prompt as described above. Copilot will create a presentation using the branded template.
3. Add content from a document to a slide
Manually copying text or other content from a document and pasting it into a new slide is a chore. Instead, you can prompt Copilot to extract information directly from a Word document, Excel spreadsheet, or PDF to create new slides.
In the Copilot pane, attach the document using the same steps described in tip 2, then tell Copilot to create a slide from the document. As always, it helps to provide details such as the new slide’s focus or what data to include:
Add a slide based on the attached document.
Use the attached file to add a slide about the project budget that focuses on Q1 projections.
Summarize only the financial section of the attached document as a slide.
A new Copilot-generated slide based on data from an Excel spreadsheet.
Howard Wen / Foundry
4. Refine your slide text
A presentation should be visual and display only the core message. Conciseness and proper writing tone are essential for your slides, so that they don’t lose the attention of your audience.
You can prompt Copilot to refine text on an individual slide in various ways, such as rewriting it in a more professional tone or making it more concise. Highlight the text inside a text box on the slide. On the toolbar that appears over the highlighted text, click Edit with Copilot.
On the menu that opens, you can select a preset prompt to refine the text, such as Condense or Make professional. Or, at the top of this menu, you can type a prompt to rewrite the highlighted text.
Choose a preset prompt for refining text on a slide or type in your own prompt.
Howard Wen / Foundry
Note that this feature affects all the text inside the text box. To rewrite only a portion of text inside a text box, you must split that portion out into a separate text box.
Alternatively, you can prompt Copilot to analyze your entire presentation and tighten up the wording throughout all of its slides. For example:
Make these slides more visual and use less text.
5. Find or create an image
If you have Copilot generate a presentation from an existing Word document that contains images, it will incorporate those images into the presentation. If there are no images in the source document, you can ask Copilot to find or create one and add it to a slide.
To add a stock image or an image from your organization’s brand library, tell Copilot what you’re looking for:
Add a stock photo of young adults in a cafe drinking boba tea.
Add a photo from our asset library of young adults in a cafe drinking boba tea.
To have Copilot create an image using Microsoft’s Designer image generation tool, describe your desired image. As always, specificity is helpful:
Create a photorealistic image of a diverse group of 5 or 6 fashionable young adults sitting in a cafe drinking boba tea. They’re smiling or laughing, and some are looking at their phones.
Copilot in PowerPoint hooks into Microsoft’s Designer tool for image generation.
Howard Wen / Foundry
Just as you need to review any text output from Copilot, take a close look at generated images to be sure nothing looks off.
Also note that Copilot image generation isn’t always reliable in PowerPoint. For some time during our testing for this story, Copilot said it couldn’t create an image because “the image generation service is returning a server error on every attempt.” After about a day and a half, the service began working again.
6. Expand your presentation with relevant slides
As you’re building your presentation, you may find that it’s become text heavy. Or perhaps it could use more visually oriented slides to break things up and make its progression flow better. Copilot can generate and insert new slides that are based on the content of the slides already in the presentation.
In the Copilot pane, specify exactly where you want the new slide to go. This helps Copilot to analyze the content of the slides before and after where you want the new slide. Then it can generate a slide to bridge between the two slides. Examples:
Add a slide after slide 3 about our competitive advantages.
Add a slide after slide 11 that transitions to slide 12.
Need a transition slide? Just ask!
Howard Wen / Foundry
7. Summarize a presentation
Maybe you need a quick refresh of your presentation before an important meeting. Or maybe a co-worker has sent you a presentation that’s packed with lots of slides. You can prompt Copilot to generate a summary of the presentation’s overall messaging.
In the Copilot pane, just type “summarize this presentation.” You can also have Copilot flag key slides that contain important information: “show me key slides.”
Ask Copilot to summarize a presentation or flag key slides.
Howard Wen / Foundry
8. Answer questions about a presentation
As you’re reviewing a presentation, especially one that you didn’t create and are not familiar with, you can get Copilot to pull key data points from its slides.
In the Copilot pane, type specific informational questions. Examples:
What are the action items in this deck?
What is the proposed budget mentioned here?
If Copilot can’t find the exact answer to the question you ask, it will provide related information from the presentation.
Ask Copilot specific questions about the contents of a presentation.
Howard Wen / Foundry
This method can also help you validate that your presentation includes everything you want it to. If you ask Copilot about the action items in a presentation and it can’t find any, you know you need to add them. (Copilot will likely offer to generate them for you based on the rest of the slides.)
You can even take this tactic a step further and ask Copilot if the presentation is missing any important data, if any slides are weak or confusing, if there are any awkward transitions, if there are key points that should be better emphasized, and so on.
9. Help you navigate a large presentation
In the business world, presentations with dozens of slides are not uncommon, such as for financial reports or project documentation. Trying to find a specific slide or multiple slides can be tough. Copilot can help you navigate such a presentation.
In the Copilot pane, prompt Copilot to find slides based on specific topics. Example:
Show me the slides about the project timeline.
Copilot will analyze the presentation and reply with a list of links to the relevant slides. Click one of these to jump directly to that slide.
Copilot can help you zoom directly to a slide that covers a particular topic or shows specific data.
Howard Wen / Foundry
10. Generate speaker notes and/or an FAQ
Here’s a great timesaver when you’re preparing to show your presentation to an audience: Copilot can automatically generate suggested speaker notes for you, based on the content of your slides. Example prompt:
Write speaker notes for every slide with one talking point per slide.
Copilot can create speaker notes in seconds.
Howard Wen / Foundry
In a related feature, Copilot can create a frequently asked questions list (FAQ) for you to consult in your speaker notes or to present as a slide:
Write an FAQ for these slides.
Copilot will ask where you want the questions and answers added — as a new slide at the end, integrated into the speaker notes of relevant slides, or somewhere else that you designate. Make a selection, and Copilot will generate the FAQ based on the content of your presentation.
Here in this high-tech era of 2026, keeping important info backed up and synced should be effortless and something that just happens on its own, automatically, without any actual thought or ongoing human effort.
In many areas of our digital life, that mercifully does Just Work™ in exactly that way. Fire up an email in most modern mail services, and you can stop at any point and find your in-progress draft in that same app on any other device. The same applies to any file you’re finessing within Google Drive or other cloud storage services or document you’re dawdling over in Docs.
One area where seamless syncing somehow still doesn’t occur, though, is in the domain of downloaded documents on Android. If someone sends you a PDF or a Word file and you save it to your phone, that file exists in an archaic-seeming silo — only locally, on that one gadget. And that, of course, means (a) you can’t access it from any other device, and (b) if you misplace your phone or move into a new one at some point along the way, the file will be left behind in time and entirely unavailable.
Well, take a moment to join me in celebration: Amidst all the Gemini gobbledegook that no one asked for (and that often falls somewhere between “pointless” and “actively counterproductive”), Google’s giving us a major upgrade to Android’s backup capabilities right now. It’s a simple-seeming switch buried in your system settings, and it’s up to you to find and activate it.
Once you do, though, those once-orphaned documents on your Android device’s local storage will be perpetually synced and protected, automatically, without any ongoing thought or effort.
All you’ve gotta do is find and flip that one new switch.
So, for a quick bit of pertinent context on this: Android’s backup systems have actually come a really long way over the years.
‘Twas a time, y’see, when little to nothing about you would sync and carry over automatically from one Android device to another. Years ago — back in the ancient-seeming prehistoric era of the early 2010s — Android enthusiasts in the know would rely on community-created third-party apps for everything from remembering and resyncing downloaded apps to restoring data from within those apps and onward. And reconfiguring your system preferences would be a whole time-consuming song and dance every single time you reset a device or moved into a new one, as little to nothing would automatically carry over.
Most of that stuff is now effortless and automatic. And, thanks to apps like Google Messages, Calendar, Drive, and Docs, many other areas of important data are also synced on their own at the app level — outside of any system mechanisms.
Locally stored files, however, have remained an awkward omission. To this day, anything you download on any Android device exists only on thatone device and isn’t synced or backed up anywhere. The only way that happens is — in a blast-from-the-past twist — if you go out of your way to find and set up a third-party app to handle the heavy lifting.
That brings us to today. Right now, as we speak, Google’s in the midst of sending out a quiet under-the-hood update that (brace yourself…) adds in the option to automatically sync and back up any documents on your device as a native part of Android’s backup setup.
See?
The easily overlooked new option for backing up documents on Android.
JR Raphael, Foundry
The option is on its way to all devices running 2018’s Android 9 release and higher. (If you’re still using a phone with an Android version older than that, you’re now a whopping eight years out of date, and you have much bigger problems.)
Once the added option is present and available for you, you’re literally lookin’ at 10 seconds to find and activate it.
Lemme show ya how.
Android’s document backup addition
I promise: This couldn’t be much simpler.
No matter what kind of Android device is in front of you, just head into your system settings and open the section called “Accounts and backup,” “Back up or copy data,” or something along those same lines. (The exact wording can vary based on who made your device and when it was released or last updated.)
Either tap the line labeled “Google Backup” or look for an option to “Back up data” via Google Drive. You should then either see a series of options for different areas of available backup right then and there — or, depending on your device, you might have to tap a line labeled “Other device data” (or something similar) to find the full list of possibilities.
However you get there, once you’re lookin’ at that list, you’ll see a newly added line for “Documents” if this latest under-the-hood update has reached you.
Android’s expanded list of backup options — now including documents alongside other forms of on-device data.
JR Raphael, Foundry
And from there, all that’s left is to tap it and enable the switch to include that in your automated backups from that moment forward.
If you aren’t seeing the option yet, don’t panic. Google always sends these under-the-hood updates out bit by bit over time, so the change probably just hasn’t reached your device quite yet. As long as you’re running Android 9 or higher, it’ll get there. Set yourself a reminder to check back once a week or so. Odds are, you’ll see it pretty soon.
Notably, all documents synced in this way are always encrypted for security, and they’re kept in your personal (or, depending on the nature of your account, perhaps company-connected) Google Drive storage. That does mean they’ll count against your overall Google storage total, so keep an eye on your Drive storage total to make sure you’re in solid shape and look to the Google One storage hub if you ever want some simple suggestions for freeing up space.
Speaking of other Google services: If you ever want to keep other types of locally stored non-document files from an Android device synced and available elsewhere, you can easily rely on Google Photos for syncing screenshots and other images — after enabling sync in general, be sure to look in the app’s “Collections” areas to find the “On this device” folder and then flip the toggle to “Backup all device folders” (or get more nuanced and open specific individual on-device folders if you want to sync some but not all of those areas) — and you can still turn to those aforementioned third-party apps for broader syncing of anything else imaginable.
But with documents now being handled automatically and natively, that’s one big worry now out of your hair. Just note that the onus will fall on you to find and flip the switch and actively opt in to the feature on each and every Android device you’re using.
Take 10 seconds to do that, though, and you’ll have one less void in your Android data arena. And you don’t need Gemini to tell you that that can only be a good thing.
Get practical Android knowledge in your inbox every Friday with my free Android Intelligence newsletter— one new thing to try each week, straight from me to you.

 Login