Login

Group of bipartisan lawmakers ask US government to ban several hack-for-hire firms
The three Indian companies are accused of using hackers to steal information used to sway litigation.

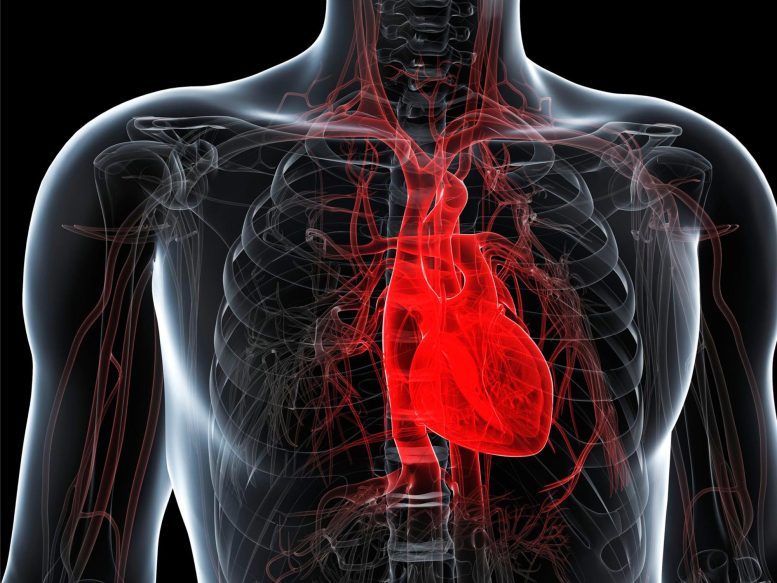 A major trial found that implantable cardioverter-defibrillators may benefit some patients younger than 70 with mild-to-moderate heart dysfunction and cardiac scarring. A more than decade-long randomized trial suggests that implantable cardioverter-defibrillators may benefit some patients who have heart scarring and only mild-to-moderate loss of heart function, a group that currently falls outside standard treatment guidelines. [...]
Hackers carried out a supply chain attack that installed malware on networks using an unusual technique: hijacking a chunk of Internet space where cloud management software used by hosting providers, data centers, and other large infrastructure companies is updated.
In a well-coordinated operation, the unknown attackers exploited weaknesses in the routing security setup of hosting provider Hetzner Online and the process for attaining valid TLS certificates. The lapses allowed the attackers to successfully perform a BGP (Border Gateway Protocol) hijacking to obtain control over IP addresses assigned to Softaculous. The company, based in the United Arab Emirates, is the maker of a platform for installing and managing Web software and is the developer of Virtualizor, a management platform for virtualized environments.
Softaculous used the IPs to issue updates and host a client and billing site. With control over the hijacked space, the attacker was now using the addresses to push malware masquerading as updates to unsuspecting users.
© Getty Images
A zero-emission compact hydrogen power plant will drive the two stages at Clifton Down in Bristol
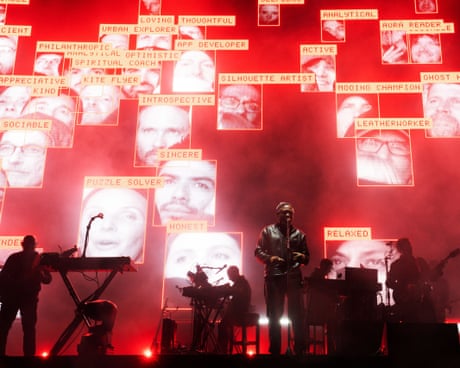
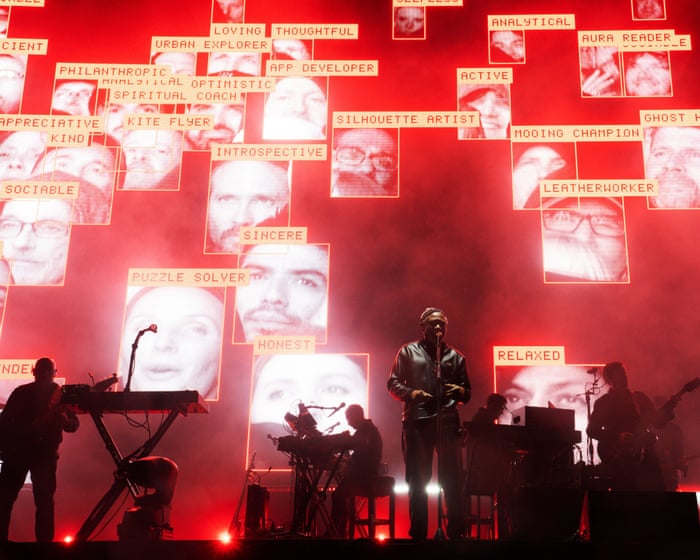
When Lorde, Little Simz and Wet Leg stride on to stages in Bristol this weekend, they will not only be entertaining tens of thousands of festivalgoers but taking part in what is being billed as a world-first clean power project.
The two stages at Forwards festival on Clifton Down are being driven almost entirely by green power – a combination of hydrogen and mobile batteries charged with sustainable energy.
Continue reading...
© Photograph: Kristian Buus/In Pictures/Getty Images
© Photograph: Kristian Buus/In Pictures/Getty Images
© Photograph: Kristian Buus/In Pictures/Getty Images


A Sudanese man has been arrested after an attempted "beheading" in Belfast last night that left a man in his 40s with serious injuries in a "critical" condition.
The post Sudanese Man Arrested After Attempted “Beheading” in Belfast appeared first on The Daily Sceptic.




Daemon Tools, a widely used app for mounting disk images, has been backdoored in a monthlong compromise that has pushed malicious updates from the servers of its developer, researchers said Tuesday.
Kaspersky, the security firm reporting the supply-chain attack, said it began on April 8 and remained active as of the time its post went live. Installers that are signed by the developer’s official digital certificate and downloaded from its website infect Daemon Tools executables, causing the malware to run at boot time. Kaspersky didn’t explicitly say so, but based on technical details, the infected versions appear to be only those that run on Windows. Versions 12.5.0.2421 through 12.5.0.2434 are affected. Neither Kaspersky nor developer AVB could be contacted immediately for additional details.
Infected versions contain an initial payload that collects MAC addresses, hostnames, DNS domain names, running processes, installed software, and system locales. The malware sends them to an attacker-controlled server. Thousands of machines in more than 100 countries were targeted. Out of the many machines infected, about 12 of them, belonging to retail, scientific, government, and manufacturing organizations, have received a follow-on payload—an indication that the supply-chain attack targets select groups.
© Getty Images
Servers operated by Ubuntu and its parent company Canonical were knocked offline on Thursday morning and have remained down ever since, a situation that’s preventing the OS provider from communicating normally following the botched disclosure of a major vulnerability.
Attempts to connect to most Ubuntu and Canonical webpages and download OS updates from Ubuntu servers have consistently failed over the past 24 hours. Updates from mirror sites, however, have continued to work normally. A Canonical status page said: “Canonical’s web infrastructure is under a sustained, cross-border attack and we are working to address it.” Other than that, Ubuntu and Canonical officials have maintained radio silence since the outage began.
A group sympathetic to the Iranian government has taken credit for the outage. According to posts on Telegram and other social media, the group is responsible for a DDoS attack using Beam, an operation that claims to test the ability of servers to operate under heavy loads but, like other “stressors,” are, in fact, fronts for services miscreants pay for to take down third-party sites. In recent days, the same pro-Iran group has taken credit for DDoSes on eBay.