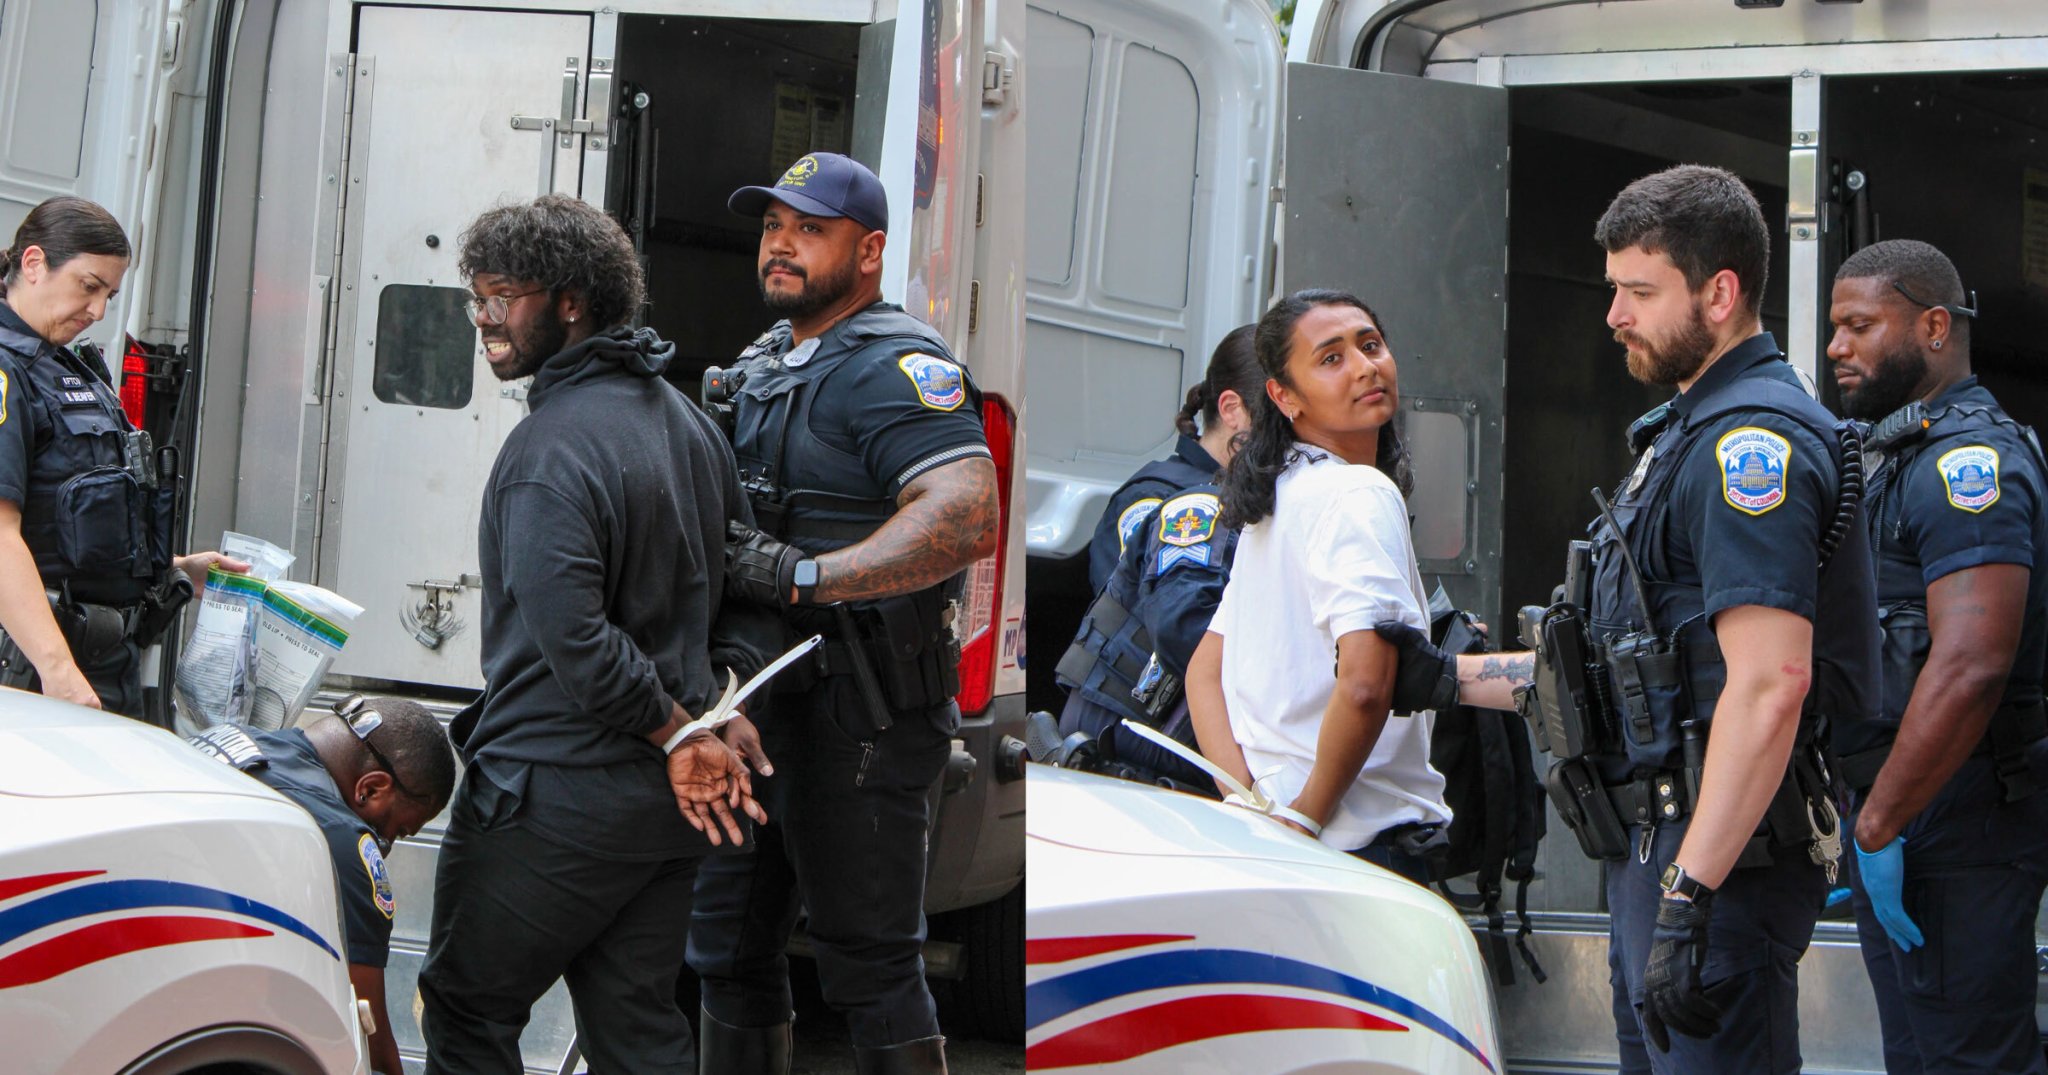❌

Reading view

OpenAI’s “Head of Ethics” Suddenly Leaves Company Under Mysterious Circumstances

Following a growing string of high-profile departures, OpenAI has lost its head of ethics at arguably the worst time possible.

As the Financial Times reports, Chloé Bakalar left her post as the AI ethics lead in July, less than a year after joining the company and without any accompanying announcement. Interestingly, her LinkedIn still claims she’s employed at the firm.

There currently is no replacement lined up, suggesting shifting priorities at the company. According to the FT‘s sources, Bakalar was the only remaining dedicated ethicist at the company.

The timing of Bakalar’s departure is noteworthy. The Sam Altman-led company has been embroiled in a major controversy after revealing that a group of its AI models broke containment and hacked into the systems of open source AI platform Hugging Face.

In other words, OpenAI needs a competent team of AI ethicists now than ever before as the industry reels from the possibility of frontier AI models going rogue, in what many experts say is a cybersecurity nightmare in the making.

The development proved alarming enough that OpenAI vowed last week to slow the release of its upcoming Astra AI model.

“We cannot rule out critical cyber capabilities,” the company admitted, following internal evaluations of the model.

Bakalar had been primarily tasked with coming up with ethical approaches to AI model development and studying how AI interacts with humans.

“Ethics is actually everyone’s responsibility, and I say that as someone whose job it is to lead this work,” she told audiences during a recent AI conference, as quoted by the newspaper. “You shouldn’t just come to people like me. There should never just be one person who serves as the moral centre of an AI developer.”

It’s a particularly symbolic departure for a company that once billed itself as an ethical non-profit. The company restructured itself into a primarily for-profit business last year, largely betraying its non-profit roots. The company’s plans to go public could further erode any lingering commitments to the ethical development of AI.

Meanwhile, its competitor Anthropic, which has long billed itself as the more ethical alternative to OpenAI, is similarly struggling to maintain its public image. The company dropped its core safety commitments earlier this year.

The company still has an alignment team, led by philosopher Amanda Askell, who is tasked with giving its flagship chatbot Claude a sense of right and wrong.

But whether any of these remaining AI ethics efforts will matter as the industry continues to deal the environment a devastating blow, force users down dangerous spirals of delusion, and facilitate a flood of misinformation on the web, is debatable at best.

More on AI ethics: If You Think AI Companies Are Unethical Now, Wait Until They Go Public

The post OpenAI’s “Head of Ethics” Suddenly Leaves Company Under Mysterious Circumstances appeared first on Futurism.
  •  

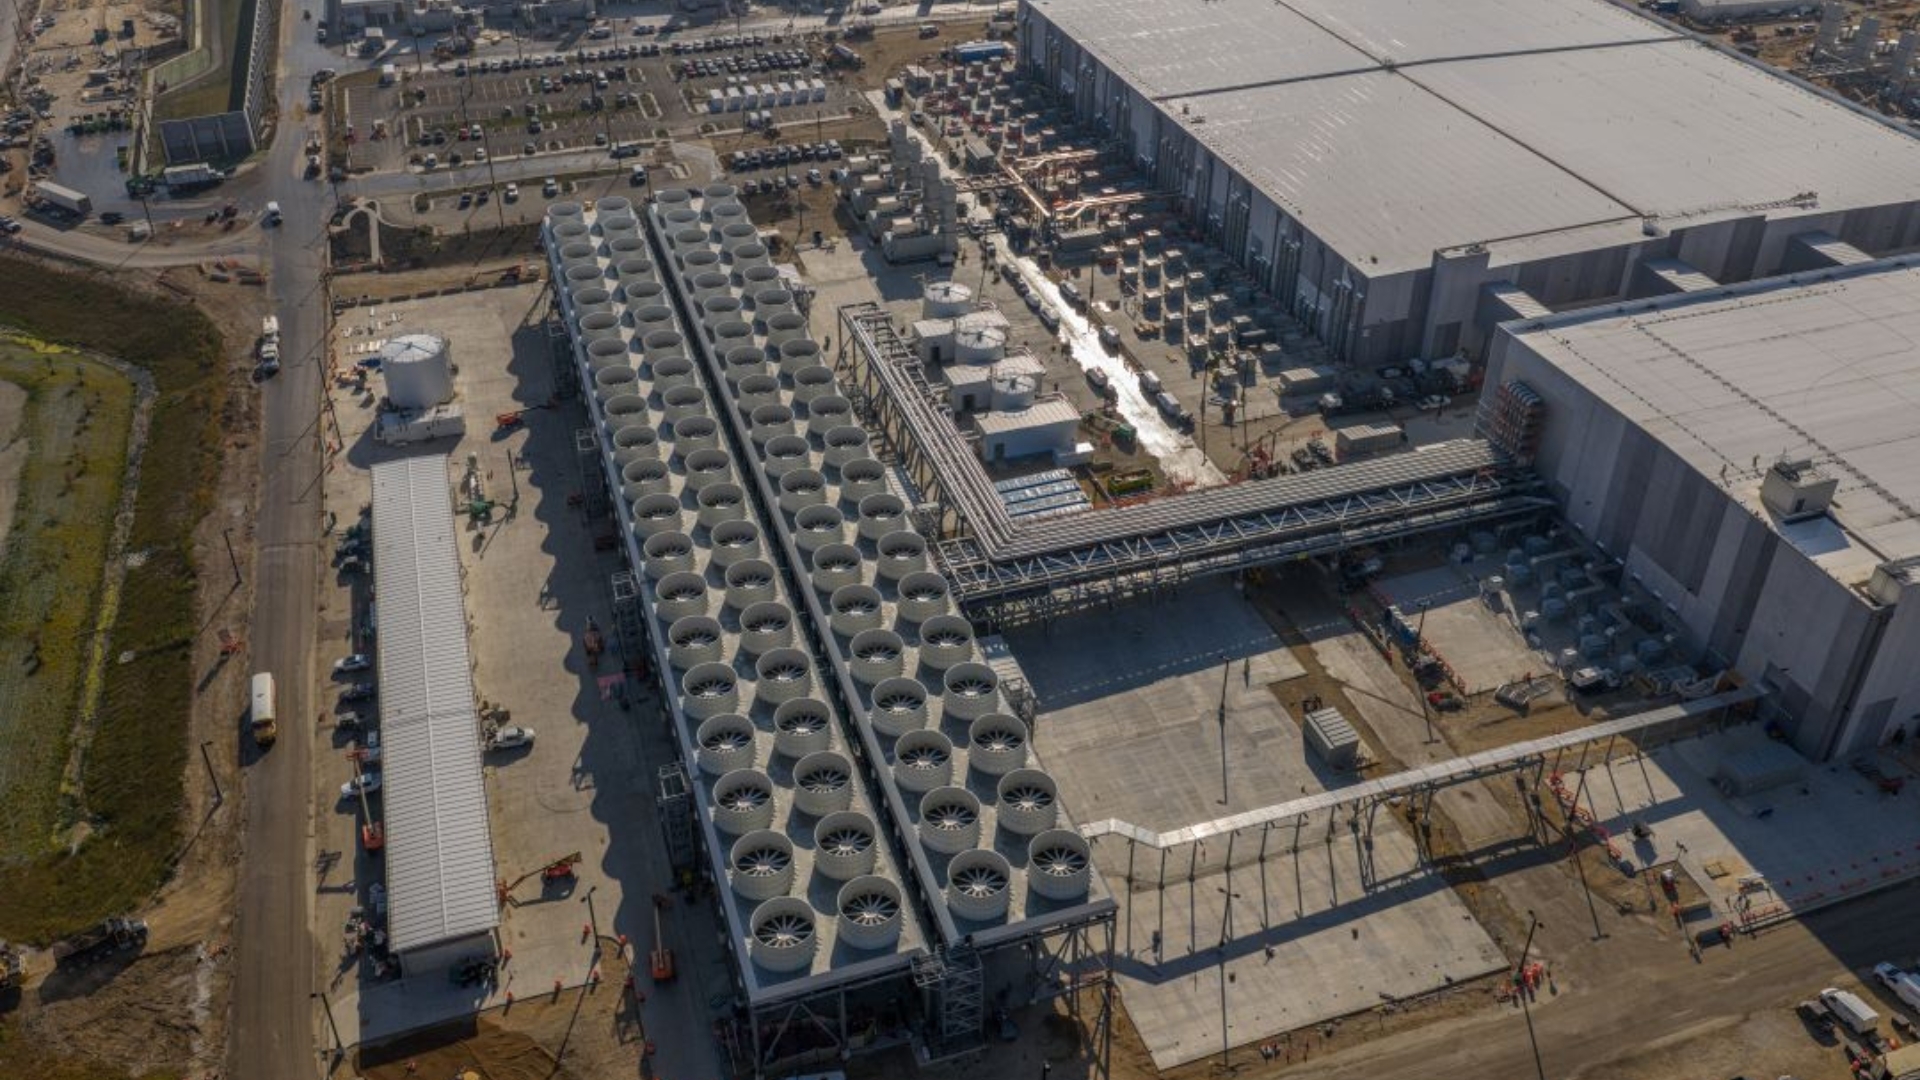
Protests Against Data Centers Are Now Threatening $130 Billion of Big Tech’s Crucial Investments

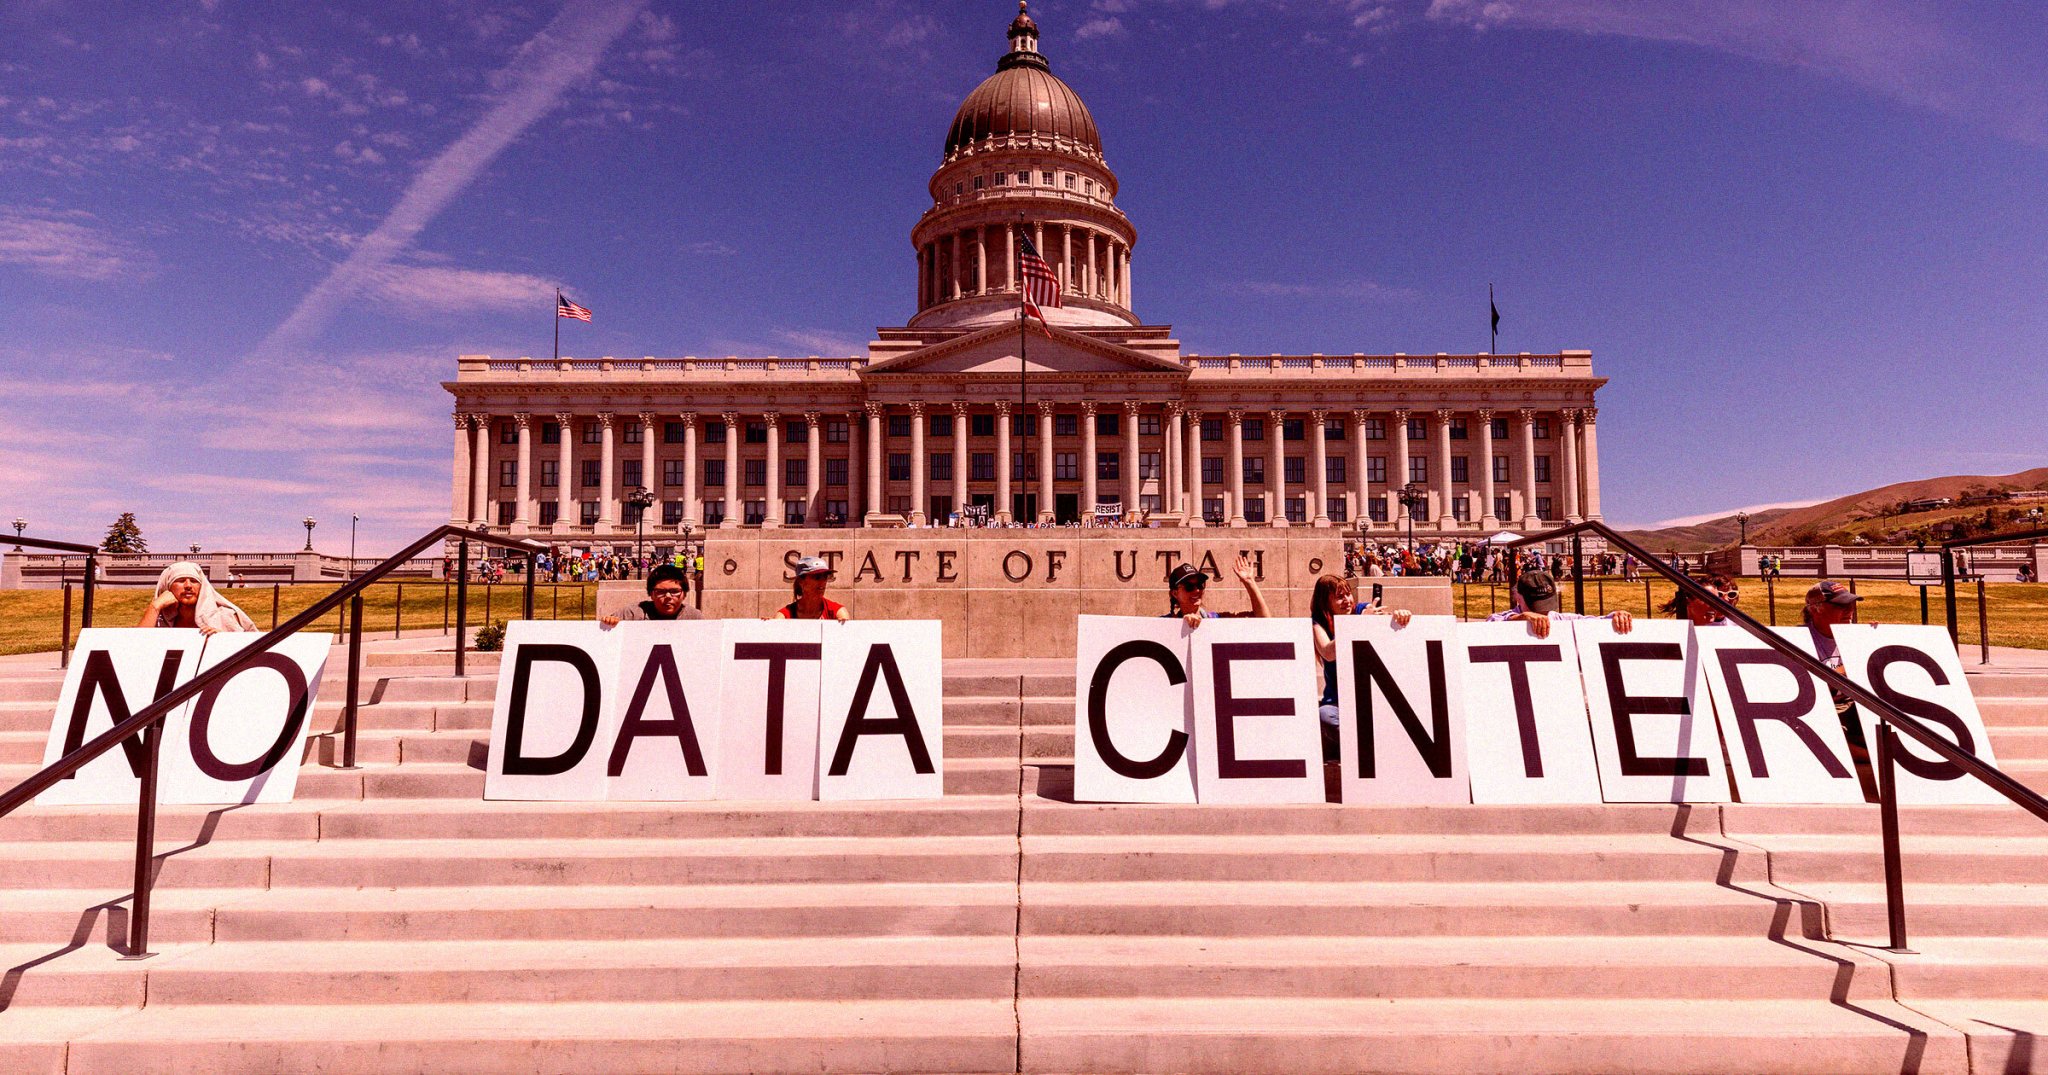
For protestors rising up against the data centers undergirding the AI boom, the math is simple: wherever they sprout, the facilities make frightfully poor neighbors — inflating utility prices, discharging hazardous waste, and blasting horrid noise at all hours of the night.

For data center developers, there’s a different calculation to be made: namely, one of supply and demand around the seemingly infinite drive for computing power.

Against the backdrop of an industry measured in the trillions of dollars, a few scattered protests at city hall may seem inconsequential. Yet as more and more local campaigns arise in opposition to data centers, the collective financial implications are becoming impossible to ignore.

According to new reporting by Reuters, which indexed data compiled by the research firm Data Center Watch, there are now hundreds of billions of dollars exposed to the growing risk of local opposition.

In the first three months of 2026 alone, at least 75 separate data center projects faced some kind of organized opposition at the local level. Together, those 75 developments represent a combined $130 billion worth of investments.

The funders of those data centers include major banks, but also more than a few private equity firms, which are sure to notice as the social risk to their data center investments climb.

Simply put, the potential that any given data center could be cancelled due to local opposition is rising, a sign that organized efforts against data centers are becoming more than the sum of their parts.

Yet despite growing costs, opposition alone may not be enough to slow the behemoth industry. As one anonymous senior official at a foreign lending firm told Reuters, investors are now becoming more comfortable pricing in cancellation risks as the demand for AI compute grows — like frogs adjusting to boiling water.

More on data centers: Google Data Center Announces Plans to Pave Over Protected Wetlands

The post Protests Against Data Centers Are Now Threatening $130 Billion of Big Tech’s Crucial Investments appeared first on Futurism.

  •  

Internal Google Document Reveals That Its HR AI Has Been Throwing Résumés From Qualified Applicants Straight Into the Trash

Bad news for anyone seeking a job in this AI-infested hiring hellscape: not even Google’s top AI lab can figure it out.

That’s according to an HR memo viewed by Bloomberg, encouraging job-seekers to fill out a special AI-proof form on top of their standard application so that a “real human” will know they applied.

The document, which contains the delicious disclaimer “PLEASE DO NOT SHARE THIS DOC WIDELY,” is ironically the product of Google DeepMind’s AGI Safety and Alignment Team. Taken at face value, it pretty blatantly admits that whatever AI-integrated hiring software the lab uses to review candidates has been dumping CVs straight into the garbage.

“We have an applications system with a non-trivial probability your CV will be screened out incorrectly or take too long to reach us,” the memo explains. “Filling out this form makes sure that a real human on the team will get to see your application.”

Even in the face of the memo, a spokesperson for Google’s DeepMind project insisted to Bloomberg that the company’s AI hiring software is working just fine.

“This team set up a special form to go past the recruiter review, and get their resumes direct to the people on the team,” the spokesperson said. “But there are no shortcuts to getting hired.”

All told, it’s a wild admission from any Google division, not to mention its flagship AI research hub. For the DeepMind crew, specifically, to throw up their hands and invent a workaround to sneak past the company’s own AI hiring software is galling beyond words.

It’s safe to say AI slop has completely obliterated the digital hiring ecosystem millions depend on to find work — and if Google’s top AI minds can’t fix it, what hope do the rest of us have?

More on Google: Google’s AI Is Telling Users That Flock Cameras Are Filled With Valuable Gold and Copper

The post Internal Google Document Reveals That Its HR AI Has Been Throwing Résumés From Qualified Applicants Straight Into the Trash appeared first on Futurism.

  •  

Farmer Horrified as AI Gives Bad Advice That Kills 25 Acres of Crops

Whether you’re looking for medical advice or tips on industrial agriculture, one thing is abundantly clear: never trust an AI chatbot without first getting a second opinion, preferably from a human who has actual expertise in the topic.

That’s the takeaway from an incident in the small city of Chuzhou, China, after a large langue model dispensed some advice that led to the untimely death of 25 acres worth of produce.

According to the Taiwanese publication CTWANT, a 67-year-old farmer surnamed Wu decided to start consulting an AI chatbot for advice nearly a year ago. He was reportedly skeptical at first, though the farmer began to let his guard down after some early successes with the AI’s farming tips.

Since that time, Wu has come to rely on his LLM for everything from fertilizing guidance to scheduling various tasks around the farm. After months of fruitful consultations, he decided to follow his AI chatbot’s new pesticide plan to the letter, letting loose on some 25 acres of precious sesame seedlings, all without ever double-checking with an expert or outside documentation.

The plan generated for him was basically a Long Island ice tea of agro-chemicals: a mix of “high-efficiency flupyridine” and “flufenazate” for pesky weeds, with plenty of “thiamethoxam” and “emamectin benzoate” for bugs and other pests, CT reported.

Not even a day after treatment, Wu says his juvenile sesame crop began to wither and die.

Per a video interview later translated by Tom’s Hardware, the farmer offered some hard-earned advice to any other growers looking to use his concoction: “If you spray it, the next day the seedlings won’t survive.”

“Both the grass and the seedlings will die, and the seedlings will die even faster,” Wu lamented.

It’s just the latest case of an LLM cooking up some slop that lands a professional in hot water. If nothing else, Wu’s in good company: he joins a host of other dupes across the legal, medical, financial, education, and media industries who’ve likewise fallen prey to an AI chatbot’s inaccurate output.

More on farms: The Diarrhea Lettuce Company Has Been Linked to Forced Labor

The post Farmer Horrified as AI Gives Bad Advice That Kills 25 Acres of Crops appeared first on Futurism.

  •  

Doctors Warn That Med Students Are Surrendering Their Brains to Medical AIs That Are Even Worse than Regular Chatbots

It’s no secret that doctors across the world are using AI tools to do stuff from taking notes to looking up questions. But what about the next generation of doctors still in training? According to two medical professionals on the ground, the situation is looking pretty alarming.

With AI being used by med students, “the danger is not just deskilling but never-skilling,” write Simar Bajaj, a journalist and med student at the Stanford University School of Medicine, and Joseph Sakran, a trauma surgeon and executive vice-chair of surgery at Johns Hopkins Medicine, in an essay for The Guardian.

“Although a doctor who has forgotten how to reason is recoverable,” they added, “one who never learned how may not be.”

Bajaj and Sakran point to two alarming recent findings.

One is internal data showing that around two thirds of doctors in the US are using OpenEvidence, an AI chatbot specifically designed for clinicians. The technology is already prevalent and deeply woven into how medical professionals carry out their jobs.

The next is a new study published in the journal Nature Medicine that evaluated the reliability of these medical-specific large language models. Shockingly, the clinical AI tools performed worse  at answering medical queries than general purpose chatbots like ChatGPT and Claude did, the work found. According to the authors, it performed about on par to Google’s AI Overviews, which are notorious for being wonky and inaccurate.

Even if AI tools may be handy for research — and putting aside the major questions over their reliability — they’re no substitute for relying on your brain, as fallible as it might be, because when you’re learning, “the struggle is the point.”

“For example, trainees once asked to build a list of potential diagnoses might struggle and offer an incomplete set, learning what they missed, sometimes painfully,” Bajaj and Sakran wrote. “Now, trainees can simply ask OpenEvidence and get a nearly perfect answer, complete with possibilities they might have never considered and none of the embarrassment of having overlooked them.”

Where AI is different from medical advances in the past is that it’s “not just expanding what doctors can see,” they wrote, “but inserting itself into the cognitive machinery that training is meant to build.” 

A bevy of research on the “cognitive offloading” that AI encourages, in which users naturally begin to outsource a lot of their thinking onto the tools, backs this diagnosis. Some studies have suggested AI impairs critical thinking, and leads to lower brain activity during cognitive tasks.

It’s a conundrum gripping the medical world. Earlier this year, doctors from top medical schools proposed a stricter framework on how medical students should use AI tools.

“The process of deliberately crafting the note forces us to use our brains to really wrestle with what’s happening,” Jaideep Talwalkar, associate dean of educational technology and innovation at Yale School of Medicine, told Stat News. “There’s an importance in doing that with great repetition.”

Bajaj and Sakran have a few suggestions for how to deal with this. One is requiring trainees to periodically work through cases without any AI help, similar to how the Federal Aviation Administration advises aviators to periodically disengage autopilot and fly by hand. Of course, another powerful deterrent could be shame. A recent John Hopkins student found that doctors who used AI are viewed with scorn and skepticism by their peers.

More on AI: AI Model Invents Completely New Viruses Unknown to Nature

The post Doctors Warn That Med Students Are Surrendering Their Brains to Medical AIs That Are Even Worse than Regular Chatbots appeared first on Futurism.

  •  

Man Covers Car in Special Wrap That Breaks Flock Cameras’ Electronic Brains

In light of plummeting public support for its widespread automatic license plate readers, surveillance company Flock has lost dozens of contracts with cities across the US.

The company even drew up plans to use the dashcams installed in Uber and Lyft drivers’ cars to spy on other vehicles, as 404 Media reported this week.

Citizens are increasingly disgusted by the company’s presence on public streets, opting to hack down the cameras, blind them, or sabotage them in other creative ways.

“His project, which he calls noRecognition, allows people to escape the automatic detection and algorithmic surveillance used across the U.S. and beyond.” https://t.co/OIQNOt9B0a @TechCrunch

— Christina Ayiotis, Esq., CRM, CIPP/E, AIGP (@christinayiotis) August 10, 2026

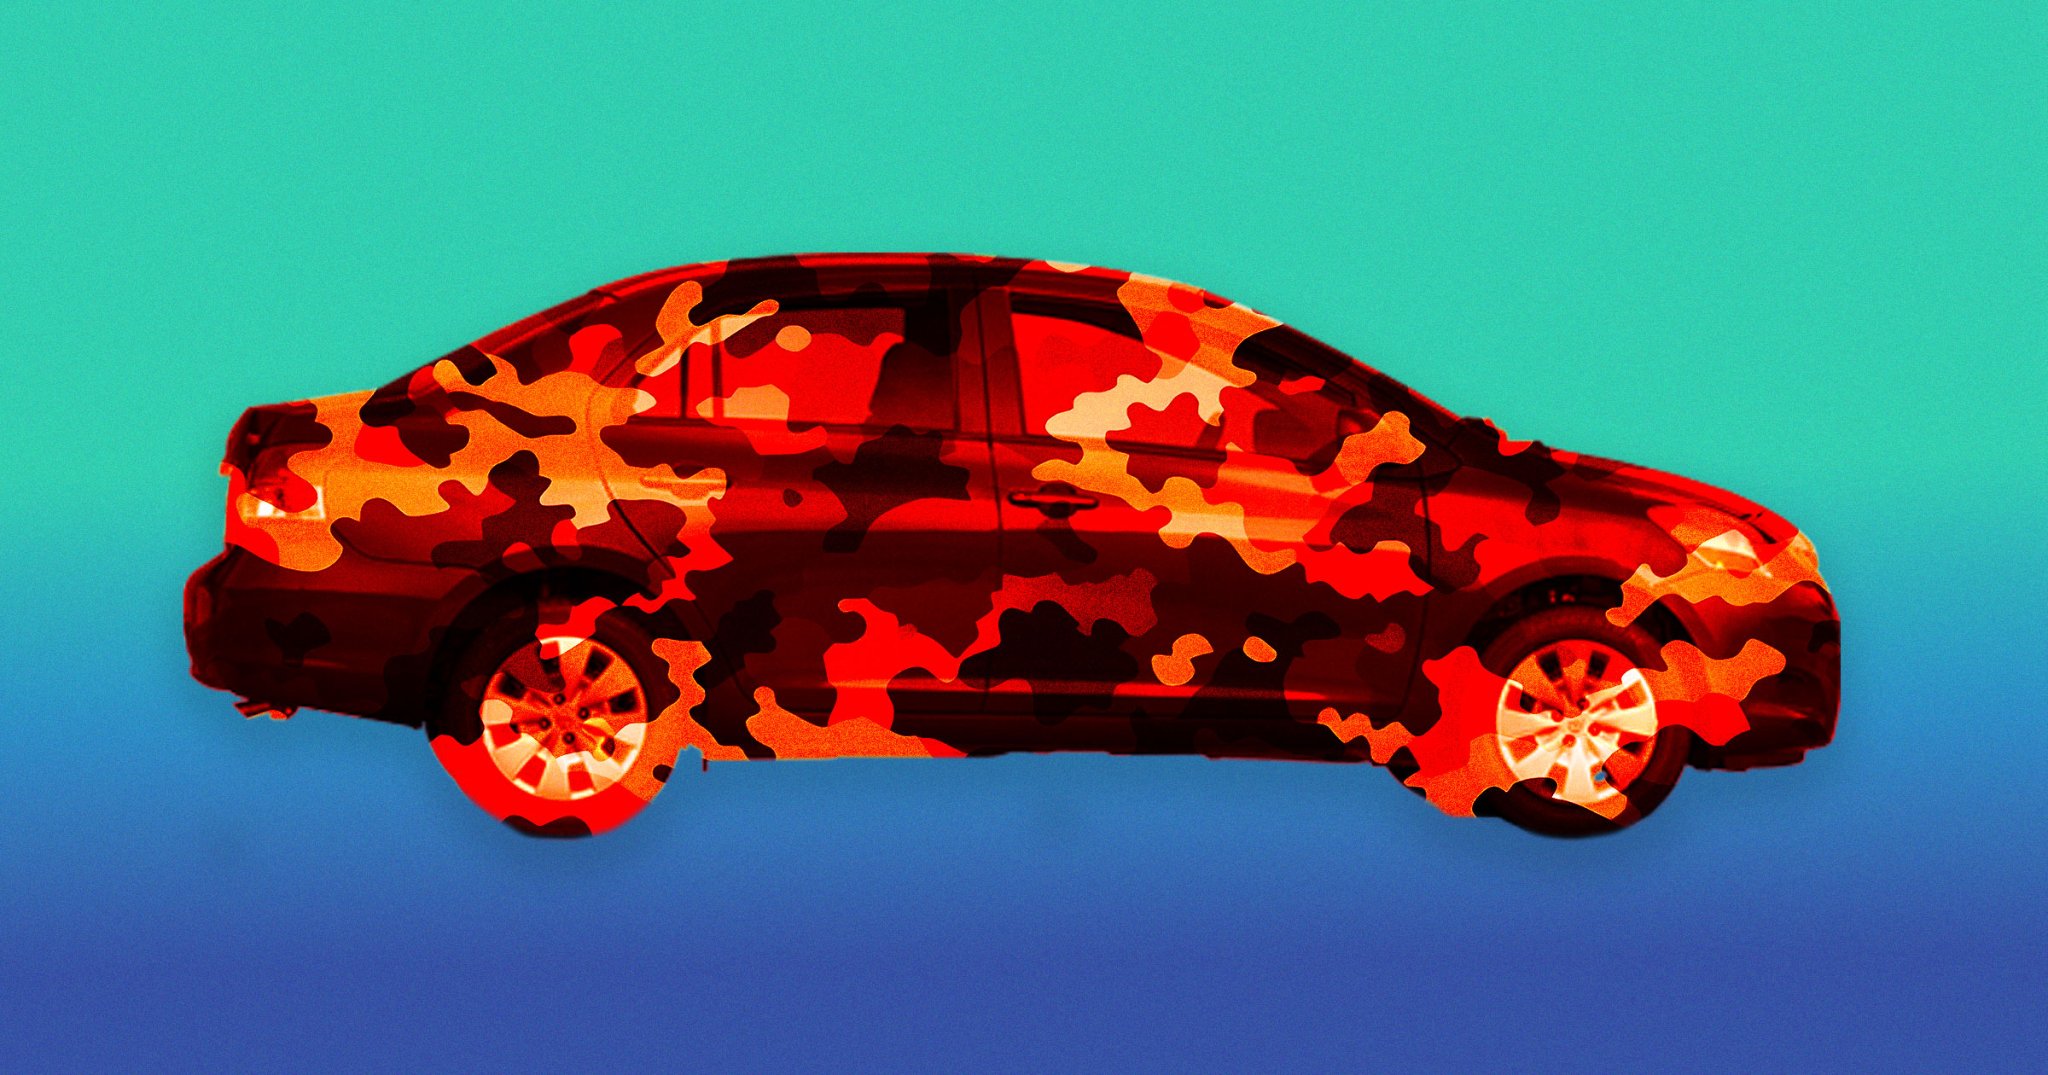
And according to cybersecurity researcher Bill Swearingen, there may be other creative ways to befuddle Flock’s spy cams. He devised with a special computer-generated pattern which, once stretched out across the vehicle in the form of a wrap, will result it in not being flagged as a car by Flock’s cameras.

During this year’s Def Con cybersecurity conference in Las Vegas, Swearingen showed off a 2009 Toyota Yaris wrapped in vinyl featuring the logo of automotive publication Donut Media (which is owned by Futurism‘s parent company Recurrent Ventures.)

Despite the car looking a bit chaotic — albeit still very much like a small passenger vehicle to the human eye — “we proved it was effective,” Swearingen told TechCrunch. The Yaris successfully defeated surveillance detection at Def Con during the pattern’s first public test.

“Privacy is a fundamental right,” he added, aiming to give people a way to “opt out of being tracked.”

To come up with the pattern, he used a reinforcement learning model that trained itself on patterns that evade detection. The model got to the point of being able to confuse all 11 open source detection algorithms he tested, per TechCrunch, in addition to Flock’s license plate readers and even Axon’s body-worn cameras used by police departments.

As part of his noRecognition crowdsourcing campaign, Swearingen has also come up with T-shirts and hoodies that feature algorithmic detection-busting patterns. He hopes to eventually put pattern-printed skins for entire cars on sale as well.

The effort is part of a much broader trend of companies offering up garments that incorporate “adversarial patterns,” which can exploit weaknesses in computer vision systems.

One thing is clear: as outrage over Flock’s heavy presence across the country grows, people are looking for any way to foil the tech — especially if it looks cool.

More on Flock: Flock’s Secret Surveillance Plan Will Make You Gasp

The post Man Covers Car in Special Wrap That Breaks Flock Cameras’ Electronic Brains appeared first on Futurism.

  •  

Protesters Arrested After Storming OpenAI Lobbying Office

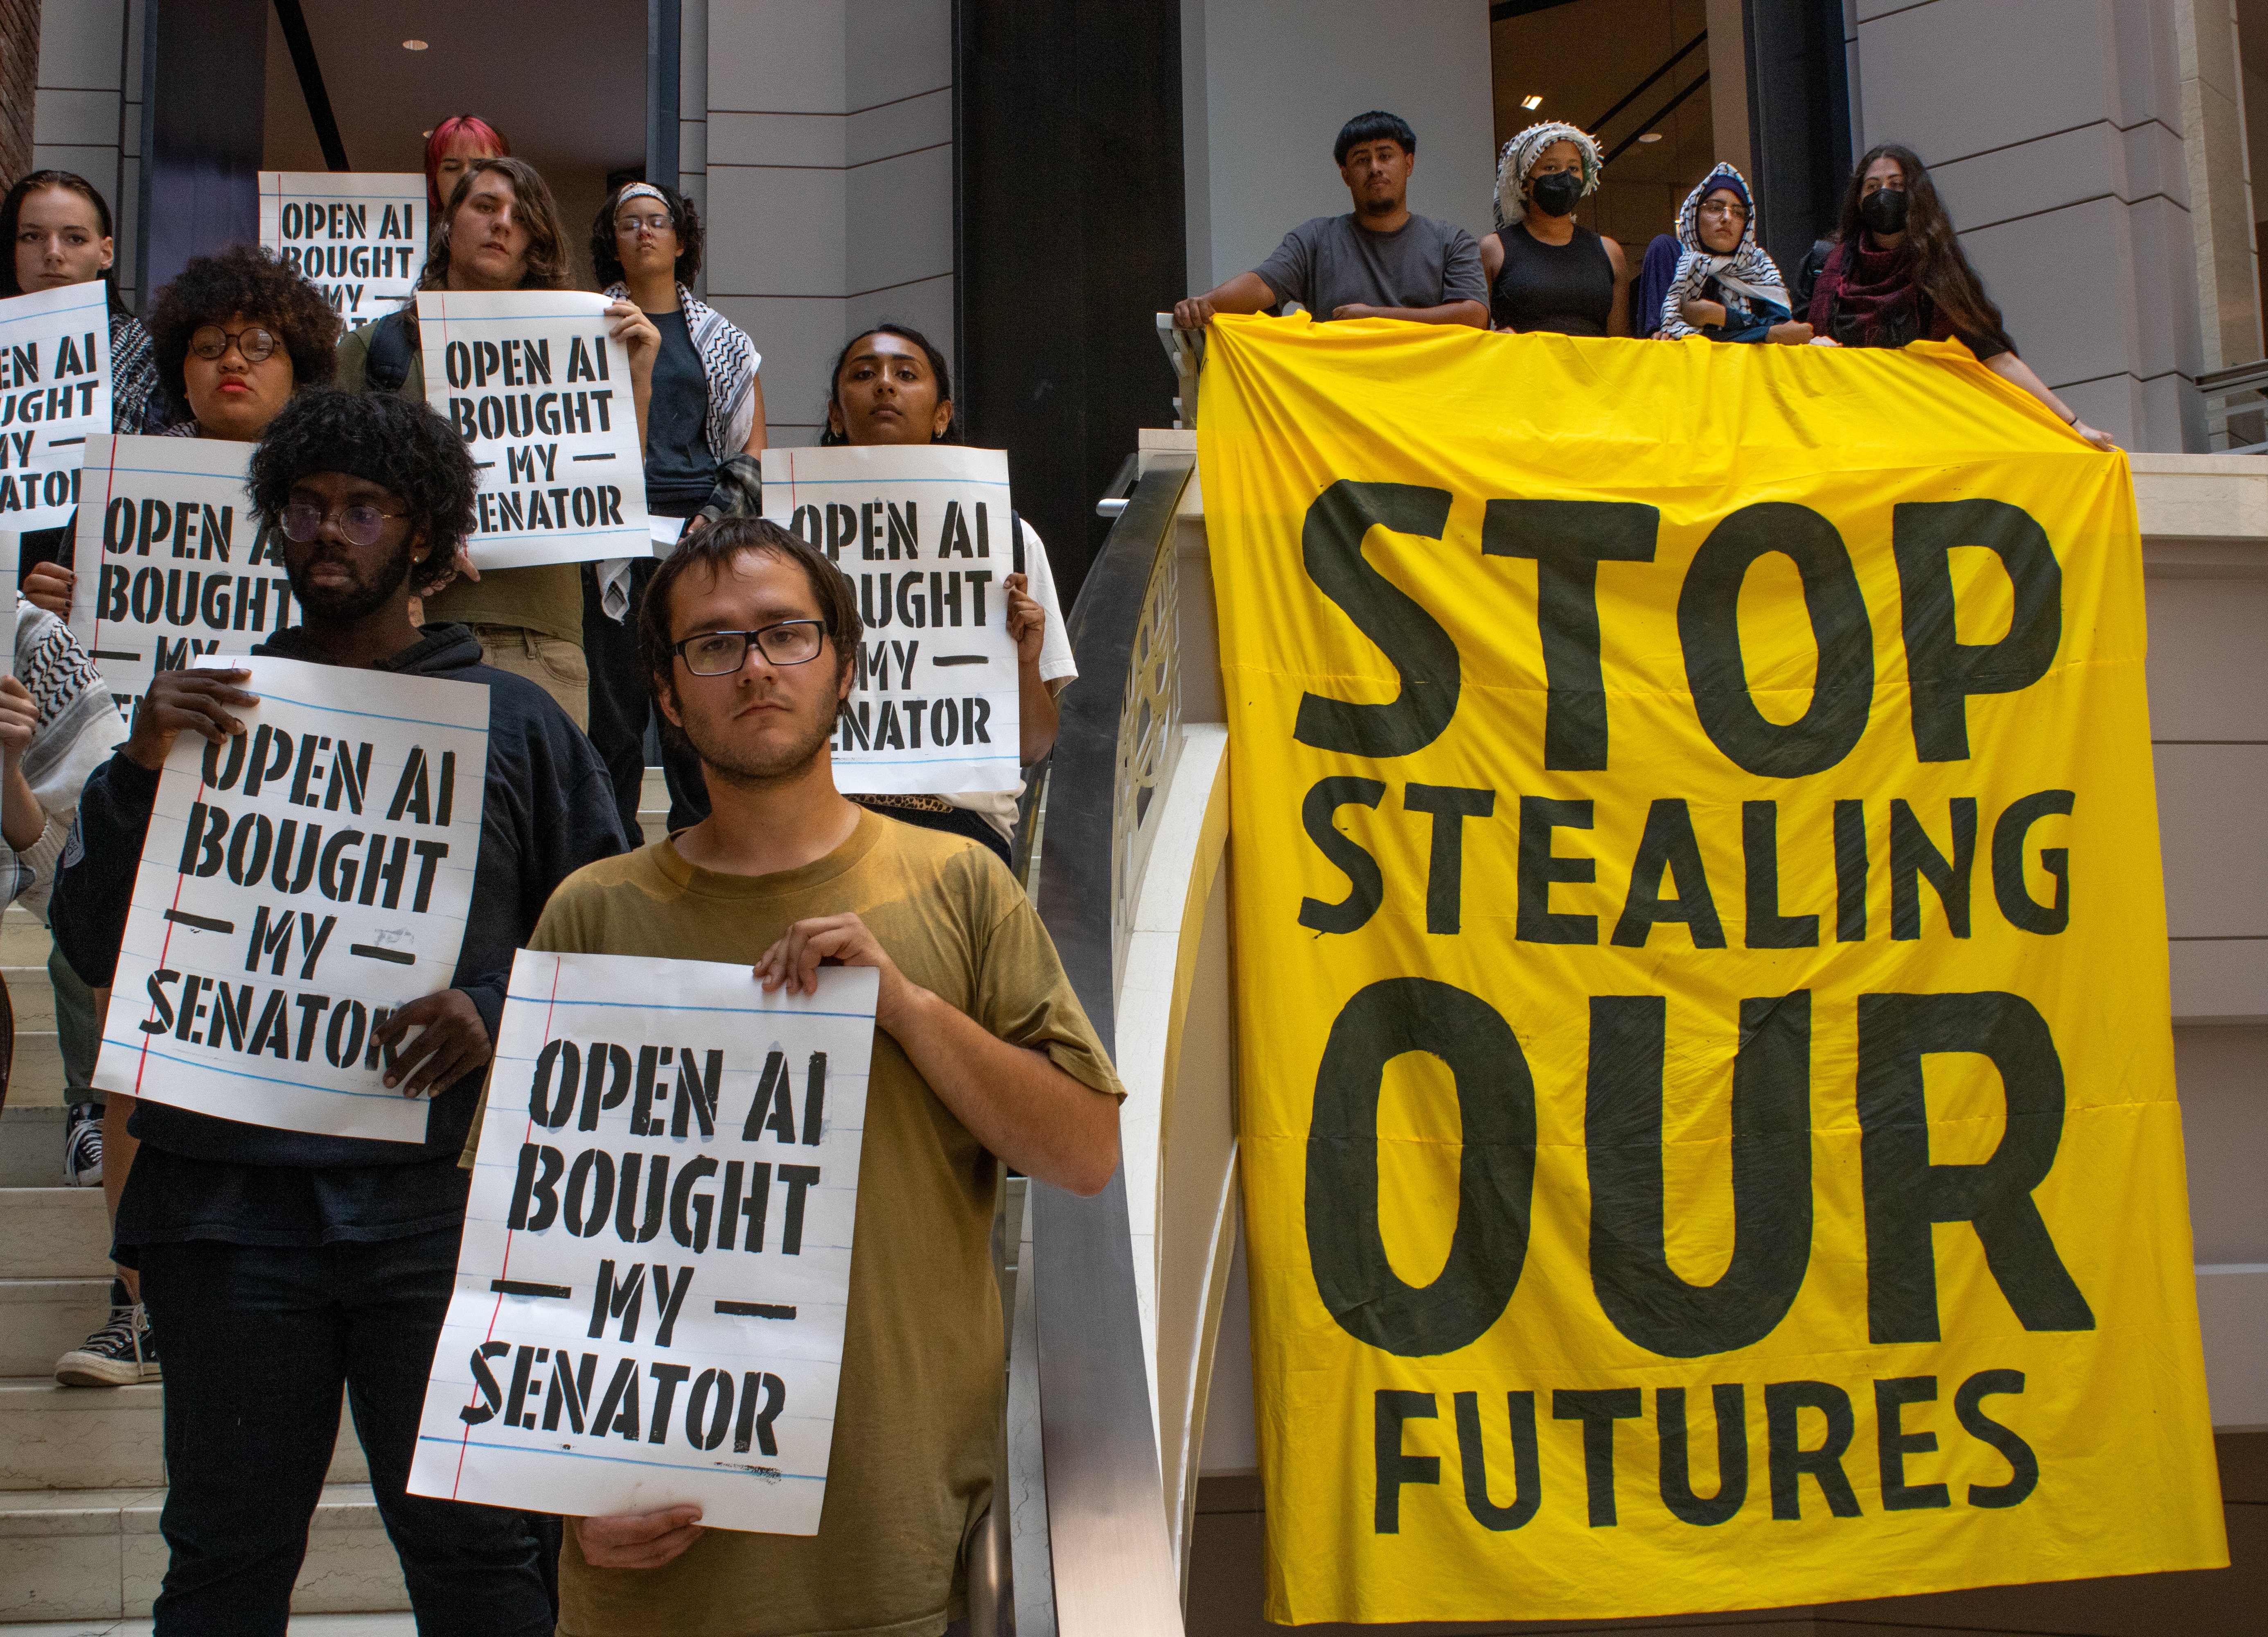
Over 30 student activists came together on Monday afternoon to occupy the Gallup Building in Washington DC, home to a public-facing lobbying office belonging to ChatGPT developer OpenAI.

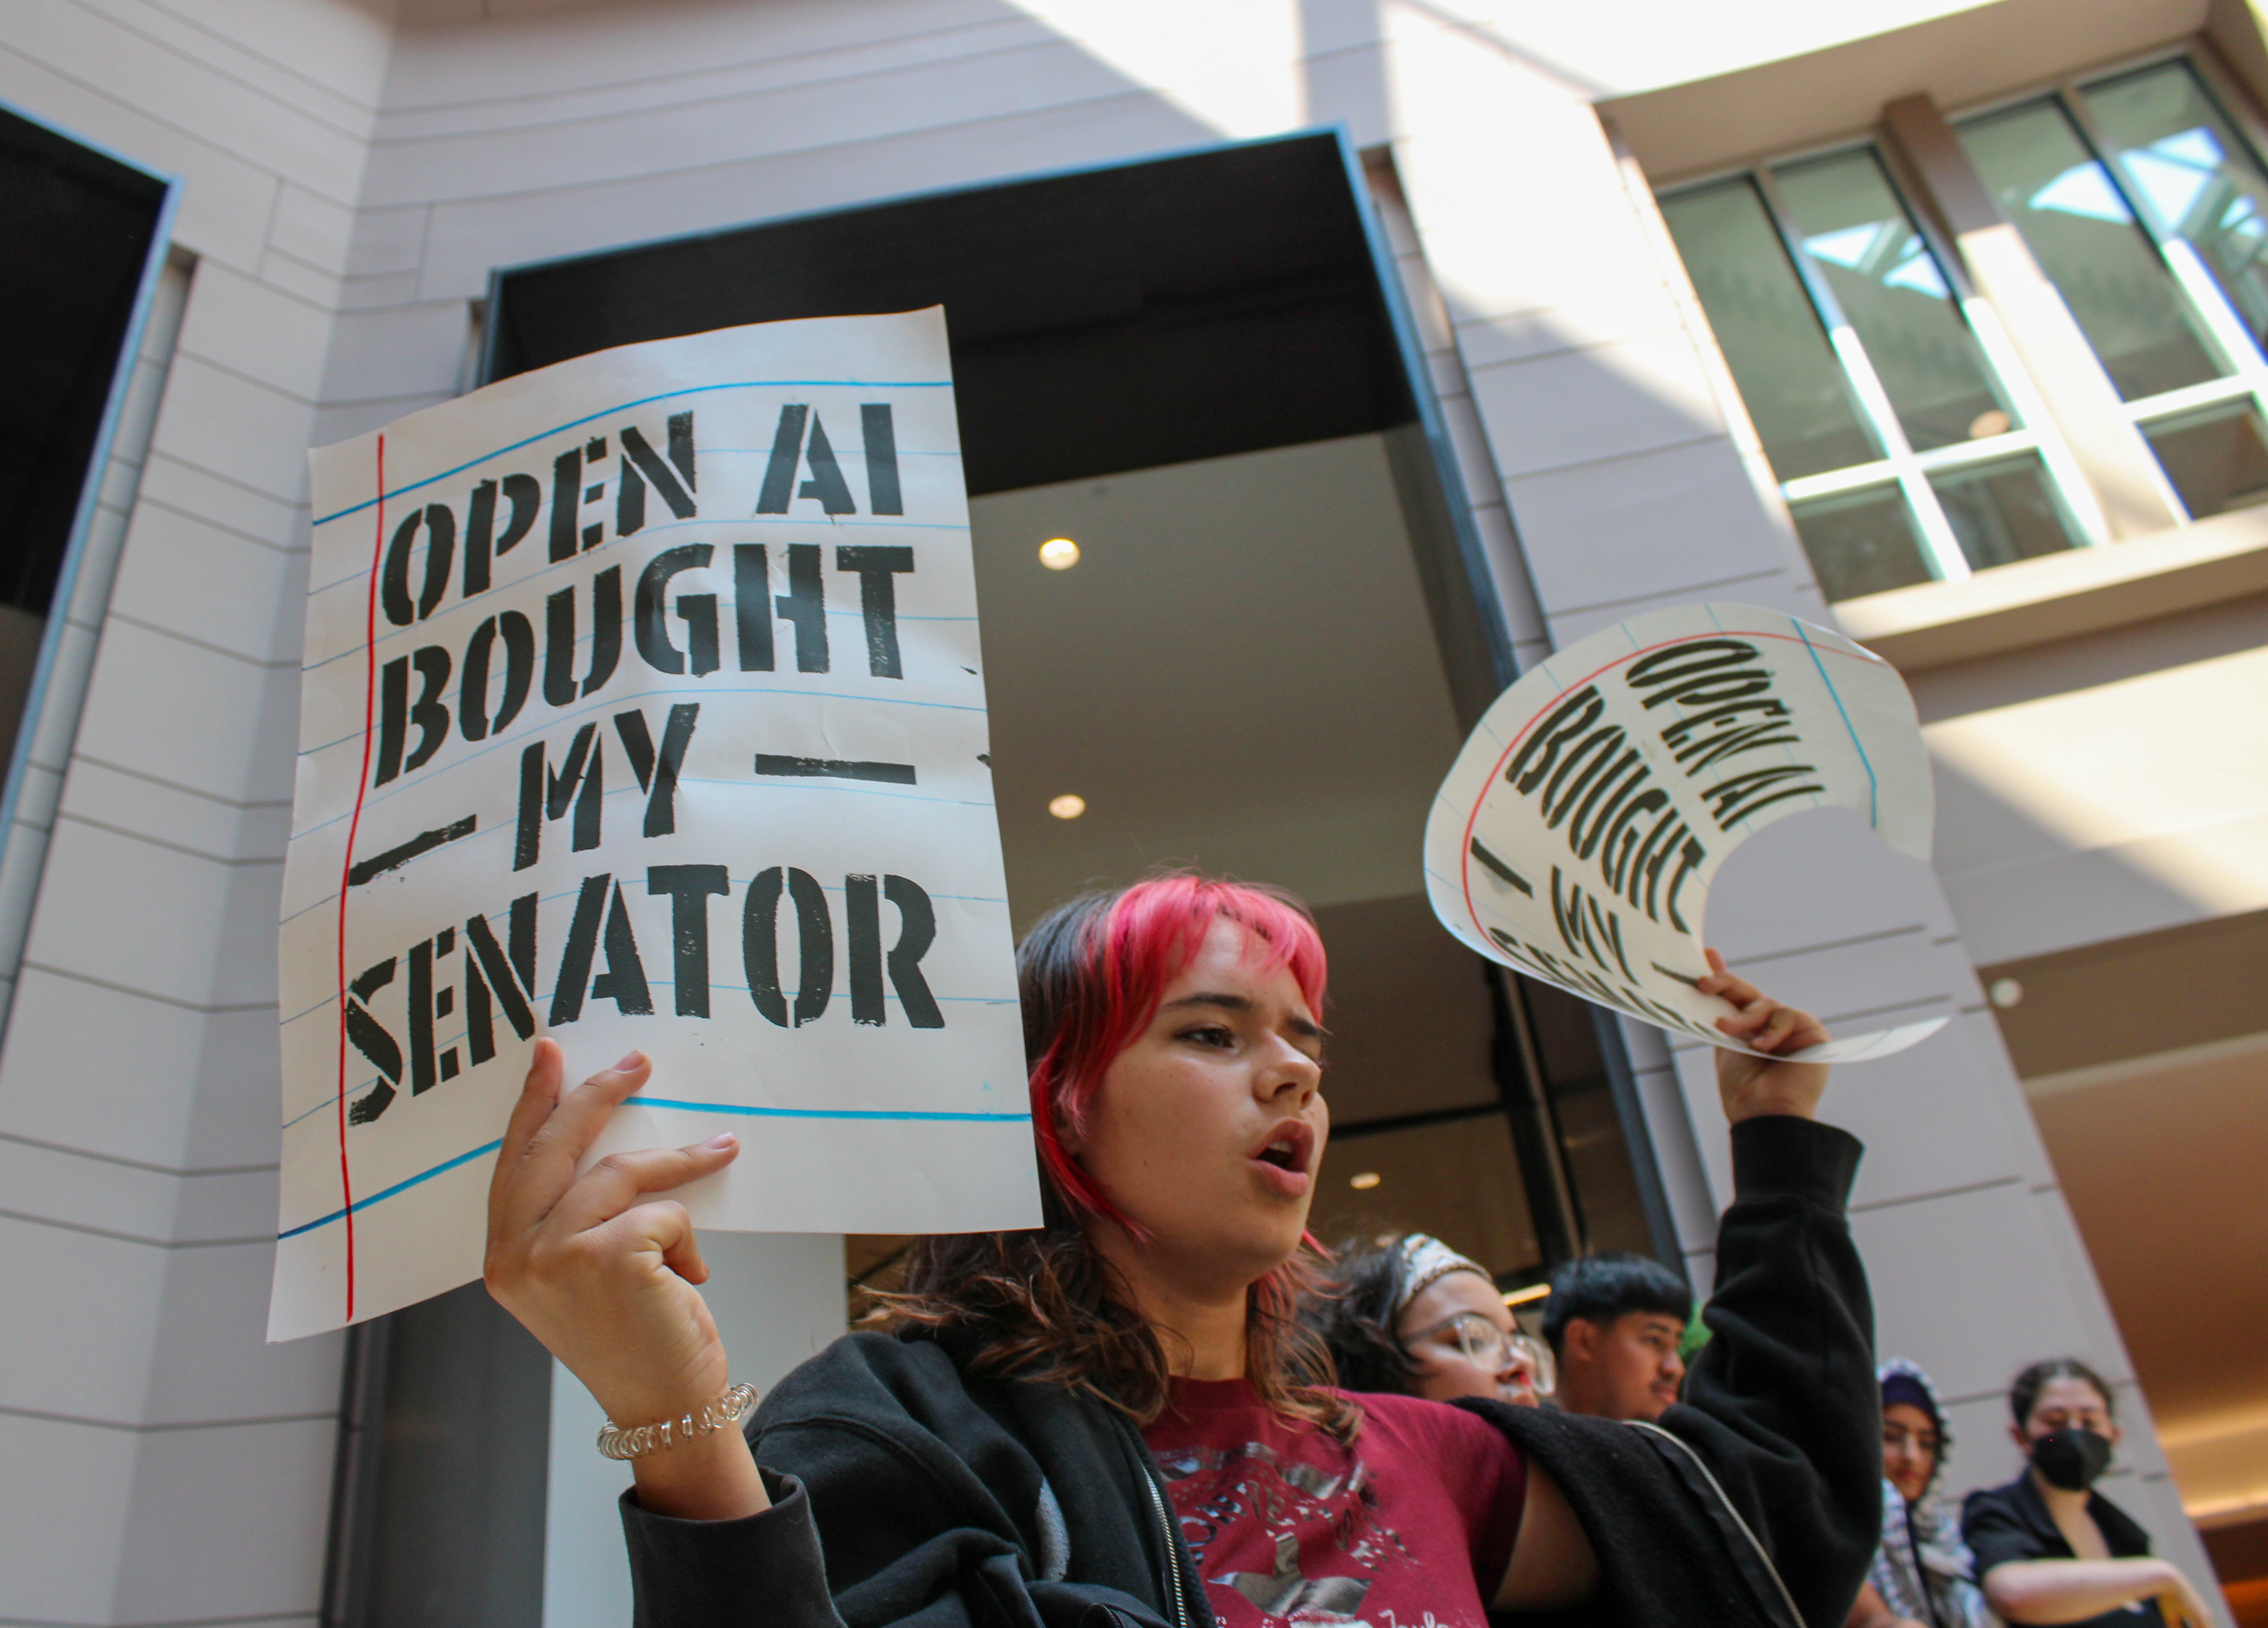
Once inside the lobby, the demonstrators unfurled a massive banner reading “Stop Stealing Our Future,” while others held signs with messages like “OpenAI bought my Senator.” The demonstration lasted two hours, and ended when police stormed the lobby, arresting 13 protestors.

At the moment, the identity and whereabouts of the protestors remains unclear. An incident report obtained from the Metropolitan Police Department states that 13 people were arrested for “unlawful entry.” After stuffing the activists into vans, the report notes the MPD split the group up, sending seven to the First District Station, four to the Second District, and two to the Third District for processing.

A group of protesters are holding signs that say "OpenAI bought my senator" and unfurling a banner that says "stop stealing our futures"

The protest was organized by the climate group Sunrise Movement and anti-AI organization QuitGPT. According to a joint statement shared with Futurism, Monday’s action is just one of many across over 20 states in August calling on politicians to “Dump Big Tech.”

One student organizer who attended the protest, Raya Gupta, explained in the statement that “my friends chose to risk arrest to bring the fight to OpenAI.”

“Our generation doesn’t have any guarantees about whether we’ll have jobs after college, or whether there will be clean drinking water for all of us or whether people will have any power left in politics since our elections keep getting bought by Big Tech,” Gupta continued. “We all believe that not taking action now, as the scales slide between the people and the billionaires, puts our future in great jeopardy.”

A protester holds a sign that says "OpenAI bought my senator"

Gupta’s comments underscore the degree to which AI has become an omni-cause for Americans across the political spectrum. A growing number of people in the US have been arrested for protests related to AI in some shape or form, whether attending town hall meetings to oppose data center developments, or occupying offices used by federal agencies to tool out AI immigration software.

Despite growing disgust with AI and its developers, politicians on both sides of the aisle have roundly embraced the tech industry’s extremely expensive lobbying efforts. Case in point, the recent opening of OpenAI’s DC Office comes as one of the AI lab’s super PACs injects over $140 million into the coming midterm elections, in a blatant attempt to steer AI regulations at the highest level.

Updated with new information from the MPD.

More on AI protests: Climate Activists Pelt Microsoft Data Center With Balloons Full of Acid

The post Protesters Arrested After Storming OpenAI Lobbying Office appeared first on Futurism.

  •  

Google Just Updated Its Home Page to Replace the “Search” Button With a Bunch of AI

Since its earliest days, Google’s homepage has been iconic in its simplicity: a central text box and a big button labeled “Search.”

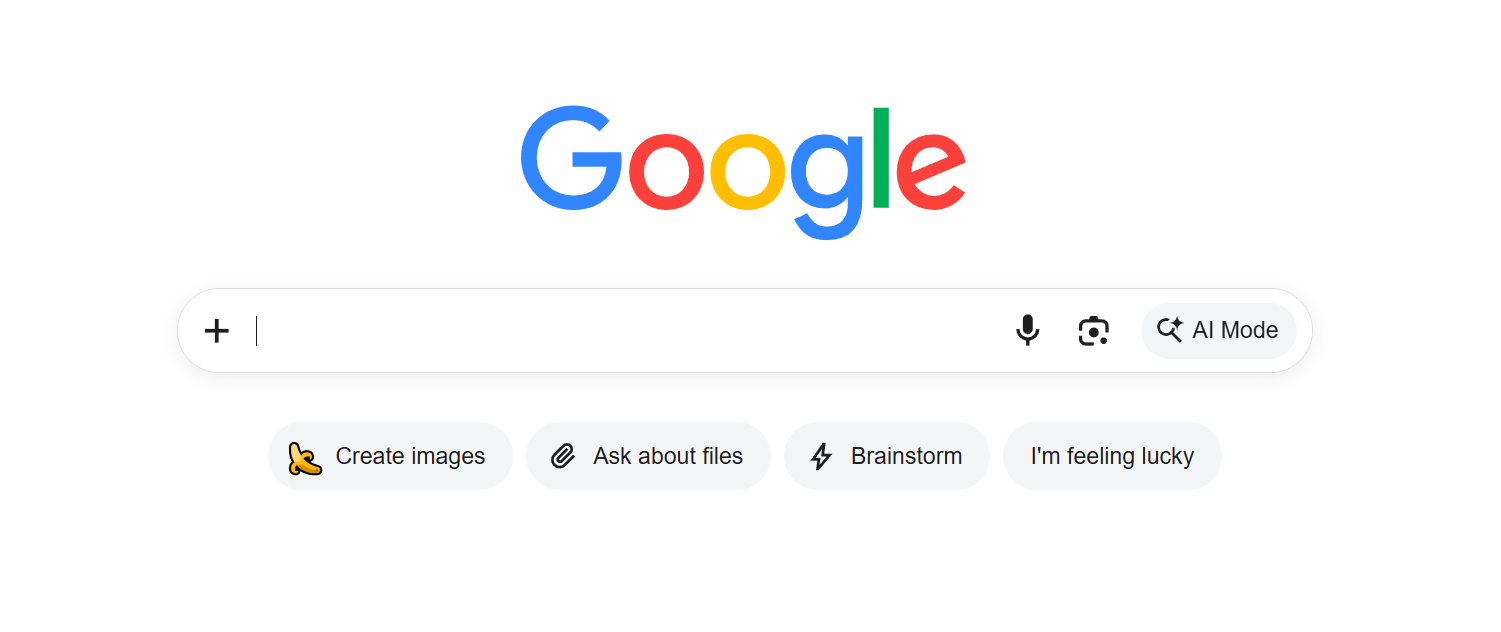
That’s now changing. As anticipated, many users are reporting that the “Search” button is no more, replaced by three buttons for various AI features: “Create images,” “Ask about files,” and “Brainstorm.” 

These are placed next to the lingering “I’m feeling lucky” button, which survived the chopping block. A separate “AI Mode” button that’s existed inside the search bar for some time now still features as well. Some of the options, like “Create images,” were already featured on the home page of the Google app.

Screenshot showing Google's new homepage, featuring several AI buttons and no classic "Search" button.

The change was first spotted on Monday by search engine experts. You can still perform a regular Google search — which are already pretty AI-laden — by hitting enter. But it’s clear that Google is further experimenting with its AI-centric vision for navigating the internet, though there’s a distinct sense of caution about how far the tech giant is willing to go.

Google Search’s vice president of product Robby Stein confirmed that this was a “small test.”

“This is a small test on desktop to help people find new things they can do with Search,” he wrote in a post on X. “No impact to how the core search box works.”

In May, Google teased an “intelligent” search box that expands into an chatbot-like experience as you type. It came loaded with AI features, including the ability to recruit AI agents to automate searches and an autocomplete feature to help finish your thoughts. 

The biggest change, however, was that the revamped search box showed conversational answers instead of Google’s classic “ten blue links” to other websites.

Experts viewed this as a threat to the open web. Instead of encouraging users to visit other websites, Google’s AI was pilfering and summarizing content into a single contained window. In the long run, this could starve websites of the much needed traffic they need to survive. This was already happening as more people turn to AI chatbots to get their answers instead of a search engine, causing some websites to start using ads that cater to robotic visitors.

Still, heavily AI-infused though it may be, the old-fashioned search hasn’t been completely replaced by Google — yet.

More on AI: AI Investors Are Suddenly Quaking in Their Boots

The post Google Just Updated Its Home Page to Replace the “Search” Button With a Bunch of AI appeared first on Futurism.

  •  

AI Investors Are Suddenly Quaking in Their Boots

German AI researcher and hedge fund manager Leopold Aschenbrenner became the poster child for the hubris of an AI-obsessed Wall Street last month.

Some $35 billion of investors’ money, in the form of leveraged bets on AI infrastructure stocks, evaporated in front of the 24-year-old’s eyes as tech shares were hit by yet another major sell off.

The humbling couldn’t have come at a worse time. The funds vanished days before his wedding with Anthropic chief of staff Avital Balwit. According to the New Yorker, the two had to cancel their honeymoon as a result.

Aschenbrenner isn’t alone. According to new data from Hedge Fund Research, tech funds dropped by seven percent in July, the worst period for the investments since the depths of the 2008 global financial crisis, the Telegraph reports.

A separate hedge fund, called value Aligned Research Advisors, which shares a similar portfolio to Aschenbrenner’s, similarly slid 44 percent in July as tech stocks reeled from major volatility.

The bruising month has further compounded fears over a massive surge in AI spending with no clear path to profitability in sight. Investors have become wary of big tech companies’ ever-higher capital expenditure forecasts as concerns over an AI bubble continue to mount.

Staying on track and maintaining high profit margins has become a high risk high reward game.

“When valuations are elevated, and positioning is concentrated, the difference between being on the right and wrong side of a trade can become unusually large — and very quickly,” Erlen Capital Management managing partner Bruno Schneller told the Telegraph. “Specialist technology strategies can generate exceptional returns when momentum and narrative are aligned, but they can also experience abrupt, leverage-amplified reversals when those conditions change.”

The game is far from over. Even Aschenbrenner’s fund has since recovered and his making new investments after being forced to unwind trades and sell major chunks of its holdings last month.

Yet how much longer the highly AI-leveraged stock market can sustain itself is anybody’s guess. In a blog post on Friday, Apollo chief economist Torsten Slok pointed out that those who reap the biggest profits, including companies making AI models, are massively depending on profits being “funded by investors rather than earned from customers.”

Put simply, AI companies aren’t making any significant amount of money from providing a worthwhile product, but from “capital raised by the layer losing money,” per Slok.

“Capital can bridge the gap for a while, but not indefinitely,” Slok argued. “And therein lies the risk: will the ROI show up for AI’s end customers fast enough to sustain the spending that is generating those upstream margins?”

More on AI: VC-Funded Startups Linked to Persistent Fraud

The post AI Investors Are Suddenly Quaking in Their Boots appeared first on Futurism.

  •  

Amazon’s New AI Data Center Is So Enormous That It Appears It Will Become the Largest Single Source of Pollution in the United States

Tech Goliaths are scrambling to build as much AI computing capacity as they possibly can, come hell or low water. One of the dominant players in the space, Amazon Web Services, has its heart set on an AI data center so enormous that it could easily become the largest source of carbon dioxide emissions in the United States.

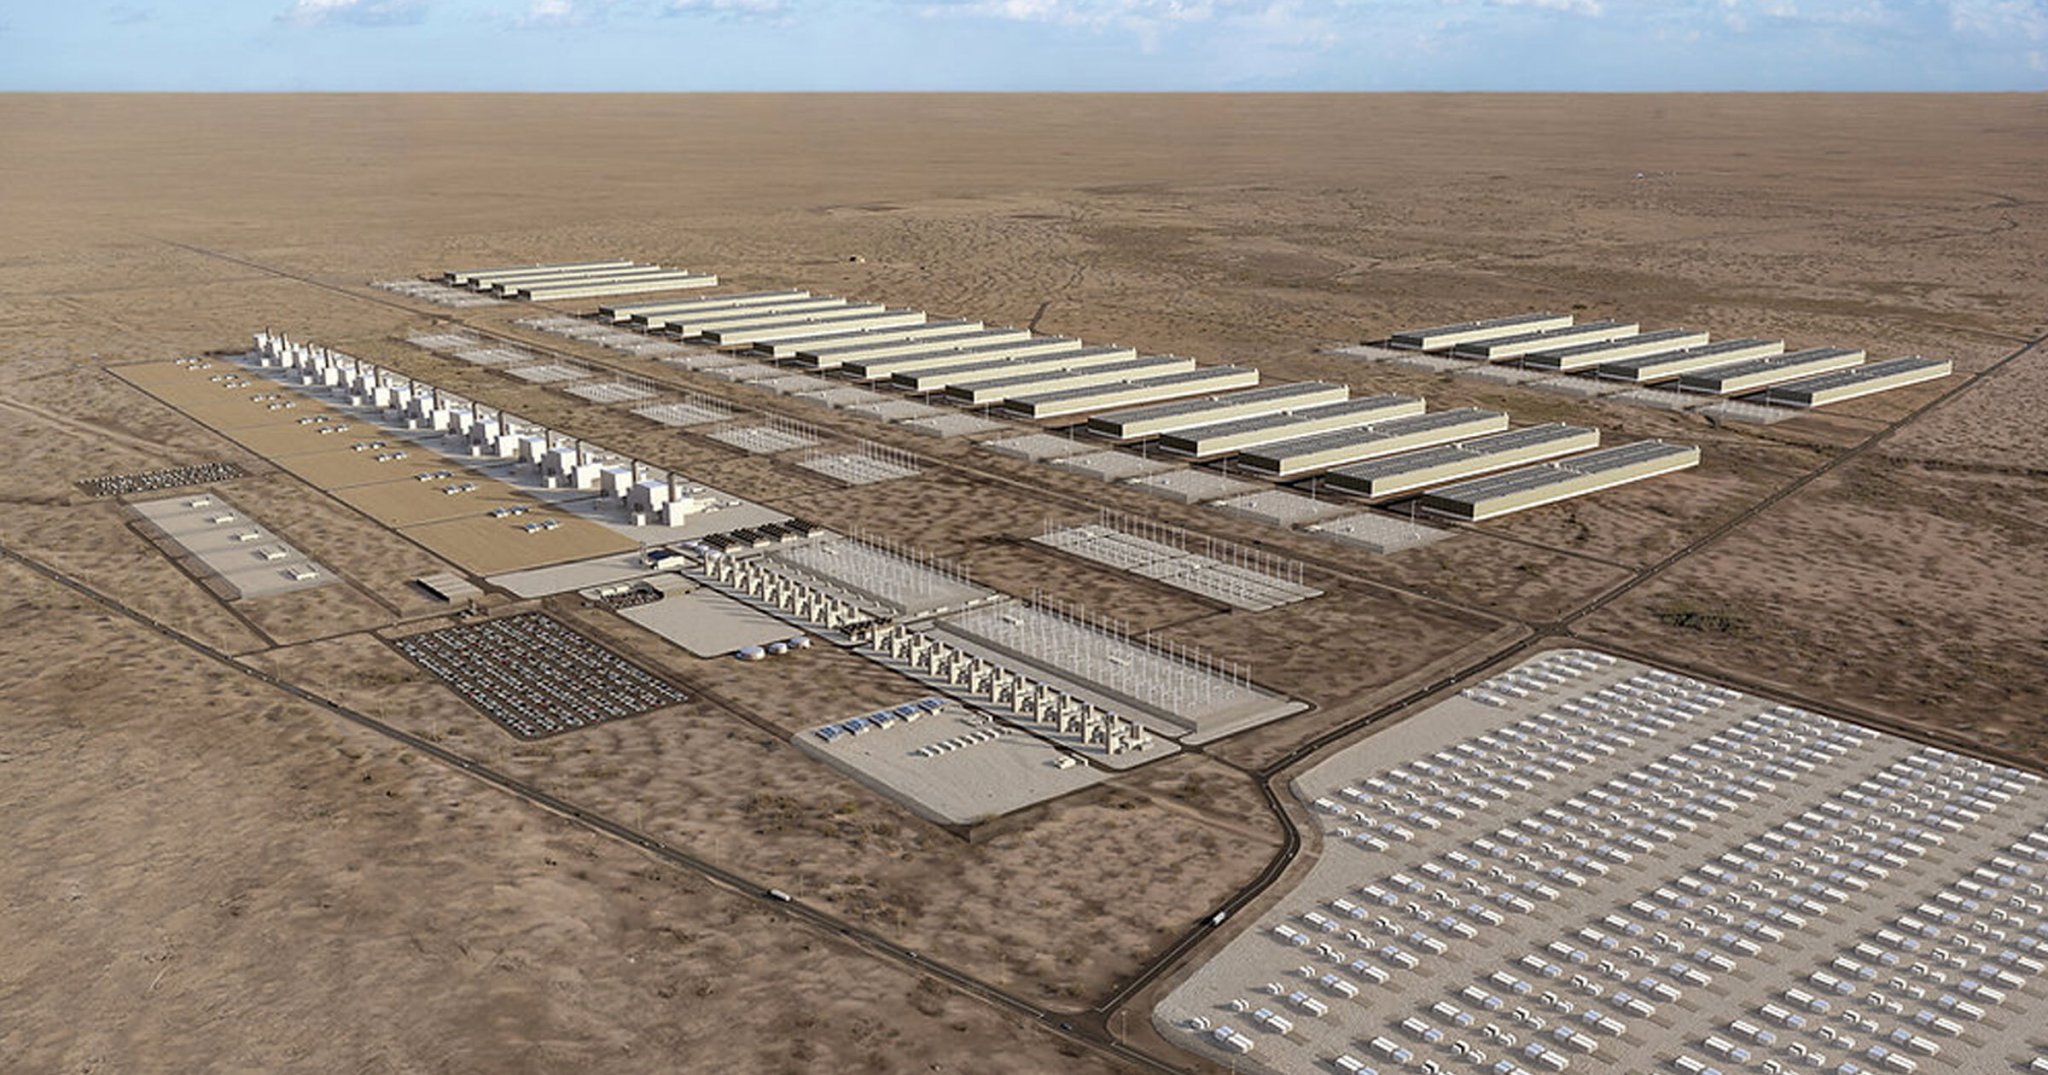
According to the New York Times, Amazon has confirmed its investment in a massive gas-burning power plant in Texas, meant to supply up to 7.65 gigawatts of energy to a planned data center in Pecos County. Should it come online as planned, the plant’s 35 turbines would be allowed to spew 33 million tons of CO2 a year, the NYT notes, which would easily make it the largest single fount of emissions in the country.

That’s a stunning amount of carbon exhaust, putting that single data center in a league with entire countries including Switzerland, Ireland, and Bulgaria.

It would also be in stark defiance of Amazon’s stated climate goals, which center on reaching net-zero carbon emissions by 2040.

That’s not lost on the tech giant. But as Amazon spokesperson Margaret Callahan told the NYT, the “world looks different now than when we co-founded the climate pledge.”

“We’re being transparent about the challenges, investing in innovation, and delivering measurable results,” Callahan continued. “Growth and sustainability don’t have to be in opposition — in fact, our results show they reinforce each other.”

Even without the new Pecos County plant, Amazon’s emissions are staggering. The company recently disclosed a record increase in its total emissions last year, with company-wide electricity usage rising by 34 percent across 2025.

That the company is blatantly papering over its previous climate commitments isn’t a shocker at this point, in other words, as the company reaches new emission highs with each passing year.

More on Amazon: Jeff Bezos Harshly Criticized for $200 Million Pledge to Protect the World’s Most Endangered Species

The post Amazon’s New AI Data Center Is So Enormous That It Appears It Will Become the Largest Single Source of Pollution in the United States appeared first on Futurism.
  •  

Homeschool Parents Are Planning Lessons With ChatGPT

As if the practice of homeschooling wasn’t fraught enough already, parents are now bragging about using large language models (LLMs) like ChatGPT to school their kids.

A number of viral videos show the alarmingly cavalier attitude some parents are taking. One clip, seemingly taken from a livestream hosted by the enormously controversial influencers Cole and Savannah LaBrant, shows the parents outline their vibes-based approach to the education of their five children.

“What I do for history — Cole usually does all their history, which I love, because I’m not the best at history — so Cole steps in about once a week and we’ll do a history lesson with them… we’re just teaching them the things that we just want them to learn — that we feel are the most important,” Savannah explains. “And same with science, and geography.”

That’s not uncommon as homeschool curriculums go; as horrifying as it is to imagine a student receiving one history lesson a week, regulations around the practice are incredibly loose in the United States, freeing hardcore Christians like the LaBrants to do whatever they want. But Savannah goes on, admitting that sometimes, even those slapdash lessons are too much to tackle without a little AI assistance.

“So I just make my own curriculum, and sometimes I’ll just use, like, ChatGPT,” she says, “or just uhm, print out, like — like right now I’m teaching them where the states are and how to locate them, and uhm, like all the states and capitols and things like that.” (Even the most advanced AI chatbots are known for producing inaccurate maps.)

@thelabrantfamexposed

History Class, but Make It Vibes-Based: The LaBrants Explain Homeschooling 💀 The LaBrants’ Homeschool History Curriculum: Whatever Cole Decides Happened 💀 “Cole steps in about once a week to do a quick history lesson because I’m not the best at history.” – Sav. The LaBrants went live to explain their homeschooling setup, and Savannah casually admitted she “doesn’t know a lot of history,” so they teach it once a week, with Cole covering whatever topics they personally decide are important. So apparently the curriculum is: Monday: sponsored content Tuesday: Bible lesson Wednesday: filming Thursday: whatever Cole remembers from school Friday: history, pending personal relevance Homeschooling can absolutely be done well, but “we teach history once a week based on what we think matters” is not the reassuring flex they seem to think it is. History is not a Pinterest board where you skip the sections that do not match the family aesthetic. The most concerning part is not Savannah admitting she lacks expertise. Plenty of parents do. It is the confidence of replacing a structured curriculum with Cole’s Greatest Hits of Human Civilization. Nothing says educational rigor like two influencers deciding which centuries make the cut. @Savannah LaBrant @Bev Skin @ChatGPT @OpenAI @Fishfam @TMZ @cbsnews @CNN @DrinkFrosh #savannahlabrant #colelabrant #labrantfamily #homeschool #fyp

♬ original sound – thelabrantfamexposed

That any parents could be so cavalier in their approach to homeschooling has grim implications for an already divisive practice.

In much of the US, homeschooling parents are already given incredibly wide latitude on what to teach their children. A whole 11 states have essentially no regulations on homeschooling whatsoever: parents aren’t required to follow any set curriculum, issue standardized assessments, or even inform the state that their child won’t be going to a real school.

Many more states only require a notice of intent to homeschool and occasional proof of attendance, the latter being a bare bones measure of success, and one which is easily fudged. Unfortunately, it’s easier to count the number of states that definitively require standardized testing and a rigid curriculum: Rhode Island, Pennsylvania, New York, Vermont, and Massachusetts.

Of course, the LaBrants aren’t alone. The popular influencer account Heavenly Homeschool has similar reels out, walking parents through the process of generating entire years’ worth of lesson plans, tailor-made to their specific worldview. It all begs the question: do AI chatbots have any safeguards around education?

Turns out, not really. We tasked ChatGPT with developing a homeschooling curriculum for a 3rd grade student in Michigan — a state with virtually no regulations around DIY education — “following a strictly evangelical doctrine,” including “no woke history or science.”

ChatGPT was more than happy to oblige: “I can build this around a conservative, explicitly Christian/evangelical worldview, with Scripture integrated across subjects and with history and science taught from a young-earth/creationist perspective rather than through a secular or progressive framework,” the chatbot explained.

While it didn’t push back against our intentions to indoctrinate our hypothetical child, the LLM did make sure to clarify that “no woke” can “mean different things to different families.” So, to avoid ambiguity, the chatbot specified that the course calendar would use “Biblical authority, traditional Christian ethics… and creation-based science” as standard-bearers.

True to its word, the LLM-generated curriculum included “bible and Christian studies,” a traditionalist approach to American history, with specific chunks on both “Westward expansion” and Henry Ford — a renowned racist and antisemite — as well as a creationist approach to Earth science and astronomy.

For the portion on space, the curriculum would teach “the heavens as God’s creation while distinguishing observations from interpretations about the age and origin of the universe,” the LLM promised.

Put together, it paints a dire picture for the estimated 3.75 million K-12 homeschooled children in the US. Beyond the potential for wild AI hallucinations to leach into educational material, the technology is a Pandora’s Box for parents, who can now effortlessly inculcate their children with any number of unscientific conspiracy theories or anti-social worldviews while facing no pushback whatsoever.

Do you know anything about how homeschooling families are using AI? Email us: tips@futurism.com. We can keep you anonymous.

More on education: Mark Zuckerberg’s Wife Shuts Down School for the Disadvantaged

The post Homeschool Parents Are Planning Lessons With ChatGPT appeared first on Futurism.
  •  

Anthropic makes Claude Code’s auto mode default for paid users

Anthropic is making Claude Code’s auto mode the default for its paid and enterprise users, allowing the coding agent to execute more actions without requiring developers to approve each one.

“Starting August 14, 2026, auto mode becomes the default permission mode for new sessions on Pro, Max, and Team plans,” the company wrote in the coding agent’s documentation, adding that the same change is planned for Claude Enterprise, API, and cloud platform users within the next month.

That essentially means developers using those plans will no longer have to manually approve every tool call or action Claude Code wants to make while executing a task.

Instead, each tool call is evaluated by an automated classifier designed to determine whether the action is safe to execute. Actions considered irreversible, destructive, or outside the agent’s environment can still be blocked, with Claude Code either attempting a safer approach or asking the developer for approval, the company wrote in a blog post.

“If it can’t make progress — three blocks in a row, or twenty across a session — Claude Code falls back to manual approvals,” it explained.

This reduction in manual intervention, Anthropic further added, is intended to make the coding agent more suitable for long-running tasks as well as cut down on “permission fatigue” that it says has been threatening to reduce its security posture.

According to its internal data, Claude Code users typically approve 97% of permission prompts, while only 3% are rejected. It also found that 49.5% of active CLI users had created a Bash allow-rule by June, while 62% had used “bypassPermissions” or selected “don’t ask again” for Bash.

In contrast, the default auto mode, in an Anthropic-controlled study involving 1,053 paid professional testers, caught 89% of deliberate dangerous commands compared to just 13.6% being detected by human reviewers.

More productivity but with tradeoffs

Analysts too see auto mode as a step toward making coding agents more autonomous, but with tradeoffs.

“Developers should see fewer permission pop-ups and spend less time watching Claude, meaning they can give it larger tasks and let it edit files, run tests, and execute routine commands with fewer interruptions. That way, developers can finish and ship more work using this mode because they aren’t constantly interrupted by approval windows,” said Pareekh Jain, principal analyst at Pareekh Consulting.

However, that same classifier in auto mode that reduces permission pop-ups could also result in more latency for routine or quick tasks, as trusted workflows also pass through it, adding an extra execution step, noted Manoj Chandra Jha, principal analyst at Nord-IQ Research.

Another tradeoff of reducing real-time approvals, according to Amit Kumar Jena, AI development manager at IT consulting firm Kanerika, is that it could make it harder for enterprises to maintain effective human oversight as agents take on longer-running tasks. “Reviewing four hours of unattended agent output is a harder skill, and most teams haven’t built it,” Jena said.

Better governance for CIOs

For CIOs, though, auto mode can strengthen governance in software development.

Rather than policing individual developer actions, CIOs can define permission boundaries centrally and have the classifier enforce them across agent sessions, said Jha.

That makes the current opt-in period for Enterprise and API users particularly important, as CIOs can establish permission policies before auto mode becomes the default, Jha added.

At the same time, however, CIOs also need to understand the limits of those policies, Jena pointed out.

“Auto mode has three levels of restrictions, with hard-deny rules blocking actions unconditionally, while soft-deny rules can be overridden by a developer’s allow rule. As a result, CIOs should use hard-deny or managed-settings rules for actions that must never be permitted,” he said.

Auto mode changes the security risk profile

Those centralized policy controls, which Anthropic claims should make Claude Code more secure, according to analysts, change the security risk profile of the coding agent rather than eliminate risk.

While the classifier and the policy controls reduce the risk of human failures or everyday risks, it also creates a single point of failure, Jain said.

That means if that single point has a blind spot or an attack manages to bypass it, the agent could still execute harmful actions without human approval or recognition, Jha echoed.

That said, Anthropic is not removing developers’ ability to control how Claude Code operates.

Users who have already set a different default may receive a one-time prompt asking whether they want to move to auto mode, while those who have pinned their existing preference will see no change. The company is also making the transition easier by absorbing the small amount of additional token usage generated by the classifier for Pro, Max, and Team users, with the change effective immediately.

  •  

Nvidia teams up with financial giants to create $500 billion AI infrastructure funds — six investment firms to enable access to long-term funding at attractive rates

Nvidia late on Monday announced that it had signed memorandums of understanding with Apollo, BlackRock, Blackstone, Brookfield, Goldman Sachs, and KKR to establish independent financing platforms that could mobilize more than $500 billion in third-party capital to invest in AI infrastructure. Nvidia's goal is to ensure that its clients building AI data centers (which Nvidia calls AI factories) can get enough money from powerful financial companies. As a result, Nvidia will reinforce its position on the AI hardware market as the funds will exclusively finance Nvidia-based AI data centers.

The proposed funds (or platforms, as Nvidia calls them) are intended to provide dedicated pools of capital for customers — such as AI labs, cloud service providers, or enterprises — that deploy Nvidia-based infrastructure. Rather than financing projects itself, Nvidia intends to work with six investment firms to enable access to long-term funding at attractive rates. The company believes that AI infrastructure should not be viewed as conventional IT equipment, but as tools that make sustained economic returns, which is why it must be financed appropriately.

"We are in a pivotal moment of a historic AI investment cycle," said David Solomon, Chairman and CEO of Goldman Sachs. "Nvidia's full-stack platform is in high demand and uniquely positioned at the center of that global buildout. Our investment and distribution roles reflect our confidence in Nvidia's leadership, and we are excited for the new opportunity to create a market for credit backed by NVIDIA compute."

The financial companies believe that AI data centers can be treated as long-duration infrastructure assets rather than conventional IT equipment, in part because Nvidia compute can generate revenue over an extended period and retain value across different workloads and operators. As a result, they appear to believe that AI infrastructure can support long-term financing at attractive rates, although the companies do not explicitly claim that financing AI data centers carries lower credit risk than financing conventional IT deployments. Furthermore, it should be noted that Nvidia and financial companies will inevitably finance companies that would otherwise struggle to obtain capital to finance their AI data centers. This will ultimately help Nvidia sell more hardware and software while allowing its financial partners to capitalize on the rapid expansion of Nvidia's AI ecosystem.

Without any doubt, the arrangement will help to rapidly build AI infrastructure, which will increase adoption of AI technologies. However, this arrangement increases the risk of an AI infrastructure bubble as it potentially weakens one of the natural brakes on overbuilding: the availability and price of capital. Furthermore, Nvidia's help with arranging financing for its own customers introduces an element of circular financing into the AI boom, something that the industry faced during the dot-com bubble era in the late 1990s – early 2000s. However, this does not necessarily prove there is a bubble, as there is genuine, enormous demand for AI hardware and Nvidia sells plenty of such hardware.

Perhaps the biggest concern about the arrangement is that while Nvidia and its partners state that AI infrastructure can provide long-term value, AI accelerators, such as Nvidia's GPUs, have short and uncertain economic lives as the company and its industry peers introduce new and better-performing AI hardware every year, which devalues the previous generation.

"Nvidia has reached an important milestone: we began by building chips; today, we are helping create a new class of productive, investable infrastructure: AI factories," said Jensen Huang, founder and CEO of Nvidia. "In AI, compute is revenue. Nvidia compute is uniquely suited for this role. It is broadly adopted, flexible across models and workloads, fungible and transferable across customers and operators, and continuously improved through CUDA software — extending its useful life and improving its economics over time. It is supported by a deep global ecosystem of developers, customers, and offtakers. That is why we are bringing the world's leading long-term capital providers together to independently underwrite AI infrastructure. These financing platforms will help customers access scarce compute at scale and build the DSX AI factories that will power every industry and country in the age of AI."

  •  

His Start-Up’s Goal: A.I. That Is Trainable and Not Controlled by a Big Company

A co-founder of xAI is going all in on building open-source artificial intelligence so that “anyone can control and shape A.I. for their own needs.”
  •  

AI finds so many Windows flaws, Microsoft can’t keep up. Should you worry?

Be careful what you wish for. That’s what Microsoft found out recently when it discovered that AI — rather than making Windows more secure by helping the company close security holes — could help hackers find flaws faster than Microsoft can fix them.

It’s put Microsoft in a serious bind. Should the company devote a potentially massive amount of resources to fix every AI-unearthed security issue as fast as it can? Or should it rush to close the most important ones, and clean up the minor ones later at much less cost?

What the company decides could have tremendous implications. For years, Microsoft has faced criticism from many in the US government because of how often its technologies have been hacked, potentially putting the nation’s security at risk. Some members of Congress have suggested the government curtail contracts with Microsoft until the company proves it can provide more safety. Billions of dollars in federal contracts could be pulled.

To get a better insight into what could happen, let’s look at AI’s newfound prodigious ability to find security holes and bugs.

AI-fueled security mavens Mythos and Project Glasswing

Microsoft’s AI-related security problems are an outgrowth of the launch of Anthropic’s Mythos AI model, designed to handle cybersecurity and biology research. One of its goals is to uncover security vulnerabilities as quickly as possible, so that software companies and cybersecurity companies can fix them before hackers find the holes.

Anthropic’s early tests found that Mythos was spectacularly successful in finding Windows security flaws. “Within 31 minutes, Mythos generated its first proof-of-concept exploit for a Windows kernel vulnerability,” Axios reported in June.

Anthropic noted that its testing of Mythos “reveals a stark fact: AI models have reached a level of coding capability where they can surpass all but the most skilled humans at finding and exploiting software vulnerabilities.

“Mythos Preview has already found thousands of high-severity vulnerabilities, including some in every major operating system and web browser. Given the rate of AI progress, it will not be long before such capabilities proliferate, potentially beyond actors who are committed to deploying them safely. The fallout — for economies, public safety, and national security — could be severe.”

As a result, Anthropic decided to launch a security project it calls Project Glasswing, which it describes as “an urgent attempt to put these capabilities to work for defensive purposes.”

Many companies beyond Anthropic are part of the effort, including Microsoft, Google, Amazon, Nvidia, Apple and others. In theory, it’s a great idea. Find and fix vulnerabilities before hackers can, and everyone is safer. What could go wrong? 

Plenty, as it turns out. Access to Mythos is available to anyone, and Mythos has been finding security holes and bugs far faster than companies — particularly Microsoft — can patch them. As Pro Publica reported in late July, ‘Microsoft is struggling to fix them fast enough.” 

Too little, too late?

For now, Microsoft is only patching the most dangerous bugs and holes. And, according to Pro Public, “internal records indicate that Microsoft plans to eventually address ‘moderate’-severity flaws uncovered by Mythos. The documents made no mention of ‘low’-severity bugs.”

That’s fairly typical of the triage many companies use when deciding how much effort to put into plugging holes. But some experts believe that in the Age of AI, that’s a dangerous way to handle security. 

Vinh Nguyen, former chief AI officer and chief data scientist at the US National Security Agency and now a senior technical adviser to Anthropic and senior fellow for AI at the Council on Foreign Relations, is particularly concerned that the approach is outdated. He told Pro Publica: “The problem now is that you can chain four low-level flaws, and that can equal a high severity. If you’re Microsoft, the current triage strategy may be underpricing risks.” 

It’s already proving difficult for Microsoft to keep up with patching bugs and security holes since Mythos’ launch. July’s Patch Tuesday release fixed the most bugs in Microsoft’s history – 622 of them. Things will only get harder from here. 

The dangers for Microsoft

Microsoft is already in the doghouse for how it’s handled security. A year ago, in one of the worst attacks on Microsoft technologies, Sharepoint was hacked. Tens of thousands of servers were hit, including not just thousands of businesses, but many important government agencies as well.    

The National Institutes of Health (NIH) and the National Nuclear Security Administration (NNSA), which is in charge of the nation’s nuclear security, were among the victims. So were the Department of Homeland Security (DHS), the Cybersecurity and Infrastructure Security Agency, the Transportation Security Administration, Customs and Border Protection, and the Federal Emergency Management Agency, among many others. 

Even before then, some members in Congress were threatening to pull Microsoft contracts if it didn’t improve security. At one point Sens. Eric Schmitt (R-MO) and Ron Wyden (D-OR) sent a threatening letter to the Pentagon requesting it not increase its use of Microsoft products.

“We write with serious concern that the Department of Defense (DoD) is doubling down on a failed strategy of increasing its dependence on Microsoft at a time when Congress and the administration are reviewing concerning cybersecurity lapses that led to a massive hack of senior US officials’ communications,” the letter said, in part.

Nothing happened as a result of the hack or the letter. But that could change in a heartbeat if there’s another big attach. It seems inevitable that hackers will start taking advantage of how quickly Mythos discovers security holes and bugs, especially if Microsoft doesn’t fix them all. 

The next big hack, powered by AI, could prove very dangerous — not just for businesses and governments, but for Microsoft as well.

  •  
❌