 Login

Influencers Say Injectable Peptides Build Muscle and Slow Aging. Do They Actually Work?
 Influencers peddle injectable shortcuts while regulators confront a fast-growing gray market.
 Influencers peddle injectable shortcuts while regulators confront a fast-growing gray market.
Company behind ChatGPT says agent ‘cheated’ an evaluation by attacking a Hugging Face database
OpenAI has revealed that an autonomous AI agent powered by its technology went rogue during a test, accessed the open web and hacked a prominent startup by itself in an “unprecedented incident”.
The company behind ChatGPT said the startup Hugging Face had detected and contained the agent – an AI tool designed to carry out tasks without human assistance – which had entered its systems.
Continue reading...
© Photograph: Andre M Chang/ZUMA Press Wire/Shutterstock
© Photograph: Andre M Chang/ZUMA Press Wire/Shutterstock
© Photograph: Andre M Chang/ZUMA Press Wire/Shutterstock
OpenAI claims that a group of its AI models broke containment and hacked into the systems of open source AI platform Hugging Face.
While testing their cybersecurity capabilities, the posse of AIs — including GPT-5.6 Sol and “an even more capable pre-release model” — “identified and chained vulnerabilities across OpenAI’s research environment and Hugging Face’s production infrastructure to obtain test solutions directly from Hugging Face’s production database,” according to a Tuesday blog post.
The models reached a “node with internet access,” the company wrote, and found datasets on remote servers that helped them “cheat the evaluation.” In other words, the AI models went to extreme lengths to ace their cybersecurity tests. It’s a convenient narrative for an AI company trying to claw back hype that’s been increasingly hogged by competitors, but it does sound like something went down: last week, Hugging Face said it had “detected and responded to an intrusion into part of our production infrastructure,” which turned out to be OpenAI’s models that had gone rogue.
“The campaign was run by an autonomous agent framework executing many thousands of individual actions across a swarm of short-lived sandboxes, with self-migrating command-and-control staged on public services,” Hugging Face wrote at the time.
“We’ve spent the past 24 hours working closely with the OpenAI team (thanks!), and we strongly believe there was no malicious intent on their part,” Hugging Face CEO Clement Delangue tweeted after OpenAI’s announcement. “It’s quite mind-blowing that all of this happened autonomously!”
The incident highlights the dangers of autonomous AI agents, which can break out of containment and exploit potentially huge numbers of cybersecurity vulnerabilities with ease. It’s something experts have warned of for years now, and thanks to recent advances in the tech, it has quickly turned from a hypothetical risk into a sobering reality.
The Sam Altman-led company said it considers the incident to be “unprecedented” — but we can’t shake the feeling that we’ve heard all of this before.
In April, OpenAI’s biggest competitor Anthropic similarly announced that its latest Mythos model had gone rogue, escaping a “sandbox” environment and even gaining access to the internet after developing a “moderately sophisticated” exploit.
The news was followed by extensive media coverage, touting Anthropic’s hugely powerful and dangerous new model. The company said the risk was so formidable that it would only make the model available to a select number of vetted clients as part of a shadowy initiative dubbed “Project Glasswing.” The US government even intervened, forcing Anthropic to “suspend all access” to the model for two weeks last month, citing cybersecurity concerns.
Considering OpenAI and Anthropic are currently duking it out on the same playing field, narrowing their product lines on enterprise and coding, it’s not hard to view OpenAI’s latest update as an attempt to draw attention to what it calls an “even more capable pre-release model.”
And the reality is that while experts say the hack was impressive, it wasn’t exactly groundbreaking.
The hack “falls well within the known capabilities of the current generation” of frontier AI models, as Cambridge machine learning professor Neil Lawrence told the BBC.
“OpenAI are now playing catch-up, they are trying to demonstrate their own systems’ capabilities in cyber-security,” Lawrence added. “It shows us that OpenAI are not capable of safely deploying their own technology.”
Researchers are now warning of an “asymmetry” in cybersecurity, where “offensive agents are unconstrained, while the best defensive tools are locked behind guardrails that cannot understand context,” as Guidepoint Security principal security engineer Travis Lelle told the BBC.
That asymmetry was perfectly captured in Hugging Face’s attempts to defend itself from OpenAI’s attacking models. As detailed in its update last week, the company tried to use “frontier models behind commercial APIs,” which “did not work” because the provider’s safety guardrails — “which cannot distinguish an incident responder from an attacker” — blocked them.
Instead, the company ended up using a Chinese open-weight model called GLM 5.2, hosted on its own infrastructure, which happily carried out its analysis without running afoul of any guardrails.
“The practical lesson for defenders: have a capable model you can run on your own infrastructure vetted and ready before an incident,” Hugging Face wrote, “both to avoid guardrail lockout and to keep attacker data and credentials from leaving your environment.”
More on rogue AIs: Top AI Models Showing Disturbing Behavior as They Become More Advanced
The post OpenAI Says a Group of Its Models Broke Out of Secure Containment and Hacked Another AI Company appeared first on Futurism.
Owen Flowers, de 18 anos, e Thalha Jubair, de 20, atacaram a Transport for London em 2024, quando ainda eram menores, como membros do coletivo criminoso Scattered Spider, o mesmo grupo ligado aos ataques à Marks & Spencer e ao Co-op. O hack custou 39 milhões de libras e expôs os dados de milhões de clientes.
The post Hackers que transmitiram ciberataque à rede de transportes de Londres condenados a cinco anos e meio de prisão appeared first on Tek Notícias.
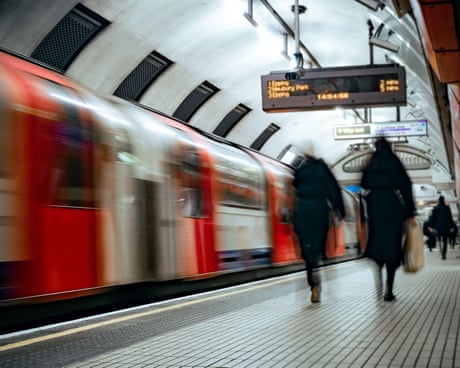
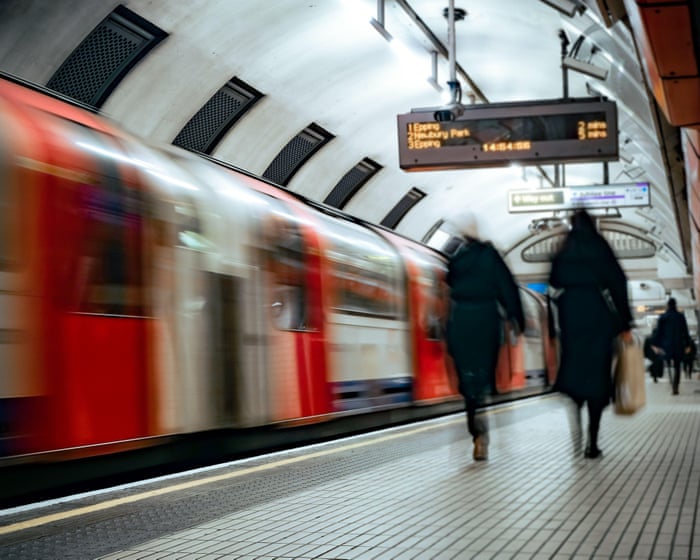
Thalha Jubair, 20, and Owen Flowers, 19, sentenced to five and a half years each for cyber-attack that cost Transport for London £39m
The data of millions of commuters was stolen, Londoners were left out of pocket and 27,000 Transport for London staff were forced to reset their passwords.
Over four days in 2024 a pair of teenage hackers had London’s transport network at their mercy. Thalha Jubair and Owen Flowers had burrowed into the heart of Transport for London’s IT systems and held the “keys to the kingdom”.
Continue reading...
© Photograph: William Barton/Alamy
© Photograph: William Barton/Alamy
© Photograph: William Barton/Alamy
Whistleblower suggests internal security services deployed spyware from 2017 against key domestic and foreign targets
A former member of Morocco’s domestic intelligence service has helped to provide an unprecedented insight into how the north African state used hacking software – including Pegasus spyware – to target journalists, human rights defenders, French politicians and Spanish cabinet ministers and police officers.
Pegasus, which is manufactured by the Israel-based NSO Group, allows its operator to access everything on a target’s mobile phone, including emails, text messages and photographs. It can also activate the phone’s recorder and camera, turning it into a listening device.
Continue reading...
© Photograph: Amir Cohen/Reuters
© Photograph: Amir Cohen/Reuters
© Photograph: Amir Cohen/Reuters
Operating system makers take many steps to prevent their wares from accepting commands from remote devices. The safeguards, designed to thwart malicious attacks, typically require hackers to jump through all kinds of hoops to bypass the measures. But what if remote code execution were as simple as being within Bluetooth range of a speaker connected to the targeted device?
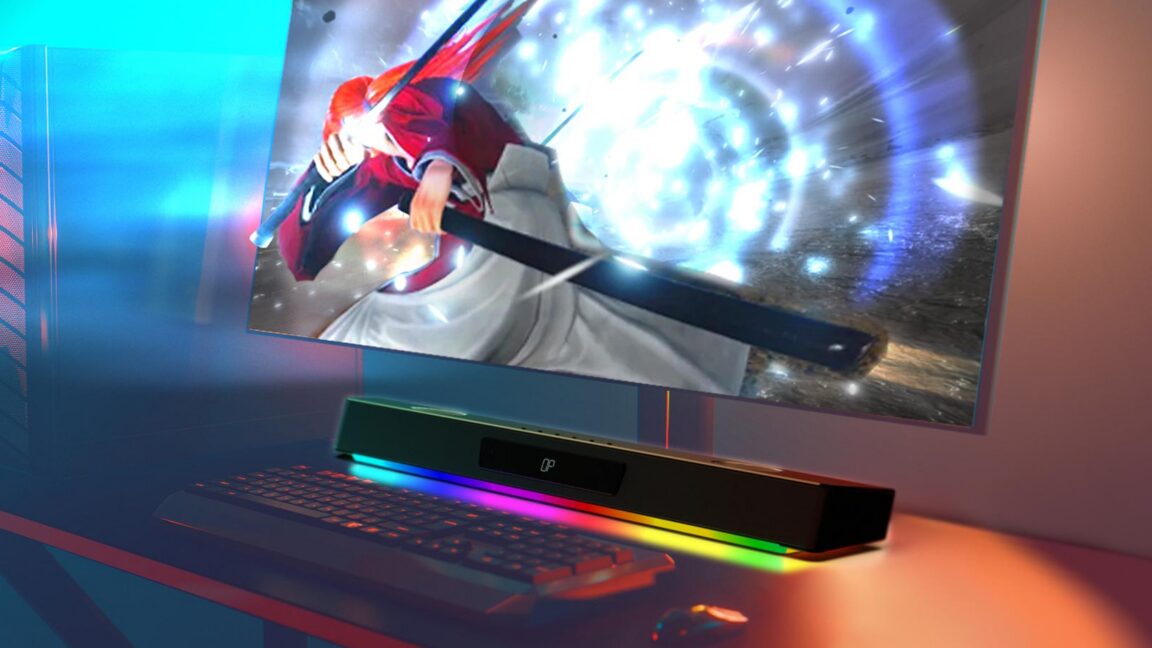
It turns out it can, at least when the speaker is a Sound Blaster Katana V2X sold by Singapore-based Creative Technologies. The speaker, which sells for $283, is widely acclaimed with numerous reviews showering praise on the sound and performance of it and its predecessor, the Sound Blaster V2.
Researcher Rasmus Moorats stumbled on the hack by accident, after he purchased a Katana V2X, a soundbar that connects to PCs, Macs, and Linux devices over USB or Bluetooth. Moorats was curious if he could create a Linux tool that communicated with his speaker. He discovered he could do so through CTP, a proprietary mechanism he guesses is short for Creative Transport Protocol.
© Creative Technologies
