South Korean cybersecurity company GITSN on July 22 presented a hardware-layer security solution designed to block wireless backdoor attacks as artificial intelligence (AI)-powered autonomous vulnerability discovery enters a new phase.
The announcement follows Anthropic's introduction of Claude Mythos Preview, a next-generation AI model that has demonstrated agentic coding and reasoning capabilities capable of autonomously identifying software security vulnerabilities and generating functional exploit code, raising concerns over a new class of endpoint security threats.
In response, South Korea's Ministry of Science and ICT (MSIT) has joined Project Glasswing, a global AI security initiative. Domestic cybersecurity companies, including AhnLab, are also strengthening defense strategies centered on exposure management to improve the speed of threat detection, analysis and response.
At the same time, wireless backdoor attacks—where malicious hardware is covertly embedded during device manufacturing or within the supply chain to bypass conventional network defenses—are expected to become a growing threat. Against this backdrop, GITSN presented Alpha-H as a solution for continuously detecting wireless backdoor attacks.
According to GITSN, Alpha-H monitors the entire radio frequency environment within a protected area in real time, 24 hours a day, 365 days a year. The system is designed to eliminate vulnerabilities in the physical radio frequency domain, where data is ultimately transmitted, preventing data exfiltration at its source.
A South Korean court has postponed until Sept. 2 its ruling in Nexon Korea Corp.'s lawsuit seeking to overturn a 11.642 billion won penalty imposed by the Korea Fair Trade Commission (KFTC) over alleged manipulation of probability-based items in MapleStory. The delay comes after Nexon submitted additional legal briefs shortly before the scheduled ruling, giving the court more time to review arguments from both sides.
According to the legal community on July 22, the Administrative Division 6-3 of the Seoul High Court changed the ruling date for Nexon's lawsuit seeking to cancel the KFTC's corrective order and administrative fine from 2 p.m. that day to Sept. 2.
The postponement is believed to reflect Nexon's decision to continue submitting legal briefs through July 15, just one week before the scheduled ruling. The court is expected to conduct additional review given the potential impact of legal standards governing probability-based game items on the broader gaming industry.
The lawsuit is not centered on whether there was a legal obligation at the time to disclose probability information. Instead, it focuses on whether Nexon failed over an extended period to disclose information that could materially influence consumers' purchasing decisions.
The case stems from Cube, a paid in-game item introduced in 2010. The KFTC concluded that beginning in 2011 Nexon altered the probabilities so that certain highly sought-after potential options, including combinations known by players as "BoboBo" and "DeuDeuDeu," would no longer appear. The regulator also found that in 2013 Nexon reduced the rank-up probability of Black Cube without informing users. The KFTC determined that the conduct constituted deceptive commercial practices under the Act on Consumer Protection in Electronic Commerce, etc., imposing an administrative fine of 11.642 billion won.
Nexon, however, argues that no legal obligation to disclose probability information existed at the time of the conduct and that applying later disclosure standards to past actions amounts to retroactive regulation. The company also contends that the statute of limitations for administrative sanctions has already expired.
The KFTC maintains that, regardless of whether there was an explicit obligation to disclose probabilities, withholding information that could materially affect consumers' purchasing decisions constituted deceptive conduct under the Electronic Commerce Act in force at the time.
The ruling is drawing attention because it could shape not only the scope of legal liability for past operation of probability-based game items but also future interpretation of regulations governing such monetization systems across South Korea's gaming industry.
Separately, the postponement is also expected to delay a truck protest planned by users of MapleStory Idle ("Meki"), which had been scheduled for July 22, to Sept. 2. Players have been preparing demonstrations against Nexon, alleging that the "HP Increase" and "Damage Taken Reduction" effects did not function properly for an extended period and raising concerns over the company's compensation plan. In response, the MapleStory Idle operations team plans to hold a meeting with users in August.
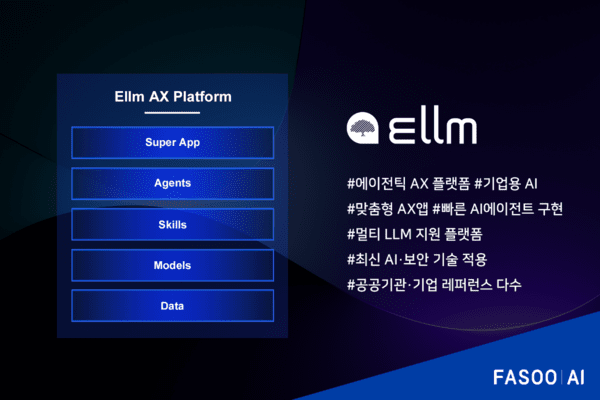
Fasoo AI's agentic AI transformation platform, Ellm. (Image: Fasoo AI)
Fasoo AI's agentic AI transformation platform, Ellm. (Image: Fasoo AI)
Fasoo AI is expanding its artificial intelligence business into the K-beauty sector by developing an AI-powered beauty platform for RIAHN Hair, a company selected for South Korea's 2026 AI Transformation (AX) One-Stop Voucher Program.
The government-backed AX voucher program, valued at 26 billion won, is designed to accelerate corporate AI transformation by providing integrated support for artificial intelligence, cloud computing and data services through a voucher system.
Fasoo AI was selected as a supplier in the AI development category, which focuses on foundation model-based AI technologies. Companies participating in the program can also select providers for cloud infrastructure, including GPUs and software-as-a-service (SaaS), as well as data acquisition and processing. Final project operators are selected through an evaluation process.
RIAHN Hair, the lead company for the project, operates several beauty franchise brands in South Korea, including RIAHN Hair, H Hairstyle, and RIAHN Wig.
Through the initiative, RIAHN Hair aims to develop an AI-powered hyper-personalized beauty experience platform to strengthen its position in the global beauty technology market.
Under the project, Fasoo AI will develop the platform's AI capabilities using its Ellm agentic AI transformation platform. Naver Cloud will provide cloud infrastructure, while LabQ will be responsible for data-related services.
The AI beauty platform will feature virtual simulations based on users' facial characteristics and personal preferences, while also providing personalized recommendations for hairstyles and designers.
Wemade Max announced on July 21 that it has launched Wind Runner Idle, a new idle role-playing game (RPG) developed by its subsidiary LightCON, in South Korea and Taiwan.
The game reimagines the Wind Runner intellectual property (IP) as an idle RPG while incorporating the franchise's signature fast-paced gameplay into its combat system.
Wind Runner Idle features a proprietary combat mechanic built around Combo, Fever, and Fever Burst, combining the convenience of idle gameplay with more dynamic combat and responsive action.
Players can freely customize their teams using more than 150 characters, companions and mounts. The game also offers a variety of content, including the real-time player-versus-player (PvP) Arena mode and Companion Land, a casual decorating feature.
To celebrate the official launch, Wemade Max is holding a series of in-game events.
Players who completed pre-registration will receive the legendary character Stella and the legendary mount Sky Ruler Griffin. In addition, users can earn various in-game rewards, including rubies and summon tickets, through the 3,000 Summons Growth Support event and the Stage Clear event.
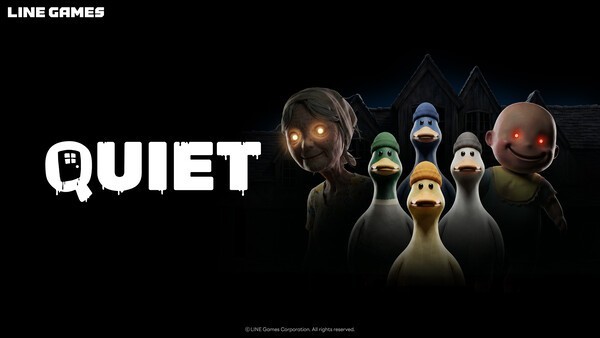
Line Games announced on July 21 that it has begun recruiting participants for the upcoming playtest of its new PC title, QUIET.
QUIET is a cooperative comedy horror game currently being developed in-house by Line Games. Players take on the role of a duck-like alien that crash-lands on Earth and must escape while avoiding the watchful eye of the game's boss character, Grandma. The game supports both single-player and cooperative play for up to four players.
Line Games is aiming to launch QUIET globally later this year. Ahead of the official release, the company will begin a public playtest on Aug. 3. Players can register for the test through the game's Steam playtest page.
The upcoming playtest will feature the game's first stage along with its co-op mode. Line Games said it will use player feedback gathered during the test to further refine and improve the game's overall quality.
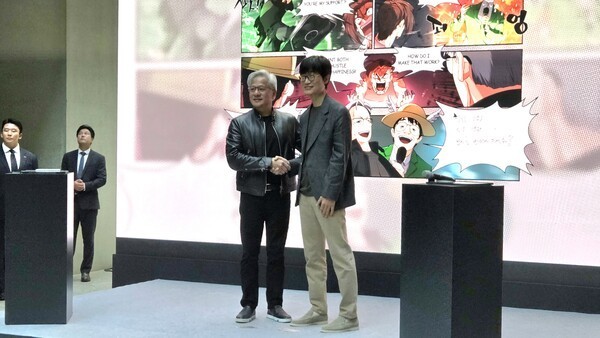
During his visit to Naver in June 2026, NVIDIA Chief Executive Officer Jensen Huang met with Naver Chairman Lee Hae-jin to discuss future areas of collaboration. (From left) Jensen Huang, Chief Executive Officer of NVIDIA, and Lee Hae-jin, Chairman of Naver. (Photo: THE ELEC)
During his visit to Naver in June 2026, NVIDIA Chief Executive Officer Jensen Huang met with Naver Chairman Lee Hae-jin to discuss future areas of collaboration. (From left) Jensen Huang, Chief Executive Officer of NVIDIA, and Lee Hae-jin, Chairman of Naver. (Photo: THE ELEC)
Naver's top management is set to visit Canadian alternative asset manager Brookfield Asset Management this week, fueling speculation that the companies could explore cooperation on AI infrastructure. With Brookfield already partnering with NVIDIA on a global AI infrastructure investment initiative, discussions are expected to focus on securing data centers, power capacity and investment funding for Naver's AI factory strategy.
According to industry sources on July 20, Naver Chairman Lee Hae-jin and Chief Executive Officer Choi Soo-yeon will visit Brookfield's headquarters in Toronto early this week. Chief Financial Officer Kim Hee-cheol and senior executives from affiliated companies are also expected to join the trip.
Brookfield manages approximately $1 trillion in assets. In November 2025, the company launched a global AI infrastructure investment program worth up to $100 billion in partnership with NVIDIA and the Kuwait Investment Authority. The initiative invests across the AI infrastructure ecosystem, including data center sites, power infrastructure and graphics processing units (GPUs).
In June 2026, during NVIDIA Chief Executive Officer Jensen Huang's visit to South Korea, Naver announced plans to work with NVIDIA to build gigawatt-scale AI factories. The company aims to begin operating a 55-megawatt (MW) AI factory in the first half of next year, expand capacity to 100 MW later that year and 200 MW by 2028, with a long-term goal of developing 1 gigawatt (GW) of AI infrastructure.
AI factories are next-generation computing facilities designed to train AI models and deliver AI services using massive datasets. As competition in AI increasingly extends beyond software to data center and power capacity, industry attention is focused on whether Naver's visit to Brookfield will lead to broader cooperation on securing the infrastructure needed to support its AI ambitions.
Industry observers believe Naver and Brookfield could discuss data center development, infrastructure investment and financing arrangements required for the AI factory project. The inclusion of CFO Kim in the delegation has also led to speculation that discussions may extend beyond strategic cooperation to more concrete investment negotiations.
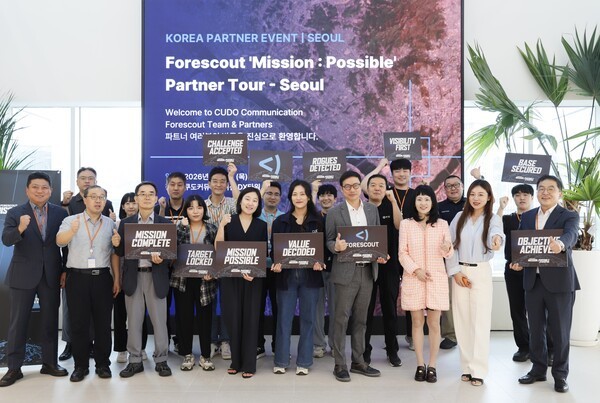
Participants at the "Forescout Mission: Possible" Partner Tour Seoul event. (Photo: Kudo Communications)
Participants at the "Forescout Mission: Possible" Partner Tour Seoul event. (Photo: Kudo Communications)
Kudo Communications announced on July 20 that it hosted the "Forescout Mission: Possible" Partner Tour Seoul event at its headquarters in Gwacheon, Gyeonggi Province, on July 9.
The event is part of Forescout's global roadshow for partners across the Europe, Middle East and Africa (EMEA) and Asia-Pacific (APAC) regions. As Forescout's exclusive distributor in South Korea, Kudo Communications invited the company's domestic channel partners to participate in the event.
The program consisted of five mission-based sessions covering topics including platform capabilities, critical asset identification and asset prioritization.
During the event, Forescout presented its unified platform strategy, which spans asset discovery across information technology (IT), operational technology (OT) and Internet of Things (IoT) environments, as well as policy enforcement and regulatory compliance. The company also introduced its long-term cybersecurity strategy for the quantum computing era, including measures designed to address "harvest now, decrypt later" attacks.
Forescout additionally outlined its vision for enhancing the platform with artificial intelligence (AI), enabling enterprise security teams to manage cyber risks more proactively.
A South Korean court will issue its ruling on July 22 in Nexon's appeal seeking to overturn a 11.642 billion won administrative fine imposed over its failure to disclose probability changes for MapleStory's "Cube" items. The decision is expected to serve as a key precedent on whether game companies can be sanctioned for conduct that occurred before mandatory disclosure rules for probability-based items took effect.
According to industry sources on July 20, the Administrative Division 6-3 of the Seoul High Court will deliver its judgment on Nexon's lawsuit challenging the penalty imposed by the Korea Fair Trade Commission (KFTC).
The central issue is not whether Nexon manipulated item probabilities. Instead, the KFTC argues that the company failed for years to disclose information that could materially affect consumers' purchasing decisions. Nexon, meanwhile, contends that the regulator is retroactively applying standards that did not exist at the time because no legal obligation to disclose probability information was in place.
During the final hearing at the Seoul High Court in April 2026, Nexon argued that most of the probability changes at issue occurred during the 2010s, while the legal requirement to disclose probability-based item information was introduced only through amendments to the Game Industry Promotion Act that took effect in 2024. The company said applying the current standard to earlier conduct is unlawful.
Nexon also argued that its failure to disclose the probability changes amounted to a mere omission rather than an affirmative false representation. It further claimed that Cube sales increased even after probability information was disclosed, making it difficult to establish a causal relationship between the alleged deception and consumer purchases.
The company additionally maintained that the probability adjustments cited by the KFTC had ended before 2016, meaning the regulator's 2024 sanctions fell outside the applicable statute of limitations.
The obligation to disclose the probabilities of random-item products was codified through Article 33(2) of the Game Industry Promotion Act on March 21, 2023, and took effect on March 22, 2024.
The KFTC has argued that the case should be judged under Article 21 of the Act on Consumer Protection in Electronic Commerce, rather than the Game Industry Promotion Act. According to the regulator, it did not retroactively apply the probability disclosure requirement but instead sanctioned Nexon for concealing or omitting material information that influenced consumers' purchasing decisions and induced transactions.
According to the KFTC's written decision, Nexon modified the Cube potential-option system in 2010 and carried out 449 updates before publicly disclosing probabilities in 2021 without informing users of the changes. The regulator concluded that the conduct constituted deceptive practices that interfered with consumers' ability to make informed purchasing decisions.
One of the KFTC's representative examples is the so-called "Bo-Bo-Bo" case. The regulator found that Nexon altered the system in a 2011 update so that three highly desirable potential options could no longer appear together. However, the company simultaneously announced that "there are no changes to existing potential abilities, which remain the same," and that "there are no functional changes to existing Miracle Cubes," thereby concealing the probability changes.
Those options were among the most valuable potential attributes obtainable through Cube items and were highly sought after because of their impact on gameplay. The KFTC concluded that whether combinations such as "Bo-Bo-Bo" remained obtainable was material information likely to influence purchasing decisions. It therefore viewed Nexon's notices not as simple non-disclosure but as affirmative statements that led consumers to believe the probability structure remained unchanged.
The ruling is also expected to have implications for the broader gaming industry. A similar case involved Webzen's mobile game MU Archangel. In November 2025, the KFTC imposed a 158 million won fine after finding that Webzen had failed to disclose a so-called "floor system" under which players had a zero percent chance of obtaining certain rare items until they reached a minimum number of draws while selling three probability-based items between June 2020 and March 2024. Depending on the item, users had to make between 51 and 150 purchases before becoming eligible to receive the rare rewards. Despite that prerequisite, Webzen advertised acquisition probabilities of between 0.25% and 1.16%. Although the conduct predated the statutory probability disclosure requirement, the KFTC concluded that concealing material acquisition conditions distorted consumers' purchasing decisions and constituted deceptive conduct under the Electronic Commerce Act. Webzen did not challenge the regulator's decision.
The Nexon case concerns an appeal against an administrative sanction rather than criminal liability. At issue is whether the Electronic Commerce Act can be used to penalize companies for concealing information that materially affected purchasing decisions before mandatory probability disclosures became law.
If the court upholds the KFTC's decision, it could establish a clearer legal standard for determining whether past probability-based item practices constituted consumer deception. A ruling in Nexon's favor, by contrast, could limit the KFTC's ability to interpret pre-disclosure omissions as deceptive conduct under the Electronic Commerce Act.
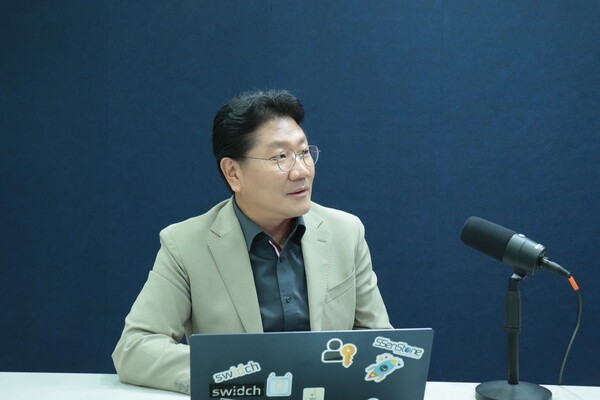
Chang-hun Yoo, chief executive officer of SSenStone. (Photo: THE ELEC)
Chang-hun Yoo, chief executive officer of SSenStone. (Photo: THE ELEC)
"SSenStone's technology is not an incremental refinement of solutions that existed in other countries. We aim to become the first company from South Korea to establish a foundational security technology used across the global market."
These are the words of Chang-hun Yoo, chief executive officer of SSenStone. SSenStone is targeting the operational technology (OT) security market with its proprietary One-Time Authentication Code (OTAC) technology, a world-first solution developed in-house.
Founded in 2015 as an authentication security startup, SSenStone spent its first three years offering a "two-way dynamic token" service that generated and received tokens back and forth between clients and servers. The company subsequently developed OTAC to overcome the structural limitations of two-way dynamic tokens, particularly their heavy reliance on network connectivity.
Two-way dynamic tokens are already familiar to most people in everyday life—quick response (QR) codes widely used during the COVID-19 pandemic are a prime example. Users would shake their smartphone to generate a QR code, which connected to a server to request authentication. Recognizing the generated QR code within a specified time window and sending the signal back constitutes a two-way dynamic token.
In contrast, OTAC enables identification and authentication simply by transmitting a generated code based on a pre-registered unique key to a server. The code changes with every use, and identical codes are never generated under any circumstance. This unique OTAC value alone allows systems to identify users or devices without requiring static inputs like user IDs or passwords.
Q&A
Q: Hello, today we are joined by Chang-hun Yoo, CEO of SSenStone. You mentioned the company name translates to "strong stone" in Korean. Could you briefly introduce SSenStone?
A: SSenStone started in November 2015 as an authentication security startup. For the first three years, we operated using two-way dynamic tokens. After three years, we developed our foundational technology called OTAC—One-Time Authentication Code—which is a unidirectional dynamic token technology unprecedented globally. In December 2018, we established a wholly owned global headquarters in the UK called swIDch. The UK government invited us through a program that included visa sponsorship capabilities.
Q: Could you elaborate on your proprietary technology, One-Time Authentication Code?
A: People already use one-time codes today, such as One-Time Passwords (OTP). But a password alone cannot identify a user; you still need a user ID first to know who the person is before applying the password. That is why OTP can only serve as a second factor for authentication. If you send only an OTP to a system without an ID, the system has no way of knowing who you are. Many security professionals are unaware of this structural limitation. When we suggested that identification and authentication could be accomplished with a unidirectional dynamic token, the global industry initially claimed it was impossible. But after more than a year of R&D, we found the solution.
Q: Could you explain the concept of unidirectional authentication in more detail?
A: Think of this mouse on the desk as a mobile phone. We experienced dynamic tokens frequently during COVID-19 with QR check-ins. You used your phone, a QR code appeared, you scanned it at a shop, and you were authenticated. That was a dynamic token, but it was two-way. The QR code was not created entirely on your phone; when you shook your device, a request was sent to service providers like Naver or Kakao. Their servers generated a code valid for three minutes and sent it back to your phone, which displayed it as a QR code to be scanned and routed back to the server within three minutes. On a device without communication capabilities, if a code keeps changing and you send it out, the server cannot know who is sending it. Before OTAC, authentication required the server to generate and send the code, which then had to return within a set timeframe.
Our unidirectional dynamic token technology works even in client environments without communication capabilities—even inside a tiny smart card chip—generating ever-changing codes that uniquely identify the user, command, or device without overlap.
Q: It is hard to grasp how that is possible. Could you explain the mechanism again?
A: What I have in my hand is a non-communicating smart card. This actual device is currently used by Korea Water Resources Corporation (K-water) and LG Energy Solution. Employees cannot bring mobile phones into factory floors, so they use OTAC codes instead of IDs, passwords, and OTPs.
When you press a button on the card, it prompts for a PIN, providing multi-factor authentication (MFA). Even if I hand this card to you, you cannot use it without knowing my PIN. Once the PIN is verified and you press OK, an 8-character alphanumeric code appears at the bottom. These eight characters replace my ID, password, and OTP. When entered, our system algorithm recognizes who I am and verifies the OTP simultaneously. It sounds improbable, doesn't it?
Q: How exactly does that single 8-character code accomplish all of that?
A: Security experts and academics worldwide believed one-way dynamic identification and authentication was mathematically impossible. When we began R&D, even SSenStone's head of research initially declined to work on it. I ended up working on it alone at first. Fortunately, because my background was not in computer science or cryptography, I had never learned why it couldn't be done—I simply didn't know the reasons it was supposed to fail. After failing for over a year, I almost gave up, thinking, "This must be a geometric structure, but it doesn't work in our current dimensional framework." While walking along the Han River, a scene from the movie Interstellar came to mind—the moment near the end where the protagonist wakes up in a hospital on a space station and sees a baseball game outside, where a hit ball smashes a window on a house hanging upside down. I realized: the XYZ axes are not straight lines; they are curved into a circle.
We started from that circular structure. The result was "continually shifting coordinates." What is generated is a coordinate that changes constantly, yet every time it drops a point, it consistently maps to my designated position. When another person generates a code, a completely different, non-overlapping coordinate appears, yet it maps consistently to that person's location. When we announced this solution, it was not immediately recognized in South Korea. We sought validation overseas, and a faculty team at the University of Surrey's cybersecurity lab in the UK mathematically verified our technology. That verification allowed us to bring the technology back to the global market.
Q: That sounds like a significant breakthrough.
A: I agree, but it is not yet widely known globally, which is why we are actively promoting it while securing major investments.
Q: Network-level information interception is one of the most common cyber threats. Does your technology mean stolen network information becomes useless?
A: Precisely. Cryptography is about making stolen data useless to an interceptor. If you write "Chang-hun Yoo" on a sticky note and pass it along, anyone who intercepts it knows the name. Encryption obfuscates the name into code so the recipient needs a key or decryption program to reconstruct "Chang-hun Yoo." However, hackers can still infer where the data came from or deduce that it is an ID and password used for login. Even with static obfuscation, vulnerabilities remain. OTAC continuously changes the token. Even if a hacker intercepts and decrypts the data, the valid timeframe—whether 30 seconds or three minutes—has already expired, rendering the decrypted data useless.
Q: What are the primary practical advantages of unidirectional technology?
A: Indonesia was among the first to adopt this technology, embedding it into their "e-Stamp" tax collection system. If you assign sequential serial numbers to tax transactions, patterns emerge that could allow forgery. They chose our technology because it generates continuous, non-sequential codes with zero discernible patterns.
Another case involves high-volume online services. In South Korea, when millions of citizens access the National Tax Service website simultaneously for year-end tax settlements, systems experience heavy congestion. Handling such traffic with traditional two-way tokens requires massive server infrastructure because servers must hold open requests while waiting for user responses. With OTAC, the server remains passive until a client device generates and sends a unique dynamic code, allowing instant identification without consuming massive server holding capacity.
Our current core focus is operational technology (OT) security. OT environments differ significantly from IT. While IT relies on robust two-way networks, OT restricts network environments, favoring air-gapped networks and unidirectional flows to prevent unauthorized access or control.
In OT environments, endpoint devices—such as Programmable Logic Controllers (PLCs), Remote Terminal Units (RTUs), Distributed Control Systems (DCS), and Human-Machine Interfaces (HMIs)—cannot easily support multi-factor authentication. Managing passwords across thousands of PLCs is impractical, and standards requiring regular password changes are difficult to enforce. Standard FIDO biometric authentication also fails because it demands active two-way communications. In these constrained environments, our clients use OTAC to authenticate access to equipment securely.
Q: Such as access control in sensitive facilities like semiconductor fabrication plants?
A: Exactly—preventing unauthorized access to critical equipment. In geopolitical conflicts, cyberattacks increasingly target OT and industrial infrastructure rather than just IT systems because the impact is immediate and physical. In traditional OT setups, once an attacker breaches the boundary network between IT and OT, internal systems are often unprotected. With OTAC, even if an attacker crosses that boundary, they cannot execute operational commands without generating the required dynamic code.
Some ask whether focusing on air-gapped, unidirectional OT environments limits our scalability. In fact, the opposite is true—the recent issue around Claude Mythos has actually worked in our favor. AI agents can now identify and exploit vulnerabilities at unprecedented speeds. Whether an attack originates from a human or an AI, the AI cannot generate an OTAC code, blocking unauthorized execution. This capability attracted investment from Hyundai Motor Group during our recent funding round.
Looking ahead, Anthropic published a report titled "Zero Trust for AI Agents" on May 27, which recommends using hardware-bound keys to prevent software-based key theft by AI agents, as well as short-lived expiring tokens. Traditional Public Key Infrastructure (PKI) or symmetric algorithms struggle to generate short-lived tokens without continuous two-way communication or challenge-response exchanges. OTAC natively generates dynamic credentials from hardware-bound keys without needing continuous two-way networks, making it a critical future-proof architecture for the AI era.
Q: Will traditional two-way security communication methods eventually disappear?
A: No, two-way security will remain necessary. However, environments where two-way communication is restricted or impractical will become increasingly prevalent.
Q: And in those restricted environments, unidirectional authentication becomes essential?
A: Whenever short-lived tokens are needed in unidirectional environments, our technology serves as the core solution.
Q: Could you share details regarding your financial performance and client traction?
A: SSenStone recently passed its 10th anniversary since founding in November 2015. During our first four years, we operated comfortably with around 10 employees, generating over 2 billion won in revenue. After developing OTAC and securing Series A funding, we shifted focus toward refining our business model rather than aggressive short-term sales.
After revenue bottomed out, license-based tech revenues began climbing steadily last year. Key commercial deployments include Korea Water Resources Corporation (K-water) and LG Energy Solution.
Q: Could you mention other corporate clients?
A: I can confirm contracted partners, though companies currently conducting proof-of-concept (PoC) evaluations cannot be named yet. Most are major domestic conglomerates and global corporations, with two to three international firms currently conducting in-house PoC trials.
Q: Company materials also list Bithumb as a client?
A: That deployment uses our legacy authentication solution, which was awarded through standard competitive bidding. The newer prospects I mentioned are specifically evaluating OTAC for advanced OT integration.
Q: Does establishing your UK headquarters signal an aggressive expansion into European markets?
A: Establishing our UK entity, swIDch, was driven less by the local UK market alone and more by our desire to build a global headquarters outside Korea. South Korea is not as widely recognized in global cybersecurity as it is in cultural industries. Initially, outreach attempts originating from South Korea received limited responses from international enterprises. Today, all our global business outreach across Europe, the US, and Asia is conducted through swIDch in the UK. The UK government offered attractive incentives, including visa sponsorship and official recognition as a UK company while maintaining its role as global HQ.
Q: Are team members permanently stationed at the UK office?
A: We maintained local staff in the UK until early last year while establishing our core tech partnerships. Now that our product maturity and commercial references are established, meetings arranged through our UK headquarters can be effectively conducted by our team operating out of South Korea, allowing us to streamline international operational costs.
Q: What are your prospects regarding the Middle Eastern market?
A: The Middle East represents a significant market opportunity. Currently, we are engaging with partners across Taiwan, the United States, France, Japan, and the Middle East without limiting ourselves to specific geographic boundaries.
Q: What is your long-term outlook for SSenStone?
A: During the years spent developing the business model for OTAC technology, many expressed skepticism. I persevered because I remained fully confident in the technology, which market research firm Gartner has also highlighted as a next-generation authentication architecture.
SSenStone's ultimate goal is to stand as a premier holder of foundational cybersecurity technology from South Korea. Rather than modifying existing foreign solutions, we intend to be recognized as the company that created the first original Korean security technology widely adopted across the global cybersecurity market.

 Login