
 Login

12 top productivity tips for Microsoft Edge
We live and work in browsers. It’s where we spend most of our time — and it’s where we waste most of our time as well. Web browsing is slow, inefficient, and full of time-sapping annoyances.
But it needn’t be that way. You can turn your browser into a lean, mean productivity machine. To do it, just follow these tips for Microsoft Edge in Windows 10 or 11. You’ll learn how to switch between home and work profiles, put idle tabs to sleep to speed up your PC, tap into the power of Microsoft’s Copilot AI assistant, and more.
(Note that these tips are written for the most recently updated version of Edge in Windows 11 25H2 and Windows 10 22H2. Things may be slightly different if you use a different Windows version, and not all of these features are available for Edge on macOS or other platforms.)
So let’s get started — time’s a-wasting, and so is your productivity.
1. Switch between work and personal profiles
With remote and hybrid work models now common, many people use the same device for work and personal use. When it comes to using a web browser, that can quickly become problematic.
Mixing work and personal favorites makes it far more difficult to quickly get to important work websites or personal websites. When you’re working, you don’t want to wade through hundreds of links to family photos, vacation destinations, and YouTube videos of cats befriending parrots when you’re just looking for the OSHA website about mine safety regulations. And when you’re off working hours and want to watch a video of a Persian cat nuzzling a cockatiel, a website detailing the GDPs of every country in Europe and Asia is not your primary destination.
Different profiles let you completely segregate your browser use. That doesn’t just mean different favorites. It also means different Collections, different extensions, different passwords, and more.
Each Edge profile is tied to a different Microsoft account. So to use different profiles, you’ll need to create different Microsoft accounts. To create a new Microsoft account in Windows 10 or 11:
- Go to https://account.microsoft.com. If you’re signed in to your account, click your profile icon or initials in the upper-right corner and select Sign out. Close Edge, restart it, and go back to https://account.microsoft.com/.
- Scroll down to the button that says Create an account, click it, and follow the prompts to create a new account.
- On the page that appears, click the Sign in button in the middle of the page. On the screen that appears, select the Create one! link, then follow the prompts to create a new account.
You’ve now got two different Microsoft accounts you can use for Edge. When you log into one of those accounts in Windows, that will be the default account that Edge will use when you browse the web.
To switch between the two accounts, you’ll need to add that second account to Edge. To do it:
- Click the user profile icon at the top right of Edge. On the small pane that appears, select Set up a new profile, then select either Personal or Work or School.
- You’ll be sent to a web page in a new instance of Edge. Click the Sign in button at the far right, then select Sign in to sync data.
- On the screens that appear, sign in and confirm that you want to proceed.
Once you’ve done that, you don’t have to log out of your current account and then log into the second account to use it in Edge. Instead, when you want to use the second account, click the user profile icon at the top right of the Edge window. A small pane appears with your current profile at the top. To switch to your other profile, select it in the “Other profiles” section.
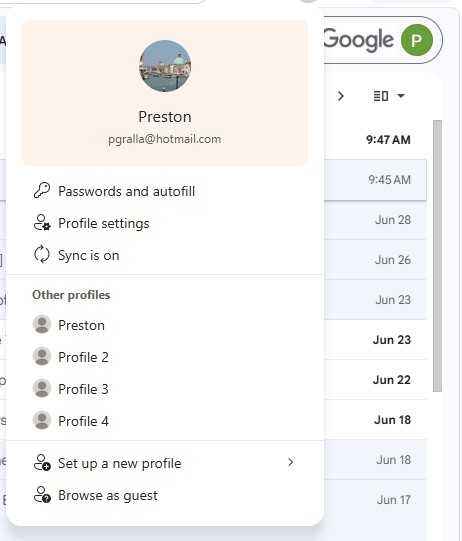
To minimize distractions, set up work and personal profiles in Edge.
Preston Gralla / Foundry
You’ll now be sent straight to that profile. When you do that, Edge will open in a new window. So you’ll have both your profiles running simultaneously, each with its own tabs, in two separate windows. (Note that you can set up multiple additional profiles.)
You can also tell Edge which profile to use when you visit certain websites. To do it:
- Click the user profile icon in Edge and select Profile settings. (Alternatively, you can click the three-dot icon next to the user profile icon and select Settings > Profiles.)
- In the “Profile settings” area, click Profile preferences.
- At the bottom of the “Automatic profile switching” section on the page that appears, click Add site next to “Custom site switch.”
- On the “Add site” popup, enter a website URL and select the profile you want to switch to for that site.
Should you decide you want to remove a profile, go to Settings > Profiles and scroll to the “More profiles” section. Click the trash can button next to any profile you want to delete. You can always add it again later using the steps above.
2. Get to your most-used sites quickly
Bookmarking and organizing favorites is a great way to manage a large collection of websites, but it’s not that useful if you simply want to get to a frequently used site quickly. Edge has some tricks up its sleeve if you want to get your most-used sites pronto.
Add a site to the new tab page
When you open a new tab in Edge, a page appears that shows you news and other items you might be interested in. It’s easy to pin a site to this page so it’s accessible whenever you open a new tab.
Look toward the top of the page, just underneath the search box. If you don’t see icons for pinned pages (such as for Yahoo, Amazon, your inbox, and so on), click the settings icon on the upper right of the page (it looks like a gear) and turn “Quick links” on.
A row of site icons appears, along with a + icon. Click the + icon and type or paste in the name and URL of the site you want to pin, then click Add. The site will now appear along with the other pinned pages.
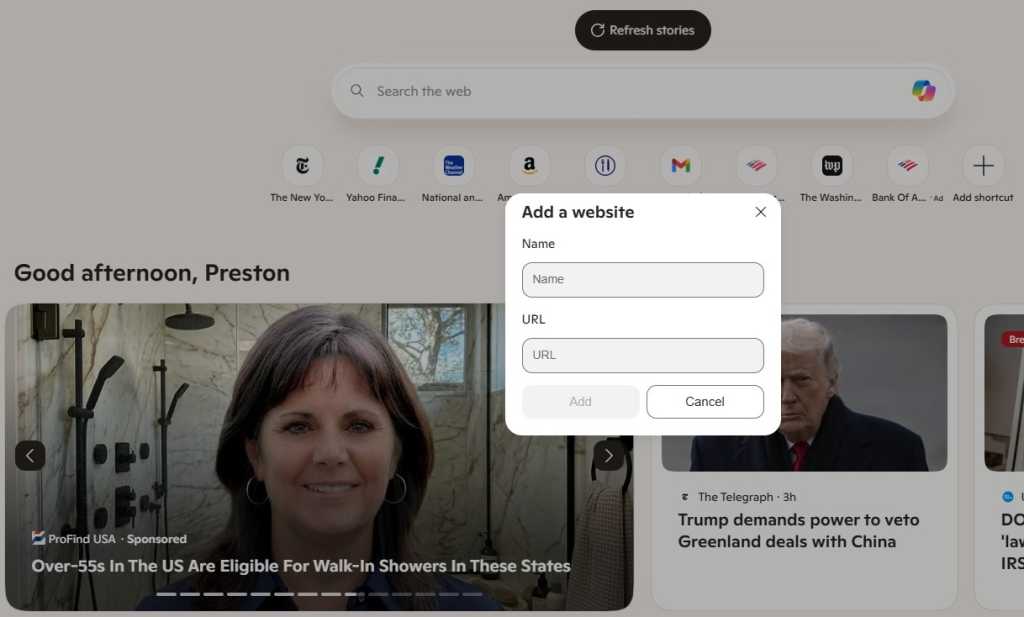
Pinning a site keeps it handy on the new tab page.
Preston Gralla / Foundry
You can rename or remove any site pinned to the new tab page by clicking the three-dot icon next to the site icon and selecting Rename or Remove from the menu that appears.
The new tab page is tied to your current profile, so you can set up different pinned sites on the new tab page for each of your profiles.
Pin tabs to the top of Edge
For even faster access to frequently used sites, you can pin them as browser tabs so they appear at the far left of all your other tabs in Edge. When you’re on the site you want to pin as a tab in Edge, right-click its tab and select Pin tab from the menu that appears. The pinned tab will now appear to the left of all your open tabs.
The icon for the pinned tab looks smaller than all of your other tabs, and it will persist even after you shut down and restart Edge. If you have multiple pinned tabs, all of them will appear to the left of any non-pinned tabs.
Like pinned sites on new tab page, your pinned tabs are unique to each Edge profile; they won’t carry over from profile to profile.
Pin sites you often visit to the Windows taskbar
For Windows users, the fastest way to access a frequently used site is to pin it to the Windows taskbar. That means it’s always visible (even when Edge isn’t running), and you can launch it with a single click.
When you’re on the site you want to pin, select the three-dot icon at the top right of the browser window and select More tools > Pin to taskbar. A small screen appears with a text box in it with the name of the site. Use the name provided or type a new name into the text box and click Pin.
3. Create tab groups for more efficient browsing
If you’re like lots of people, you frequently browse with many tabs open, and find yourself wasting time switching to the tab you want because of all of the clutter.
There’s a simple fix: group tabs into categories so you can quickly switch to the tab group that has the tab you want. For example, you might group them into “News,” “Museums,” “Finance,” and so on. Or you could create a tab group for research related to a specific project.
To do it, right-click a tab, select Add tab to new group, and then name the tab group. You can then drag other tabs into the group. You can also assign each tab group a unique color so they’re easy to differentiate at a glance.
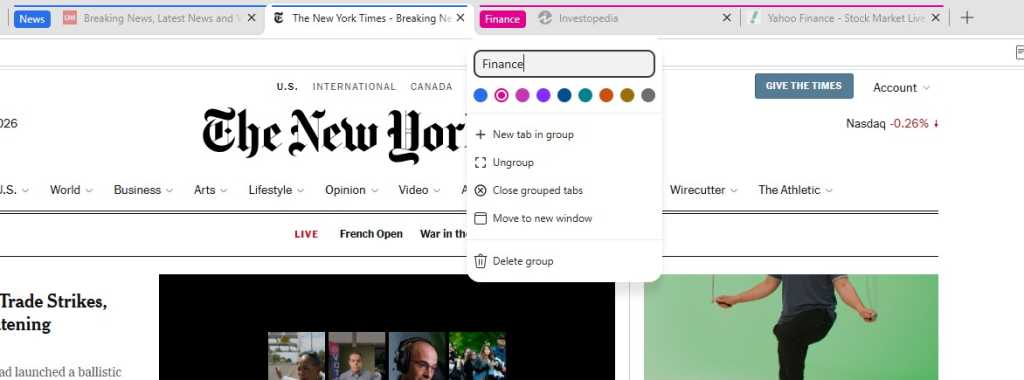
Creating tab groups makes it easier to find the tab you want quickly.
Preston Gralla / Foundry
If you’ve already created a group, when you right-click a tab, you’ll see “Add tab to group” rather than “Add tab to new group.” When you click the arrow next to it, you’ll see a list of all your existing groups, so you can easily add it to any of them. You’ll also see “New group,” which will let you create and customize a new group.
Once you’ve created a tab group, you can rename it, change its assigned color, add new tabs to it, ungroup the tabs from it, delete the group and all the tabs in it, and more. Just right-click the name of any group and select an option from the menu that appears.
4. Enlist a Copilot as you browse
Microsoft’s genAI chatbot, Copilot, has become increasingly integrated with Edge, so much so that Microsoft now calls Edge an “AI browser.” At the moment, that’s more hype than fact, but it is true that Edge gets new Copilot features added on a regular basis.
Edge provides a couple of ways to interact with Copilot, one of which is to open the Copilot sidebar to the right of the main browser window. (We’ll go over the other method later in the story.) Click the Copilot icon at the top right of Edge, and the Copilot pane appears. Here’s where you type in prompts for Copilot.
There’s a tremendous amount you can do with Copilot, most of which is beyond the scope of this article. To learn more about what it can do and how to use it, see our story “9 ways to use Copilot right.”
However, here’s one use designed specifically for web browsing: summarizing the contents of the page you’re currently visiting. Depending on the structure and content of the page, Copilot can give a high-level overview of the entire page, provide capsule descriptions of individual articles or sections, and more. You can also ask Copilot to extract specific information from a page, such as all the AI-related information on it, and organize the information into a bulleted digest.
To do all that, open a web page and open the Copilot sidebar. You’ll see a few suggested prompts, one of which should be related to summarizing the page, such as Summarize the main points on this page or Create a summary of this page. Click the prompt, or if you don’t see it, type it into the text box at the bottom of the Copilot pane.
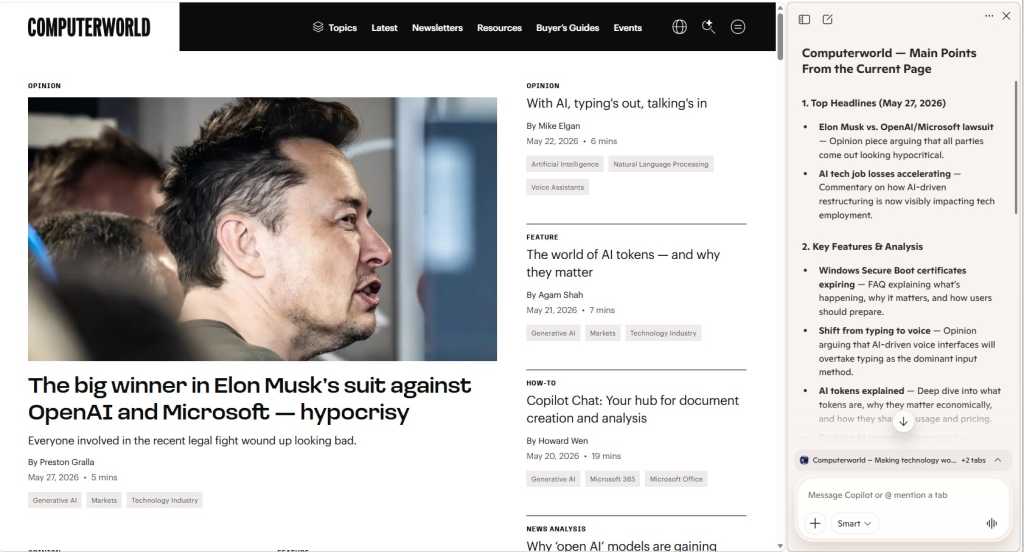
Use Copilot to summarize the content on a web page.
Preston Gralla / Foundry
You can also ask it to summarize the last page you’ve visited. Click the down arrows towards the bottom of the Copilot pane, and you’ll see a listing for the previous page you’ve visited, such as Computerworld.com. Click the text summarize my recent activity on [page] and it will do that for you. Again, if you don’t see that text, type it into the Copilot text box.
The summarization feature, though, still has rough edges, or at least it did when I was writing this article. If you leave the web page you’re currently on and go to a new one, the summary of the old page remains, and there isn’t an immediate way to summarize the new one. To get a summary of the new page, you’ll have to scroll to the bottom of the Copilot pane, click the arrow (it will be facing either up or down, depending on whether you’ve previously clicked it) and click “Create a summary of this page.”
In that section, you can also click listings of your other open tabs and get summaries of any of them.
5. Remove clutter when you launch new tabs
When you create a new tab, the initial page is filled with pinned sites, suggested news stories, widgets, and more. If you find that page distracting, you can change it to a much cleaner, more stripped-down page.
If you haven’t pinned specific sites to the row of icons below the search box (see tip #2 above), you can make Edge’s default icons go away: Click the gear icon on the upper right of the page, and a “Page settings” panel pops up. In the “Quick links & search” section, click the dropdown next to “Quick links” and select Off. That gets rid of the icons for web sites just beneath the search box.
If you have pinned your own preferred sites there, you’ll want to leave quick links enabled, but you can turn the “Show sponsored links” toggle to Off to get rid of ads.
To get rid of the news articles that overwhelm the page, go to the “Show content” area of the panel and move the “Show feed” toggle to Off. Or, if you want to really strip down the page, move the “Show content” toggle to Off. That kills pretty much everything on the page except the weather. If you don’t want to see that either, scroll down a bit more and move the “Weather” toggle to Off.
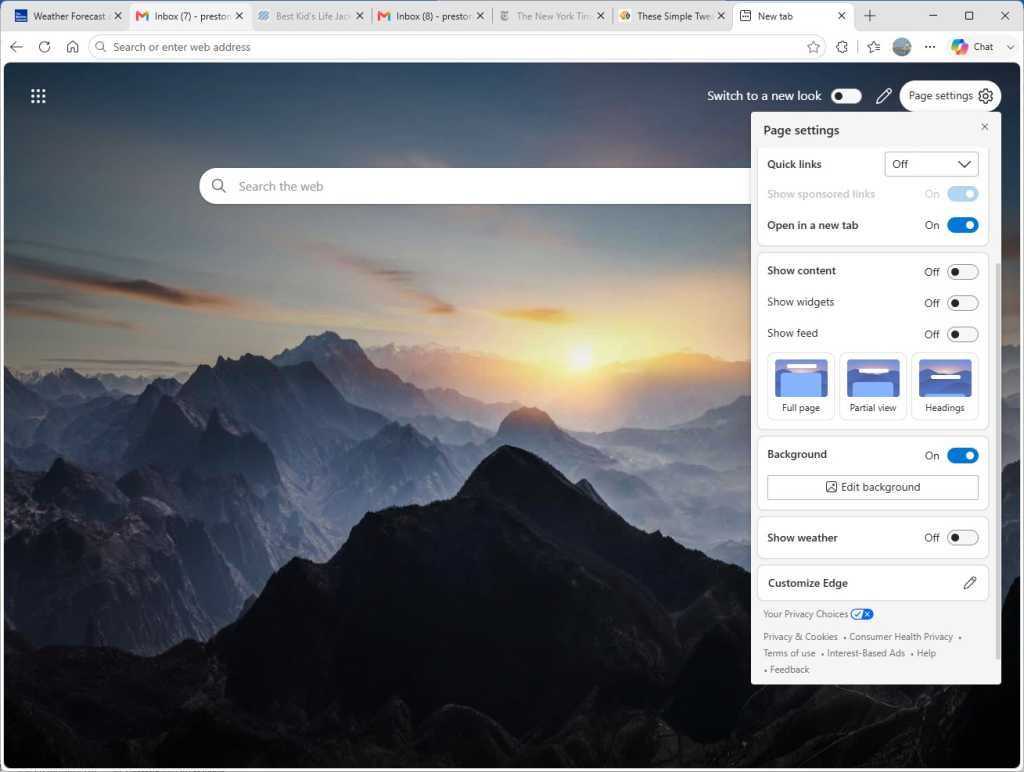
Going with the stripped-down new tab look in Edge.
Preston Gralla / Foundry
You can also strip out the background graphic for the new tab page by turning off the “Background” toggle. I don’t recommend it, though, because when you do that, you’ll get a gray page with a big Microsoft logo dead center when you launch a new tab.
6. Launch Copilot-centered new tabs
If you’re a frequent Copilot user, you might want to take a different approach to the new tab page.
The Copilot you get in a side pane when you click the Copilot icon at the top right of Edge is a somewhat stripped-down version of Microsoft’s full-blown Copilot app. If you’re looking to use the full-fledged version, there’s a simple way to do it: Tell Edge to open Copilot every time you open a new tab.
To do it, click the three-dot icon to the left of the Copilot icon at the top right of Edge and navigate to Settings > Start, home, and new tab page. In the “New tab page” section, turn on the Copilot new tab page toggle. From then on, every time you open a new tab, you’ll launch a full Copilot screen that’s similar to the standalone Copilot app.
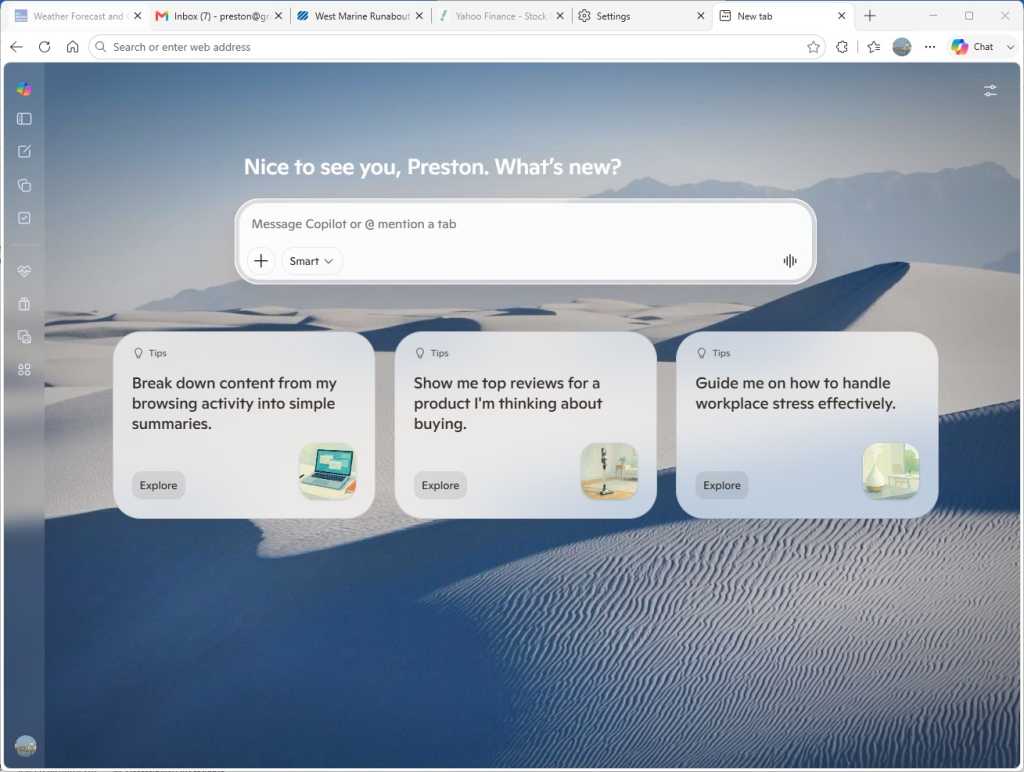
The Copilot new tab page puts Copilot chat front and center.
Preston Gralla / Foundry
You’ll see the usual Copilot prompt box front and center, and beneath that, several prompts Microsoft thinks you might want to use. (Note to Microsoft: I’ve never used one of those suggestions even once. I’d guess few other people have either.)
What’s really new here are the vertical icons running down the left side of the page. Here’s a brief rundown of what each one does:
- Open sidebar: Widens the navigation bar and shows a list of your recent chats so you can revisit any of them.
- New chat: Start a new chat with Copilot.
- Library: Build a library of Copilot-created content such as images, reports, podcasts, documents, and more.
- Tasks: Create a Copilot task that automates something you want done, such as sending you a weekly email about a company’s stock price.
- Health: Open Copilot Health, a version of Copilot designed specifically for getting health information.
- Shopping: Use Copilot as a shopping assistant.
- Imagine: Create or edit an image using Copilot.
- Experiments: Discover and use new Copilot features that Microsoft is testing but that may or may not be officially launched at some point.
Clicking the Copilot icon at the top of the list of vertical icons returns you to the main Copilot interface you get when you launch a new tab.
As you can see, many of these new Copilot functions are aimed at consumers and unlikely to be useful in a business setting. Still, if you frequently turn to Copilot for help, you might find the Copilot new tab page a good alternative to the standard new tab page.
And note that setting up the Copilot new tab page doesn’t prevent you from browsing or searching the web normally. Just enter the search term or website you want to visit in the address bar at the top of the screen.
7. Put tabs to sleep to conserve system resources and boost battery life
If you’re like most people, you keep multiple tabs open in Edge so you can easily switch among the sites, web apps, and information important to you. It’s a great time-saver.
But it can also be a big memory and processor hog, which can slow down both your browsing and your other computing tasks. It needn’t be that way, though. You can put inactive tabs to “sleep” until you need them, freeing up resources, which will make your PC speedier and make its battery last longer, even when you have multiple tabs open. Microsoft claims that putting inactive tabs to sleep reduces memory use by an average of 32% and CPU use by an average of 37%.
Here’s how to do it:
- In Edge, click the three-dot icon on the upper right of the screen and select Settings > System and Performance > Performance.
- In the “Memory” section, move the slider to On next to Automatically put tabs to sleep.
- To change the length of time it takes to put an inactive tab to sleep, below “Automatically put tabs to sleep” click the drop-down arrow and select a time. Your choice is anywhere from 30 seconds to 12 hours.
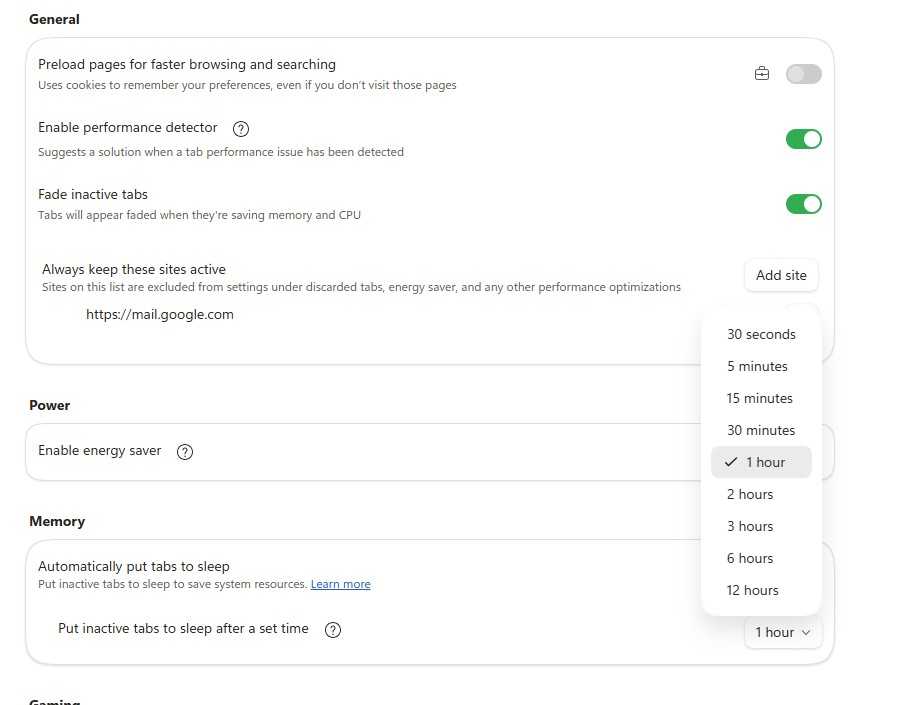
Putting tabs to sleep can significantly reduce CPU and memory use.
Preston Gralla / Foundry
To reawaken any tab that’s been put to sleep, simply click on it, and it will resume normal activity.
There’s a chance that some sites might not work properly after they’ve been put to sleep. If that happens to you, you can tell Edge never to put that site to sleep again. To do it, scroll up to the “General” area on the “System and performance / Performance” page of Settings. Click the Add site button next to the “Always keep these sites active” item and paste in the URL of any site you don’t want to sleep.
8. Reduce power use with ‘energy saver’
Browsers can be power hogs, especially if you have multiple tabs open and are playing videos or music in them. That can be a particular problem if you’re using a laptop that isn’t plugged into a power source.
In Edge, the “energy saver” setting reduces the amount of system resources the browser uses, which extends your PC’s battery life. If you enable energy saver, it becomes active when your laptop is unplugged. Microsoft claims energy saver can give you on average an extra 25 minutes of battery life. To use it:
- In Edge, click the three-dot icon on the upper right of the screen and select Settings > System and Performance > Performance.
- In the “Power” section, make sure the toggle next to “Enable energy saver” is turned on. When you do that, you see two options: “Balanced” and “Maximum savings.”
- Select Balanced if you want your laptop to go into a lower-power mode to save battery life when your laptop is unplugged or has a low battery. Select Maximum savings if you know you’re not going to be able to plug your laptop in for some time. Note that in this mode, your video quality may be affected.
There’s also a separate option to use energy saver even if your laptop is plugged in. Use this option if you want to consume less energy when you use your computer. Note that if you use it, you may experience slowdowns when browsing the web.
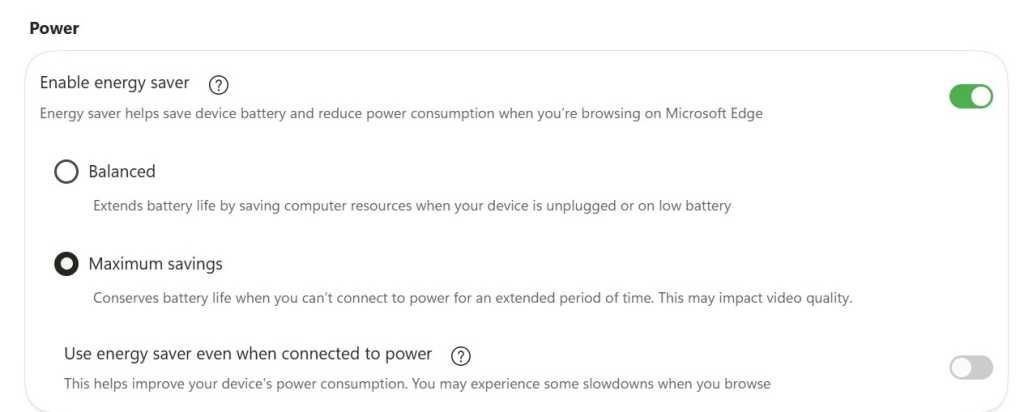
You can get an extra 25 minutes of battery life with the energy saver setting, Microsoft claims.
Preston Gralla / Foundry
9. View and mark up PDFs
With Edge, there’s no need to launch a separate application when you want to read or mark up a PDF; its built-in PDF app is quite good. With it, you can draw on and highlight sections of the PDF and erase the marks you made as well. So save yourself time and use Edge rather than third-party software.
You don’t need to do anything to read a PDF online. Simply click it, and by default it will launch in Edge’s reader. You’ll find the markup tools, including for drawing, highlighting, and erasing, in a toolbar towards the top of the screen. To open a PDF from your hard disk, when you’re in Edge, press Ctrl-O, then navigate to the PDF and click it.
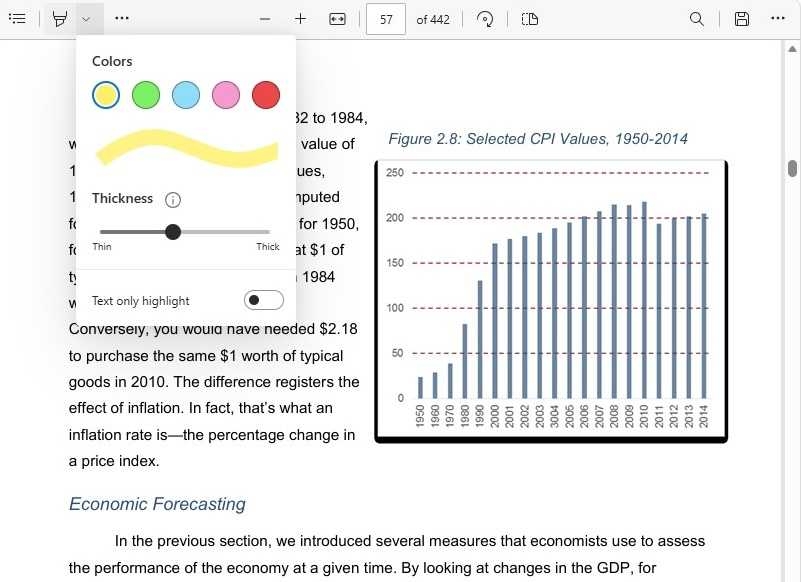
Edge has a surprisingly useful PDF viewer with markup tools.
Preston Gralla / Foundry
If you prefer to use your own PDF reader, even for PDFs found online, you might be annoyed that every time you click a PDF, it opens in Edge’s PDF reader. You can change that, though, by changing your default PDF reader.
In Windows Settings, select Apps > Default Apps and in the search box at the top of the screen just below “Set a default for a file type or link type,” type in .pdf. After you do that, the listing “Microsoft Edge Microsoft Edge PDF document” appears. Click it, and a screen appears showing you all the applications on your PC that can read PDFs. Select the one you want to use instead of Edge.
10. Turn on Edge’s AI-powered ‘scareware’ blocker
The internet is filled with scammers using sophisticated attacks to steal your data or money. A common one is so-called “scareware,” in which when you visit a website, your PC is suddenly locked into full-screen mode filled with fake malware warnings that claim your computer has been infected and urge you to call a phony tech-support line or allow remote access to your device to supposedly fix the problem.
Once you do that, the scammers steal your data, get you to pay for phony solutions, or embed malware on your system.
To fight that, Edge includes an AI-powered scareware blocker that builds and constantly updates a machine-learning model that detects suspicious behavior and stops the scamware in its tracks.
Typically, the scamware detector is turned on, but there’s a possibility it’s been turned off at some point or was never turned on in the first place. For example, on PCs with only 2GB of RAM or fewer than 5 cores, it’s not turned on by default. Microsoft recommends enabling it on those machines. To do it, in Edge go to Settings >Privacy, search, and services > Security, and in the “Scareware blocker” setting, turn the slider from off to on.
When you do that, make sure that “Block sites detected as scams” and “Share detected scam sites with Microsoft Defender SmartScreen” are turned on as well.
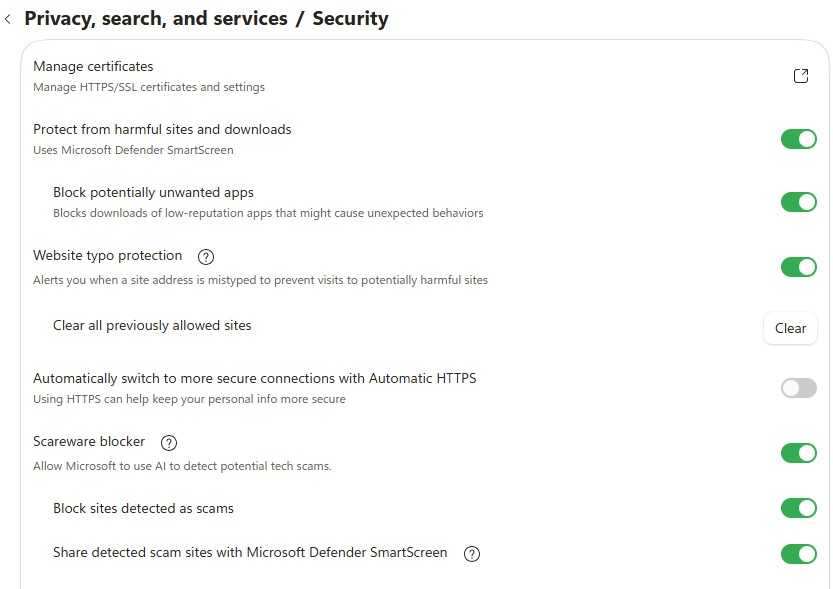
Turn on Edge’s scareware blocker to protect yourself from scams and data theft.
Preston Gralla / Foundry
11. Use Edge’s one-click form filler
How many hours a week do you spend mindlessly filling out web forms — your office or home address, shipping address, email address, and phone number? Wouldn’t it be nice to get that time back?
With autofill, built into Edge, you can. To use it, in Edge go to Settings > Passwords and autofill > Addresses and more. Turn on the toggle next to “Save and autofill addresses.” You can also choose to have Copilot analyze web forms and decide which bits of your information belong in which part of the form.
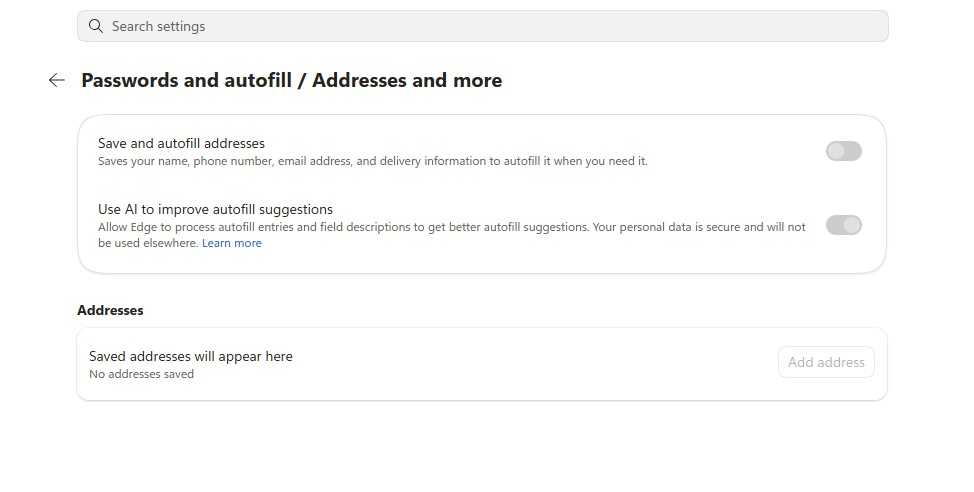
Microsoft autofill saves information that can be used to fill out forms online.
Preston Gralla / Foundry
From now on, whenever you visit a web form, just click in a text box, and your information will appear in a popup. Select it and the form will fill in. You can go back to Passwords and autofill to change any information you want.
12. Save time with keyboard shortcuts
There’s a good chance you use keyboard shortcuts for some of your office applications, like Word and Excel — and you likely use some for Windows itself.
But when it comes to browsers, many people forgo the keyboard except when absolutely necessary. That’s too bad, because keyboard shortcuts are a big timesaver. So to improve your productivity, check out these keyboard shortcuts for Edge in Windows. (Mac users can generally substitute the Cmd key for Ctrl and the Opt key for Alt.)
For even more shortcuts, see Microsoft’s complete list of keyboard shortcuts for Edge.
Useful keyboard shortcuts in Microsoft Edge
| Key combination | Task |
|---|---|
| Ctrl-Shift-B | Show or hide the favorites bar |
| Ctrl-D | Add the current site to favorites |
| Alt-D or Ctrl-L | Select the URL in the Address bar |
| Ctrl-E or Ctrl-K | Open a search in the Address bar |
| Ctrl-F | Find on the current page |
| Ctrl-R | Reload the current page |
| Ctrl-H | Open your History |
| Ctrl-M | Mute or unmute volume on the current tab |
| Ctrl-N | Open a new window |
| Ctrl-Shift-N | Open a new InPrivate window |
| Alt-F4 or Ctrl-Shift-W | Close the current window |
| Ctrl-T | Open a new tab and switch to it |
| Ctrl-W | Close the current tab |
| Ctrl-Tab | Switch to the next tab |
| Ctrl-Shift-Tab | Switch to the previous tab |
| Ctrl-+ (plus symbol) | Zoom in |
| Ctrl– (hyphen) | Zoom out |
| Ctrl-P | Print the current page |
| Ctrl-Shift-. | Open the Copilot pane |
This article was originally published in March 2021 and most recently updated in July 2026.


