 Login

CISA: Hackers now exploit SolarWinds Serv-U flaw to crash servers
CISA warned today that hackers are now actively exploiting a recently patched high-severity SolarWinds Serv-U flaw to crash servers. [...]

Experts say increased use of crops for fuel is ‘dangerous game’ that could send food price inflation soaring
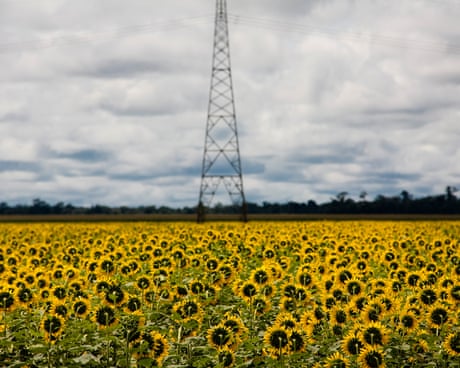
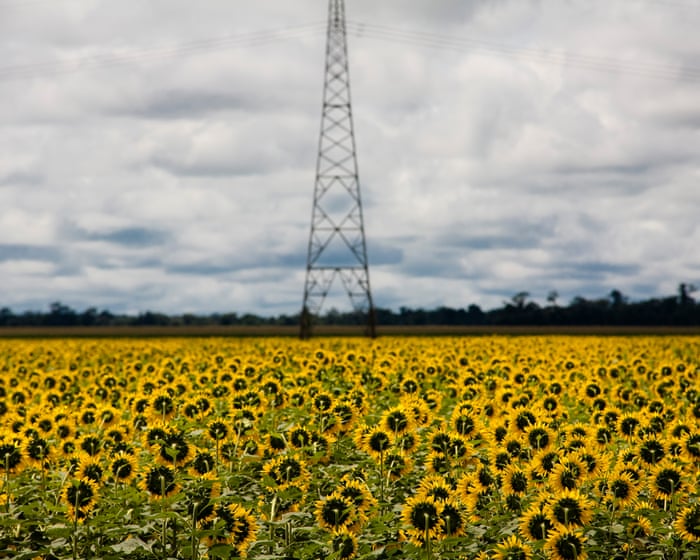
Demand for biofuels is likely to leap by nearly a third this year, which could send food price inflation soaring further and push the world closer to a global food crisis.
More countries are opting to increase biofuel use as the price of oil has jumped to nearly $100 a barrel after the US-Israeli attacks on Iran and the closure of the strait of Hormuz.
Continue reading...
© Photograph: Brazil Photos/LightRocket/Getty Images
© Photograph: Brazil Photos/LightRocket/Getty Images
© Photograph: Brazil Photos/LightRocket/Getty Images
Dashlane said that attackers mounted a coordinated hacking campaign against a large base of its users in an attempt to recover as many encrypted password vaults as possible. The password manager provider said fewer than 20 personal user vaults were downloaded before it shut down the operation.
In a campaign that started Sunday, the unknown threat actor abused the mechanism that allows Dashlane users to add new devices, such as computers or phones, to their accounts. By abusing Dashlane's programming interfaces for device enrollment, the attackers sent requests to large numbers of existing users’ registered email addresses. In an update published Thursday, Dashlane wrote:
The threat actor targeted the API endpoints for device registration and used a brute force attack to send a large volume of automated requests to those endpoints.
In response, Dashlane’s automated security systems operated as intended, triggering an automatic lockout of the targeted accounts to protect those users. Before the attack was fully mitigated, the threat actor was able to brute force and generate valid tokens for fewer than 20 personal plan customers, allowing them to register a new device on those accounts and download copies of users’ encrypted vaults.
When a user installs the Dashlane app on a new device and attempts to enroll it in their existing account, Dashlane first verifies the account holder's identity. This verification is completed by sending a one-time six-digit token to the user’s registered email address (or, for users who have enabled two-factor authentication, by validating a six-digit code generated by their authentication app).
© Getty Images
