❌

Reading view

The Messages That Show Covid Scientists Secretly Suspected a Lab Leak

Scientists who were instrumental in shutting down theΒ Covid lab-leak theoryΒ admitted in private "we can’t rule it out" months after publishing a paper closing down the possibility, newly released messages show.

The post The Messages That Show Covid Scientists Secretly Suspected a Lab Leak appeared first on The Daily Sceptic.
  •  

Russia appears set to finally address long-term, serious space station cracks

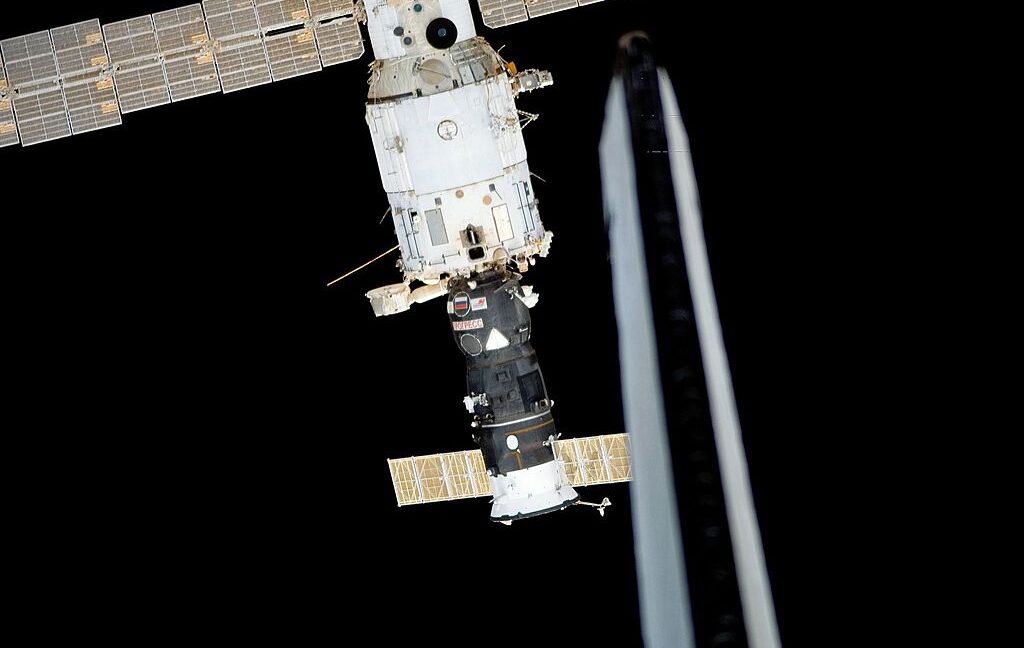
Ten days ago, in a moment of very high drama in orbit, NASA directed its astronauts living on the International Space Station to briefly seek emergency refuge in a Crew Dragon spacecraft.

Since then, neither the US space agency nor Roscosmos has provided additional public information about the situation in orbit. But according to sources who spoke to Ars, following the spectacle in space, the problem has been successfully fixed.

At issue were persistent cracks in a small area of the International Space Station attached to the Russian Zvezda service module, known as the PrK module. The problem has been ongoing since 2019, and Russian astronauts have been attempting various fixes, often using a sealant called Germetall-1.

Read full article

Comments

Β© NASA via Getty Images

  •  

In stunning display of stupid, secret CISA credentials found in public GitHub repo

Security researcher Brian Krebs brings us the news that America's Cybersecurity & Infrastructure Agency (CISA) has had a large store of plaintext passwords, SSH private keys, tokens, and "other sensitive CISA assets" exposed in a public GitHub repo since at least November 2025.

The now-offline public repoβ€”named, somewhat aspirationally, "Private-CISA"β€”was brought to Krebs' attention by GitGuardian's Guillaume Valadon, who was alerted to the repo's presence by GitGuardian's public code scans. Krebs says that Valadon approached him after receiving no responses from the Private-CISA repo's owner.

In an email to Krebs, Valadon claimed that the repo's commit logs show that GitHub's default protections against committing secretsβ€”protections designed to protect unwitting or unskilled developers against exactly this kind of stupidnessβ€”had been disabled by the repo's administrator.

Read full article

Comments

Β© Dzmitry Skazau / Getty

  •  
❌