❌

Reading view

Cameras, sensors, and 3D body scans: All the tech helping eliminate blown calls

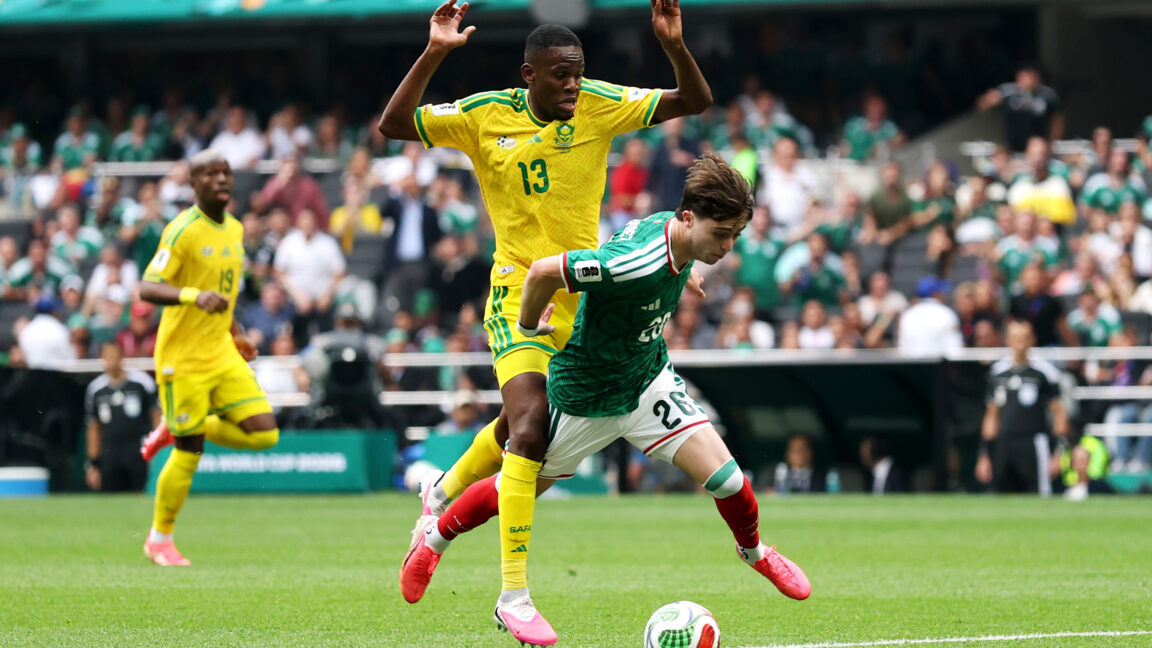
At the 2026 World Cup, the refs on the field and the officials on the sidelines will be able to use an abundance of tech to help call penalties, spot offside violations, and make other consequential decisions.

The video assistant referee system, known as VAR, and the semi-automated offside technology (SAOT) have been used in soccer for years. But the setup at this summer's World Cup represents some of the most advanced uses of adjudication tech to dateβ€”not just in soccer, but across all high-level sports.

During each match, the pitch will be awash in sensors, cameras, and new computer vision software. One especially notable advancement this year is the use of digital twins. Every player in the World Cup has had their body scanned by a computer. The digital twin of any athleteβ€”which precisely matches their height, limb length, and shoe sizeβ€”can be dropped into a virtual simulation of the game to determine their exact position relative to the ball, boundary lines, and other players. Officials can use all of this data to help spot infractions, determine penalties, and smooth out the edges of the beautiful game.
Read full article

Comments

Β© Luke Hales/Getty Images

  •  

One day after discovery, Meta pulls facial recognition code from its smart glasses

One day after WIRED revealed that Meta had quietly embedded an unreleased face-recognition system into an app installed on more than 50 million phones, the company removed it, according to a WIRED analysis of the latest version’s code.

The most recent version of Meta AI, a companion app for its line of smart glasses, strips out the unactivated software components that powered the system Meta internally called NameTag. The version published the day of WIRED’s report included several code libraries explicitly named for face recognition. Friday’s release includes none of them.

Andy Stone, Meta's vice president of communications, told WIRED on Monday that the feature is purely exploratory, adding: β€œNo final decision has been made on what to do here, if anything.”

Read full article

Comments

Β© David Paul Morris/Bloomberg/Getty

  •  

A hacker group is poisoning open source code at an unprecedented scale

A so-called software supply chain attack, in which hackers corrupt a legitimate piece of software to hide their own malicious code, was once a relatively rare event but one that haunted the cybersecurity world with its insidious threat of turning any innocent application into a dangerous foothold in a victim’s network. Now one group of cybercriminals has turned that occasional nightmare into a near-weekly episode, corrupting hundreds of open source tools, extorting victims for profit, and sowing a new level of distrust in an entire ecosystem used to create the world’s software.

On Tuesday night, open source code platform GitHub announced that it had been breached by hackers in one such software supply chain attack: A GitHub developer had installed a β€œpoisoned” extension for VSCode, a plug-in for a commonly used code editor that, like GitHub itself, is owned by Microsoft. As a result, the hackers behind the breach, an increasingly notorious group called TeamPCP, claim to have accessed around 4,000 of GitHub’s code repositories. GitHub’s statement confirmed that it had found at least 3,800 compromised repositories while noting that, based on its findings so far, they all contained GitHub’s own code, not that of customers.

β€œWe are here today to advertise GitHub’s source code and internal orgs for sale,” TeamPCP wrote on BreachForums, a forum and marketplace for cybercriminals. β€œEverything for the main platform is there and I very am happy to send samples to interested buyers to verify absolute authenticity.”

Read full article

Comments

Β© NiseriN via Getty Images

  •  
❌