❌

Reading view

Scientists Develop New Technique to Protect Privacy of Electrocardiogram Data

In a groundbreaking development addressing the burgeoning concern of privacy in modern medical technology, researchers at the University of Kansas have unveiled a transformative artificial intelligence (AI) model designed specifically to safeguard sensitive biometric data embedded within electrocardiograms (ECGs). This innovation is poised to reshape how medical institutions share and analyze vital cardiovascular data without compromising patient confidentiality. Electrocardiograms have long been renowned for their role in capturing the heart’s electrical activity to diagnose and monitor cardiac health; however, as AI integration deepens, these signals inadvertently reveal more than just clinical information — exposing personal attributes such as sex, age, race, and even uniquely identifiable biometric markers.

The research team at Kansas, led by doctoral candidate Fairuz Shadmani Shishir in collaboration with the KU Medical Center, has pioneered the privacy-preserving variational autoencoder (PP-VAE). This novel AI architecture is specially engineered to retain the clinical utility of ECG data while systematically obfuscating sensitive biometric features that might otherwise be inferred through advanced AI analysis. The dual objective of PP-VAE is both technically sophisticated and ethically imperative, ensuring that predictive diagnostic accuracy remains uncompromised while minimizing the risk of privacy breaches inherent in sharing raw biomedical signals.

Electrocardiograms, traditionally viewed as a straightforward diagnostic tool, have grown in complexity with modern AI techniques that can extrapolate a multiplicity of patient traits beyond the cardiovascular parameters they were designed to measure. Shishir notes that these advanced systems can uncover “soft biometrics” such as demographic information, which raises pressing data governance and patient privacy challenges. By developing PP-VAE, the researchers aim to reimagine ECG data processing whereby sensitive attributes are masked without degrading the signal quality necessary for important medical prognoses, such as identifying patients at risk of left ventricular ejection fraction (LVEF) abnormalities, a critical indicator linked to heart failure and mortality risk.

The technical underpinning of PP-VAE involves training independent convolutional neural networks to disentangle and suppress identifiable biometric markers while preserving clinically relevant features within the ECG signal. This balancing act required careful engineering to ensure that the encoded ECG data remained diagnostically rich, capable of supporting predictions related to conditions such as left ventricular hypertrophy and forecasting five-year mortality risk. The research showcased that their method consistently outperformed or competed with other state-of-the-art AI models, marking a significant stride in machine learning’s ability to harmonize privacy with clinical efficacy.

Importance of such privacy-preserving strategies becomes particularly clear against the backdrop of the healthcare industry’s increasing reliance on data sharing for collaborative research, AI model development, and multi-institutional patient care coordination. The KU team articulates that unrestricted data sharing without privacy controls introduces tangible risk vectors for patient re-identification and misuse. PP-VAE proposes a scalable approach toward enabling secure exchange of ECG data, thus fostering innovation and improving medical outcomes while staunchly protecting individual privacy rights.

This research also touches on the profound issue of bias within AI-driven medical diagnostics, which has historically contributed to disparities in healthcare delivery among marginalized populations. The team consciously incorporated balanced datasets reflective of gender and racial diversity in their model training to mitigate bias and improve generalized performance across varied demographic groups. While initial validations were primarily conducted using data from KU Medical Center and publicly available datasets, future work is projected to expand this cross-regional training, enhancing the robustness and impartiality of the model when applied globally.

Another compelling facet of this breakthrough is the planned public release of the PP-VAE model, reflecting the researchers’ commitment to transparency, collaboration, and democratization of AI tools in medicine. By allowing institutions worldwide to access and further refine the model with local datasets, the innovation promises to catalyze a new era of secure, privacy-conscious healthcare analytics. Adoption of PP-VAE could alleviate prevalent trust issues among patients concerned about the confidentiality of their biometric health information—a critical barrier to broader acceptance of AI-driven healthcare technologies.

Furthermore, the researchers discuss the broader implications for data-driven diagnosis, illustrating how balancing the protection of sensitive attributes with clinical utility could become a standard principle in biomedical AI applications beyond cardiology. This approach offers a blueprint for addressing ethical and privacy challenges that increasingly pervade the intersection of health data science and artificial intelligence.

The University of Kansas team’s work is also distinguished by its multidisciplinary nature, featuring collaboration between electrical engineering, computer science, and cardiovascular medicine experts. Such an integrated approach enabled the synthesis of advanced machine learning expertise with intimate clinical insight, culminating in a pragmatic solution tailored precisely to real-world healthcare needs.

This pioneering study was recently published in Scientific Reports, showcasing detailed methodology, experimental evaluations, and comparative performance analyses that underscore the efficacy and potential transformative impact of PP-VAE. Supported by the American Heart Association, this research is an exemplar of innovative technological stewardship addressing one of the most pressing challenges in digital health.

As AI continues to proliferate across medical diagnostics, models like PP-VAE will undeniably play a critical role in shaping ethical frameworks and technological architectures for future patient data management. By protecting sensitive biometric identifiers embedded in ECG data, the model not only preserves patient autonomy but also enhances the potential for AI-driven insights to be safely harnessed for better clinical outcomes worldwide.

The journey ahead involves validating and deploying this technology in diverse healthcare environments globally to ensure scalability, efficacy, and fairness remain intact as data heterogeneity increases. Yet, with the foundational work from the University of Kansas, a robust and privacy-conscious approach to ECG analysis and beyond appears well within reach, heralding a new era of secure AI-driven cardiovascular care.


Subject of Research: Privacy-preserving AI models for electrocardiogram data analysis
Article Title: Safeguarding Patient Privacy in Electrocardiogram Analysis with AI-driven Models
Web References: Scientific Reports Article
Image Credits: Fairuz Shadmani Shishir / University of Kansas

Keywords

Privacy-preserving AI, Electrocardiogram (ECG), Variational Autoencoder, Convolutional Neural Networks, Biomedical Data Security, Cardiovascular Diagnostics, Left Ventricular Ejection Fraction, Patient Privacy, Machine Learning Bias, Medical Data Sharing, Artificial Intelligence in Healthcare, Clinical Decision Support

  •  

FBI Issues Urgent Kali365 Security Warning For Teams, Outlook, OneDrive Users

alternative_right shares a report from The Hill: The FBI released an urgent security warning to the public about a fast-acting scam targeting Microsoft 365 users on Teams, Outlook and OneDrive. The agency warned that the hacking platform Kali365 seeks out OAuth device codes, allowing scammers to sneak past multi-factor authentication codes, and without the need for a password, to access Microsoft accounts. Scammers will send a phishing email impersonating a trusted document-sharing service with a device code and instructions on how to verify, according to the FBI. "Kali365 lowers the barrier of entry, providing less-technical attackers access to AI-generated phishing lures, automated campaign templates, real-time targeted individual/entity tracking dashboards, and OAuth token capture capabilities," the FBI stated. The platform is sold to scammers with a $250 per month subscription. The FBI, which first detected Kali365 in April, described the hacking platform as an "emerging Phishing-as-a-Service platform." Hackers with limited skills can access advanced phishing tools through the platform, according to NordPass.

Read more of this story at Slashdot.

  •  

Roblox exec says ticking a box for age verification is ‘not enough anymore’

Pixels of data over an obscured human face with a date entry form.

Roblox's vice president of safety product policy, Eliza Jacobs, told NBC News that Roblox is "optimistic" that its new facial age estimation tech will "continue to get better," saying, "Ticking a box to say you're 13 or older, it's not enough anymore." NBC invited a group of kids to try out Roblox's new video selfie age check process, but they weren't able to get around it with a fake mustache. Jacobs claims Roblox's facial age estimates can typically land "within 1.4 years of a child's exact age."

Roblox announced plans in April to begin using its video selfie age estimation tech to sort players into age brackets. Users under 16 and unde …

Read the full story at The Verge.

  •  

Meta Tapped a Pentagon Supplier to Prototype Face Recognition for Its Glasses

Rank One, whose board includes a former CIA deputy director and a former FBI science chief, supplied face recognition to Meta for internal development of its smart glasses app.

  •  

Inside the coming war over face cameras

Several trends are now converging that threaten to pit tech companies against the general public. 

Miniaturization has finally enabled companies to build AI glasses that look and function like normal glasses, but with microphones and cameras. People are increasingly talking to AI, rather than typing. And multimodal input, especially video, is on the rise. 

Put all of these trends together and you get a nascent industry pushing toward all-day, everyday AI glasses with cameras — and a worried public already pushing back at  the idea.

Let’s look at how we got here.

Meta started it with a surprise hit: its second-generation Ray-Ban Meta glasses, which later gained multimodal AI capability. Its Meta Ray-Ban Display glasses add one in-lens screen — but both versions of the glasses have cameras. (The company is working on a third generation that will probably ship next year.)

Google provides the AI and software platform through Android XR and Gemini, partnering with hardware makers to put its AI on other companies’ glasses. At Google I/O last month, Google unveiled frames from Gentle Monster and Warby Parker running Android XR with Gemini AI; they’re scheduled to launch this fall. Google is working on two types of AI glasses, one with screens and one that is audio-focused. Both types have cameras, though. 

Samsung is working to launch AI-powered smart glasses, too, code-named “Jinju.” The company offered up details at Google I/O alongside Google. The glasses feature a 12-megapixel camera with autofocus; run on Android XR with Gemini AI; are co-designed with Gentle Monster and Warby Parker; and are slated to launch in July at the Samsung Unpacked event. 

(As with Meta and Google, Samsung is working on AI glasses with and without screens, but both of its models have cameras.)

Tech giant Apple is also on the glasses train, based on reporting from anonymous insiders. Codenamed N50, the Apple glasses could have two cameras, one for pictures and videos, the other for multimodal AI input and hand-gesture control. (Apple is also working on a pendant and next-gen AirPods, both of which have cameras.) 

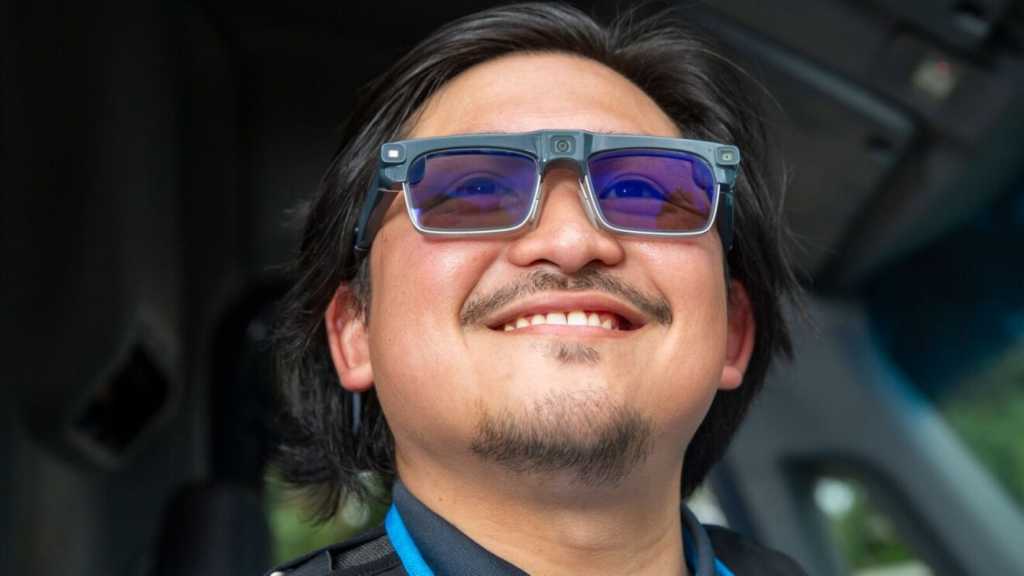
There’s Amazon, which is reportedly developing a new line of consumer AI glasses with a camera after its earlier, camera-less Echo Frames and Carrera Smart Glasses lines failed. (My guess is the problem was Alexa, not the lack of cameras.) Although its Echo Frames have been effectively discontinued — displayed as sold out online — the company is already testing AI glasses with cameras for enterprise use on hundreds of US-based Amazon drivers. 

Amazon Smart Delivery Glasses

Amazon Smart Delivery Glasses

Amazon

Huawei in April launched its AI Glasses for the Chinese market — the lightweight glasses sport a dual-engine AI architecture and integration with its HarmonyOS ecosystem. It’s joined there by Xiaomi’s AI Smart Glasses, which are powered by the company’s HyperOS ecosystem and have cameras for photos and videos and for for reading QR codes. 

Beyond those well-known firms, other companies are making daily-wear AI glasses with cameras in them, including XREAL, Rokid, TCL, Solos, and Brilliant Labs.  

A minority of other companies is focused on glasses without cameras, including Even Realities (G1 and G2); MIRA (MIRA glasses); Dymesty (Dymesty AI glasses); Lucyd (Lucyd Lyte); and Huawei (Eyewear 2).

Get the picture?

Clearly, by the end of the year, the market will be flooded with all manner of AI glasses designed for everywhere, everyday wear. They can use prescription lenses or serve as sunglasses — and most of them will have cameras built in for photos, videos and multimodal AI. 

There’s just one problem: The public hates AI glasses with cameras.

Return of the ‘Glassholes’?

As we learned from Google Glass, a lot of people feel uncomfortable with a camera pointed at them while they’re talking to someone. And that backlash is back with the current generation of AI glasses. 

Because Meta is the market leader in the US, its Ray-Ban Meta glasses have borne the brunt of early disaffection. 

Texas Attorney General Ken Paxton recently launched a formal investigation into Meta’s AI glasses, calling them “a privacy nightmare for Texans,” claiming the devices “can easily invade personal privacy by collecting biometric data and recording Texans without their knowledge or consent.” 

Paxton also claimed the LED light on the glasses, which is designed to alert others that the camera is taking pictures or videos, can be easily defeated. In fact, some modders-for-hire charge up to $100 to physically destroy the LED and TikTok videos describe how to disable or cover the light. 

The pushback is happening elsewhere. Philadelphia courts banned smart Meta AI glasses with recording features from city courthouses and a petition is circulating to ban them from New York City bars and restaurants. MSC Cruise Line banned smart glasses in all public areas. And restaurants, gyms, and workplaces have begun banning smart glasses because of the camera. 

Uncertainty drives some of the concern. People don’t know whether they’re being recorded, and if they are, they don’t know who will see the video. It turns out, those  suspicions might be warranted. 

In February, Swedish publications Svenska Dagbladet and Göteborgs-Posten published an investigation that found Meta contractors in Kenya were reviewing footage from Ray-Ban Meta smart glasses — including “bank details, sex and naked people who seem unaware they are being recorded.” 

The New York Times published an internal Meta memo in February describing plans to add facial recognition (“Name Tag”) to Ray-Ban Meta glasses. The memo said the “political tumult in the United States would distract critics from the feature’s release.”

Then earlier this month, WIRED discovered dormant facial-recognition code called “NameTag” hidden inside Meta’s AI companion app. The code would let Ray-Ban Meta glasses identify strangers by face, a feature Meta publicly claimed “does not exist.” Meta quietly erased the code with an update one day after the exposé was published.

A coalition of civil society organizations wrote Congress to demand that Meta abandon its Name Tag facial recognition plans, calling it a “creepy and unacceptable escalation of surveillance.” The letter warned the technology could be adopted by law enforcement to surveil immigrants, people of color, and nonviolent protesters.

Finally, a range of reports involving AI glasses with cameras in them has emerged in recent months involving secret recording, harassment and extortion. 

The coming conflict over face cams

On one hand, all the biggest consumer electronics companies are either shipping AI glasses with cameras in them or planning to do so — and many smaller companies are looking to do the same. The industry expects AI glasses with cameras to go totally mainstream. 

On the other hand, a growing public, legal and legislative backlash has erupted in opposition to AI glasses with cameras in them. 

One possible outcome is that the public disdain for the cameras will fade, overwhelmed by widespread enthusiasm for the benefits they offer. A new social norm might emerge that mirrors the broad acceptance of everybody having cameras in their phones and pointing them in random directions. 

Another possibility is that companies will be forced by consumer disdain and legal action to abandon cameras in glasses and focus instead on AI glasses that can’t take pictures or use video for multimodal AI input. 

Either way, the war is surely coming. 

  •  

A warrantless wiretap law is about to expire — but surveillance networks aren’t actually ‘going dark’

WASHINGTON, DC - JUNE 09: Speaker of the House Mike Johnson (R-LA) holds a news conference following the passage a $70 billion legislation to fund immigration enforcement at the U.S. Capitol on June 09, 2026 in Washington, DC. The bill will fund Immigration and Customs Enforcement and the Customs and Border Protection agencies for the remainder of President Donald Trump’s term. (Photo by Chip Somodevilla/Getty Images)

Congress has failed to pass a three-week extension of Section 702 of the Foreign Intelligence Surveillance Act (FISA), with the House voting 218-198 against reauthorizing the controversial warrantless wiretapping authority through July 2nd. After a short-term extension earlier this year, the spying program now appears set to lapse for at least a week. This is the nightmare scenario FISA's proponents have been warning about - but it doesn't actually mean the US has lost its surveillance capabilities.

Proponents of a clean extension claim a lapse will hinder intelligence agencies' efforts to thwart potential terrorist attacks, with surveillan …

Read the full story at The Verge.

  •  

How to opt out of Google’s new AI training default

Heads-up, my fellow Android-appreciating animals: Google’s in the midst of rolling out a subtle change to its privacy settings that’s well worth your while to notice.

The change includes a new clause that says the company can use images, files, video, and audio from your interactions with Google Lens, Search, and Gemini Live to train and improve its AI models.

By default, that switch will soon be on and active for your account.

But with about 20 seconds of one-time effort, you can opt out and flip it off (both literally and metaphorically, if you’re so inclined) once and for all.

Lemme show ya how.

[Get level-headed knowledge in your inbox with my free Android Intelligence newsletter. Something new and useful every Friday — from my keyboard to your email.] 

Google’s new AI training privacy default

First things first — the nature of the change: According to Google, starting in the next few days, a new “Search Services History” section within the general Google account settings will lead to a significant-seeming policy shift. As per an email the company sent out to users this week:

Your media [will now be] saved when Search Services History is on. Saved media includes your images, files, audio, and video from your interactions with Search services to help improve your experience. … Your saved media is also used to develop and improve Google services and technologies, including AI models and safety measures.

Riiiiiiiiiiight.

Now, to its credit, Google does say the data will never be associated with your account or identity once it’s used for these purposes, and it’ll rely on “filters” to “automatically remove a broad range of identifying info or sensitive personal information.” But still, whether you’re working with important corporate info or simply put off by the idea of your personal media being fed into the AI training machine, this may be news you aren’t exactly thrilled to hear.

If you’re finding AI increasingly creepy or you’re just not so keen on knowing whatever media you submit to search-related services will be used to train and develop AI for the future, now’s the time to proactively speak up and change your Google account settings to shut down this setup before it begins.

That, unfortunately, is where things get slightly complicated — ’cause for most of us, this new Search Services History section doesn’t seem to be present and available just yet.

But that doesn’t mean you’re plum out of luck.

Your 20-second opt-out roadmap

To start on your AI training opt-out adventure, make sure you’re signed into whatever Google account you rely on for work and/or personal purposes, then head to the Google Activity Controls page and see if you see a section there called “Search Services History.”

If you do, this is especially easy for you: Just use the option right then and there to disable the “Save Media” setting within that section, which will stop any media files from being saved and used without eliminating the entire history of things you’ve searched. (If you’d rather eliminate all of your Google Search history from being saved and used even for your own future discovery and recommendations, you can also opt to turn that entire section off. Just be aware that it may have some wide-reaching effects on the personalization you see across a lot of Google services.)

If you don’t see that section — and, again, that appears to be the case for most of us at this point — you’ve got two options for the moment:

  1. You can completely disable all of “Web & App Activity.” Google says if you do this, once your account transitions over to the new approach, all of those “Search Services History” settings will stay off as well. Just be aware that doing so will prevent any and all search history from being saved for you from here on out — which, again, means you won’t be able to revisit your search history yourself and won’t see suggestions and personalization based on past searches throughout Google apps in the future.
  2. If you want to avoid entirely eliminating all of your search history, you can for now uncheck the boxes only for “Include voice and audio activity” and “Include Visual Search History.” That’ll stop search-related media from being saved to your Google account for the time being — though I’d also suggest setting yourself a reminder to look back at that same page once a week or so until you see “Search Services History” appear and can confirm that “Save Media” is unchecked as a result of that previous preference. Right now, Google isn’t explicitly saying that such a preference will carry over, so I’d put it on yourself to double-check and make sure (and then make the needed adjustment in the new interface, if not).

The choice is ultimately 100% yours — but in this case, it’s up to you to take action and opt yourself out if you aren’t comfortable with the default. It’s an unfortunate position to be put in, but now you at least know what’s happening and how you can make your own decision to take back control.

Find the tips and tools that’ll *actually* help you with my free Android Intelligence newsletter. No hype, no nonsense — just useful new stuff in your inbox every Friday, from one (alleged) human to another. 

  •  

Google will save your Lens photos, Search Live recordings, and Translate audio for AI training

Google is making some changes to how it saves your interactions with Search. In an email sent to users, Google says it will save the images, files, audio, and video you use to search under a new "Search Services History" setting.

That includes the images you search for with Google Lens, recordings from its real-time Search Live tool, voice searches, and phrases spoken into Translate, according to an update on the company's website. You can switch off the Search Services History setting and disable the "Save Media" option if you don't want Google to save these interactions.

Google says it will use your Search Services History to "provide, d …

Read the full story at The Verge.

  •  

What Safari reveals about Apple’s AI strategy ahead of WWDC

Apple’s latest Safari privacy campaign is more than pre-WWDC marketing. It is an early signal of how the company plans to frame artificial intelligence (AI): as something that only works if users trust the platform behind it.

The week before WWDC is often significant, as Apple tends to make announcements it simply can’t fit into the keynote itself. This year’s first pre-show reveal is a new campaign focused on privacy that shows how much more private Safari is than rival browsers; there’s even a highly entertaining video that makes the point.

Privacy on Safari

Apple has been building privacy protections into Safari for years. The browser protects you from malicious scripts that might attempt to access passwords or credit card information. Safari also tells you what data an extension wants to access and can restrict access to match your settings. It blocks third-party cookies by default, detects and removes trackers, and has measures in place to prevent data companies from identifying — and following — you through device characteristics. 

That’s even before Apple’s powerful Private Browsing mode, which includes meaningful protections. The company has put together a page packed with resources to explain the privacy protections it has in place across its platforms.

Privacy is critical to Apple — not only because the company regards it as a human right, but because it correctly recognizes that to make new generations of sensor-laden technologies it must ensure privacy is protected. Without privacy and trust, people won’t use the technology.

Trust is the product, not you

The truth is that people are becoming increasingly concerned about how the digital devices we depend on for convenience are now being used for different kinds of surveillance, and we need to be convinced that our personal data is protected. We do not want every aspect of our life to become fodder to feed a digital dystopia, even as we still want the positive solutions technology promises.

Think about the Apple Watch. Consider the data it gathers: distance walked, calories burned, and more — it’s a rich trove of personally identifiable data that no one really wants to share with others without consent. Apple Watch is not the only Apple device that is gathering information, even your web browser captures a great deal of it. Hence, the focus on Safari in Apple’s new campaign.

Privacy will become an even greater concern as AI spreads. Data brokering services already make extensive use of AI to analyze and identify patterns in the online data they harvest. AI deployed without strong privacy protections poses serious risks to the way we live, while the consolidation of AI ownership in the hands of a few companies risks creating dangerous imbalances of power. That’s the context in which private data needs to be protected, making privacy an essential component of a positive tech-augmented future. 

Why the AI era raises the stakes

Apple’s focus on privacy is far from new; it has been consistent in this work for many years. Competitors often accuse Apple of hypocrisy, but the company has been arguing for privacy’s importance for more than a decade. Others have adopted some of the same principles, though not all of them — and while Apple may sometimes use privacy as a moat for its own products and services, that does not diminish its value.

It’s with all this in mind that I consider Apple’s latest privacy ad campaign and its rollout just before WWDC, where it is expected to introduce new AI services. That Apple’s new privacy campaign seems not to have made the final cut for the show tells me the company has much more to discuss on the topic, particularly around Apple Intelligence.

What Safari’s signals suggest

When Apple introduces its new AI features at WWDC it will do so while celebrating the privacy built into them. The current privacy ad campaign will be part of an overall push as the company explains that its ecosystem can run third-party AI services while also offering its own bespoke Apple Intelligence AI to do really useful things in complete privacy.

This isn’t just a competitive moat, it’s a realistic assessment in practice. It shows that Apple understands that in the age of AI, privacy matters more than ever. As AI becomes central to everyday digital experiences, privacy is no longer optional — and Apple is prepared to make the case to support it.

You can follow me on social media! Join me on BlueSky,  LinkedIn, Mastodon, and follow The Core.

  •  
❌