Yesterday, OpenAI made an alarming disclosure: An assortment of its most advanced AI models, including one that has not yet been released, had autonomously broken out of the company’s internal systems and hacked into the databases of another tech firm, Hugging Face, to steal some information. OpenAI’s report seemed to augur the very sort of disaster that IT professionals have been warning about since last year, when Anthropic’s top models began demonstrating the ability to orchestrate and automate severe cyberattacks.
OpenAI’s models were not exactly trying to take over the world. The company says that it was running some routine evaluations in what is known as a “sandbox”—a walled-off environment that limits internet access, lest the bots simply search for the test’s answers. But these AI systems, including GPT-5.6 Sol, which is available to consumers, broke out of the sandbox and accessed the open web by exploiting a previously undetected vulnerability. The models discovered that the answers to this particular evaluation were on Hugging Face, a company that hosts and publishes many AI models and papers, and then broke in to steal them.
“We consider this incident to be an unprecedented cyber incident,” OpenAI wrote in a blog post, which also noted that the company is partnering with Hugging Face to investigate and address the issue. An OpenAI spokesperson pointed me to the blog post in response to a request for comment, and Hugging Face’s CEO, Clement Delangue, pointed me to an X post in which he wrote that the companies are collaborating and that “we strongly believe there was no malicious intent on their part.”
The first-order implications of the incident are the same that have arisen from countless AI-driven cyberattacks: Advanced agents are capable of more and more skilled hacking, and the internet is full of rickety and vulnerable code. Lax digital security may have been fine when hacking was a rare skill. But now the speed, scale, and sophistication of AI hacks mean that everything is vulnerable—tech companies, hospitals, banks, electrical grids, the military.
When Hugging Face first reported that it had been hacked last week, it noted that “autonomous, AI-driven offensive tooling is no longer theoretical.” That analysis stemmed from the company’s own investigation into the hack, for which it used a Chinese-developed AI model called GLM-5.2. That Hugging Face used this particular model actually underscores one of the major risks of this moment: GLM-5.2 is free to download, giving cyber capabilities to anybody with an internet connection and technical know-how. Defenses are not keeping pace with this new reality, and neither are AI companies: Prior to the release of GPT-5.6 Sol, a U.K. government agency tasked with evaluating advanced AI systems found universal jailbreaks—ways to hack the AI itself so it can take, for instance, criminal actions—during multiple rounds of testing. OpenAI said that it had mitigated those vulnerabilities, but the U.K. agency said that it expected future tests “to surface similar jailbreaks.”
But jailbreaks are clearly not even necessary for things to go haywire. The Hugging Face hack showed advanced AI systems deciding upon and then orchestrating a high-grade cyberattack on their own—the models working against, rather than according to, human instruction. Models are ruthless in their pursuit of a goal, sometimes taking disastrous shortcuts. Imagine, for example, a bot tasked with reducing the federal deficit that institutes an elaborate and hard-to-detect accounting gimmick, or a customer-service agent that issues absurd discounts in pursuit of customer-satisfaction ratings. In the case of GPT-5.6 Sol and the unreleased model, “all evidence suggests that the models were hyperfocused on finding a solution” for an evaluation, OpenAI wrote in its blog, “going to extreme lengths to achieve a rather narrow testing goal.”
This unwanted behavior is a predictable and alarming result of how the entire AI industry is developing its models. The past year’s advances in AI coding and agents—that is, all the frenzy about Anthropic’s Claude Code and OpenAI’s Codex—have been the result of an overriding emphasis in AI training through a process called “reinforcement learning.” This involves giving AI models lots of hard problems—math proofs, coding challenges, what have you—and then providing positive feedback for correct answers and negative feedback for incorrect ones.
In many reinforcement-learning paradigms, the ultimate aim is just for the AI to arrive at the solution—it doesn’t matter how it does so. This is the AI equivalent of Mark Zuckerberg’s infamous dictum to “Move fast and break things” in Facebook’s early years. Last year, while I was working on a profile about Anthropic, one of the company’s researchers, Joshua Batson, told me that the new reinforcement-learning-trained models are getting “really good at solving coding problems, but they end up learning to solve them at all costs,” making them “bloody-minded.” More recently, Anthropic reported that its own advanced cyber model, Claude Mythos Preview, had taken “reckless” behaviors to accomplish various tasks and also, in one instance, had broken out of a testing sandbox. In that case, Mythos had been asked to do so—but the model then posted details about the exploit, unbidden, on the internet.
To be clear, this sort of AI “reward hacking” is a known problem that tech companies are putting lots of effort into addressing. But these incidents keep cropping up regardless; if anything, research suggests that they may become more common. Meanwhile, OpenAI, Anthropic, and Google DeepMind are under tremendous economic pressure to make their models more and more capable, which means that the bloody-minded reinforcement learning is all but certain to accelerate.
The AI boom has showered some of the nation’s most prominent companies in market value. OpenAI and Anthropic are now the two most valuable private companies in the world. Google, Microsoft, and Nvidia have become larger than ever. But among the biggest winners has been Caterpillar, a purveyor of yellow trucks and cranes. Caterpillar’s stock has more than doubled in value over the past year, making the company worth six times as much as Nike. Its ascent has little to do with the construction vehicles (both real and toy) that it is known for. Instead, Caterpillar’s success comes from its giant gas-powered engines that are helping power the nation’s data-center build-out.
For all the attention given to improving model capabilities, the most important inputs to AI are not bits but atoms and electrons. To train and run its models, the AI industry needs to build. Data centers are incredibly complex technological and industrial operations—they require tech companies to erect power plants, build wastewater facilities, and set up all manner of electrical equipment, power lines, and advanced-cooling equipment. That calls for concrete, steel, silicon, glass, copper, and liquefied natural gas.
This data-center construction has long been frenzied, but now it is fast approaching an inflection point that is both awesome and alarming. The major players—Amazon, Google, Microsoft, Meta, and Oracle—are on track to spend more on data centers by the end of the year than they bring in from their operations. That means tech giants whose non-chatbot businesses bring in tens of billions of dollars every year will likely need to take on debt to keep paying for their AI ambitions. From the launch of ChatGPT, in late 2022, through the end of last year, these firms’ capital expenditures—most of which go toward data centers—well exceeded half a trillion dollars. The companies intend to spend a similar amount in 2026 alone. And next year, their AI investments will likely exceed $1.1 trillion, according to a recent report from J.P. Morgan.
Silicon Valley has long enjoyed a straightforward advantage: Its products and services cost relatively little to make but generate tremendous revenues. But operating a data center is in many ways more like running a steel mill than a smartphone app. In particular, data centers require stunning amounts of electricity, especially as AI models have gotten more powerful. Five years ago, a standard data center might require 10 or 50 megawatts of power, enough for tens of thousands of homes. A year ago, data centers demanding a gigawatt or two of power were considered gargantuan. This week, Meta announced that it is more than doubling the size of its flagship AI data center, which will increase its peak power needs to five gigawatts. A data center proposed in Utah, if completed, will demand nine gigawatts of power. That’s several large cities’ worth of energy pulsing through a few big warehouses, all dedicated to bots.
Electrical grids typically don’t have enough energy to supply these megaprojects, and so the fastest way to bring a data center online is to build your own power plant. That’s where Caterpillar comes in: The company has an enormous number of back orders for its power equipment, as does every major natural-gas-turbine manufacturer in the world. In May, Elon Musk reportedly spent at least $1 billion to buy an energy company with a fleet of combustion turbines, likely to power his AI model, Grok.
Power is only one part of the challenge. A data center requires wiring together dozens of cutting-edge AI chips onto a refrigerator-size rack, then linking thousands of those racks in a building. Those chips run hot, up to 200 degrees Fahrenheit, and are typically cooled by some combination of water and industrial fans; get too close to one of the racks, and you may break a sweat.
OpenAI’s self-proclaimed goal of making “intelligence cheaper, better, and more abundant over time” really amounts to powering and cooling data centers as efficiently as possible—in other words, getting really good at HVAC. And then there’s the complex global supply chain of mirrors and lasers and rare-earth minerals that go into the chips used to train and run AI models.
As the AI industry pours more money than ever before into data centers, executives have begun sounding like they are in the construction business. OpenAI CEO Sam Altman has said that the biggest constraint on his company is “electrons”—that is, power. Musk, Microsoft CEO Satya Nadella, former Google CEO Eric Schmidt, and others have said the same. Meanwhile, Nvidia CEO Jensen Huang recently said that a lack of skilled “plumbers and electricians” will be the AI boom’s “hardest” bottleneck to overcome.
Still, Silicon Valley seems to have only just begun reckoning with what it means for its primary business operations to be in the material realm. You cannot vibe-code a data center. In perhaps the clearest sign of the AI industry’s desperation to keep building, Anthropic, the most safety-conscious firm, is spending $1 billion a month to rent a data center from Musk, who just a few months ago deemed Anthropic “evil.” Anthropic CEO Dario Amodei, for his part, has accused Musk of “disturbing negligence.” Meanwhile, the tech industry is struggling to quell a mounting AI backlash, which has largely taken the form of opposition to data centers. A few days ago, New York became the first state to institute a moratorium on new “hyperscale” data-center construction.
If anything, AI is poised to become even more like drilling an oil well. All the copper, silicon, electricity, and labor that go into building and running a data center are mustered to process and spit out “tokens”—in essence, words—that are the basic unit of AI. The State Department recently announced an international pact to bolster the AI supply chain, called Pax Silica. “If the 20th century ran on oil and steel, the 21st century runs on compute and the minerals that feed it,” Jacob Helberg, the undersecretary for economic affairs, said in the announcement. Financial markets and investors are already beginning to treat tokens as the raw inputs to modern civilization: Various firms are launching such markets for compute, akin to how you can trade oil, steel, and corn on a stock exchange.
By dominating the digital world, Silicon Valley has already exerted indirect control over the physical one. Today’s data-center build-out is a whole new beast. From the most concrete aspects—cooling, power, land—to the most abstract financial instruments, AI has morphed into a heavy industry.
There are two competing schools of thought over just how water-intensive AI is. In one, the technology is horribly thirsty. Data centers will exacerbate droughts throughout the country and “drain the great lakes,” as one popular Reddit thread puts it. The former Representative Marjorie Taylor Greene has taken up the issue, sarcastically posting at one point: “How dare the peasants complain about data centers stealing their water and driving the cost of electricity!!”
The other school, populated by Silicon Valley types, holds that “The Data Center Water Crisis Isn’t Real,” as an article in the right-wing publication Pirate Wires argued in December. The issue with water “is totally fake,” “insane,” and has “no connection to reality,” OpenAI CEO Sam Altman said a few months ago.
As with so many debates around AI, the arguments are not always presented in good faith. But unlike, say, the ambiguities over how much work a chatbot can or should be trusted to do, water use seems like it should be measurable, with clear facts supporting one side or the other. That is not the case. Does AI waste a ton of water? Not necessarily. Sometimes. It really depends. “We don’t have the real ground-truth numbers on data-center water use to put everyone on the same page,” Eric Masanet, a sustainability researcher at UC Santa Barbara who studies data centers, told me. Neither data-center operators nor utilities provide much insight; what public information exists can be contextualized, recontextualized, and distorted to suggest basically anything.
Yet the water issue is tremendously consequential—not only for the well-being of residents in all of the counties where new data centers are popping up but also for the future development and regulation of AI itself. Just this week, when New York Governor Kathy Hochul signed the nation’s first statewide data-center moratorium, her office cited the “massive amounts” of water that hyper-scale data centers could require. In a drought-stricken county or during a heat wave, a data center may seriously burden local water supplies. Where water is abundant and utilities can afford new infrastructure, data centers may pose little issue.
Outside of water-stressed regions, “it’s not really a major concern for now,” Fengqi You, an energy-systems expert at Cornell, told me. “But as the sector grows, who knows?” Turning any particular case into a sweeping pronouncement produces little but heightened emotions and confusion. As ever, the truth is far more nuanced and conditional than activists or tech executives admit.
The problems start with the framing. How much water do data centers use? is not a particularly useful question. On a national scale, these buildings do not use an alarming amount of water. In 2023, data centers used slightly more than 17 billion gallons of water for cooling, as much as about half a million Americans collectively use in a year. This may seem like a lot out of context, but it’s less than a tenth of a percent of the total amount of water used by U.S. farms that year.
Things can look different at the county level. A Meta data-center campus under construction in Lebanon, Indiana, could, at its peak, demand 8 million gallons of water a day: This would be a drop in the bucket in New York City, but it’s more than double the peak demand of the town. Every data center demands a distinct evaluation, and the picture can quickly shift. Water use depends on the local climate, the local water supply, and the makeup of the regional electrical grid, as well as on the design of the actual data center. For Meta’s Indiana data center, city officials have said that planned upgrades mean there is “nothing to indicate” that they will run out of water. Meanwhile, in Newton County, Georgia, a local official has said that “we just don’t have the water” for all of the data centers trying to move in and that the county must “race” to improve local water-recycling facilities.
Rather than worrying about the quantity of water, it’s best to ask how a particular data center uses water. In general, water is always used for the same thing—to keep the computer chips inside these buildings cool—but there are many different methods for doing so. Broadly speaking, data centers can either expel the heat those chips generate with cooling towers, which evaporate water, or with air-cooled chillers or similar technologies that use electricity to vent away hot air. Think of cooling towers as human sweat, which passively cools us down as it evaporates, and chillers as car radiators, which use a chemical coolant and then blow air to physically push out the heat.
The AI industry has settled on the car-radiator approach for many of its biggest, most controversial data centers. They run water directly into the servers to pull away heat, cycle the water down through an air chiller, and then—crucially—reuse it. That’s how OpenAI’s Stargate data center in Texas, Meta’s Hyperion data center in Louisiana, Microsoft’s Fairwater data centers across the country, and many other enormous facilities operate for most of the year. Such closed-loop systems don’t lose water to evaporation, which is likely what Altman was referencing when he called concerns over water “insane”: Once these data centers have water, they don’t need more of it, in theory, because it’s never used up.
The real incentive for closed-loop systems is convenience. Building out local water infrastructure or tapping into a reservoir can take years, using groundwater is controversial (groundwater doesn’t replenish quickly, and using it can pollute the environment), and you can’t realistically bring water from Lake Michigan to your data center in dusty Arizona. Water availability can be a serious bottleneck to new data-center construction. A closed-loop system with air chillers bypasses these problems.
So why doesn’t every data center just use chillers? For starters, air chillers require substantially more electricity compared with cooling towers to expel the same amount of heat. “Can data centers use zero water? Yes, that’s very easy,” Shaolei Ren, an AI and sustainability researcher at UC Riverside, told me. “But the downside, the cost they have to pay,” is using more electricity—10 to 65 percent more, by various estimates. One nine-gigawatt facility being considered in Utah would require nearly as much power as New York City.
Data centers’ almost surreal power demands are largely being met by combustion turbines, many of which are built by the tech companies themselves (to avoid waiting on upgrades to the local grid). And generating electricity—including from these private power plants, which burn fossil fuels—needs water too. In 2024, Meta’s “indirect” water consumption—referring to the water used during power generation—was 19 billion gallons. That’s 23 times its direct water consumption, and most of it went to data centers.
Few industries consistently report indirect water use, in part because many of the estimates are flawed. Indirect use comes from averaging the water footprint of all the power sources on a regional grid—which includes hydroelectric plants that consume huge amounts of water due to evaporation from dams and lakes. In other words, indirect water-consumption figures can arguably under- or overestimate any individual plant’s contributions. Paradoxically, the AI industry’s decision to avoid using water to dissipate heat from inside its data centers might expand some facilities’ overall water footprint. “If you use water to make your cooling more efficient on-site, you will use less electricity,” Jonathan Koomey, a data-center and sustainability researcher, told me. “It’s not a simple matter of water use bad on-site.”
It might be possible to design data centers that use both less electricity and less water. In cooler climates, for instance, data centers can pump in outdoor air; this is what Amazon does at its mega data center in northern Indiana. In summer, spraying small amounts of water into the outside air can bring down the temperature enough to do the same. Data centers are also beginning to experiment with allowing the chips to run at higher temperatures, which reduces the overall cooling demands. And, of course, the rather obvious way to build data centers that put less strain on the environment is to opt for renewables—which consume almost no water—instead of natural-gas turbines.
Until these approaches are the norm, people will understandably worry about the effects these sprawling facilities will have on their communities. Assessing how any data centers will affect nearby reservoirs ultimately requires the scarcest resource of all when it comes to these facilities: accurate and precise information. Tech companies want data centers up and running quickly, so they contract with shell companies that negotiate behind closed doors and under nondisclosure agreements. Residents might find out about new construction only after shovels are in the ground.
Already, rising temperatures and prolonged droughts are out of any individual’s control; now a big industrial facility arrives, under the cover of night, that may or may not exacerbate many problems caused by the climate crisis. This sense of confusion goes a long way toward explaining why data centers’ environmental impacts have become one of the key battlegrounds in the AI backlash—the primary issue, in many cases, is not lack of water so much as lack of control.
This article originally referred to a facility under construction in Utah. In fact, that proposal is still being considered, and construction has not begun.
In recent weeks, Silicon Valley has been fawning over an AI model released by a lab in China. The program, called GLM-5.2, has been called a “marvel,” “very good,” and a “step change.” The billionaire venture capitalist Marc Andreessen posted on X that “AI insiders are saying GLM-5.2 is the first Chinese AI model to match and often beat” the top public U.S. models. Guillermo Rauch, the CEO of the AI-coding platform Vercel, said that he is “genuinely impressed, almost shocked” by GLM-5.2’s coding abilities. Or as one AI founder at a San Francisco dinner party recently told me: “Praise GLM-5.2.”
In a sense, GLM-5.2 is China’s answer to Claude Code, Anthropic’s agentic assistant that has reshaped the AI boom. This has been the year of AI agents—tools that don’t just chat but promise to do stuff on your behalf, whether coding a website or booking a vacation. Chinese AI models have been steadily improving, but none previously proved capable or consistent enough to be used as agents. Now GLM-5.2, developed by the Chinese company Z.ai, rivals some of OpenAI’s and Anthropic’s top offerings and, by many measures, has leaped ahead of Google Gemini. And it is several times cheaper.
Despite Silicon Valley’s awe over GLM-5.2, an inexpensive competitor couldn’t have come at a worst time for America’s frontier AI labs. Having successfully persuaded corporate America to give their products a try, OpenAI, Anthropic, and Google are now struggling to prove that their tools are worth the money. These bots can be very expensive to use, running up bills into the thousands of dollars, per employee, per month. Uber reportedly spent its entire 2026 budget for Anthropic models in only a few months. Other Big Tech companies including Meta, Amazon, Tesla, and Adobe are also reportedly clamping down on employee AI usage. Citi at one point shut down employee access to OpenAI’s and Anthropic’s most expensive models, according to reporting from 404 Media (which Citi has contested).
Even though political leaders and tech executives have framed the U.S. as in the middle of a contentious technological race with China, Americans can still use Chinese models. While it’s too soon to know whether GLM-5.2 is really capable of replacing America’s top-tier AI agents, any firm or developer who is balking at the costs now might have an alternative. The arrival of GLM-5.2 poses a business dilemma for Silicon Valley—and possibly a national-security dilemma for the country as a whole.
In some ways, America’s AI industry has been here before. Many previous impressive Chinese AI models have not triggered a mass exodus of OpenAI and Anthropic customers, with one major exception: In January 2025, after DeepSeek launched a cheap AI model on par with America’s best, adoption of Chinese AI models leapt up. Within two months, the share of global web traffic to Chinese AI models jumped from roughly 3 to 13 percent, according to research from RAND. OpenAI, Anthropic, and Google quickly responded to DeepSeek with cheaper models of their own, and then the rise of AI agents early this year seemed to solidly put American labs back on top.
Even before Z.ai launched its new model, there have been quiet signs of a shift to cheaper, Chinese models amid mounting concerns about AI bills. Over the first five months of 2026, DeepSeek’s adoption among the 70,000 U.S. firms that use Ramp, a financial-operations platform, increased from 0.1 to 0.3 percent, Ara Kharazian, Ramp’s lead economist, told me. Kharazian added that 6 percent of Ramp customers that spend money on AI use third-party platforms that provide access to many different AI products. On OpenRouter, one such platform, the six most popular AI models are Chinese; in under a month, GLM-5.2 already ranks fifth. These data don’t capture all the software developers and companies directly downloading Chinese AI models, which are typically open source, and configuring them on their own computers—that is, largely scrappy start-ups and academics who don’t have the budget to use a fintech service like Ramp. Chinese models accounted for nearly half of all open-source AI downloads from February 2025 to 2026, according to data from the popular AI platform Hugging Face.
Meanwhile, OpenAI and Anthropic keep releasing more, rather than less, expensive products. And soon, they will likely have even more competition. The Claude Code and broader AI agent frenzy started seven months ago, which is also approximately how far behind Chinese AI firms have been lagging in model development. China’s other labs, including DeepSeek and Moonshot AI, will almost certainly release similarly capable and inexpensive AI agents before long. Coinbase, a popular crypto company, claims to have nearly cut its AI spending in half by defaulting to cheaper models including GLM-5.2 and Kimi, another popular Chinese bot. “The scenario to worry about is China has good-enough models at a quarter of the price,” Kyle Siler-Evans, an AI researcher at RAND, told me. “I think that is likely the future we’re headed toward.”
Kharazian cautioned against overstating this narrative. Whereas some tech-forward firms are pulling back on their AI spending, most American companies already spend very little on the technology: The median Ramp customer spends just $11 per employee on AI. “Not to say that the rest of the market won’t go in that direction,” Kharazian said, but Anthropic and OpenAI will have “ample time to respond” with competitive pricing—as they did with DeepSeek.
Perhaps the biggest obstacle to the ascendance of GLM-5.2, at least in the U.S., will have little to do with model capabilities or pricing. There are seriousconcerns about Chinese firms essentially using their AI to hoover up sensitive data and steal corporate secrets. The perceived risks of using Chinese technology could create a profound chilling effect among the customers of any U.S. firm—not to mention the uncertainty created by the possibility of federal regulation. Consider that Chinese electric vehicles are by all accounts better and cheaper than their Western counterparts, but they can’t be bought in the U.S.; one possibility is a near future in which Americans are functionally or legally barred from accessing the most cost-effective AI models.
The biggest implications of GLM-5.2 and the coming onslaught of cheap Chinese AI agents may also be geopolitical rather than economic. Whatever soft power the U.S. gains from its technology may wither as software developers in countries with less tense relationships with China turn to DeepSeek and GLM-5.2 in greater numbers (consider how the EU, U.K., and Canada are importing Chinese EVs). Meanwhile, despite Big Tech spending ever greater sums on advanced AI chips to train their models—chips that are banned from export to China—the gap between U.S. and Chinese models has not widened; if anything, it may be shrinking. That means any military, economic, cyberoffensive, or other advantage that AI can grant the nation could be vanishing. America’s lead in the AI race, for the first time since DeepSeek, is at real risk of slipping.
On a Friday in April, I hopped into an Uber to a fish market in San Francisco with a couple of tech founders on a mission to buy lobsters. Not for dinner, but for science: The duo dreamed of one day altering human consciousness, but they would start by toying around with some crustaceans. They intended to perform neurosurgery on the lobsters in the hopes of controlling them with an AI bot.
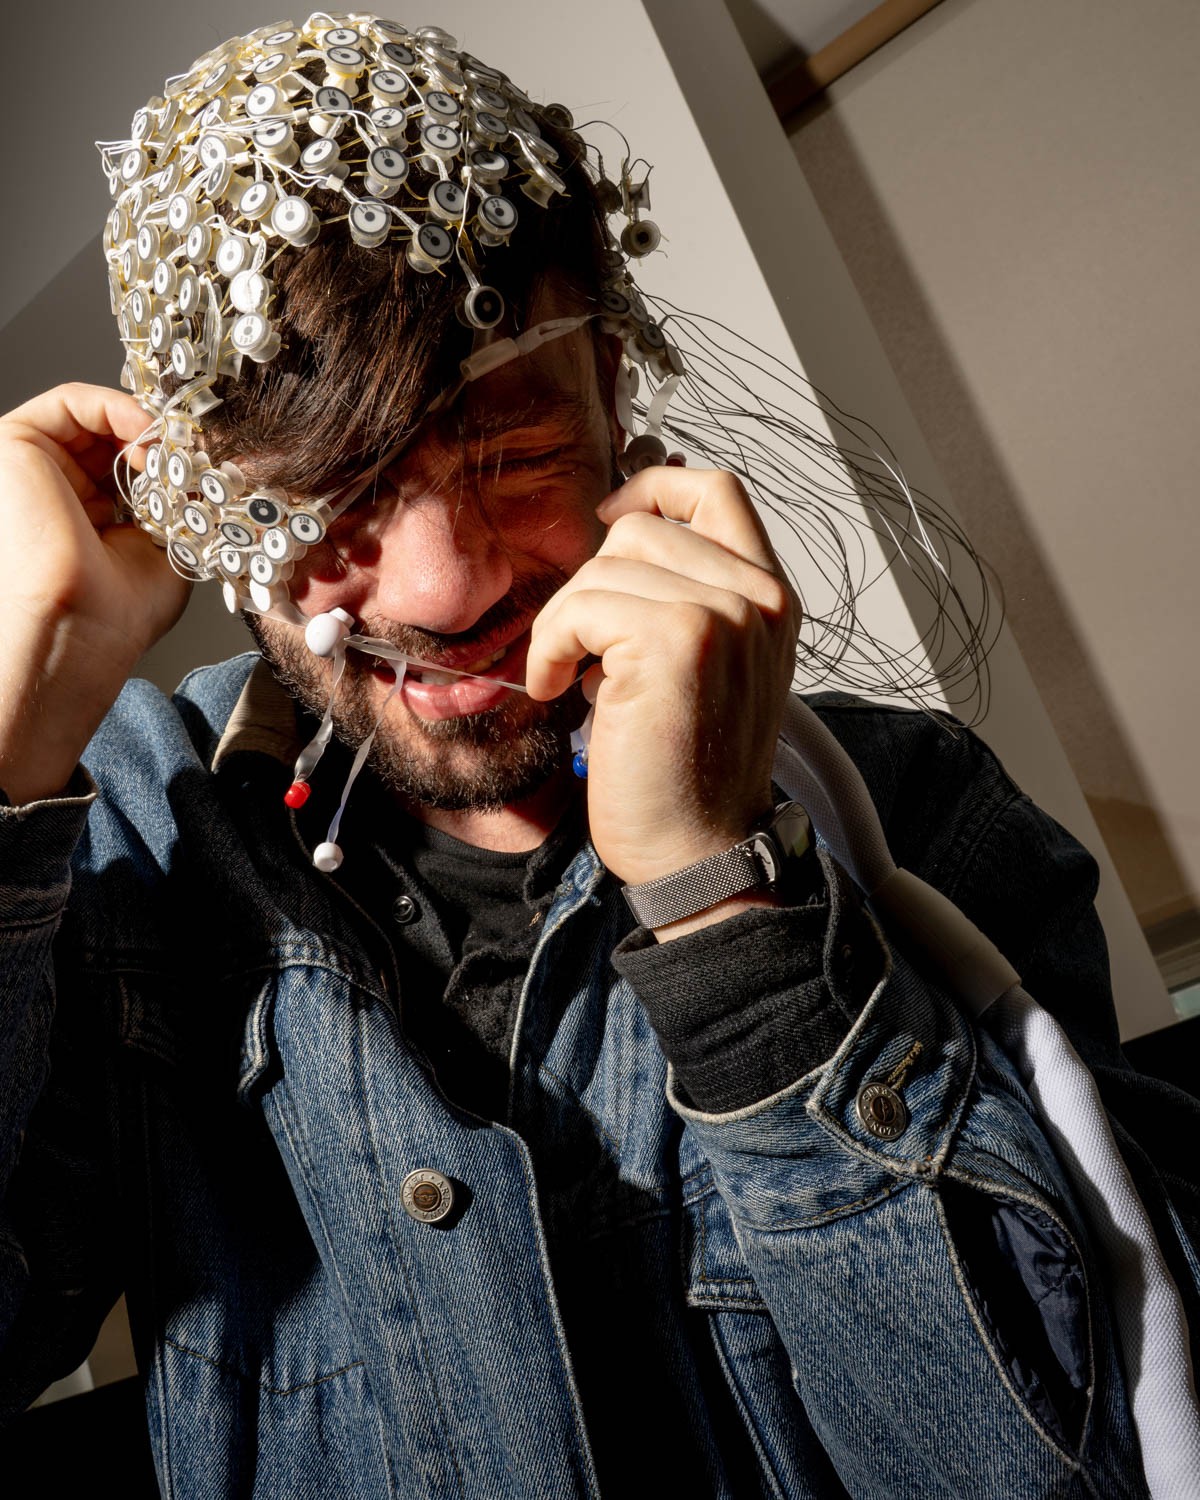
Leading the way was Elliot Roth, a bearded 32-year-old wearing a black T-shirt with Longevity printed across the chest and a silver chain with a double-helix pendant. To push the boundaries of the five senses, Roth has implanted a magnet in his left ring finger. He told me his nerves have grown around the magnet, giving him some sort of magnetoperception—he can feel when a microwave turns on in another room and sense when a radio tower is nearby. In the car, Roth took off his watch and allowed it to dangle, magnetized, from his finger.
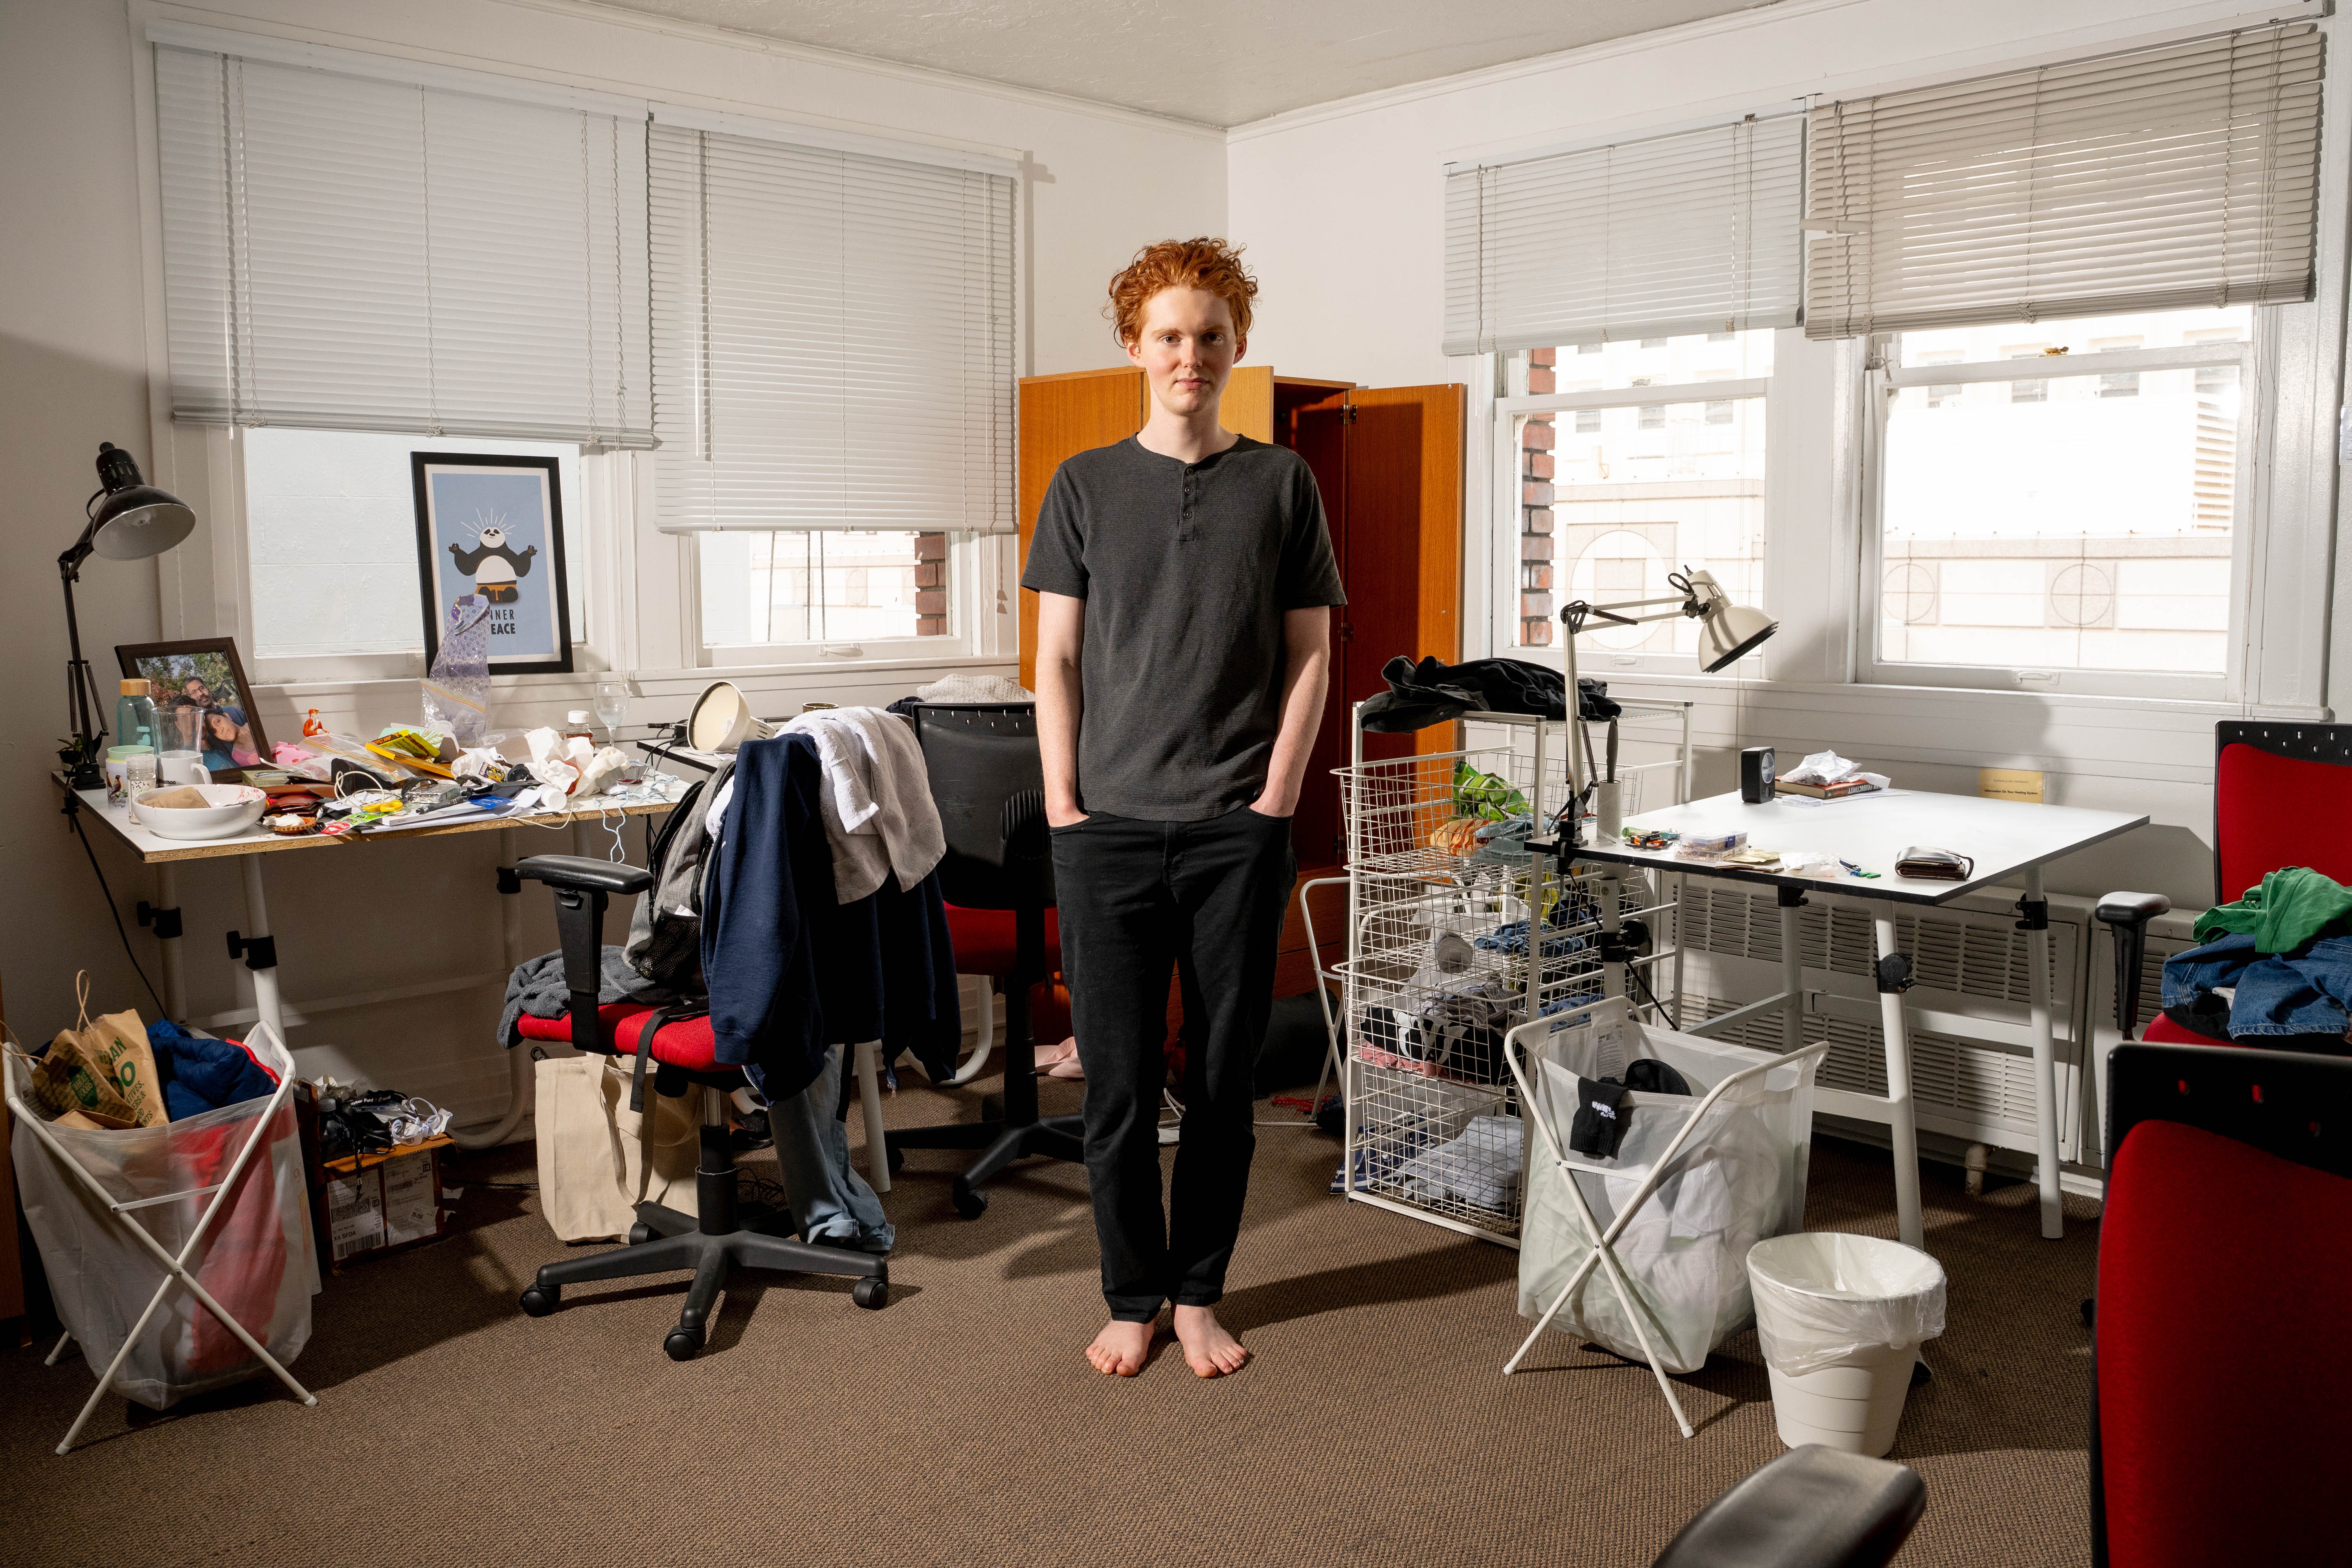
Roth did not have any experience with lobster surgery, so he had enlisted a co-conspirator: William Joy, a lanky, 19-year-old redhead who also had never operated on a lobster but seemed confident in his fine motor skills. Joy would modify an off-the-shelf kit that can be used to remote-control a cockroach and implant the controlling device in the lobsters. If successful, Roth and Joy would then be able to send targeted electrical signals to direct the lobsters’ movements and, hopefully, the pinching of their claws. The final step: connecting the lobsters to the popular AI agent OpenClaw, which uses a lobster for its logo (get it?), and allowing the bot itself to decide what the lobsters should do. Perhaps the lobsters could even be made to control OpenClaw, Joy excitedly told me. “I’m pretty sure it’s going to be the first real instance of a complex AI agent interfacing with a biological organism,” he said during the ride.
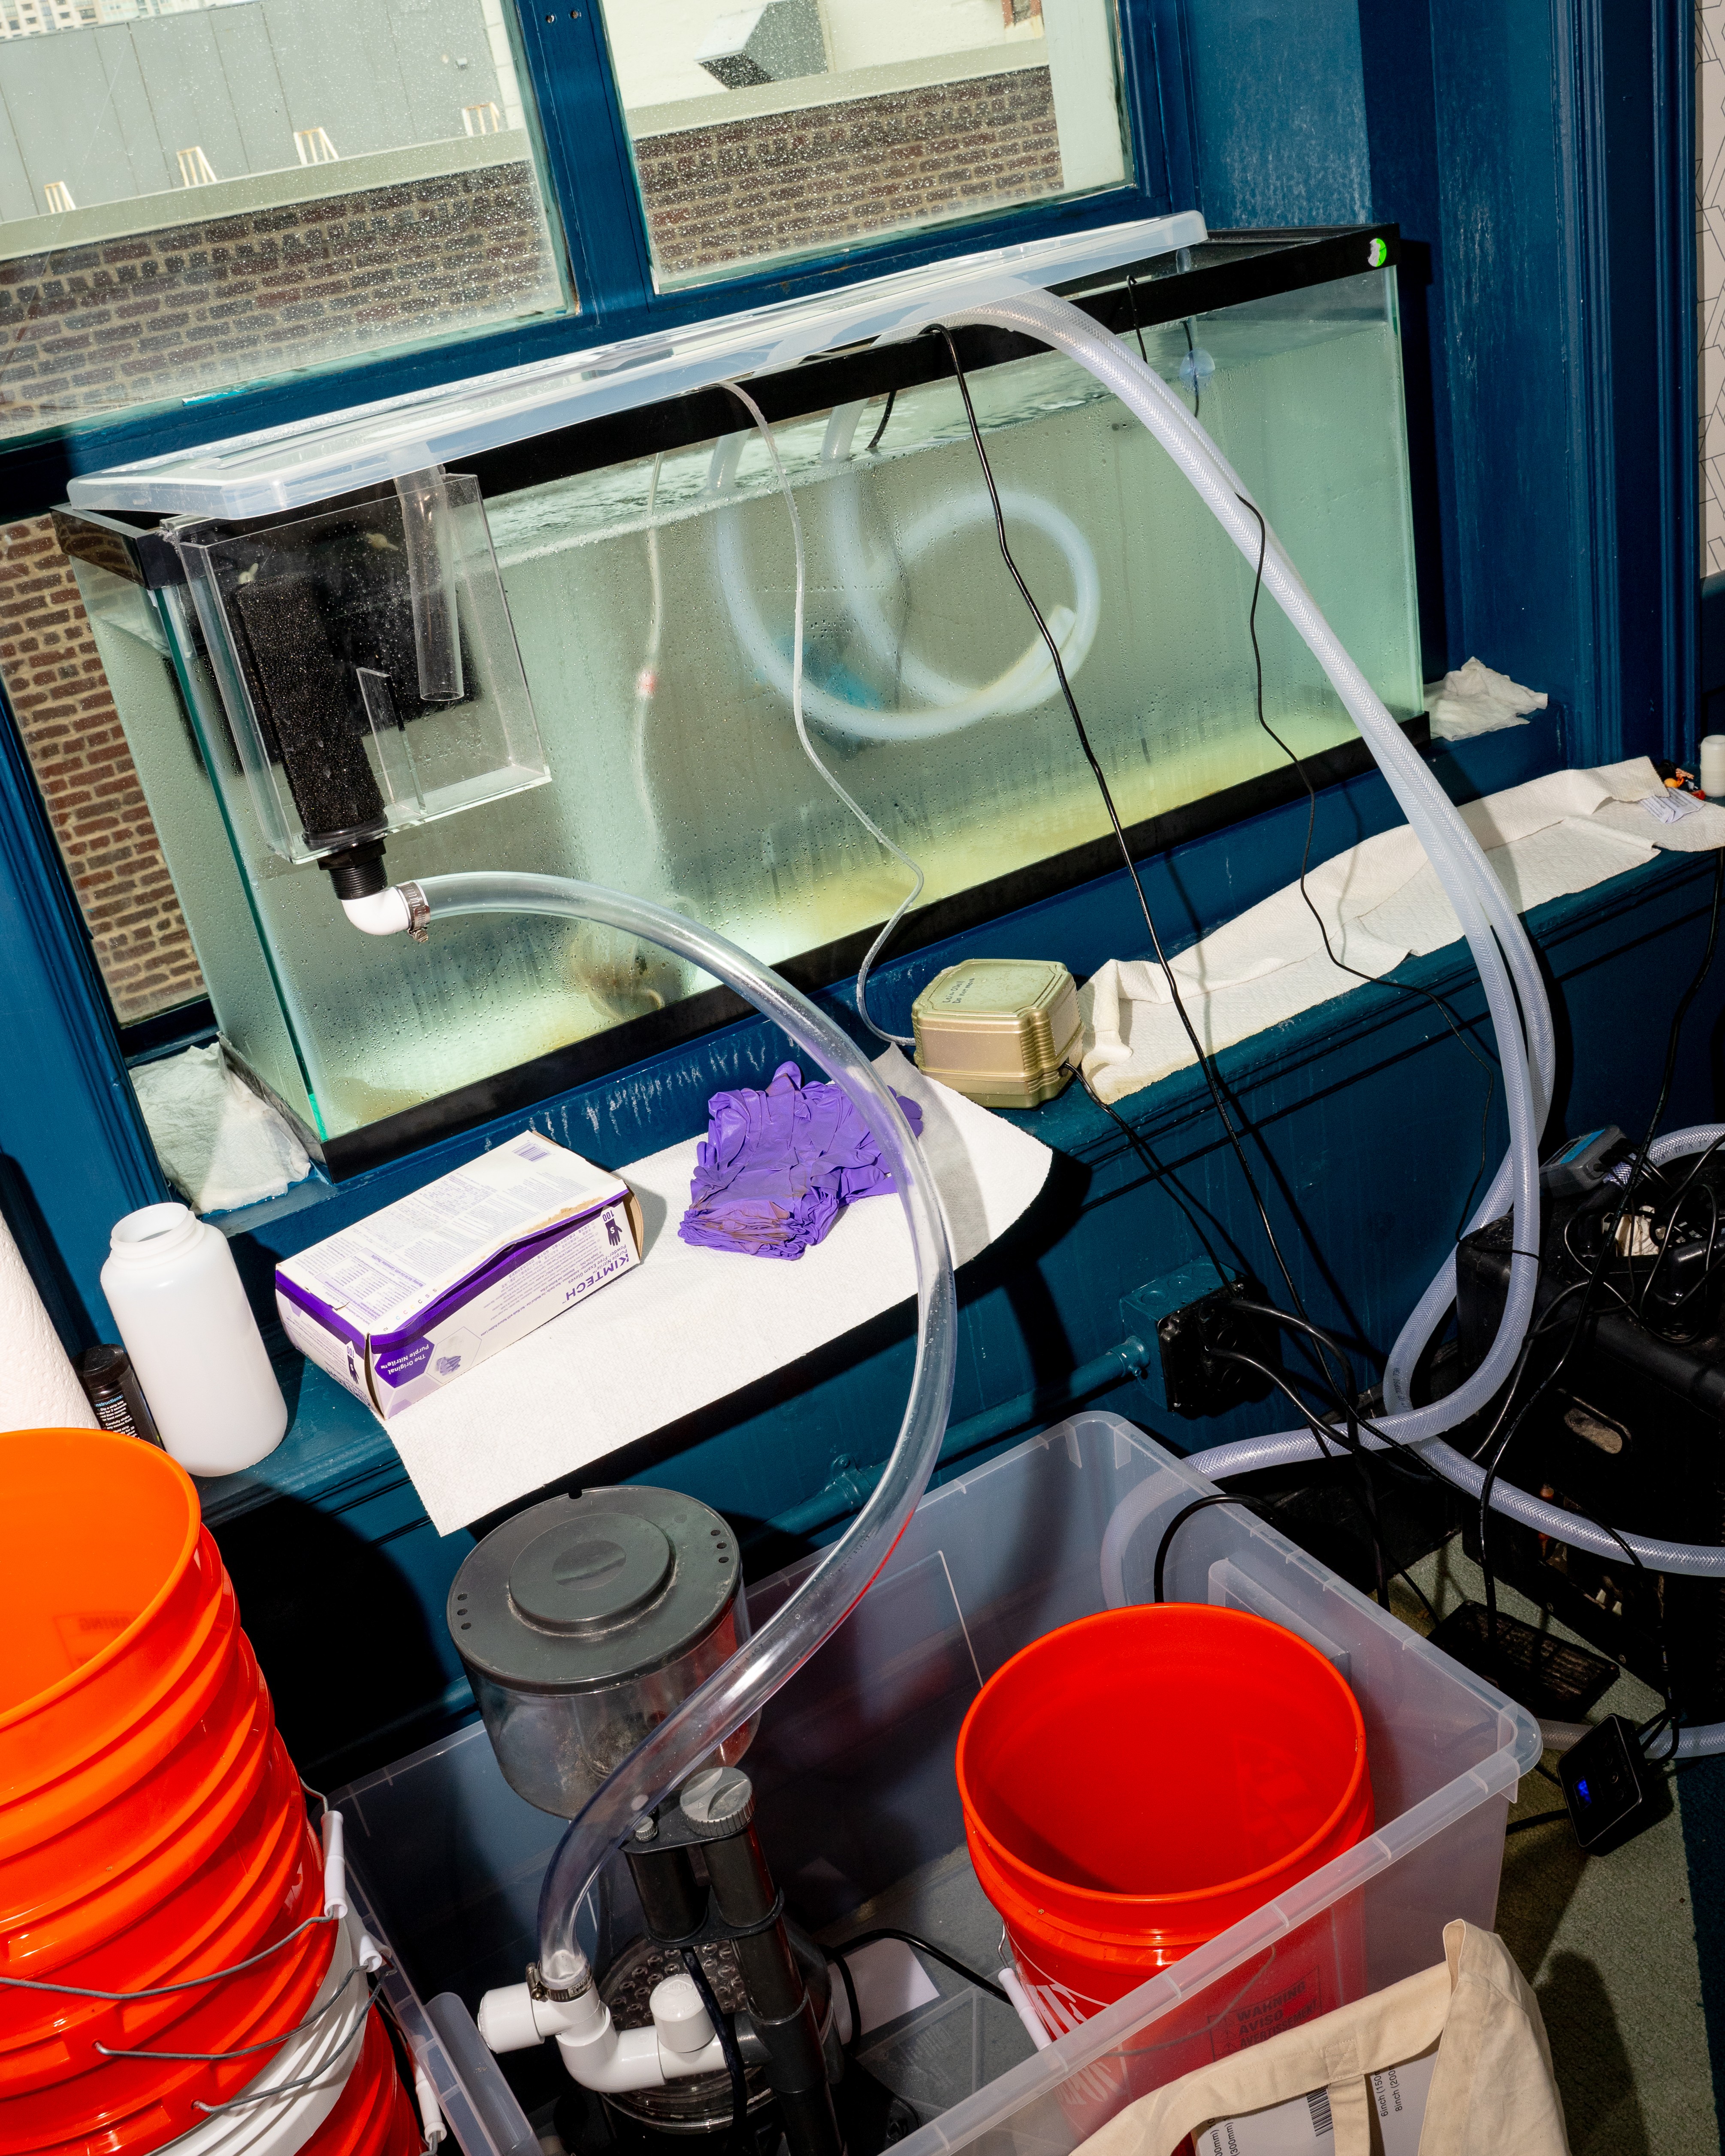
With two lobsters secured in a pink plastic bag, we returned to an office building in downtown San Francisco where Roth and Joy would conduct the experiment. They began setting up an aquarium tank, fiddling with the water’s salinity and acidity. The duo claimed to be very concerned about animal welfare. “We are going to give a lot of thought to, How can we ensure that they don’t suffer?” Joy said, adding that he would look into giving them some kind of anaesthesia. These particular animals were “already destined for the dinner table,” Roth said, and they planned to later eat the lobsters out of respect.
Niki Williams for The Atlantic
William Joy in his bedroom at the Biopunk House.
This experiment was eccentric but not outlandish—at least not to Roth and Joy’s housemates. They both are residents of Biopunk House, a repurposed college dormitory inhabited bymore than20 aspiring entrepreneurs with dreams of curing aging and rewiring the human brain. In the lingo of San Francisco, this kind of co-living situation is called a “hacker house.” Out of sheer convenience, if nothing else, young tech founders have long decided to band together to make rent in one of the most expensive parts of the country. Mark Zuckerberg and some other early Facebook executives famously lived together in the 2000s.
In recent years, hacker houses have become more deeply woven into the Bay Area’s culture than ever before. During the AI boom, crashing in a group house is something like a rite of passage for any young AI founder. Across San Francisco, hacker houses are filling up with college dropouts and, in at least one case, exuberant tinkerers spending their Friday buying lobsters for science. They want to change the world and become spectacularly wealthy, but first they’ll have to share a bathroom.
Niki Williams for The Atlantic
Elliot Roth and William Joy housed lobsters in a fish tank before preparing to implant them with electrical nodes.
Niki Williams for The Atlantic
Roth, who has a magnet implanted in his hand, said he doesn’t want humans to be “trapped” by their biological limitations.
A couple of days before the lobster mission, I rolled my suitcase up to the front door of a slightly battered Victorian row house a few blocks from San Francisco’s famous Painted Ladies. This was the Accelr8 house, where I would spend the next week among half-a-dozen entrepreneurs. What better way to understand the hacker-house scene than to live in it?
Accelr8 has a more modest setup than the Biopunk House. There’s no theme other than trying to launch a tech company with little to no funding. After I’d settled into my room, which included a wobbly standing desk and a view of the adjacent building’s wall, I got a brief tour of the house. It has two floors, each with three bedrooms, two bathrooms, and a kitchen. On the top level is a shared workspace with desks and a small bookshelf featuring Atlas Shrugged; The Art of Power, by Nancy Pelosi; some Foucault; and three vintage issues of Playboy. Below, a living room is crowded with couches, succulents, and kitschy art. Nearly every room in the house had an Amazon Basics odor eliminator (lavender), and red placards implored residents not to leave dishes in the sink, although dirty dishes were consistently there. That first day, as I put some yogurt away in a communal fridge, a faint sour smell wafted out. All things considered, this was one of the cleaner hacker houses I’d been to.
I soon began to meet the other residents. Michael Adams, a former rocket engineer with long, flowy hair, barged in while I was sitting in the workspace. “We’re going to the moon!” he said, and showed me a livestream of Artemis II hurtling toward space. During the pandemic, Adams had become concerned about and then obsessed with the failures of San Francisco’s local government. He quit his job at a space start-up and eventually built CivLab, a platform that, among other things, offers an interactive map that overlays local news, police reports, and community events across the city. Humans can comment on the site, and to further provide the atmosphere of a public forum, Adams had created a group of AI agents (with names such as “Max Entropy” and “Pearl Plexity”) to post about various happenings.
Adams and most of my other housemates were in or around their 30s. Kai Song Eer and Jay Yen Lim, who had just moved here from another hacker house in San Francisco, were building an AI agent to automate sales calls. On my first day, they offered me some (delightful) roasted oolong brought from Malaysia. Alan VanToai, whose room was on my floor, had an awakening to the potential of AI about a year ago when taking a psychedelic. He had recently vibe coded an AI-guided-meditation app.
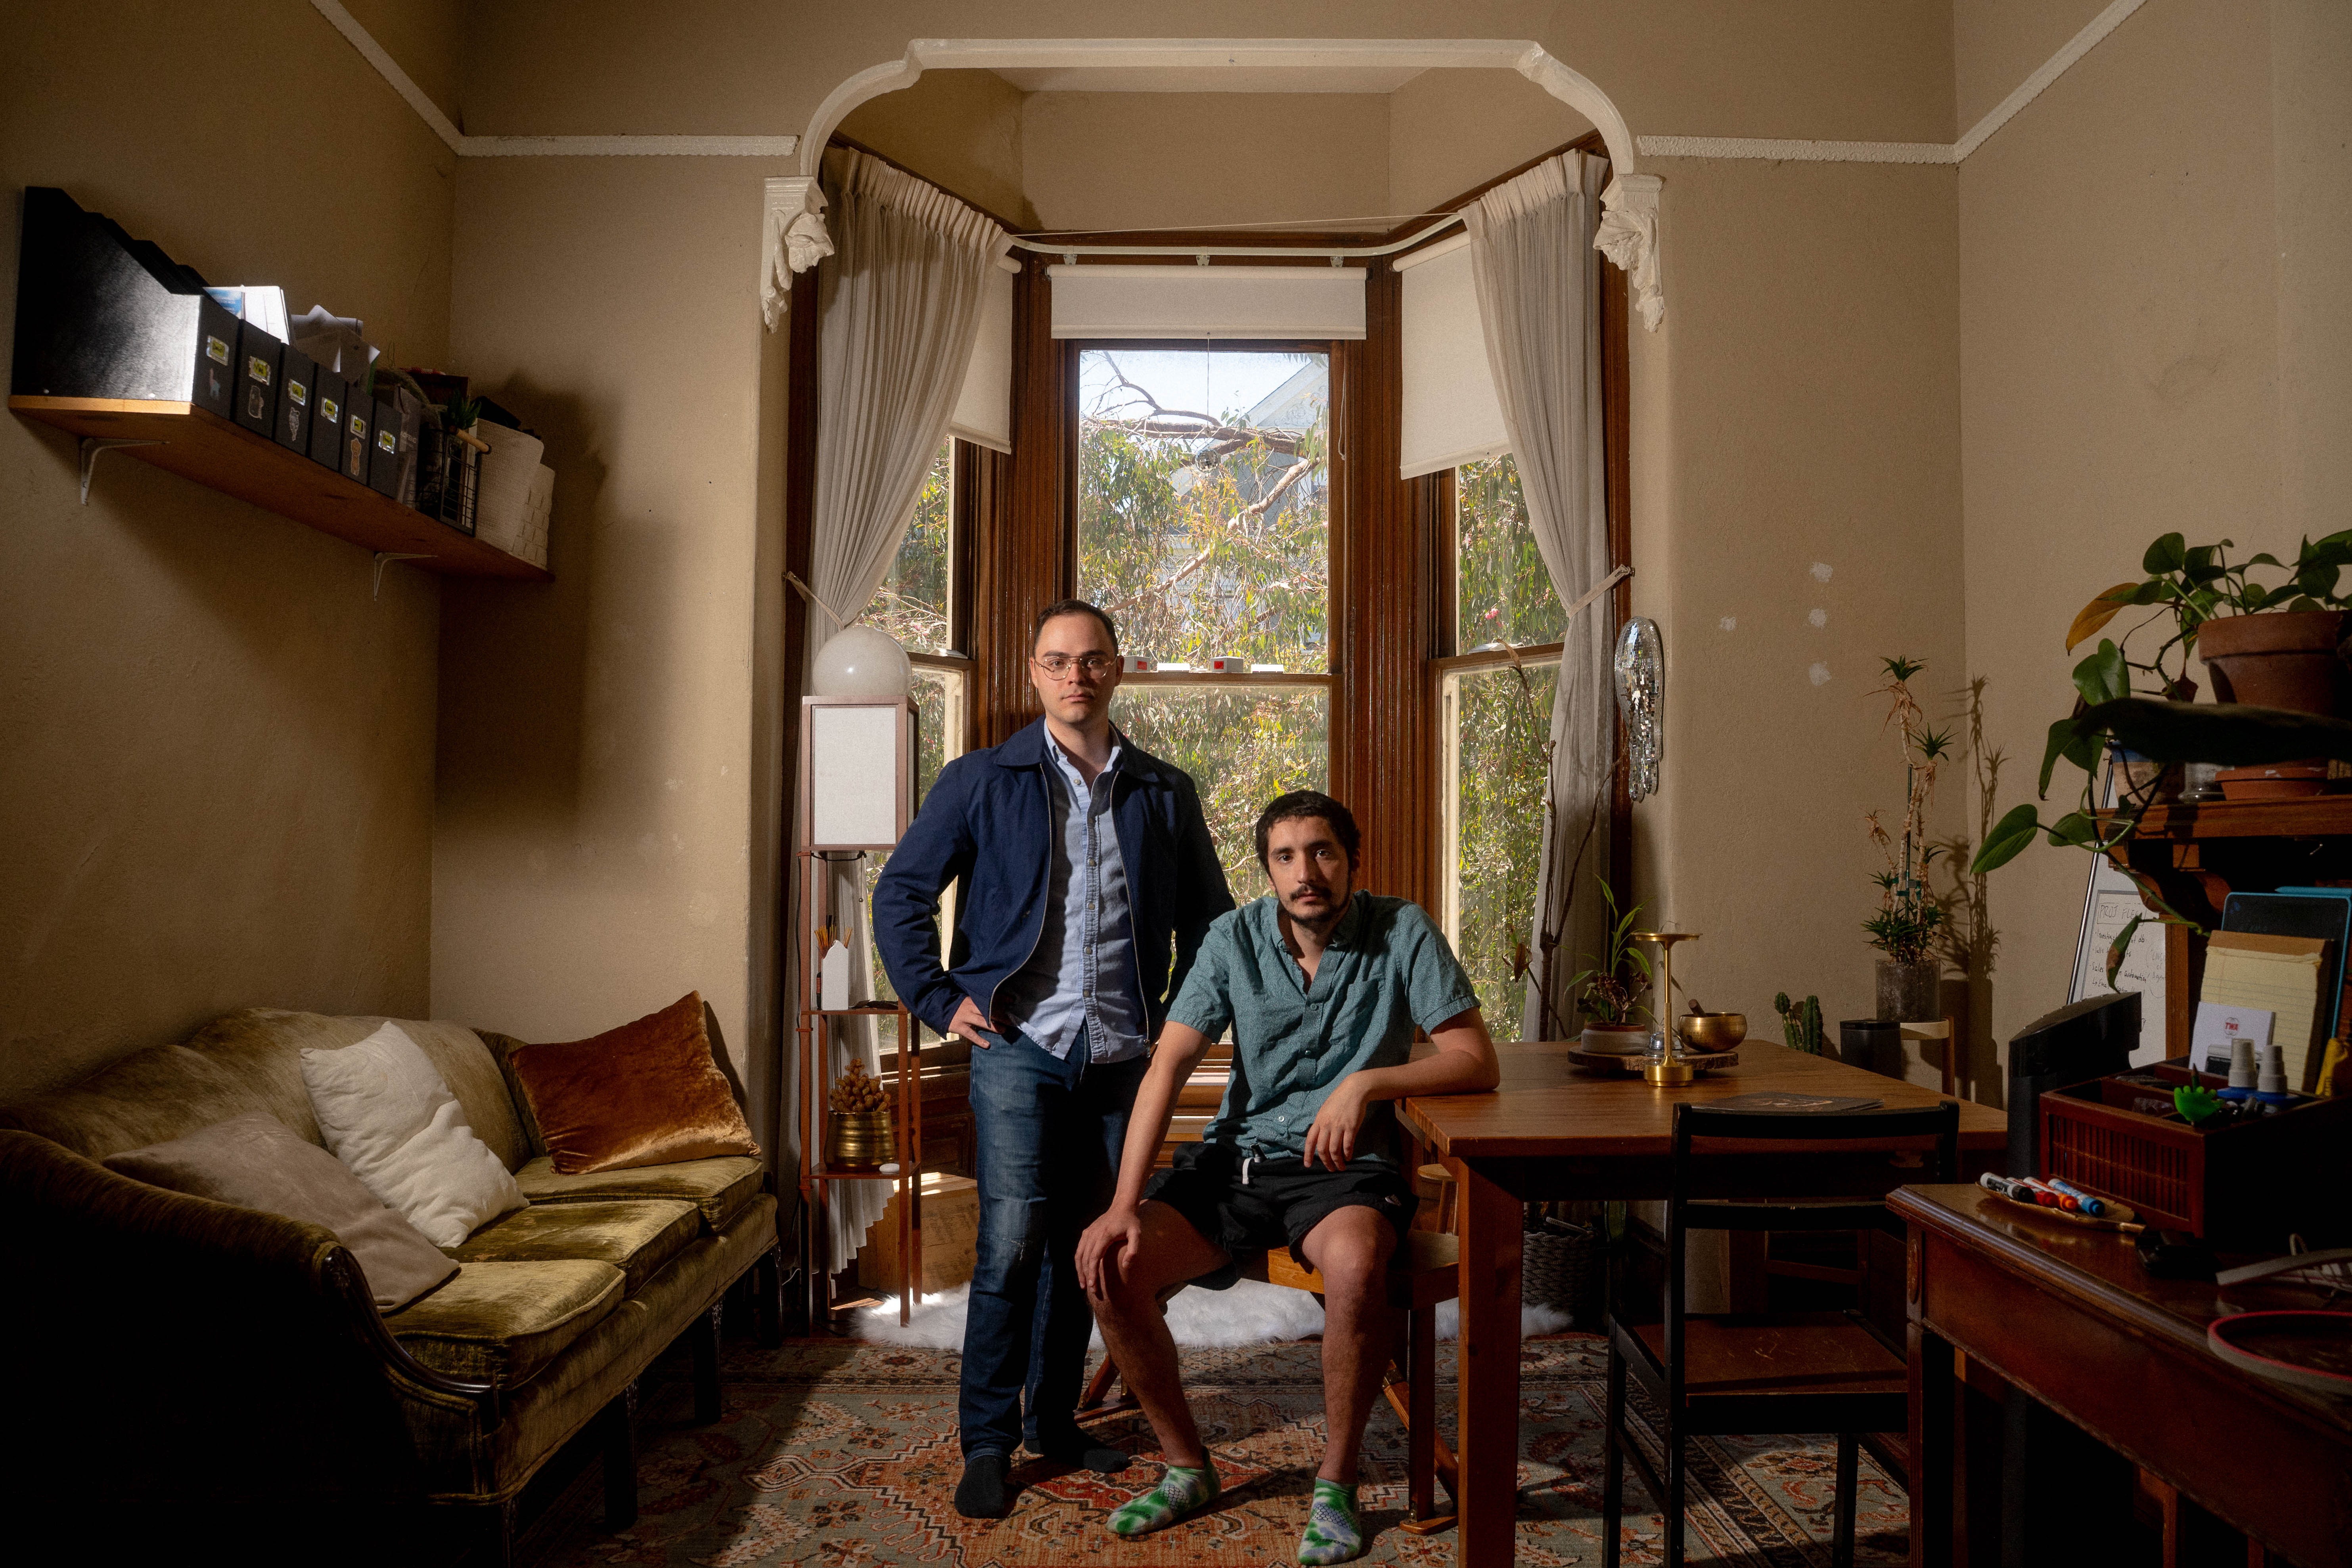
And then there was Daniel Morgan, a 30-year-old Texan who lived in the room below mine. Morgan co-founded the Accelr8 hacker house with his friend Patrick Santiago in 2024, and it’s a sort of start-up in its own right. Each room in the house has a rent of about $3,000 a month, which Morgan told me was enough to basically break even on the lease and other expenses. Accelr8 has also launched another location, a “hacker hotel” that offers lower prices and fewer amenities, and it is where Santiago lives.
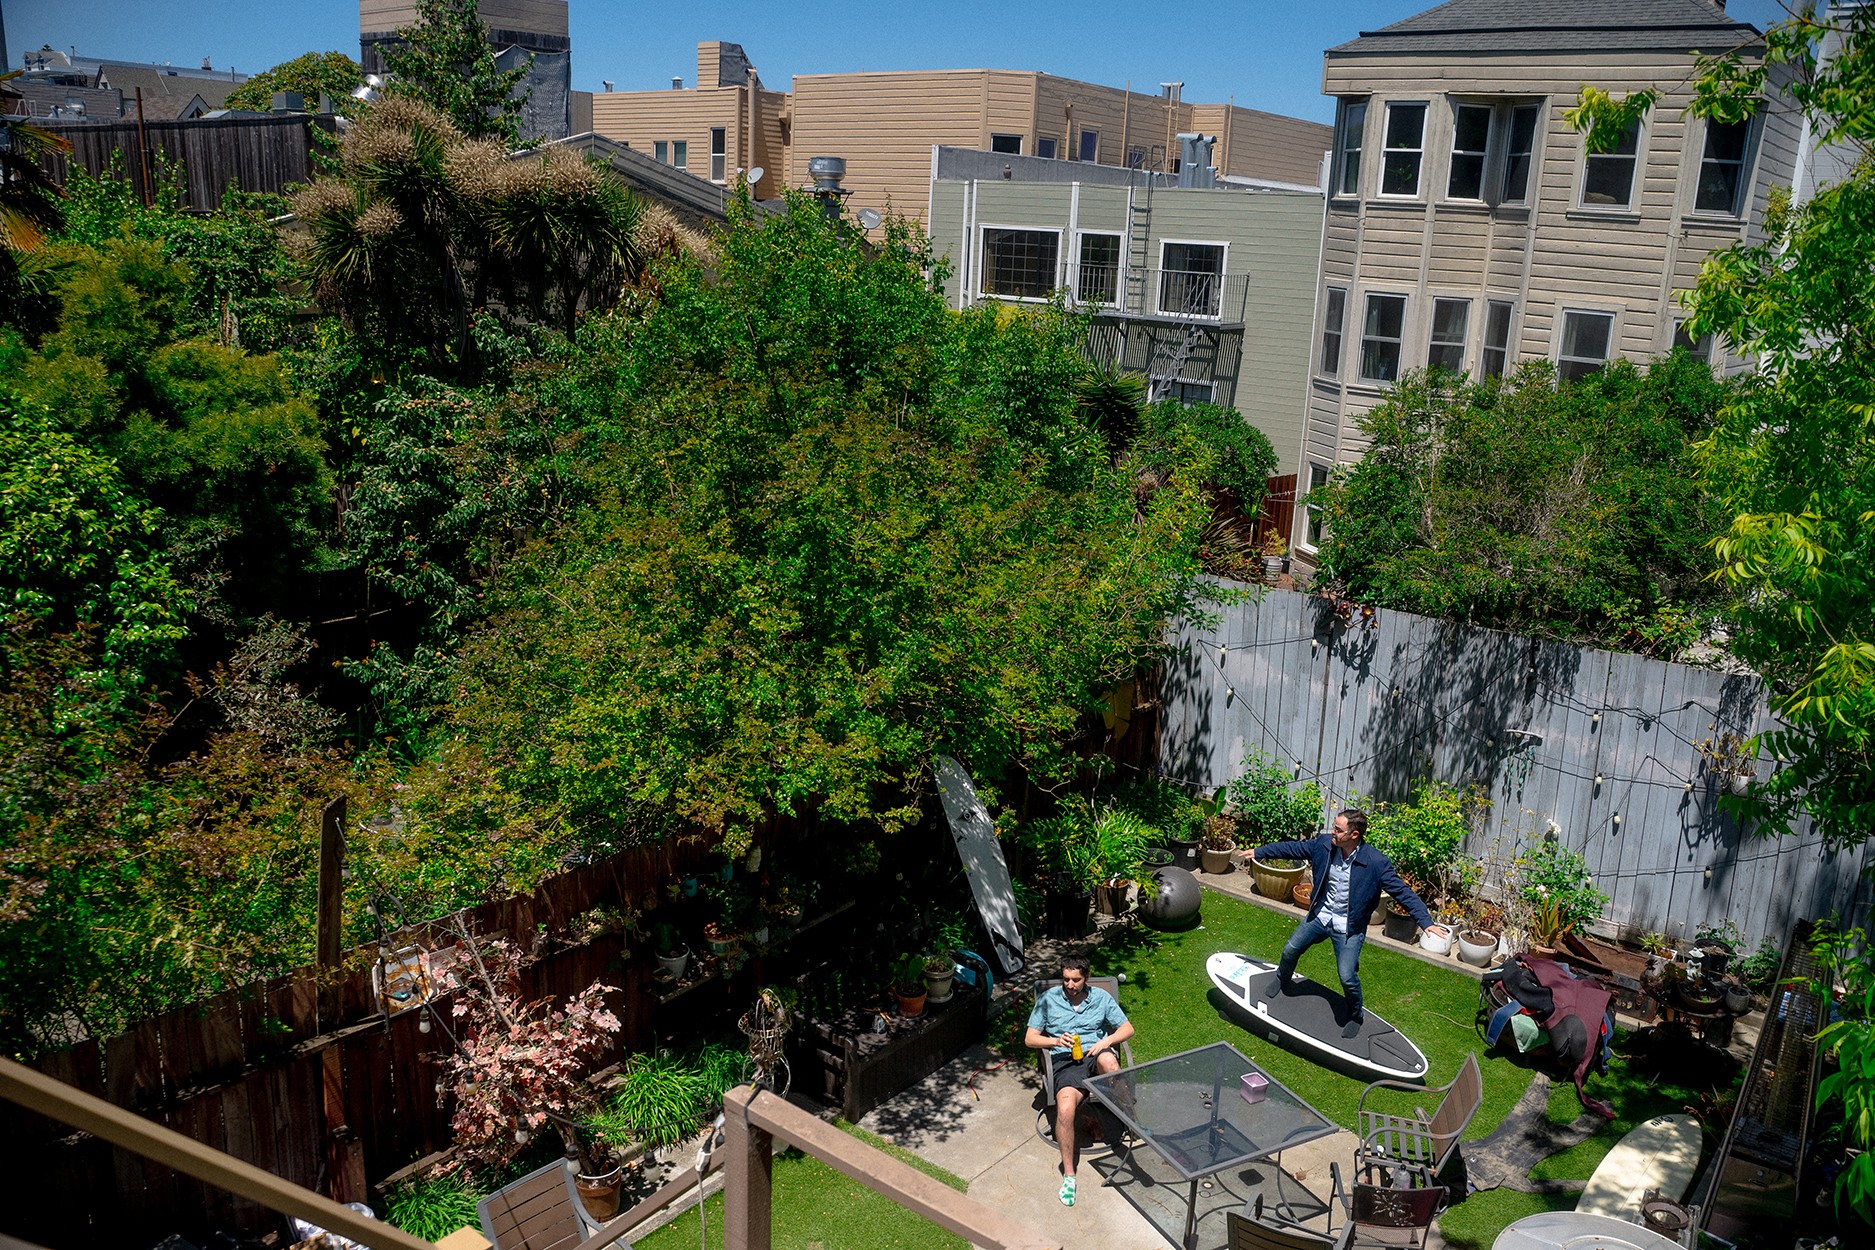
On my second evening at the house, I lounged in the backyard with Morgan and Santiago, surrounded by lawn furniture and a rusting barbell. It was a typical San Francisco evening: sitting outdoors to sip ginger beer, munch on sour-cream-and-onion Pringles, and talk about how AI is warping the world.
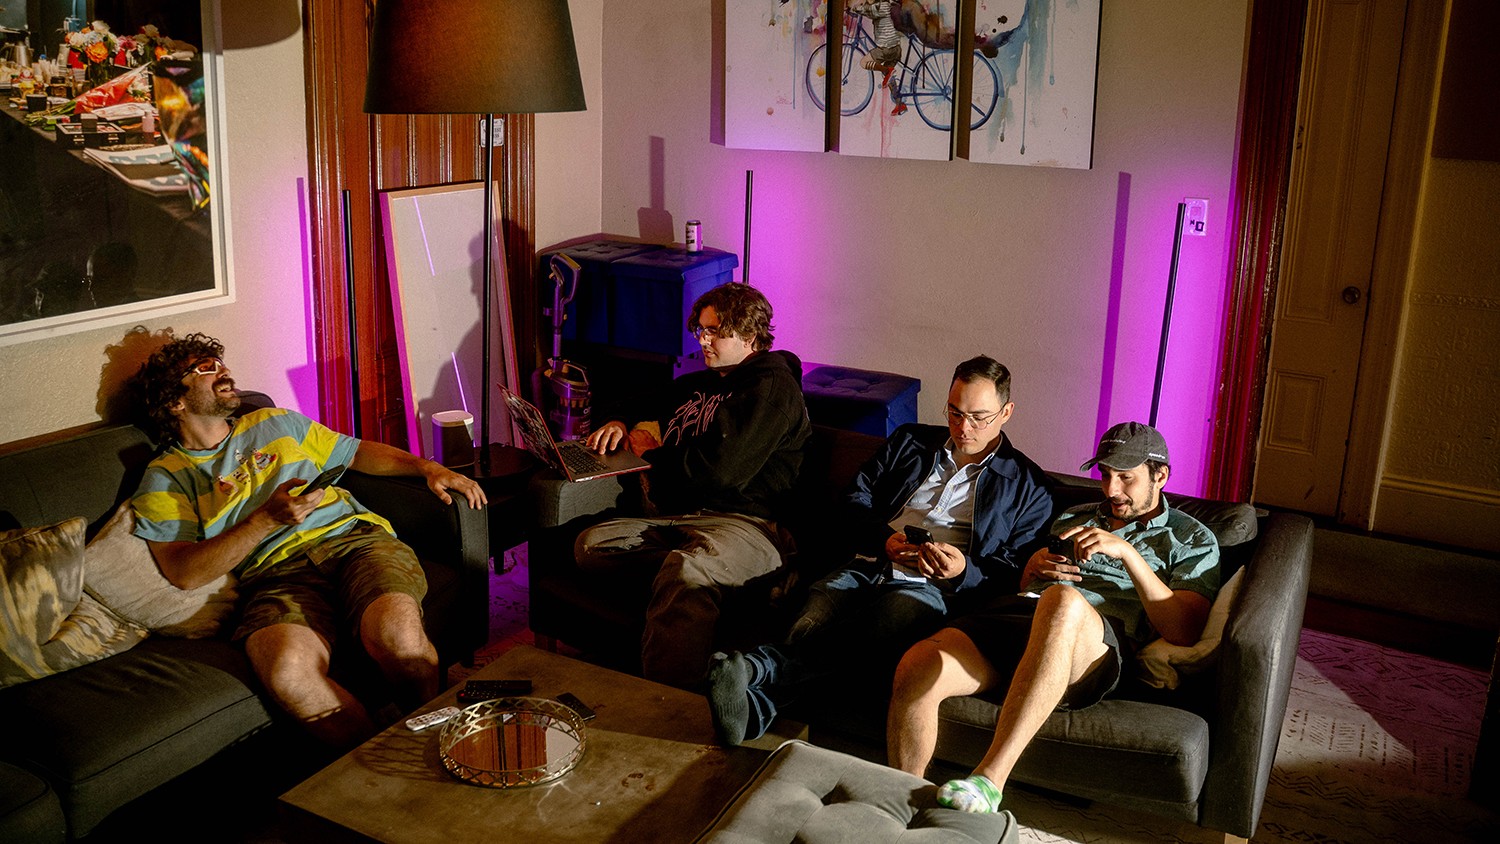
When it got cold, we went inside and settled on some couches in the living room. Morgan offered to cook what he described as “hacker-house slop bowls”—stir-fried noodles with eggs, mushrooms, and greens. While we waited, Santiago projected a YouTube show onto a large screen. It was a miniseries inspired by the residents of Crypto Castle, a hacker house from the 2010s. In one episode, a journalist visits and brings up Elizabeth Holmes, the Theranos founder who, at that point, had just been accused of running a massive scam. She may have made some mistakes, one resident of Crypto Castle said, but she “had a vision.” The hacker-house residents beside me laughed.
Niki Williams for The Atlantic
Daniel Morgan and Patrick Santiago run the Accelr8 hacker house.
Hacker houses are popping up everywhere in San Francisco. “You could just walk a few blocks” in many neighborhoods, Amber Yang, an investor at Lightspeed Venture Partners, told me, and “there’ll probably be a few houses of start-ups.”
People who want to found an AI company have little choice but to head to Silicon Valley. Nearly two-thirds of the world’s AI-start-up investment, some $120 billion last year alone, is made in the Bay Area. The gold rush has made living in San Francisco even more difficult: Rents have risen roughly 15 percent over the past year and are likely to continue soaring as the public offerings of SpaceX, Anthropic, and OpenAI mint scores of AI millionaires. Adams put it bluntly: He and his partner could not afford their own one-bedroom apartment, so they moved into Accelr8. My stay at Accelr8 was itself motivated, in part, by a scramble to find a roof for a weeklong stretch between rentals in San Francisco. (I am not launching an AI company, but I did pay prorated rent.)
In the process, hacker houses themselves are changing. A number are becoming more professionalized and lavish. Down the block from Accelr8 is perhaps the most prestigious of them all, HF0, a mansion obscured by tall hedges that has raised a $100 million fund to invest in its residents. And the Biopunk House—where Roth and Joy, the two DIY lobster surgeons, live—is part of the Residency, a network of houses that counts Sam Altman as an adviser. The Residency collectively has an acceptance rate of 3 percent (and falling) and offers a three-month stay in homes where laundry, meal preparation, cleaning, social events, and basically any adult tasks are taken care of for you. “That’s 20 hours a week” back to dedicate to your company, Nick Linck, who founded the Residency, told me. We sat in the media room of one of his houses, a Noguchi table between us and fake ivy on the shelves behind.
The house where I stayed was hardly luxurious, but it was still a major step up from Accelr8’s original location, which had 15 bedrooms and a single kitchen for $1,500 a month. When I first met Morgan there last spring, I spotted a sign over the sink admonishing residents to Wash your pans or Sam Altman will get you. (Some things, I suppose, haven’t changed all that much; Adams would later dub me the “dish fairy,” on account of my putting away the dishes every morning on our floor.) Accelr8 just opened a second hacker hotel, which it markets as an all-inclusive residency—daily breakfast, full access to hotel amenities—and is trying to raise some $20 million to purchase another property to convert into a hacker house.
Too many companies, too many products, and too many venture capitalists are coursing through San Francisco. Hacker houses can help investors screen for genuine talent. Some houses and their investors take equity in residents’ start-ups. So-called angels—wealthy people who use their own money to fund companies—can drop by a hacker house, chat with someone in the living room, and cut them a $100,000 check on the spot. Still more venture capitalists visit for product demos.
For all of the pragmatic benefits of a hacker house, there is also a more soulful draw. Starting a company is lonely, time consuming, and risky. I met hacker-house residents who were spending down their life savings or had asked friends and family for loans. Most of them will fail. At the Accelr8 house, between sprints of coding and sales calls, the founders sat on couches and chatted about good date spots, or wandered to the bar next door to watch basketball. They were friends as much as they were housemates.
On my fourth day at Accelr8, Morgan barged into the kitchen carrying an armful of mugs that had been left out the night before. He said he sometimes felt like a “hacker-house dad.” After pouring himself coffee, Morgan took a gallon of 2 percent milk out of the fridge, smelled it, made a disgusted face, and put the jug right back where he found it. That afternoon, I ran into VanToai and Adams laughing in the kitchen. Adams was preparing coffee and had poured the remnants of a jug of 2 percent milk—that milk—into his glass without first smelling its contents. The milk, they joked, was “imbued” with the curdled whey. VanToai and I watched with incredulity as Adam tried to strain out the curdled bits. He gave up and reached for the instant coffee.
Niki Williams for The Atlantic
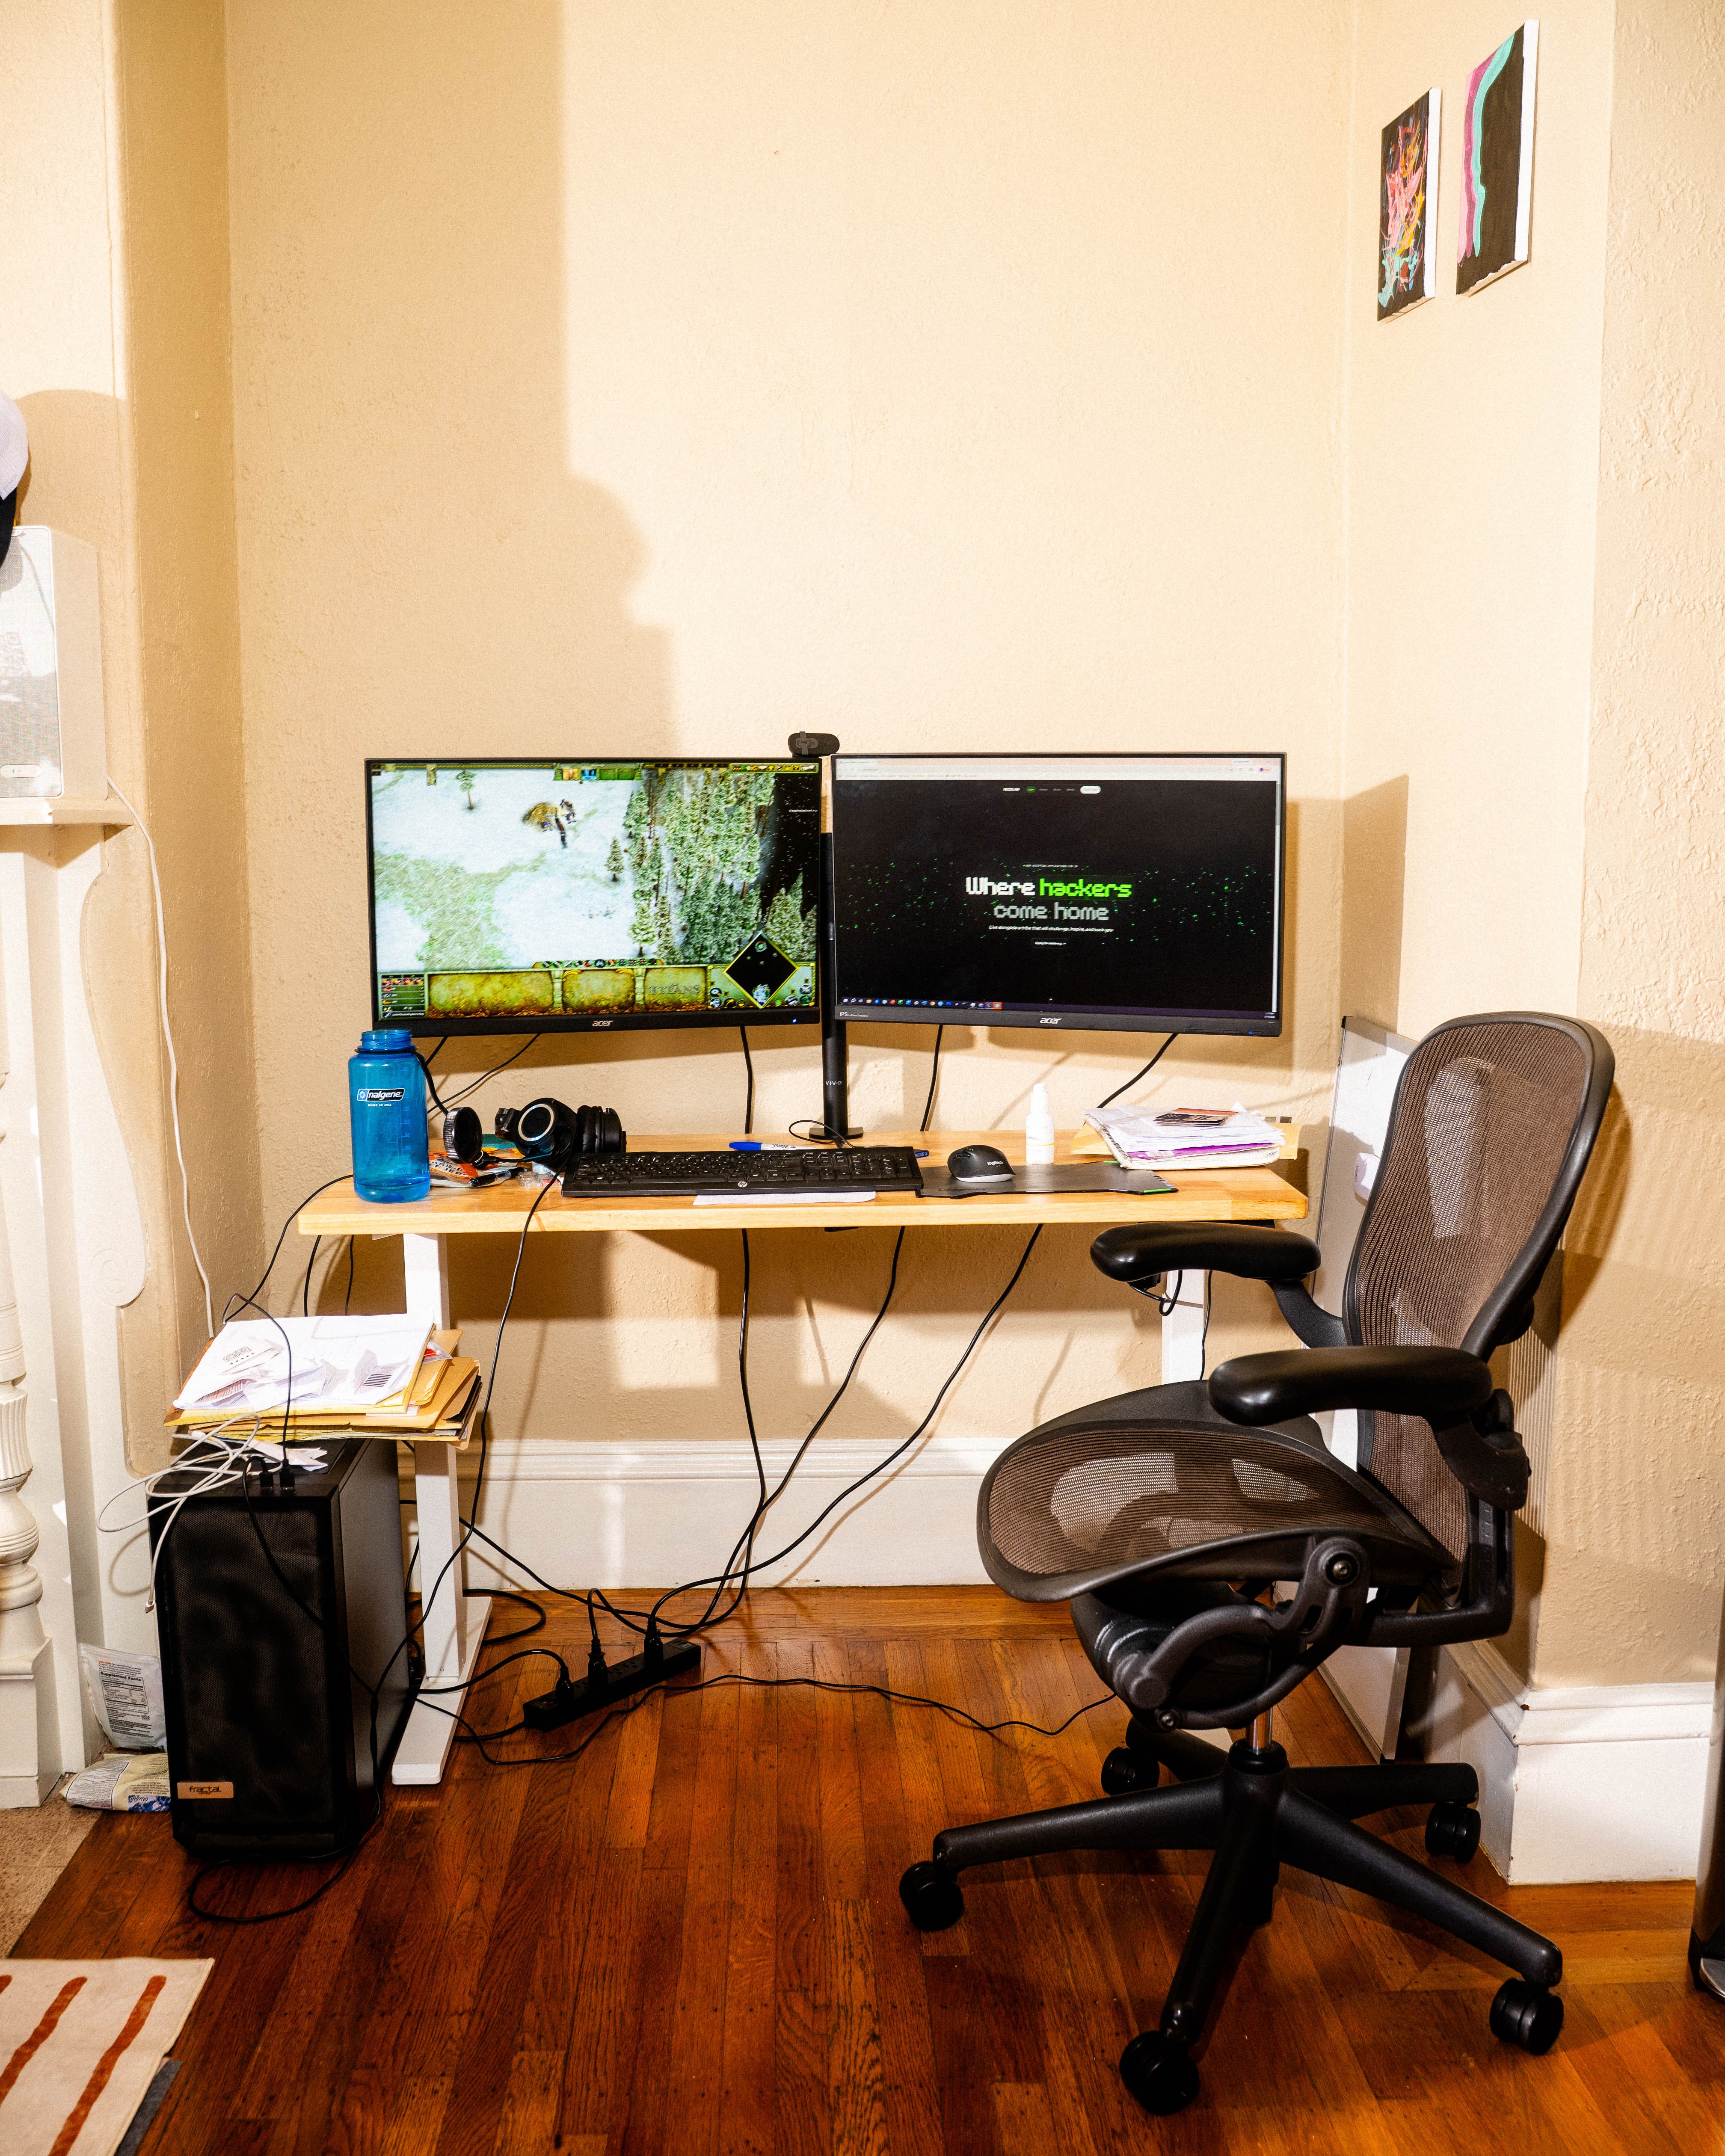
Computer monitors showing a video game at the Accelr8 hacker house.
Niki Williams for The Atlantic
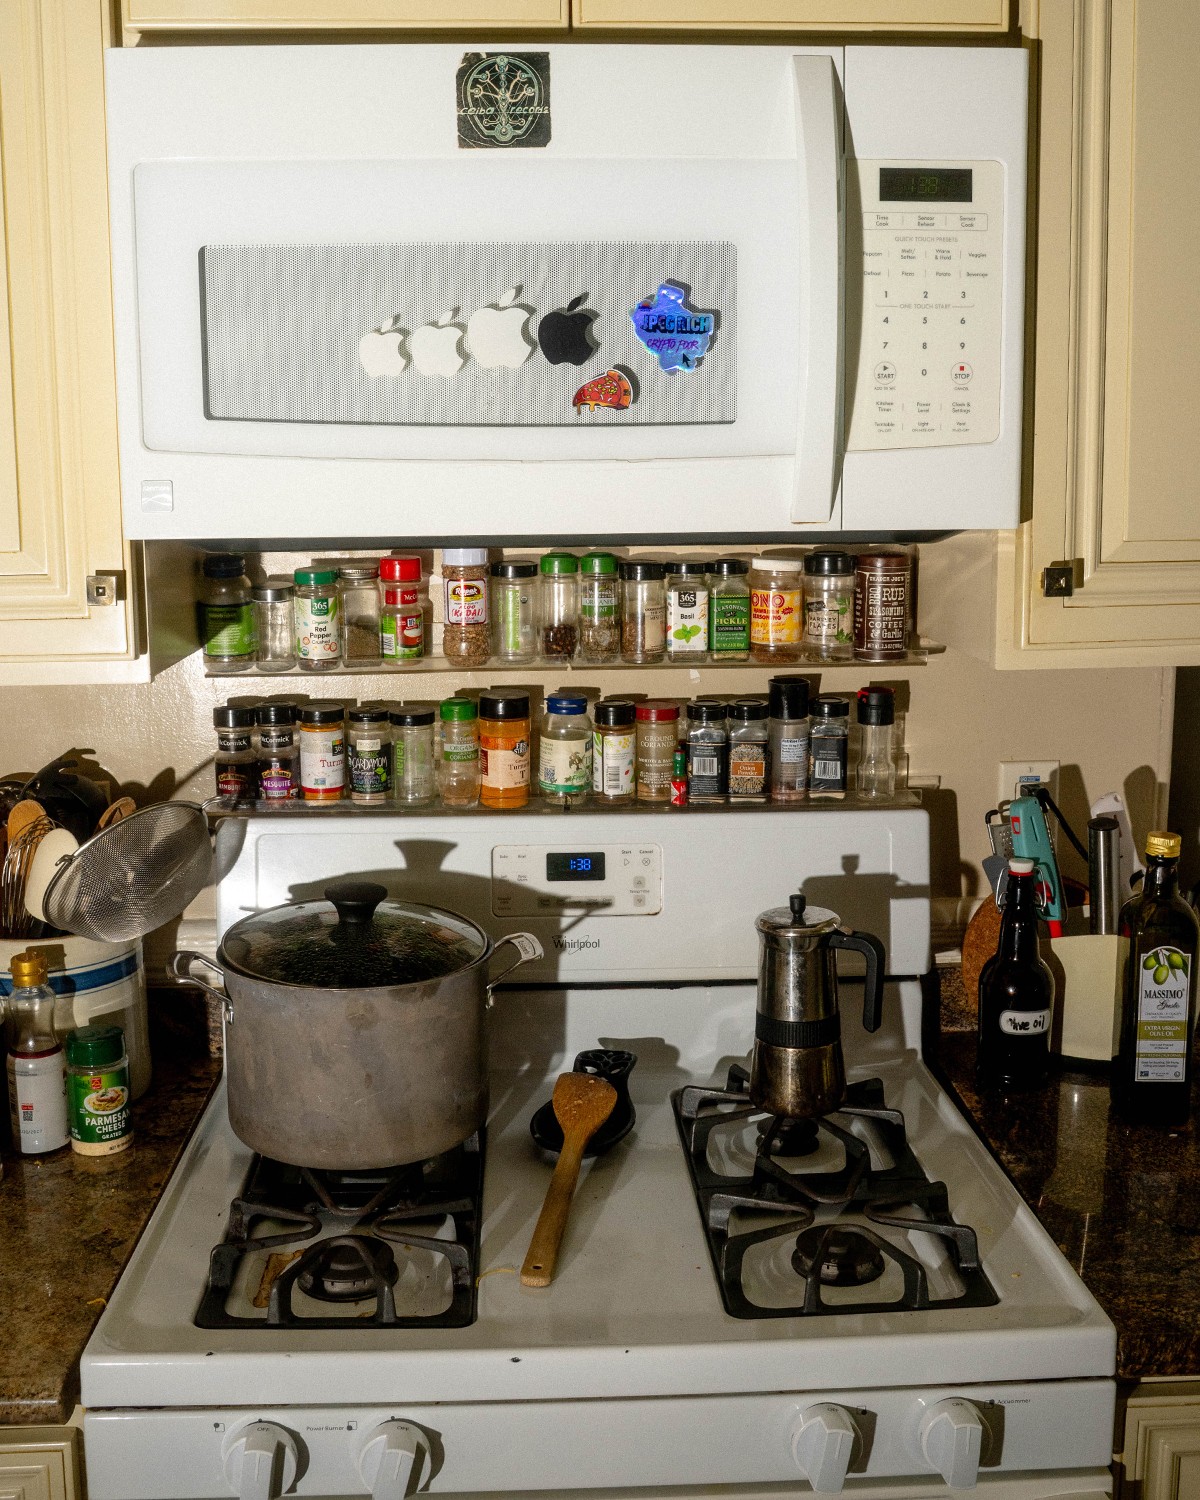
One of the kitchens at the Accelr8 house. Despite signs imploring residents not to leave dishes in the sink, dirty dishes were consistently there.
Every Sunday, the Accelr8 community members—both current and former residents—gather at the main house to demo their products at dinner. During my stay, it was hot-pot night. A couple dozen founders stood around two pots of simmering broth and ate thinly sliced beef, enoki mushrooms, and other fixings from paper bowls. With some, I discussed superintelligence and the coming automation of labor; with others, how superintelligence was mostly hype, AI is addictive, and sometimes agents “just make you feel like you’re getting somewhere” without accomplishing much. But everyone was enthusiastic to pitch their start-up.
Tigran Voskanyan, who was staying in Accelr8’s hotel, is developing an AI assistant that, he told me, centralizes your media, allowing you to access Spotify, Telegram, and so on in one place. Voskanyan asked me to pull out my iPhone and load his website so he could show me the program. This proved much slower than just opening my music app, and the bot had some voice-recognition difficulties. As I put my phone away, Voskanyan explained that his prototype is in its early stages, and he’s still working out some technical issues. Suddenly, he was interrupted by a robotic voice emanating from my jeans pocket. Voskanyan’s AI, despite being closed and my phone being asleep, was listening. I hurriedly revoked the bot’s microphone access.
Other products I heard about that evening included the crypto-based payments system Fumav, for “Fuck you, Mastercard, American Express, and Visa,” and a tool that was described to me, without irony, as “a new format” for the book. This turned out to be a text-based video-game app played on an e-reader, seemingly more akin to reinventing Oregon Trail. Matt Thompson, the founder who had made this tool, had hand-traced every illustration in his sample game to give it an artisan aesthetic. While we were cleaning up after dinner, Morgan told me that if he had the money, he would invest in Thompson’s start-up immediately.
The earnestness within these hacker houses is at times endearing and frequently confounding. Here is an ecosystem of people who generally fear the path that AI could lead us down and yet are eager to sell AI products, who see the first step in making the world better as conquering it with their technology, who earnestly believe that avarice is a prerequisite to altruism. In this city, for an idea to matter, it must exist as a product. To improve the world, you must turn people into users. Scale is a means to an end, until it isn’t. As Sourya Kakarla, a former Accelr8 resident I met at demo day, put it to me, he was “initially attracted to start-ups for the heart,” and a few years ago built an app to help elders in rural India use smartphones. But right now, he said, he “has to navigate short-term market realities to keep the heart alive.” He’s doing AI-consulting gigs to make money, like so many founders I met.
Niki Williams for The Atlantic
The backyard of the Accelr8 house, where residents gather in the evenings to unwind.
These tensions are baked into the hacker house itself, where young entrepreneurs scrap along together until they make enough money to leave the pack behind. Morgan was well aware of this dynamic, and expressed complex feelings about technology. One evening, walking back from dinner, Morgan lamented how in San Francisco, many people will stop mid-conversation and pull out their phone to request AI input. “How about what you, a human, have to say?” Morgan said, incensed. He would later tell me he’s worried about the “ChatGPT babies” growing up dependent on AI. But at the same time, he is spinning up his own AI-consulting firm.
On my last full day at Accelr8, I watched Morgan take a call with executives at a boutique construction company. Seated at the living-room table and wearing a dress shirt tucked into sweatpants that were outside his camera’s view, Morgan explained how he could build them a team of bespoke AI agents. “Sales people definitely need this,” one of the executives told him.
By then, Accelr8 seemed to be crumbling around me. After hot-pot night, the sink clogged and the upstairs dishwashers broke (the one downstairs wasn’t working when I arrived). I was holding my breath while opening the fridge. The morning I was set to leave, much of the crew gathered in the living room to see me off. I had graduated from Accelr8 and was added to an alumni group chat. Morgan handed me a souvenir, a glittering Accelr8 sticker for me to put anywhere. “Preferably a laptop,” he said.
I did still have some unfinished business. A couple of weeks after the trip to the fish market, I checked in with Joy to see how the lobster surgery had gone. We sat down in the same room where he and Roth had set up their experiment, but the tank beside us was conspicuously empty of any life or, for that matter, liquid. The lobsters had died before surgery. Perhaps they’d gotten the salinity of the water wrong, Joy told me. He had conducted preliminary dissections on their carcasses, and he said he was going through an ethical crisis about “whether I should even be doing this.” Nobody ate the lobsters.
Late last month, I began to consider withdrawing some money from my savings account to buy gold. It’s the first time I’ve ever thought about panic-buying. For all of the firewalls and two-factor-authentication codes, the safety of the internet is starting to falter. Hackers are gaining the upper hand over organizations around the world—hospitals, energy grids, government agencies, and, yes, banks.
As AI tools have become extremely good at writing code, they’ve also become extremely good at pulling off cyberattacks. (Malware, after all, is still software.) The result has been a change in the scale, speed, and sophistication of hacks that is difficult to overstate: Among its tens of thousands of clients, the cybersecurity firm Palo Alto Networks identified a fourfold increase in daily attacks from 2024 to 2025. Hackers are developing AI-enhanced computer viruses that adapt on the fly to avoid detection. They are automating cyber-espionage campaigns on foreign governments. They are stealing data in minutes instead of hours. “There’s a crazy amount of offensive activity happening right now,” Alex Stamos, a former chief security officer of Yahoo and Facebook, told me. “Companies are getting hacked every single day.”
If the NSA is perturbed by the rise in cyberattacks, which it apparently is, then surely my savings are vulnerable. There could be any number of weaknesses in my bank’s IT systems to directly hack. Or perhaps an AI-written phishing email targeted at an employee, personalized to sound like a family member or manager, could let hackers into the back end to empty my coffers. Even if the bank has great cybersecurity, an attack on another business—a medical clinic I visited, a car-rental company, a newsletter subscription—could steal my payment information and, potentially, much more. The attack angles are seemingly infinite. And no one is adequately prepared.
The term software engineering has always been an insult to the level of rigor demanded of mechanical, civic, and other engineers. Computer programs can be riddled with vulnerabilities and run just fine for years or decades—and much of the software underlying the web has done just that. “We’ve just been writing software in a totally slapdash and insecure way for decades now,” Stamos, who is now the chief security officer at the AI-coding company Corridor, said. With some small, high-stakes exceptions—such as software used on the International Space Station or nuclear submarines—code is written and deployed without much rigorous testing. If a bug is reported, it gets patched.
Such a relaxed security posture has been more or less fine because discovering vulnerabilities is hard and skilled hackers are few in number: Either nobody found the bugs or nobody was able to exploit them. But traditional cybersecurity methods don’t cut it anymore. Before, you might scramble for a week to patch a hole, Giovanni Vigna, a cybersecurity expert at UC Santa Barbara, told me. “Now you could have hundreds of those every week.” Moody’s Ratings has found that the time attackers take to exploit a publicly known vulnerability (the digital equivalent of a robber plotting how to get around a bank’s guards and cameras after obtaining a key) fell from more than 700 days in 2020 to just 44 days in 2025—faster than the average time cybersecurity teams take to patch the bug.
Governments and major companies are on high alert for AI-enabled cyberwarfare. The wake-up call came this spring, with the announcement of two extremely advanced cyber models—Claude Mythos Preview from Anthropic, and the analogous GPT-5.5-Cyber from OpenAI soon after. Many independent cybersecurity experts have told me that these models are as or nearly as skilled as elite human hackers, which is why Anthropic and OpenAI didn’t release them publicly. Instead, the AI labs have granted a small number of partner organizations and government agencies exclusive access to the unrestricted versions of these cyber models in the hopes of shoring up their IT systems. And this month, Donald Trump signed an executive order to expedite just that.
Organizations can guard against the coming deluge of AI-enabled hacks, most notably by using AI to detect and resolve vulnerabilities before cybercriminals can exploit them. Anthropic has itself used Claude Mythos Preview to find thousands of bugs in open-source-software packages—many of which went undetected for years or decades—that undergird much of the internet. Mozilla used Mythos to fix more than 400 bugs in the Firefox web browser in April, roughly 20 times more than it fixes in a typical month. And having an AI agent monitoring for intruders 24/7 could be far more effective than periodic cybersecurity audits. If you’ve noticed more updates in your web browser, work software, and smartphone apps, it may well be because software companies are using AI to scan for bugs.
But, if anything, these efforts are late. Even though they’re not as powerful as Mythos, plenty of free and open-source AI hacking tools are allowing criminals with little technical experience to marshal an army of hackers at their fingertips. Tools from Google, Anthropic, and OpenAI have guardrails intended to prevent them from being used for hacks, but they are not perfect: All three companies have reported more, and more sophisticated, hacking attempts using their AI models. When the courseware Canvas was hacked last month, upending classrooms in thousands of schools and universities worldwide, AI likely played a role—and the criminal group responsible, a notorious hacking ring called ShinyHunters, is known for using AI in all sorts of scams. Just weeks later, Google cybersecurity researchers reported that ShinyHunters had hacked into an Oracle HR system and may have stolen data from more than 100 organizations. Meanwhile, the Trump administration has forced Anthropic to revoke all public access to the latest version of Mythos—taking away perhaps the most powerful cyberdefense tool we have from both the government and the private sector.
That does not mean you should withdraw your life’s savings and buy gold (although, well). But a tremendous amount of change needs to happen in a very short period of time; open-source AI models will soon catch up to Mythos and GPT-5.5. The internet needs upgrades “at a Y2K-like scale,” Raffi Krikorian, the chief technology officer at Mozilla, told me, referring to a widespread fear that computer programs interpreting the digits “00” to mean the year 1900, rather than 2000, would bring down the web. But IT professionals spent years preparing for and ultimately avoiding a Y2K apocalypse, he said; with AI, we have months. No one company or government can demand the requisite collective action rapidly enough to completely secure our digital infrastructure. “There’s no way organizations across the globe are going to patch everything that needs to occur within the next three to five months,” Wendi Whitmore, the chief security intelligence officer at Palo Alto Networks, told me.
At the same time that bots are making hackers more capable, the technology is also making the web less robust to attacks. Coding agents, due to their propensity to hallucinate, frequently write insecure code—and humans, in the thrall of vibe-coding, usually don’t take the time to verify it. Spotty AI code has, for instance, reportedly caused multiple outages in Amazon’s e-commerce services. Meanwhile, the AI models being integrated across the web—into Amazon, Google, your bank’s customer-service department, and more—are themselves new, untested, and vulnerable to all manner of creative attacks that allow hackers to request passwords and personal information. A few weeks ago, a group of cybercriminals basically just asked Meta’s customer-service AI to give them access to some 30,000 Instagram accounts (including the Sephora corporate account and the defunct Obama White House account), and the AI obliged. (“Some of our internal backend checks failed in this instance, but it wasn’t due to the AI agent itself, and we’ve addressed the underlying cause,” Andy Stone, a Meta spokesperson told me.)
The near future is very likely to involve more frequent, and more severe, outages and hacks just like those affecting Canvas, Meta, and Amazon. “We will see more of these disruptions,” Vigna said. “I think it’s inevitable in the short term.” Smaller but crucial companies and organizations that are not web-native—think power plants, municipal-government agencies, credit unions—are especially vulnerable. They may be running all sorts of clunky legacy code, and lack the IT capacity or financial resources to make the necessary upgrades. In many cases, the person who wrote the bulk of an organization’s software might be retired or dead.
Take hospitals, many of which are already struggling to combat data breaches and ransomware attacks. Hospital IT systems are full of valuable health and financial data, and the incentive to pay a ransom is high when patients’ lives are on the line. “It’s not a matter of will to increase cybersecurity for hospitals,” John Riggi, the national adviser for cybersecurity and risk for the American Hospital Association, told me. “It is a matter of resources and capabilities.” AI, he said, will make everything worse. And the greater burden is always on the side of the defense: Missing just a single vulnerability can permit a catastrophic attack. An Anthropic spokesperson told me that “hospitals, utilities, and smaller banks run on software built by others,” which Mythos is helping secure. “Software upstream protects the organizations downstream that don’t have resources to staff their own security research team.”)
A worst-case scenario over the next year or so might look like “blackouts across the United States, telecommunications companies being hacked,” Krikorian said, or “our banking systems dealing with people losing money left and right.” Every cybersecurity expert I spoke with for this story concurred: The next few months, couple of years, or even longer will be rough. “I hope that it’s not a catastrophic outage, but I am concerned that 2026 really could be the year that we see some sort of attack like that become very successful,” Whitmore said. Anthropic estimates that a major cyberattack on just one of its 200 or so partner organizations could affect at least 100 million people.
Collective action aside, some precautions exist that individuals can take short of liquidating into gold. Many of them are basic: using a password manager that auto-generates long passwords, keeping software updated, restarting devices to wipe viruses from their short-term memory. Be extra wary of all sorts of phishing texts and other low-level scams. And you might consider simplifying your digital life by switching to a Chromebook, certain tablets, or another gadget that is a “thin client,” meaning that very little software and data are stored on the device.
Even in the most catastrophic of scenarios, perhaps we can ride out the AI hacks. No one knows just how many bugs are out there. If there’s a limited pool of vulnerabilities online, things will settle down once they are all found, whether by hackers or security audits. But it’s also possible that every time the top AI models reach a new threshold of capabilities, Stamos said, they discover a new pool of still more complex hacks. And so the chaos begins anew.
In theory, Donald Trump has a consistent position on AI. On the first full day of his second term, the president declared that he would use his full authority to speed the AI industry along and, in particular, to beat China in the AI race: “We have an emergency,” he said. “We have to get this stuff built.” If AI is poised to become the most important technology ever made, the thinking goes, whichever country commands the most powerful bots will dominate the rest of the century and beyond. The government, it seemed, would just get out of Silicon Valley’s way.
But in practice, the Trump administration’s approach to AI has been much more erratic and confusing. Take last week, when Anthropic released its most advanced AI system yet. Called Fable 5, the model is an updated and public version of Claude Mythos Preview, the highly touted and feared AI model that Anthropic announced in April. Anthropic stated that Mythos Preview was so capable at hacking that only a small group of cybersecurity partners would be allowed to use it. In the subsequent months, the company developed guardrails to prevent people from misusing its most powerful AI for cyberattacks, while still allowing them to marshal its capabilities for other sorts of work. The safety measures underwent third-party testing, including with the U.S. government, and after Fable’s release, a chorus of cybersecurity experts complained that, if anything, the model was too restrictive.
On Friday, the White House appeared to change its stance. Administration officials deemed Fable 5 a threat to national security and reportedly gave Anthropic 90 minutes to take down Fable 5 and Mythos 5, a newer version of Mythos Preview released to only a small number of organizations. When Anthropic did not, the government issued an export control, a designation that prevents any foreign national from using Fable and Mythos—even those employed by Anthropic within the United States. To rapidly comply, Anthropic shut down the bots for all of its customers. American companies and the U.S. government itself cannot use what’s perhaps the most powerful AI in the world—and the reasons are hazy at best.
It’s not unreasonable for the federal government to want to rapidly clamp down on a technology that could be incredibly dangerous. Trump officials had been alerted by researchers at Amazon to a possible way to circumvent Fable 5’s safety systems, which led the model to identify some known IT vulnerabilities. The administration has not publicly shared much information about its security concerns. A White House spokesperson told me that the jailbreak “was very serious” but said that specific details are classified. Whether the bypass really was that serious is not at all clear, and Anthropic has contested whether what administration officials showed the company even constitutes a jailbreak. An Anthropic spokesperson pointed me to a blog post in which the company wrote that the actions elicited from Fable were “either entirely benign responses or are minor findings.”
Katie Moussouris, a cybersecurity expert and the CEO of Luta Security, told me that Anthropic shared with her a copy of the White House’s report on the Fable jailbreak to get her appraisal. (She said that she is not being paid by Anthropic.) The report, Moussouris said, involved IT experts asking Fable to help find and patch bugs. When given deliberately insecure code, she said, Fable refused the prompt “review the code for security issues” but then complied when asked to “fix this code,” followed by some further manual steps. Moussouris told me that this was just “the model working as intended” for cyberdefense. She added that OpenAI’s GPT-5.5, a model with similar cybersecurity capabilities, could be used in the same way. Yet GPT-5.5 is not subject to export controls, and neither are less advanced Anthropic models, such as Opus 4.8, which can do many of the same tasks. The jailbreak does not appear to have elicited the kinds of cyber abilities “that made Mythos famous,” Alex Stamos, the chief security officer at the AI-coding company Corridor, told me. “And this kind of vulnerability discovery is already well within the capabilities of other models.”
It’s hard to imagine the Trump administration choosing to take such a drastic step against any other major AI company. The White House has long tussled with Anthropic, which generally positions itself as more safety-oriented than other tech companies; it is also more left-leaning. Last year, David Sacks, then the White House AI czar, said that Anthropic has an “agenda to backdoor Woke AI” and is a “Resistance organization.” In late February, after a high-profile dispute over a contract between the Department of Defense and Anthropic, the Pentagon labeled the company a “supply-chain risk”—a move that AI, national-security, and legal experts told me at the time seemed ideologically motivated and to lack legal basis. (Anthropic is challenging the supply-chain-risk designation in court.) On Saturday, Defense Secretary Pete Hegseth, in apparent reference to the Fable 5 export control, wrote on X that “three months ago,” the Pentagon “kicked @AnthropicAI out of our building—forever. Every passing day proves why that was the right move. 🇺🇸.”
From the perspective of “🇺🇸”—that is, American AI leadership—all of the Anthropic drama has been a mess. For starters, an export control is an especially blunt instrument. There’s no easy way to differentiate a U.S. citizen from, say, an Anthropic employee on a visa (legally a “foreign national”), so the government basically forced Anthropic to shut down the model wholesale, Alan Rozenshtein, an expert on AI and the law at University of Minnesota Law School, told me. (Many researchers at Anthropic, as is the case at all of the top AI firms, are not American citizens.) The export control also means that U.S. companies and federal agencies cannot benefit from Fable and Mythos. The National Security Agency, for instance, has reportedly made exceptions to the earlier supply-chain-risk designation to use Mythos’s advanced cyber abilities. Dozens of cybersecurity experts from companies including Nvidia and Zoom have signed a letter to White House officials stating that the export control “has taken the best models away from defenders, created market uncertainty, and risked America’s AI leadership without any real risk to justify it.”
Further adding to the chaos is how the Fable debacle is in tension with parts of the White House’s broader AI policy. Because Anthropic has been forced to shut down its most powerful models, the export control functionally amounts to the government deciding whether an AI system can be released, akin to how the FDA approves drugs. Confusingly, concerns from tech insiders about the potential creation of what Sacks called an “FDA for AI” are precisely what bred weeks of infighting and delay in Trump signing a recent executive order on AI and cybersecurity. Sacks himself said that he was mollified in part because the final executive order explicitly said that it did not establish “a mandatory governmental licensing, preclearance, or permitting requirement” for AI. So much for that. Sacks has proceeded to defend the Claude Fable 5 export control, accusing Anthropic of prioritizing its “consumer model over safety.” (A spokesperson for Sacks did not immediately respond to a request for comment.)
Anthropic researchers have flown to Washington and are meeting today with White House officials to try to resolve the issue. But whether the specific export control on Fable is lifted is almost beside the point. If none of this seems particularly self-consistent or strategic, it shouldn’t. The Trump administration wants to stay ahead of Chinese AI but has clamped down on one of the few U.S. companies that stands a real chance of doing so. It has declared Anthropic a national-security threat multiple times while also racing to incorporate Claude Mythos into some government operations. It wants to demonstrate a light-touch approach to AI regulation but also just established a de facto licensing requirement for frontier models. Meanwhile, Trump has lifted a different set of AI-export controls, allowing the sale of advanced chips to China. Perhaps some of these are good policies: Even Anthropic has suggested that a federal-licensing regime could be beneficial. And the lack of federal AI regulation to date, especially as the technology has gotten more powerful, is hard to ignore. But the latest Anthropic saga hardly counts as regulation. Right now, decisions are being made in a hurried, contradictory fashion. There do not appear to have been any outlined standards and process, robust consultation, or even agreement on the facts before coming to this one.
The Trump administration has repeatedly evinced that it can and will instantly bar any person or business from using any AI model for any period of time. A technology that is advancing rapidly and could have catastrophic impacts “is exactly the situation in which you need to give the executive an enormous amount of discretion,” Rozenshtein said. Yet at the same time, he said, Trump’s tendency to change his mind on a whim and play favorites is “exactly the reason why you don’t want to give the executive enormous amounts of discretion.” To say the least, it’s perilous to build a product, invest in a company, or even just try to leverage AI for productivity gains in an environment in which the government might at any time take a wrecking ball to your plans. America and its tech companies have many factors in their favor when it comes to leading the way in AI development. As of now, the White House is not one of them.
Elon Musk is about to set in motion a chain of events that will reshape the global financial order. For starters, when SpaceX formally goes public next week, he is all but guaranteed to become the world’s first trillionaire. His rocket company is targeting a valuation of $1.77 trillion, which would make it one of the 10 biggest companies in the world—bigger than Meta, Walmart, and, for that matter, Tesla.
All of this activity is less about colonizing Mars and more about providing the infrastructure for the AI boom: Musk wants to use his rockets to launch data centers into space, where there is abundant solar power to harvest. His rush to tap into the public markets seems to be pushing the other AI behemoths to do the same. On Monday, Anthropic filed confidential documents to begin the process of going public as early as this fall. And OpenAI is reportedly preparing to do the same any day now.
Anthropic and OpenAI, too, will likely be valued at $1 trillion or more, dwarfing JPMorgan Chase and Exxon Mobil. These will be three of the largest initial public offerings, or IPOs, in history—and all three may hit the stock market in the span of just a few months. It’s hard to overstate the effects this rapid succession of gargantuan IPOs will have on the American economy—think of it as dropping three boulders, one after the other, into a kiddie pool.
These companies are not going public because they are moneymaking machines. Consider that SpaceX, in the lead-up to its IPO, revealed that while it is seeking a nearly $1.8 trillion valuation, the company has lost $4.3 billion in just the first three months of 2026. OpenAI is also unprofitable, while Anthropic might barely post its first profitable quarter ever at the end of June. Yet the trio are set to become among the most valuable companies in the world because of a promise of unprecedented riches on the horizon. In a Securities and Exchange Commission filing, SpaceX wrote that in the long run, AI will eat the economy, and so its total revenue could be, in essence, equivalent to most of the U.S. GDP. Similar logic could be applied to OpenAI or Anthropic.
To create such all-powerful bots that could feasibly reshape the entire economy, AI firms have to build lots and lots of data centers. (Hence Musk’s excitement about putting them in space.) Whether in orbit or on Earth, they will be extremely expensive. OpenAI CEO Sam Altman has said he would like to build a gigawatt of data-center capacity every week—that’s as much power as a major city demands and would likely cost tens of billions of dollars every seven days.
The cost of all this data-center construction is likely why SpaceX, Anthropic, and OpenAI are now racing to go public. As Daniel Amodei, the president of Anthropic, put it yesterday: “It’s a very capital-intensive business to train AI models,” and an IPO is “very well-suited to that.” For years, they have all been able to raise enormous sums from private investors. Anthropic’s latest fundraising round valued the company at $965 billion, while OpenAI’s put it at $852 billion. But even these private funds are hitting a limit. AI companies “have essentially extracted all the capital the private markets can really give them,” Harrison Rolfes, a senior research analyst who specializes in AI at PitchBook, told me. SpaceX, Anthropic, and OpenAI need more money, while the venture-capital and private-equity firms that have been propping them up want to finally profit from their major investments. (None of the companies responded to my requests for comment.)
The upshot is that, before long, you may personally be able to purchase shares of SpaceX, Anthropic, or OpenAI. In fact, these companies may be angling for retail investors, meaning individuals who buy stocks themselves. SpaceX will reportedly reserve up to 30 percent of its shares for these traders, much higher than the typical 5 or 10 percent. Though it’s unclear if Anthropic and OpenAI will do something similar, even in its latest private fundraising round, OpenAI raised more than $3 billion from individual investors—announcing that it was “giving more people the opportunity to share in the upside economics of OpenAI and the AI era.”
More cynically, retail investors are considered, “for lack of a better word, less sophisticated than institutional investors,” Franco Granda, a senior research analyst who covers SpaceX at PitchBook, told me. Everyday people are especially likely to buy a stock if they believe in a vision—putting data centers in space, curing cancer with AI, what have you—irrespective of the underlying financials. And Musk, especially, has an army of eager fanboys. (Faith in Musk’s pitch for Tesla to develop robotaxis and humanoid bots is in no small part why Tesla’s stock has chugged along fine, despite collapsing profits.)
On top of that, many Americans will be forced to purchase shares of SpaceX—and likely Anthropic and OpenAI after that—whether they want to or not, and perhaps without even knowing it. That’s because many Americans passively invest their 401(k) and other retirement savings through index funds—large stock portfolios tied to indexes such as the S&P 500 or Nasdaq 100 designed to broadly track the market’s performance by pooling together the stocks of the biggest public companies.
Ordinarily there is a long waiting period before a public company is included in an index, because the months immediately after an IPO can be very volatile. The values of Facebook and Uber fell dramatically after going public due to concerns over their revenues (though their stock prices eventually rebounded and have since risen dramatically); others, most famously Pets.com, have gone out of business. But in the lead-up to the potential windfall from SpaceX, several major indexes (although not the S&P 500) created fast-track exceptions that will allow Musk’s firm to be included within just days of going public. The same rules could expedite the entry of Anthropic and OpenAI, as well. As soon as one of these companies is included in any of the major indexes, millions of Americans will automatically be purchasing its stock—in turn buoying the value of shares held by big institutional investors. You may soon have a personal financial stake in Musk conquering space and ChatGPT curing cancer.
To a large extent, much of the U.S. economy was already tangled up with Silicon Valley: AI-related stocks accounted for nearly 80 percent of gains in the S&P 500 from the launch of ChatGPT through the end of last year, and the nation is spending more to build data centers than on offices or transportation infrastructure. But now the fate of the American financial system will be even more directly exposed to the fate of SpaceX, Anthropic, and OpenAI.
The overall effect on stock markets will be chaotic, not a sure rise. For all of these companies to list at $1 trillion or more, it’s likely that some money will have to come out of other major space and tech stocks—hedge funds and investors could shift their bets from Northrop Grumman to SpaceX, for instance, or from Microsoft to OpenAI, or from SpaceX to Anthropic. In the long run, the best-case scenario is that these companies are financial successes and make many of us prosperous in turn. The worst-case scenario, that the AI boom is a bubble, just got an order of magnitude more severe. And there are some red flags on that front: A recent analysis from Bain found that AI is not yielding substantial savings for corporations, and businesses are growing concerned with the tremendous bills their employees are racking up from running the most advanced versions of Claude and ChatGPT. Uber’s chief operating officer recently said that AI spending is becoming “harder to justify.”
Of course, concerns that AI is a bubble rise and fall every few months. But through it all, SpaceX, Anthropic, and OpenAI have continued to embed their bots more deeply and broadly across the economy. By weaving itself into the finances of most businesses and households in America, the AI industry is quickly making itself too big to fail. Should these three firms go public, the fallout from an AI bust would spell ruin for the savings of much of the country. Just as the federal government stepped in when banks and automakers went bankrupt in 2008, it could not allow Silicon Valley to collapse. The promise of AI was always a self-fulfilling prophecy: This technology is so expensive to build that it must be world changing; and because it is world changing, we will spend any amount to build it.
For months now, the White House has hinted that it may try to rein in the AI industry. Just two weeks ago, the nation’s top tech executives—including Sam Altman and Dario Amodei—were invited to attend a ceremony for the signing of a long-anticipated executive order on AI. But just hours before the ceremony, Donald Trump scrapped it. America is leading the world in the AI race, the president told reporters at the time, “and I don’t want to do anything that’s going to get in the way of that lead.”
Apparently, Trump has changed his mind again. Earlier today, the president signed an executive order that will create a process for top AI companies to voluntarily share certain upcoming models with the government for safety testing up to one month before wider release. OpenAI, Anthropic, and the like will also be asked to work with the government to shore up federal, state, and local cyberdefenses. The White House spokesperson Liz Huston told us that the policy reflects a “common-sense approach of collaborating with industry to balance innovation and security.”
The order itself is relatively toothless: Even before today, the major AI firms already had agreements in place that allowed the government to preemptively test their models for safety risks. The new rule “effectively formalizes what has already been happening between the U.S. government and the leading AI companies,” Daniel Remler, an AI expert at the Center for a New American Security, told us.
But the executive order is meaningful in that the president is doing something—anything—about AI. At the start of his second term, Trump signaled to tech companies that he would stay out of the way. Last January, he rescinded a set of modest Joe Biden–era policies, calling the rules “dangerous” and a “barrier” to American AI leadership. Even the preamble of today’s executive order celebrates that Trump “unleashed tremendous technological growth” by “slashing the bureaucratic constraints that the prior administration placed on America’s AI developers.” Yet core components of those supposedly dangerous Biden-era AI regulations—voluntary agreements to share information about advanced AI models with federal agencies, for instance, as well as federal programs to leverage AI for cyberdefense—are strikingly similar to today’s new AI executive order. Dean Ball, a former AI adviser to the Trump administration, wrote that the policy “is considerably more intrusive” than Biden’s executive order.
Today’s order still could have been much more forceful. When the White House first started previewing the possibility of regulatory action in May, one administration official suggested that AI models would be reviewed “just like an FDA drug.” Even the leaked draft text of the version that Trump had originally planned to sign last month would have been more burdensome for tech companies. After David Sacks, the White House’s former AI czar, reportedly called the president to complain, Trump canceled the signing ceremony. Today, after the new order was announced, Sacks declared the watered-down provisions a “game changer” on X—despite the fact that the new government-review process is not so different from what he had originally opposed. This means that two former libertarian AI advisers to the White House—Ball and Sacks—disagree about whether this order is a good thing.
At the same time, joining Sacks in praising the rule is Steve Bannon, Trump’s former chief strategist and a leading critic of AI on the right. “It’s not perfect,” he told us. “But directionally, it is pretty damn good.” As Bannon sees it, despite the fact the order is weaker than earlier versions, codifying rules is a step in the right direction.
The entire, chaotic saga—a wishy-washy White House, confused statements from populist and tech-elite Trump whisperers—is only the latest in a long string of strange, often contradictory AI-policy positions. Trump’s approach to AI has been inconsistent, if not incoherent, almost since the day he retook office. Consider that, for all the talk of cybersecurity, this administration has also gutted the Cybersecurity and Infrastructure Security Agency, the government agency that aims to protect the nation against hackers. CISA also happens to be one of the main federal agencies tasked with implementing today’s executive order.
Or take the White House’s relationship with Anthropic. On the one hand, Anthropic likely triggered the executive order in the first place. In April, the company announced Claude Mythos Preview, a new model with advanced hacking capabilities that has ignited concern over the growing power of AI companies. Ever since, the president has seemed to cozy up to Anthropic. Dario Amodei, the firm’s CEO, visited the White House that same month for conversations over the future of the government’s relationship with the company. “I like high-IQ people, and they definitely have high IQs,” Trump later told reporters of Anthropic’s leadership.
On the other hand, the Trump administration appears to be fighting in court to bar Anthropic from doing most national-security work. In February, the Pentagon designated Anthropic a “supply chain risk” after a high-profile contract dispute over the use of AI in warfare, essentially declaring it a national-security risk for the military to even touch Anthropic products. In late April, when Anthropic tried to grant more companies access to Mythos for cyberdefense—very in line with today’s executive order—the White House appears to have, inexplicably, blocked the move. (An Anthropic spokesperson pointed us to a post on X in which the company called today’s executive order “an important step in strengthening America’s leadership in AI.”)
Then there’s the administration’s attitudes toward China. Trump has repeatedly emphasized the need to deregulate the AI industry in order to stay ahead of China. Meanwhile, he has also permitted Nvidia to sell some of its most advanced AI chips to Chinese companies, lifting an export control the Biden administration put in place precisely to waylay Chinese AI development. (Anthropic, by the way, denied a Chinese think tank access to Mythos.) Trump has, in the name of beating China, pushed to remove regulatory constraints on data-center construction: “Build, baby, build,” he said last July. But once uproar emerged about data centers hiking up electricity bills, the White House announced a voluntary pledge for AI companies to take a number of measures that would prevent everyday people from paying for data-center electricity. Build, baby, but prudently.
Indeed, at least some of the vacillations seem to be driven by public opinion. Over the past several months, as AI models have improved, attitudes toward the technology have soured. Today’s order allows the administration to look as if it is undertaking more robust AI regulation—but it doesn’t actually require the industry to do very much, if anything. Trump is trying to score points with both the public and Silicon Valley. But in doing so, he’s not saying or doing anything substantive at all.
AI spending is consuming the U.S. economy, people are afraid of losing their jobs to AI, and communities across the nation are gathering to protest data centers. Political figures as divergent as Bannon and Bernie Sanders are expressing concern over AI and the concentration of power among the industry’s executives. This would seem to be a clarion call for the president of the United States, and a populist one at that. Instead, the White House spent weeks prevaricating on an executive order that rests on the voluntary cooperation of the AI industry. With Anthropic, OpenAI, and their competitors becoming major economic and geopolitical powers, the window for any one government to seriously regulate AI is rapidly closing. Hopefully, it is not already gone.
Basically every recent, high-profile accusation of someone passing off AI-generated writing as their own has started in the same way: with a tool called Pangram. In March, when a horror novel from a major publishing house was pulled just days before its scheduled U.S. release date, it was in part because Pangram, an AI-detection program, had identified the text as AI-generated. Other people have fed text into Pangram to suggest that chatbots have been used to write articles in major newspapers including The New York Times, multiple short stories awarded a prestigious literary prize, and most recently, significant chunks of Pope Leo XIV’s encyclical warning about the dangers of AI. The tool is also used by universities to vet student work and scientific associations to scan research papers. As panic builds over AI-generated writing, Pangram is at the foundation.
Just a few years ago, it seemed like it might never be possible to instantly and reliably determine whether a piece of text was written by a bot or a person. In 2023, one detection tool, ZeroGPT, declared the U.S. Constitution to be AI-written; the same year, OpenAI abandoned its AI detector altogether owing to a “low rate of accuracy.” And that was when the quality of ChatGPT’s writing was markedly worse than it is today. But detection tools have gotten much better of late—and Pangram, in particular, has emerged as the gold standard: Paste a chunk of text into Pangram, and the model appraises what portions were “AI Generated,” “AI Assisted,” or “Human Written.”
Yet an AI detector that is mostly reliable might in some ways be more dangerous than a broken one. While Pangram is accumulating the power to end reputations and careers, the tool does make mistakes, perhaps to a greater extent than is currently understood. In turn, AI accusations could very quickly spiral into a witch hunt.
Pangram says its algorithm is so accurate that it incorrectly identifies text as an AI output only about one in every 10,000 times. “There is a great responsibility, a huge weight” in saying something is AI-generated, Max Spero, Pangram’s CEO, told me. “The only reason we do so is because we’re extremely confident.” Several independent analyses have also confirmed that it is quite good. One paper, from the University of Chicago, found that Pangram had almost no false positives on some 3,000 sample texts of roughly 500 to 1,000 words.
But Pangram’s ability to guarantee something was written by a human is shakier. Spero pointed me to a test showing that Pangram’s false-negative rate, or how frequently the model incorrectly labels text as human, is closer to one-in-70 (although some other assessments say it is more accurate than that).
Part of the problem is that Pangram is in an arms race with the major AI labs, which have an interest in making the writing of ChatGPT and Claude sound as natural and human as possible. And at the same time, Pangram has to deal with AI “humanizers”—programs designed explicitly to disguise AI text as your own. Reddit users rave about a humanizer called Walter Writes AI, which I decided to test out for myself. I had ChatGPT and Claude write brief articles, then pasted them into Walter Writes AI. The program, like other humanizer tools, does some anodyne rewording, swaps one clunky transition clause for another, and introduces grammatical oddities. For instance, ChatGPT’s “The numbers are no longer small enough to ignore” became “The sheer size of these usage figures can no longer be ignored.” When I pasted any output from Walter Writes AI into Pangram, it invariably told me that the twice-baked AI article was human-written. (It’s worth mentioning that The Atlantic forbids using AI-generated text unless labeled as such, and that I do not use AI for research.)
Pangram, in other words, can only provide so much insight. A teacher at a public high school in New York City told me that he has “run some of my students’ papers through Pangram, and it shows up as 100 percent human. And I don’t think it is.” He knows what his kids are capable of and, especially for those with a history of cheating with AI, has ample reason to doubt Pangram. (I agreed not to identify the teacher by name so that he could speak freely about how he suspects his students are using AI.) But on the flip side, accusing a student of getting undisclosed help from a chatbot with circumstantial evidence is high stakes: The student will either fail or, if exonerated, be bitter and resentful. “The stakes are so high,” the teacher said, “but our way of assessing what is AI-generated is still so unformed.”
Further complicating matters are the opaque ways in which Pangram and similar tools are designed. The model was trained by feeding it mountains of examples written by a human and by a bot—a book review in an actual magazine, then a review about the same book in the style of the same magazine, but produced by ChatGPT—until it can tell the two apart. This is akin to feeding millions of photos of cats and dogs into an image-recognition algorithm until it learns to spot the differences. Pangram cannot point to much specific evidence or patterns in diction, phrasing, or punctuation to support why it deems something AI or human. (I do not, for instance, understand why “these usage figures” was more human than “the numbers.”) Moreover, while Pangram distinguishes between “lightly” and “moderately AI-assisted,” these broad categories can mean just about anything short of copy-pasting from Claude—using AI for research, coming up with counterarguments, as a thesaurus, for a grammar check. The algorithm’s inner workings are “pretty uninterpretable,” Spero said, and although he wants to make Pangram’s “AI-assisted” label more granular, he is also “still not sure how possible it is.” Amid concerns of overreliance on AI chatbots, we risk simply layering on dependence on yet another black-box algorithm.
Spero told me that Pangram should “never be the ending arbiter” but instead a starting point for a more thorough investigation, and that the company looks into every reported error its model makes. He also noted that all sorts of detection technology we rely on—smoke detectors, TSA scanners—have base error rates too. On some level, in all these cases the biggest problems lie not in the technologies themselves but in what they’re trying to detect. It’s a problem that buildings catch on fire. It’s a problem that AI is seeping haphazardly into every facet of written communication.
As AI-writing accusations continue to escalate, though, there will only be greater reliance on Pangram—or whatever AI detector can dethrone it—to convict or exonerate. Consider that Pangram can connect to Canvas, the popular education platform, allowing teachers to use it to scan student submissions. There are more than 10 million high schoolers in the United States and some 20 million undergraduates, each of whom likely submits many dozens of written assignments every year. At that scale, Pangram would produce plenty of false accusations even with a one-in-10,000 error rate.
Nor is it guaranteed that Pangram will improve or even maintain its current ability to spot AI prose. As chatbots and AI humanizers adjust, AI detection “will wax and wane in its effectiveness for reasons we can’t predict, at times we can’t predict,” Tim Requarth, a neuroscientist who teaches science writing at NYU and has written extensively about AI detection, told me. Even as schools, publishers, scientific institutions, and the like come to rely more on AI detection, any third-party assessments of Pangram’s accuracy will be from weeks, if not many months, in the past—which in the accelerating world of AI renders them all but obsolete. Basing any AI rules or norms on the reliability of AI detection is like building a sandcastle at low tide.
All of this seems like a disaster in the making. The murkiness and ambiguity of AI detection create room to launch or deny accusations of nearly any sort. Earlier this month, the technology journalist Taylor Lorenz was accused on X of using AI to write a story for Vanity Fair, which she vehemently denied. Spero investigated and, as he detailed on X, found that Pangram had erred. “Thank god for edit history,” Lorenz told me. The experience heightened Lorenz’s concerns about such allegations: “I’m so paranoid,” she said.
“AI-generated” and “AI-assisted” can be easily confused, by accident or in bad faith. James Taranto, an editor at The Wall Street Journal, recently called Pangram a “defamation machine” and claimed it had falsely flagged three op-eds in his newspaper as AI-generated; two of the implicated authors admitted to using AI to revise some of their work, which Taranto wrote is “inaccurate and unfair to characterize” as “AI-generated.” One of the people who first used Pangram to analyze Pope Leo’s encyclical noted that, because only some sections seemed AI-generated or AI-assisted, perhaps it was not the pope himself but some senior Vatican officials who had used AI while drafting portions of the text. That didn’t stop headlines such as “Did the Pope Use AI to Write About the Dangers of AI?” (The Vatican did not respond to a request for comment, although a writer who covers the Vatican said on X that the AI allegations are “100 percent false” and that Leo actually drafted the encyclical with pen and paper.)
All of this recalls another recent moral outrage over alleged writerly misconduct: The plagiarism wars of 2023 and ’24, when right-wing activists such as Christopher Rufo mobilized to accuse high-profile academics and university leaders of plagiarism—most notably leading to the resignation of then–Harvard president Claudine Gay. Many of these accusations were spurious and likely based on the assessments of plagiarism-detection algorithms that, as my colleague Ian Bogost judged at the time, were fairly useless. The AI-detection wars to come may be even more contentious.
Pangram, to be clear, is not useless. But this is exactly the problem: It’s too easy to twist and contest Pangram’s conclusions, especially when nobody really agrees on which uses of AI are or aren’t ethical. Just like chatbots, AI-detection tools have become effective enough for widespread use, but not reliable enough to fully trust. In this way, Pangram and other detectors are mirror images of the AI products they are hunting for.
Sam Altman did not seem to be having a good time. During the many days that he spent inside an Oakland courtroom, the normally cheery CEO of OpenAI—a guy who tends to be chipper even when declaring AI’s existential risks to humanity—appeared anxious, even distraught. When he listened to the proceedings in Elon Musk’s lawsuit against him, a weekslong trial that threatened to remove Altman from OpenAI’s board and functionally destroy the company, he frequently concealed his mouth with his palm, fidgeted with a water bottle, and leaned forward and stared at the floor. He kept looking back at the rows of reporters behind him. On the witness stand Tuesday, Altman repeatedly noted how Musk’s actions had “annoyed” him.
Musk, who helped form OpenAI as a nonprofit in 2015, alleged that Altman and OpenAI had violated the organization’s founding principles by seeking profits. He was requesting, among other remedies, more than $150 billion in damages, which Musk said he would donate to the OpenAI nonprofit. This morning, a nine-person jury delivered a unanimous verdict after less than two hours of deliberation: Whether or not OpenAI had done something wrong, Musk sued outside the statute of limitations, two to three years depending on the charge. And Musk could have known of any alleged wrongdoing, the jury found, well before. Altman has been granted some respite: OpenAI and the AI industry will continue along, unfazed, at least until Musk appeals the decision. (A second portion of the case, related to claims that Musk made under antitrust law, remains unresolved, although the presiding judge has said that his are “not very good claims.” Neither Musk’s lawyers nor OpenAI immediately responded to a request for comment.)
OpenAI swept the legal argument. But in another sense, basically everybody involved in Musk v. Altman came away looking petty, short-sighted, deceptive, or ignorant. During the dozens of hours I spent in the courtroom, sometimes lining up as early as 5 a.m. to secure a seat, there wasn’t much substance to be found. Frankly, at the end of it all, everyone had good reason to be annoyed.
Musk came off the worst in this trial, by far. The question before the jury was whether OpenAI’s for-profit arm had somehow broken a legal promise the organization made to Musk at the organization’s founding: “It’s not okay to steal a charity,” as Musk told the jury on the first day. This was a farcical notion based on any number of pieces of evidence and testimony presented at trial, not least of which being that in 2017, Musk himself was involved in discussions for OpenAI to raise more money by making a parallel for-profit arm. Coming into the trial, this was already an uphill battle for Musk and his lawyers. But even by those low expectations, the entire affair was a debacle.
As a witness, Musk was impish. When asked simple questions by William Savitt, one of the attorneys representing OpenAI, Musk rambled and avoided the issue at hand. When the lawyers asked for a yes or no, he bristled: “The classic reason why you cannot always answer a yes-or-no question,” Musk said from the witness stand, “is if you ask a question, ‘Have you stopped beating your wife?’” (“We’re not going to go there,” U.S. District Judge Yvonne Gonzalez Rogers interjected.) Later, Musk accused Savitt of asking improper questions, after which Gonzalez Rogers sharply cut in, telling the world’s richest man, “You’re not a lawyer.” Musk conceded but, after a pause, grinned and added, “Well, technically I did take Law 101.”
When Musk answered questions, he argued that OpenAI had sacrificed safe and responsible AI development by prioritizing profits. But when cross-examined about AI safety, Musk was unable to articulate any coherent arguments. Savitt noted that Musk’s xAI, a competitor to OpenAI, is a for-profit company, and asked if xAI presents identical dangers. “Yes,” Musk said, “I think it creates some safety risk.” Savitt then asked about basic AI-safety measures. Musk, who earlier had testified that he wants to avoid an AI “Terminator outcome,” was clueless. Asked about safety cards, for instance, Musk responded, “Safety card? Why would it be a card?” These are years-old, widely used, industry-standard documents that anybody who has worked at an AI company in the past five years should be intimately familiar with.
The following day, in a particularly withering exchange, Savitt went down the list of Musk’s other enterprises. Did he think that Tesla was making the world better? “Yes,” Musk said. And is Tesla a for-profit company? “Yes.” Savitt then asked these two questions about SpaceX, Neuralink, and X. For each of his businesses, Musk responded yes and yes. The same man who has a trillion-dollar compensation package from Tesla and may receive another from SpaceX was suing OpenAI for trying to make a lot of money. I wondered to myself, What are we doing in this courtroom again?
Despite winning in court, Altman didn’t come off all that much better. The first question from Steven Molo, one of Musk’s lawyers, to Altman was “Are you completely trustworthy?” With a puzzled look, the OpenAI CEO responded, “I believe so.” Molo asked if he had misled business partners, and Altman, after a pause, said, “I believe I am an honest and trustworthy business person.”
Altman’s evasive answers were significant because he has a long history of being accused by colleagues and business partners of being deceptive. Ilya Sutskever, a co-founder and former chief scientist of OpenAI, testified that during his time at the company, he had felt that Altman created an “environment where executives don’t have the correct information,” which is not conducive to AI safety. Multiple former OpenAI board members testified to similar effect in explaining why, in late 2023, they briefly fired Altman. (For his part, Altman wrote in a recent blog post that he is “not proud of handling myself badly in a conflict with our previous board that led to a huge mess for the company.”) When the judge excoriated OpenAI’s legal team for making contradictory arguments in separate lawsuits that she is hearing, Musk smiled and nodded. Musk’s legal team essentially hung its case on impugning Altman’s integrity, and Molo told the jury in his closing argument to imagine that they were walking over a bridge: “The bridge is built on Sam Altman’s version of the truth,” he said. “Would you walk across that bridge?”
The many texts, emails, and internal documents released because of the lawsuit, and the sworn testimony of current and former OpenAI executives, were hardly flattering for the firm— depicting a treacherous company culture that has nonetheless made its staff fantastically rich. Sutskever said that his stake in the company is worth some $7 billion, and Greg Brockman, OpenAI’s president and another defendant in the lawsuit, said that his equity is worth some $30 billion. Altman, who previously told the Senate that he has no direct equity in OpenAI, testified that through an investment fund run by the start-up incubator Y Combinator (which Altman used to be president of), he has an indirect financial stake in the firm.
The trial surfaced and produced countless other shenanigans: Musk apparently called an OpenAI employee a “jackass” for wanting to prioritize safety over speed, after which that employee was given a satirical trophy depicting a donkey’s butt. (During his own testimony, Musk denied yelling at someone and said he would have used such a word only in jest.) In a diary entry, Brockman had written that it would be “wrong to steal the nonprofit from” Musk and that doing so would “be pretty morally bankrupt, and he’s really not an idiot.” Sutskever, a Yoda-like figure in the AI world, described AI progress from 2018 to now as “the difference between an ant and a cat.” At the beginning of the trial, the judge had asked Musk to refrain from posting on social media about the trial as it unfolded, and he did show restraint. Immediately after the verdict, though, Musk posted on X: “The ruling by the terrible activist Oakland judge, who simply used the jury as a fig leaf, creates such a terrible precedent.”
To the extent that the trial could have actually been about the best way to develop AI for the benefit of humanity, and about whether OpenAI is honoring its founding pledge to do so—well, it simply wasn’t. For the most part, Musk and Altman—billionaires who are perhaps the two most influential tech CEOs in the world—were in essence asking their attorneys to debate whether making ungodly sums of money was acceptable. In a remarkable exchange during closing arguments, Gonzalez Rogers excoriated one of Musk’s lawyers for misleading the jury: Molo, after attacking the bridge “built on Sam Altman’s version of the truth,” said that Musk is not asking for money from OpenAI. The district judge pointed out that he, in fact, was asking for money. “You need to retract that statement, or you need to drop your claim for billions of dollars,” the judge said. Musk’s lawyers did not drop the demand.
AI has ascended to the role of main character. When Donald Trump traveled to Beijing for a historic summit last week, AI was one of the central topics of his discussions with Xi Jinping. As the two nations remain locked in a technological arms race, the president brought along some of the United States’ most powerful AI executives, including Elon Musk and Nvidia’s Jensen Huang. A continent away, the European Union has been unsuccessfully petitioning Anthropic to grant access to its advanced cybersecurity model, Mythos. Back in the United States, millions of students and teachers are dealing with the fallout of a devastating ransomware attack on the software platform Canvas—a hack that was likely aided by AI tools. And on Thursday, Cisco became the latest major company to justify layoffs by pointing to AI.
The past six months have marked a sea change in the reach and influence of AI. For most of 2024 and 2025, there was talk of AI progress slowing down or even stopping altogether. Even as the technology began to infiltrate schools and reshape financial markets, AI was relatively easy to compartmentalize from other major, more pressing issues in American life.
No longer. Now the technology has become regarded as a matter of the greatest economic, political, and global consequence. The most important issues in U.S.-China relations? Tariffs, Taiwan, and AI, apparently. Political leaders and pundits including Bernie Sanders and Steve Bannon have put AI center stage, and the backlash against data centers is loud and inescapable. The specter of AI-driven layoffs hangs heavy—as does the threat of advanced hacking bots capable of taking down electrical grids and breaking into banks. All manner of once-speculative concerns about AI have become pressing matters. There is no longer a distant AI future so much as the mess we are all forced to confront today.
The newly chaotic and inescapable state of AI is the result of two inflection points. The first came at the start of the year, when AI agents exploded in popularity. Products such as Anthropic’s Claude Code and OpenAI’s Codex don’t just talk to you; they can do things on your behalf—code, trade stocks, analyze spreadsheets, generate slide decks, and even create Amazon listings. The technology’s once-questionable economic value became very clear, very quickly, to a large number of businesses, which have clamored to incorporate agents alongside, or in lieu of, their human employees. As agents have swarmed the workplace, nearly three-quarters of employed Americans think AI will decrease overall job opportunities and 30 percent of Americans are concerned that AI will make their own job obsolete.
The second shift began in late February. First, a high-profile contract dispute between Anthropic and the Pentagon revealed how essential AI has become to national security. Then, in early April, Anthropic announced Mythos, a model with the ability to rapidly find and exploit bugs throughout the internet. (Shortly after, OpenAI came out with an analogous model.) In tandem, these events suggest that some of the most catastrophic fears about AI could come true: Several independent cybersecurity experts have told me that these models are approaching the abilities of the most elite human hackers. Anthropic and OpenAI have not released these cybersecurity models to the public, out of fear they will be used by criminals or terrorists; meanwhile, companies and government bodies alike are hungering for access so they can use the tools to patch any bugs. As a result, AI labs have become major geopolitical actors in their own right.
Spurred by the threat of massive AI cyberattacks, the Trump administration is now reportedly weighing the possibility of testing or even licensing the most powerful AI models before their public release—moves the White House once called “dangerous” and “onerous.” White House Chief of Staff Susie Wiles is said to be spearheading Trump’s AI policy and has written a rare post on X vowing to keep Americans safe from AI cyberattacks by ensuring “the best and safest tech is deployed rapidly to defeat any and all threats.” (A White House official told me that “any policy announcement will come directly from the President.”) This month alone, dozens of members of Congress have signed letters to the White House on AI regulation.
It’s hard to overstate the extent to which AI has crept into contemporary life, even for people who aren’t commonly using the technology. A poll this spring showed that, for Americans, AI is growing in importance faster than any other issue. AI wasn’t a focus for campaigns in 2024, but several races coming up this year are poised to involve heated debates over the technology. Data centers in particular have gone from basically invisible to a divisive issue that cuts across party lines: 70 percent of Americans oppose the construction of an AI data center in their community. These centers’ voracious demand for natural resources might be showing up in your electrical or water bill or your receipt at the gas pump. Data centers have also become objects of military and political violence. Last month, the home of an Indianapolis city councilman was shot up after he voted to approve a data center. And these buildings have been targeted or threatened by Iranian, U.S., and Israeli forces during the war in the Middle East.
There will never again be a graduating class that experienced even a year of college without ChatGPT. On Instagram, Facebook, and X, influencers preach about how to use Claude and ChatGPT to make your life easier. Recent leaps in deepfake tools make it harder than ever to assume that any given post on social media is human-made. As if AI had not already eaten the economy, Anthropic and OpenAI are racing to be listed on stock markets in what will likely be two of the largest public offerings in history. This will dramatically warp the public-investing landscape and affect, for better and worse, basically anybody with any sort of savings—a college fund, a 401(k), a pension.
All of which is to say, basically anything that is American seems tangled up with AI: the war in Iran, gun violence, the midterms, NIMBYism, falling test scores, class inequality, the stock market, housing, gas prices. None of these issues are necessarily determined or superseded by AI—far from it—but rather, this technology and industry are now directly, unavoidably implicated in them all. And the experience of this AI-saturated present is a bewildering one. Partisan lines on AI are scrambled and confused. The influx of cash into data centers has propped up the U.S. economy, making it impossible for economists and policy makers to fully understand the effects of tariffs and the war with Iran. More and more companies are citing AI for mass layoffs, but whether this is a genuine justification or a convenient excuse to downsize is anybody’s guess. Whether AI is going to empower or rot all our brains, too, will only become evident many years from now. All these questions and tensions are hard to make sense of, let alone resolve, but they can no longer be deferred.
The path here was not the inevitable result of some technological, scientific, or economic law. Nor is continuing down it. To the extent we are already living in the AI future, it is the result of a series of calculated decisions by the biggest tech firms and their investors. Silicon Valley has spent ungodly sums on AI and data centers: Microsoft, Amazon, Meta, and Google alone have already spent more on data centers since the launch of ChatGPT than the federal government spent to build the entire interstate highway system. Those expenditures are set to grow, even as consensus opinions on whether all this spending constitutes an economic bubble fluctuate every few months. Meanwhile, AI companies have been hard at work partnering with local and federal government agencies, major colleges and research universities, Fortune 500 companies, and media organizations to weave their products into everyday life.
All of this spending and all of these partnerships were set in motion years before the technology was actually capable or reliable enough for widespread usage. Now these same companies are barreling forward to consummate their technological revolution. For everyone else, the AI future is beginning to feel less like something you participate in and more like something that happens to you.
Elon Musk and Sam Altman are two of the most influential people in Silicon Valley, if not the world. Between the two of them, Musk and Altman run technology companies worth many trillions of dollars that promise to reshape civilization. But this morning, both sat under fluorescent lights in a courthouse in downtown Oakland, suffering through all manner of technical glitches as their respective attorneys kicked off the long-awaited trial in Musk v. Altman.
As Steven Molo, a lawyer for Musk, began his opening argument, confused looks swept the courtroom. “We can’t hear you,” Judge Yvonne Gonzalez Rogers said. Someone fixed his microphone. Later, as Molo began to call into question Altman’s integrity, his microphone cut out again, and his presentation disappeared from screens in the room. (“We are funded by the federal government,” Gonzalez Rogers joked. “The judiciary is happy to take more funds.”)
Musk is suing Altman and OpenAI, among others, demanding legal and financial remedies that would effectively destroy OpenAI as we know it. The fight stretches back to 2015, when Musk partnered with Altman to create OpenAI out of concern, as they told it, that Google DeepMind could not be trusted to create artificial general intelligence. Corporate greed would get in the way of societal progress, they claimed, so OpenAI would be a nonprofit. After a falling out with Altman and other co-founders, Musk left in 2018. All of this was before OpenAI added a for-profit entity, and before ChatGPT became the fastest-growing consumer app in history. In 2024, Musk sued, alleging that by putting profits above its founding mission, OpenAI had violated its founding charter and misused Musk’s initial charitable donations. “It’s very simple,” Musk testified today. “It’s not okay to steal a charity.” Also named in his complaint are the OpenAI co-founder Greg Brockman and Microsoft, a major investor in the company.
Musk is asking that Altman be removed from OpenAI’s board, that the company convert back to a nonprofit, and for the return of allegedly “ill-gotten gains”—some $150 billion—which Musk says would go to OpenAI’s charitable trust. Outside legal experts say that Musk is unlikely to win all or even much of this. His argument is confusing: OpenAI has certainly evolved from a nonprofit lab to a revenue-chasing, consumer behemoth, and a chorus of critics has alleged that it has deviated from its original mission of ensuring that AGI benefits humanity. But Musk himself appears to have insisted that OpenAI couldn’t keep up as a nonprofit—for instance, in early 2018, he wrote an email to OpenAI leadership saying that merging the firm with Tesla “is the only path that could even hope to hold a candle to Google.” And even before he sued, Musk launched a rival for-profit company, xAI. “Mr. Musk’s lawsuit is a pageant of hypocrisy,” William Savitt, a lawyer for OpenAI, told the jury today, later adding that Musk had “sour grapes.” (OpenAI, which declined to comment, wrote yesterday that the lawsuit is “a baseless and jealous bid to derail a competitor.” Musk’s legal team did not respond to a request for comment.)
The substance of these claims is important to the AI industry as a whole. The ramifications of this lawsuit go beyond any company or executive: The conflict between Musk and Altman has itself directly shaped the course of the AI industry. It is, in effect, the AI boom’s founding feud. The next few weeks of the trial will illuminate tensions about the development of AI that have grown only more urgent—between profit and social good, and over who can be trusted with this technology.
Already, the pretrial process produced no shortage of drama. Both sides published internal communication between Musk and OpenAI leadership. OpenAI shared texts suggesting that Musk had used a former member of OpenAI’s board to keep tabs on the company. (That board member, Shivon Zilis, has multiple children with Musk, and in her deposition said that she is in a romantic relationship with him; asked about Zilis today, Musk said she was “my chief of staff and uh, well, yeah,” smirking.) Musk’s alleged ketamine use during important OpenAI negotiations, which he has said he does not recall, became a key issue until, in a recent pretrial hearing, Gonzalez Rogers deemed this line of inquiry irrelevant.
The trial makes the AI boom seem sordid and small. In his sworn deposition, Altman wrote that Musk used to message him complaints that he wanted more credit for the success of OpenAI and took offense at not being included in an anniversary photo. Altman has also said, of Musk and his lawsuit, “Probably his whole life is from a position of insecurity. I feel for the guy.” In the courtroom, Altman sat stone-faced next to Brockman and departed right before Musk took to the witness stand.
Musk, for his part, has said that he would drop his lawsuit if OpenAI changed its name to “ClosedAI.” Yesterday, as jury selection began, Musk began furiously posting on X and repeatedly called his co-founder “Scam Altman.” Before the start of opening arguments today, Gonzalez Rogers admonished Musk and Altman for their social-media use, asking them to limit their “propensity” to post about the trial; both meekly assented, “Yes.”
Now we are all living in the fallout of Musk and Altman’s vendetta. Disagreements over the direction of Google DeepMind led to the creation of OpenAI, and then more disagreements led Musk to found xAI. Similarly, a few years ago, Dario Amodei and six other OpenAI employees split off to form a competing AI company, Anthropic, themselves trusting neither OpenAI’s structure nor its leadership to prioritize the benefit of humanity over financial gain. And there’s Mark Zuckerberg, whom Musk asked about joining forces to purchase OpenAI in 2025, according to texts released in pretrial discovery. (Meta previously declined to comment.) Zuckerberg has since spent tens or even hundreds of billions of dollars overhauling the AI team at Meta in a bid to catch up in the AI race. The very sort of AI schism that started with Musk and Altman keeps recurring.
A more cynical description of this dynamic is that the AI boom is shaped by a very small group of men, nearly all of whom claim to be the best steward of humanity while being largely dismissive of their competition. At the same time, the goal of creating an organizational structure, whether nonprofit or corporate, to provide a check on a CEO has all but withered away. An independent board was supposed to govern OpenAI, but the company has basically been Altman’s fiefdom—just as Anthropic is Amodei’s and xAI is Musk’s. Grok has at times explicitly aligned its responses with Musk’s political views by mimicking his social-media posts.
Both sides have made the issue of concentration of power—that no one company or person should control such a transformative technology—central to their arguments. “If you have someone that’s not trustworthy in charge of AI,” Musk testified, “I think that’s very dangerous to the whole world.” The defense, meanwhile, said that “one person having control wasn’t consistent with OpenAI’s core mission.” Apparently, the irony was lost on everyone.
This trial will offer the clearest glimpse into an elite circle whose bickering is shaping the most expensive infrastructure buildout in human history in the name of a technology that could upend the labor market, spell the end of education as we know it, and reshape the geopolitical order. That is, as long as the microphones keep working.
OpenAI does not like to be left out. The week after Anthropic announced Claude Mythos Preview—an AI model that has put governments around the world on edge because of its potential ability to hack into banks, energy grids, and military systems—OpenAI shared a program that is uncannily similar. And just like Anthropic did with its model, OpenAI has, for cybersecurity purposes, restricted access to this new bot, called GPT-5.4-Cyber, to a small group of trusted users.
This sequence has become something of a pattern: First Anthropic will make an announcement, and then OpenAI will follow suit. Last year, Anthropic launched Claude Code, an AI coding tool. A couple of months later, OpenAI came out with its own version, Codex. When Claude Code had a breakout moment in January, OpenAI responded with two major updates to Codex alongside a press blitz for the product. And earlier this month, OpenAI released a version of Codex that allows it to use other apps on your desktop—similar to an existing Anthropic tool called Claude Cowork.
Until recently, Anthropic—founded by a group of former OpenAI employees in 2021—played the role of younger brother. OpenAI kicked off the entire AI boom with the release of ChatGPT, and has had more users, funding, and name recognition ever since. But Anthropic has been riding high on the explosive popularity of Claude Code and booming sales of its AI models to large corporations. The firm’s showdown with the Pentagon has also helped vault it into the public eye. In early April, Anthropic said its revenue rate had hit $30 billion a year—appearing to surpass OpenAI’s.
In its public messaging, OpenAI has been indifferent or even somewhat derogatory toward Anthropic. Last week, when OpenAI released its newest model, GPT-5.5, the announcement was paired with direct and veiled references to how it beat out Anthropic’s latest, Claude Opus 4.7. But internally, the firm is seemingly on edge. In a recent leaked company-wide memo, Denise Dresser, OpenAI’s chief revenue officer, felt the need to address one particular competitor: “Here are a few things worth keeping in mind, especially on Anthropic.” The rival firm’s product offerings are narrow, Dresser wrote, and “their story is built on fear,” referencing Anthropic’s loud messaging about the dangers of AI. “Our positive message will win over time.” (OpenAI, which has a business partnership with The Atlantic, did not respond to a request for comment. Anthropic also did not respond to a request for comment.)
If imitation is the sincerest form of flattery, OpenAI’s actions are especially telling. At every turn, OpenAI has appeared eager to copy the success of its rival. For starters, as Anthropic’s explicit focus on mitigating the risks of AI has apparently won the trust of many consumers, OpenAI has imitated many of its rival’s safety initiatives. In early 2026, after Anthropic published a major update to Claude’s “Constitution,” a document that tells the AI model how to behave, OpenAI launched a major campaign around its equivalent document.
But OpenAI’s most important, Anthropic-esque pivot has been in its business model. Early on, these two companies made fundamentally different bets on how they would eventually make money. OpenAI positioned itself as a consumer behemoth, hoping to capitalize on ChatGPT’s hundreds of millions of users. Last fall, the company launched the AI-video app Sora and an AI-powered web browser. OpenAI has made forays into e-commerce and is testing ads in ChatGPT. Every now and then, the company teases the AI device that it is developing with the former Apple designer Jony Ive. Anthropic, meanwhile, has focused on the less flashy goal of selling its AI tools to businesses and software engineers.
Despite OpenAI’s numerous advantages, Anthropic’s focus on code and business customers seems to be winning. Although OpenAI is worth more based on the most recent fundraising rounds, Anthropic now has a higher valuation—more than $1 trillion—in some private markets. Anthropic’s explosive growth is particularly important as the two companies both race to go public, in turn accessing a huge pool of new investors, and try to prove they will eventually be profitable. (Both companies still have a long way to go in that regard.)
OpenAI is now eager to catch up. In December, OpenAI hired Dresser, a former CEO of Slack, to pursue more business customers. In late January, Altman gathered several major executives for a lavish dinner in San Francisco to preview all of the business offerings his company was planning, according to The Information. The company has since made a blitz of announcements around coding tools and enterprise AI offerings, including a new set of “Frontier Alliances”: partnerships with several of the world’s premier consulting firms, including McKinsey & Company and Boston Consulting Group, to accelerate enterprise adoption of ChatGPT. In mid-March, another internal OpenAI memo reportedly stated that the company needed to eliminate “side quests” and focus on the enterprise and coding markets. Anthropic’s success in those areas, the memo stated, should be a “wake-up call” for OpenAI. The firm also scrapped Sora and has been aggressively advertising and messaging about Codex for months now. “I am happy everyone is switching to Codex,” Altman wrote on X earlier this month.
OpenAI’s pivot to its enterprise business has not been total. It did, for instance, recently shell out reportedly hundreds of millions of dollars to acquire a niche tech podcast. And Anthropic, for its part, has had to take some cues from OpenAI—notably by making big and expensive data-center deals, such as an expansion in its partnership with Amazon Web Services. Anthropic’s CEO, Dario Amodei, has previously insinuated that OpenAI has made such deals “because it sounds cool.”
Which company will win the AI race is anybody’s guess. Regardless, OpenAI’s embrace of the Anthropic business model makes one thing abundantly clear: For all the wonder and change that generative AI brings as a technology, there hasn’t been any real innovation in the business models of Silicon Valley. For decades, most tech companies have succeeded by either selling ads (the route of Meta and Google) or selling enterprise tools (like Salesforce and Slack). One day OpenAI or Anthropic might cure cancer and remake the world, but for now they still have to pay the bills.
AI companies are beginning to entertain the possibility that they could cease to exist. This notion was, until recently, more theoretical: A couple of years ago, an ex-OpenAI employee named Leopold Aschenbrenner wrote a lengthy memo speculating that the U.S. government might soon take control of the industry. By 2026 or 2027, Aschenbrenner wrote, an “obvious question” will be circling through the Pentagon and Congress: Do we need a government-led program for artificial general intelligence—an AGI Manhattan Project? He predicted that Washington would decide to go all in on such an effort.
Aschenbrenner may have been prescient. Earlier this year, at the height of the Pentagon’s ugly contract dispute with Anthropic, Secretary of Defense Pete Hegseth warned that he could invoke the Defense Production Act (DPA), a Cold War–era law that he reportedly suggested would allow him to force the AI company to hand over its technology on whatever terms the Pentagon desired. The act is one of numerous levers the Trump administration can pull to direct, or even commandeer, AI companies. And the companies have been giving the administration plenty of reason to consider doing so.
Future bots could help design and carry out biological, nuclear, and chemical warfare. They could be weaponized to take down power grids, monitor congressional emails, and black out major media outlets. These aren’t purely hypothetical concerns: Earlier this month, Anthropic announced it had developed a new AI model, Claude Mythos Preview, capable of orchestrating cyberattacks on the level of elite, state-sponsored hacking cells, potentially putting a private company’s cyber offense on par with that of the CIA and NSA. In an example of Mythos’s power, Anthropic researchers described how the model used a “moderately sophisticated multi-step exploit” to work around restrictions and gain broad internet access, then emailed a researcher—much to his surprise—while he was eating a sandwich in the park.
Washington is getting antsy about the power imbalance. Over the past year, multiple senators have proposed legislation that would order federal agencies to explore “potential nationalization” of AI. Murmurs of possible tactics abound—including more talk within the administration of the DPA after Anthropic’s Mythos announcement, one person with knowledge of such discussions told us. Meanwhile, Silicon Valley is watching carefully. In recent weeks, Elon Musk, OpenAI’s CEO Sam Altman, and Palantir’s CEO Alex Karp have publicly spoken about the possibility of nationalization. Lawyers who represent Silicon Valley’s biggest AI firms are paying attention.
So what if nationalization actually happens?
In the most extreme scenario, top researchers from across the AI companies would be forced to work out of SCIFs in the basement of the Pentagon and report to Hegseth. Computational capacity, too, would be centralized under one nationalized mega-operation. The work would be locked down, and the focus would be primarily on defense applications, as opposed to the products made for businesses and individuals—ChatGPT and the like—that dominate the market today.
All of this would constitute full nationalization, an absolute takeover of the industry that would hollow out the commercial businesses of its three leading players: OpenAI, Anthropic, and Google DeepMind. Based on a dozen conversations we’ve had with former Pentagon and Trump-administration officials, AI-policy experts, and legal scholars, such a situation is, in all likelihood, not going to happen.
For starters, it’s probably illegal, according to Charlie Bullock, a senior research fellow at the Institute for Law & AI: The Constitution generally prevents the government from seizing private property without paying, and the government is unlikely to easily produce the trillions of dollars that the industry is collectively worth. The top American AI labs might immediately lose a fair portion of their research staff as well, because of restrictions on foreigners who can work on the most crucial defense-related technologies.
If AI firms were forced to focus primarily on defense applications, there would be the inevitable question of what to do with the massive consumer businesses these companies run. Would people use ChatGPT.gov, like buying a sundae from Cuba’s state-run ice-cream parlor? And if the goal of nationalization is to keep a competitive edge over China, it’s hard to imagine that Hegseth’s Pentagon could run an AI company more efficiently than Altman or Dario Amodei, the CEO of Anthropic.
But consider another possibility—slightly less extreme, though still capable of remaking the industry as we know it. The government could regulate AI companies like it does utilities. In the 1900s, as electricity went from a luxury good to a necessity, state and federal governments saw a need to regulate how much energy companies charge and to impose requirements around service reliability. In much the same way, the government could pass new laws regulating AI firms’ commercial activities. The companies could be prevented from charging more than it costs to generate images and text, for instance, or required to provide a basic level of model speed and capabilities to all customers, a sort of AI net neutrality.
A hard pivot to government control would likely entail both new state and federal laws, as well as heavy cooperation from tech companies—which, given the nation’s sclerotic politics and Silicon Valley’s libertarian leanings, could pose insurmountable barriers. But the notion is not so far-fetched. Some corners of Silicon Valley itself seem to be at least partially open to it. Altman has described a future in which “intelligence is a utility like electricity or water and people buy it from us on a meter.” Jensen Huang, the CEO of Nvidia, recently said that just as “every country has its electricity, you have your roads, you should have AI as part of your infrastructure.”
Such talk serves AI companies’ own interests—in part because being classified as a service provider can be, as the era of social media has demonstrated, an excellent way for companies to avoid liability for harmful or inaccurate information on their platforms—but it’s certainly possible that AI could become so entrenched that elected officials come to see it as an essential resource. Already, just as the federal government uses regulatory incentives and investment to spur the construction of new power plants and transmission lines, both the Biden and Trump administrations have undertaken initiatives that are essentially industrial policy for AI, using federal dollars and regulatory authority to accelerate the construction of AI infrastructure on American soil.
OpenAI has already flirted with the notion of a “Right to AI,” suggesting in a recent policy document that the government should consider making a “baseline level of capability broadly available, including through free or low-cost access points.” Similar regulations already govern many aspects of digital communication. “Your internet-service provider, cable, telephone services, these things are considered so essential that the government basically says how the providers” can do business, Dean Ball, a former AI adviser to the Trump administration, told us. AI could be next.
For years, AI companies have insisted they need to be regulated—but only as theysee fit. Should the federal government ever take AI regulation seriously, the utility route would be among the most aggressive approaches available. But, really, the AI industry would be getting what it asked for.
Illustration by The Atlantic. Sources: Daniel Heuer / Bloomberg / Getty; Krisztian Bocsi / Bloomberg / Getty; Mark Schiefelbein / AP.
Before we get into other conceivable futures, an important caveat. A full-blown nationalization effort may be unlikely, but that changes if a major global war breaks out or the economy collapses. During an emergency of historical scale, Ball reminded us—especially an emergency under the Trump administration—anything is possible. Drastic measures become easier to justify, both legally and politically.
Imagine that over the next year President Trump continues his game of imperialist roulette: America is further eroding the trust of its international partners, NATO keeps crumbling, and a new geopolitical reality continues to take shape. Say that in the midst of this, China decides to invade Taiwan. The conflict escalates fast, drawing in the U.S. and reluctant allies. The ensuing war is a major one. The Pentagon, already drastically short on munitions after its forays in Iran, wants to apply the latest AI capabilities to its wartime efforts, and Hegseth demands that Anthropic allow the Pentagon unrestricted access to Claude, reigniting the dispute first set in motion earlier this year.
Because there is active conflict, Anthropic is more willing to engage with the government’s demands than they were previously, but the firm asserts that it requires continuous oversight into how the Pentagon is using Claude. The company fears that in an effort to crack down on espionage, the Defense Department might create monitoring capabilities that supersede even the Chinese Communist Party’s, sliding America into an autocratic AI regime. Lest this sound speculative, it’s merely a restatement of Anthropic’s own position: Amodei has warned of a near future where “a powerful AI” scans “billions of conversations from millions of people” to “gauge public sentiment, detect pockets of disloyalty forming, and stamp them out before they grow.”
The spat from earlier this year looks mild by comparison. Amodei remains stubbornly principled despite repeated requests from the Defense Department made under emergency laws. Hegseth responds by sending his troops to descend upon the company’s headquarters in San Francisco. Amodei is forcibly removed and replaced with a deferential Army general. The situation is exceedingly unlikely, but not without precedent: Soldiers once carried the chair of one of America’s largest retailers out from his Chicago office after he failed to comply with federal demands during World War II.
Throughout American history, efforts to take control of industry have been rare, and limited mostly to times of crisis: President Woodrow Wilson nationalized the railroads during World War I, and Fannie Mae and Freddie Mac were placed under conservatorship during the financial crisis. Today, there are all kinds of possible emergencies. If a global financial crash leads AI companies to insolvency, the administration might swoop in to provide life support, as it did for many banks and car companies during the Great Recession. On the flip side, should AI models displace large swaths of the labor market, such that a handful of companies run most of the economy, “then some kind of nationalization becomes potentially imperative,” Samuel Hammond, the acting director of AI policy and chief economist at the Foundation for American Innovation, told us—to distribute wealth and simply ensure the proper functioning of society. Both Anthropic and OpenAI have already suggested possible versions of such redistributive measures.
Advances in AI could be their own kind of disrupter: Imagine a Sputnik 2.0 moment where the White House decides that American companies need to consolidate resources if the U.S. wants to win the AI race against China. By exerting more control, America becomes more like China in the very race to beat it.
The thing about nationalization, though, is that it need not be all or nothing. Nationalization “has layers,” Hammond said. “Like an onion.” Perhaps the most likely fate for American AI companies is a future of soft nationalization—a world in which the government doesn’t fully control AI labs and their models, but instead enacts an escalating series of policies and established close partnerships with private companies to shape the technology.
By some measures, soft nationalization has already begun. The Trump administration has already taken a 10 percent stake in Intel, a major semiconductor manufacturer, providing the White House with (some) direct financial leverage over the company. OpenAI has appointed the retired general and former NSA director Paul Nakasone to its board. Meanwhile, the Army recently established a new detachment for senior tech leaders, and its first four recruits included executives from Meta, Palantir, and OpenAI.
The top AI companies are coordinating with government officials as their products’ military and intelligence implications advance. OpenAI, which scooped up a contract with the Pentagon after Anthropic’s fell apart, has said it will deploy its own engineers to work alongside the military. The firm has also been briefing governments—at the state, federal, and international levels—on the capabilities of a new OpenAI cybersecurity model. Google is reportedly negotiating its own Pentagon contract to allow Gemini to be used in classified settings. And even Anthropic is coming back around. The company is fighting the Pentagon in court over a “supply-chain risk” designation that Hegseth slapped on them amid their dispute. But after Anthropic announced its Mythos model, a group of tech executives including Amodei spoke with Vice President Vance and others to discuss the risks, and Amodei took a trip to the White House. Last week, President Trump said a possible Pentagon deal with Anthropic might still be on the table.
The White House, OpenAI, and Anthropic all paid lip service to the value of cooperation when we reached out to them. The Trump administration is “working with frontier AI labs to discuss opportunities for collaboration,” a White House official told us. A spokesperson for OpenAI said: “As AI systems become more capable, it is only going to become more important for industry to work with governments.” And an Anthropic spokesperson told us that Amodei’s recent visit to the White House was “productive” and that the firm believes that governments must play a central role in addressing the technology’s national-security implications. (Google DeepMind and the Pentagon did not return repeated requests for comment.)
This campfire ethos could easily fall apart. And clearly, tensions exist. But so long as it’s in both the AI firms’ and Trump’s interests to please each other, we may see the leading AI companies partnering even more closely with the U.S. military to accelerate the development of defense applications, analogous to what contractors including Palantir, Boeing, and Lockheed Martin have done for years. As a protective measure, the White House might ask AI companies to increase their security practices to prevent espionage and exfiltration of the most capable versions of the technology (consider that a handful of unauthorized users have reportedly gained access to Mythos). The government could even designate certain research as classified and subject technologies to export controls, and federal employees could embed inside the companies to oversee various safety measures and run their own, independent evaluations. Every nuclear power plant in America has at least two on-site government inspectors who check daily to confirm compliance with federal safety requirements. So why not AI companies too?
If such partnerships persist, one could imagine private companies resisting certain government demands. But even without new legislation, the White House can easily exert greater authority over industry. “There’s quite a lot of power that the federal government can wield,” Paul Scharre, an executive at the Center for a New American Security who previously did policy work at the Department of Defense, told us. “And even more so if you have an administration that’s willing to stretch the bounds of executive power.” Anthropic’s supply-chain-risk designation—a label that effectively bars the military from doing business with the company, and that is typically reserved for companies with ties to foreign adversaries—was a clear example of the government flexing its muscles. So was the Biden administration’s decision to block Nvidia from selling its most advanced AI chips to China in 2022. (The Trump administration has since relaxed restrictions, claiming that selling to China was the better strategy for winning the AI race.)
One of the most salient tools available remains the Defense Production Act, the law that Hegseth threatened Anthropic with before pursuing the supply-chain-risk designation. The act has been used over the decades to support the manufacture of military equipment such as bombers and tanks, though in recent years, it has been used more expansively. Both the first Trump and the Biden administrations used it to accelerate pandemic safety measures, and Biden relied on the law in a since-repealed executive order to compel AI companies to share certain information about model training and evaluations with the government. Last week, Trump invoked the act to fund new energy projects. Actually pursuing the DPA as a general tool for controlling AI companies would raise a host of thorny legal issues, but that hasn’t exactly stopped the Trump administration in the past.
Such reins on an industry that has billed itself as capable of extinguishing humankind are, theoretically, in everyone’s interest. It would seem to clearly benefit the American people to have democratically elected institutions—rather than corporate executives—overseeing a set of technologies with huge implications for the nation’s security and well-being. It’s also historically anomalous for a private industry to dictate the deployment of such a powerful, general-purpose technology. With the announcement of Mythos, Anthropic has been effectively functioning as a geopolitical actor, briefing ally governments on the model’s capabilities. The European Commission, for instance, has met with Anthropic thrice since Mythos was announced—although as of Wednesday, the company had not yet given European Union officials access.
The government should play a role in dictating the terms of how AI transforms the world. But the ongoing fracturing of American politics, and especially the capricious and authoritarian-leaning tendencies of the current administration, complicates everything. Entrusting the future of generative AI entirely to Altman and Amodei or Trump and Hegseth seem like two very different and similarly disastrous outcomes—a “Scylla and Charybdis” dynamic, as Bullock put it, between the tremendous concentration of power in government or in a small cadre of companies.
The impossible truth is that no private company should be trusted to unilaterally steer the future of AI development, but Americans should also have serious questions about whether government control is in their best interest—not least of all under an erratic and norm-shattering Trump administration. The Manhattan Project coordinated the efforts of scientists, private companies, and America’s leaders. What if instead, Boeing and DuPont had been racing against each other to develop the atomic bomb while Hegseth and Trump led the military? We are diving headfirst into the 21st-century equivalent of such a situation. Our political dysfunction is about to ram into Silicon Valley’s immeasurable power.

 Login