❌

Reading view

“The Lord of the Rings: The Hunt for Gollum” Will Use AI to De-Age Actors

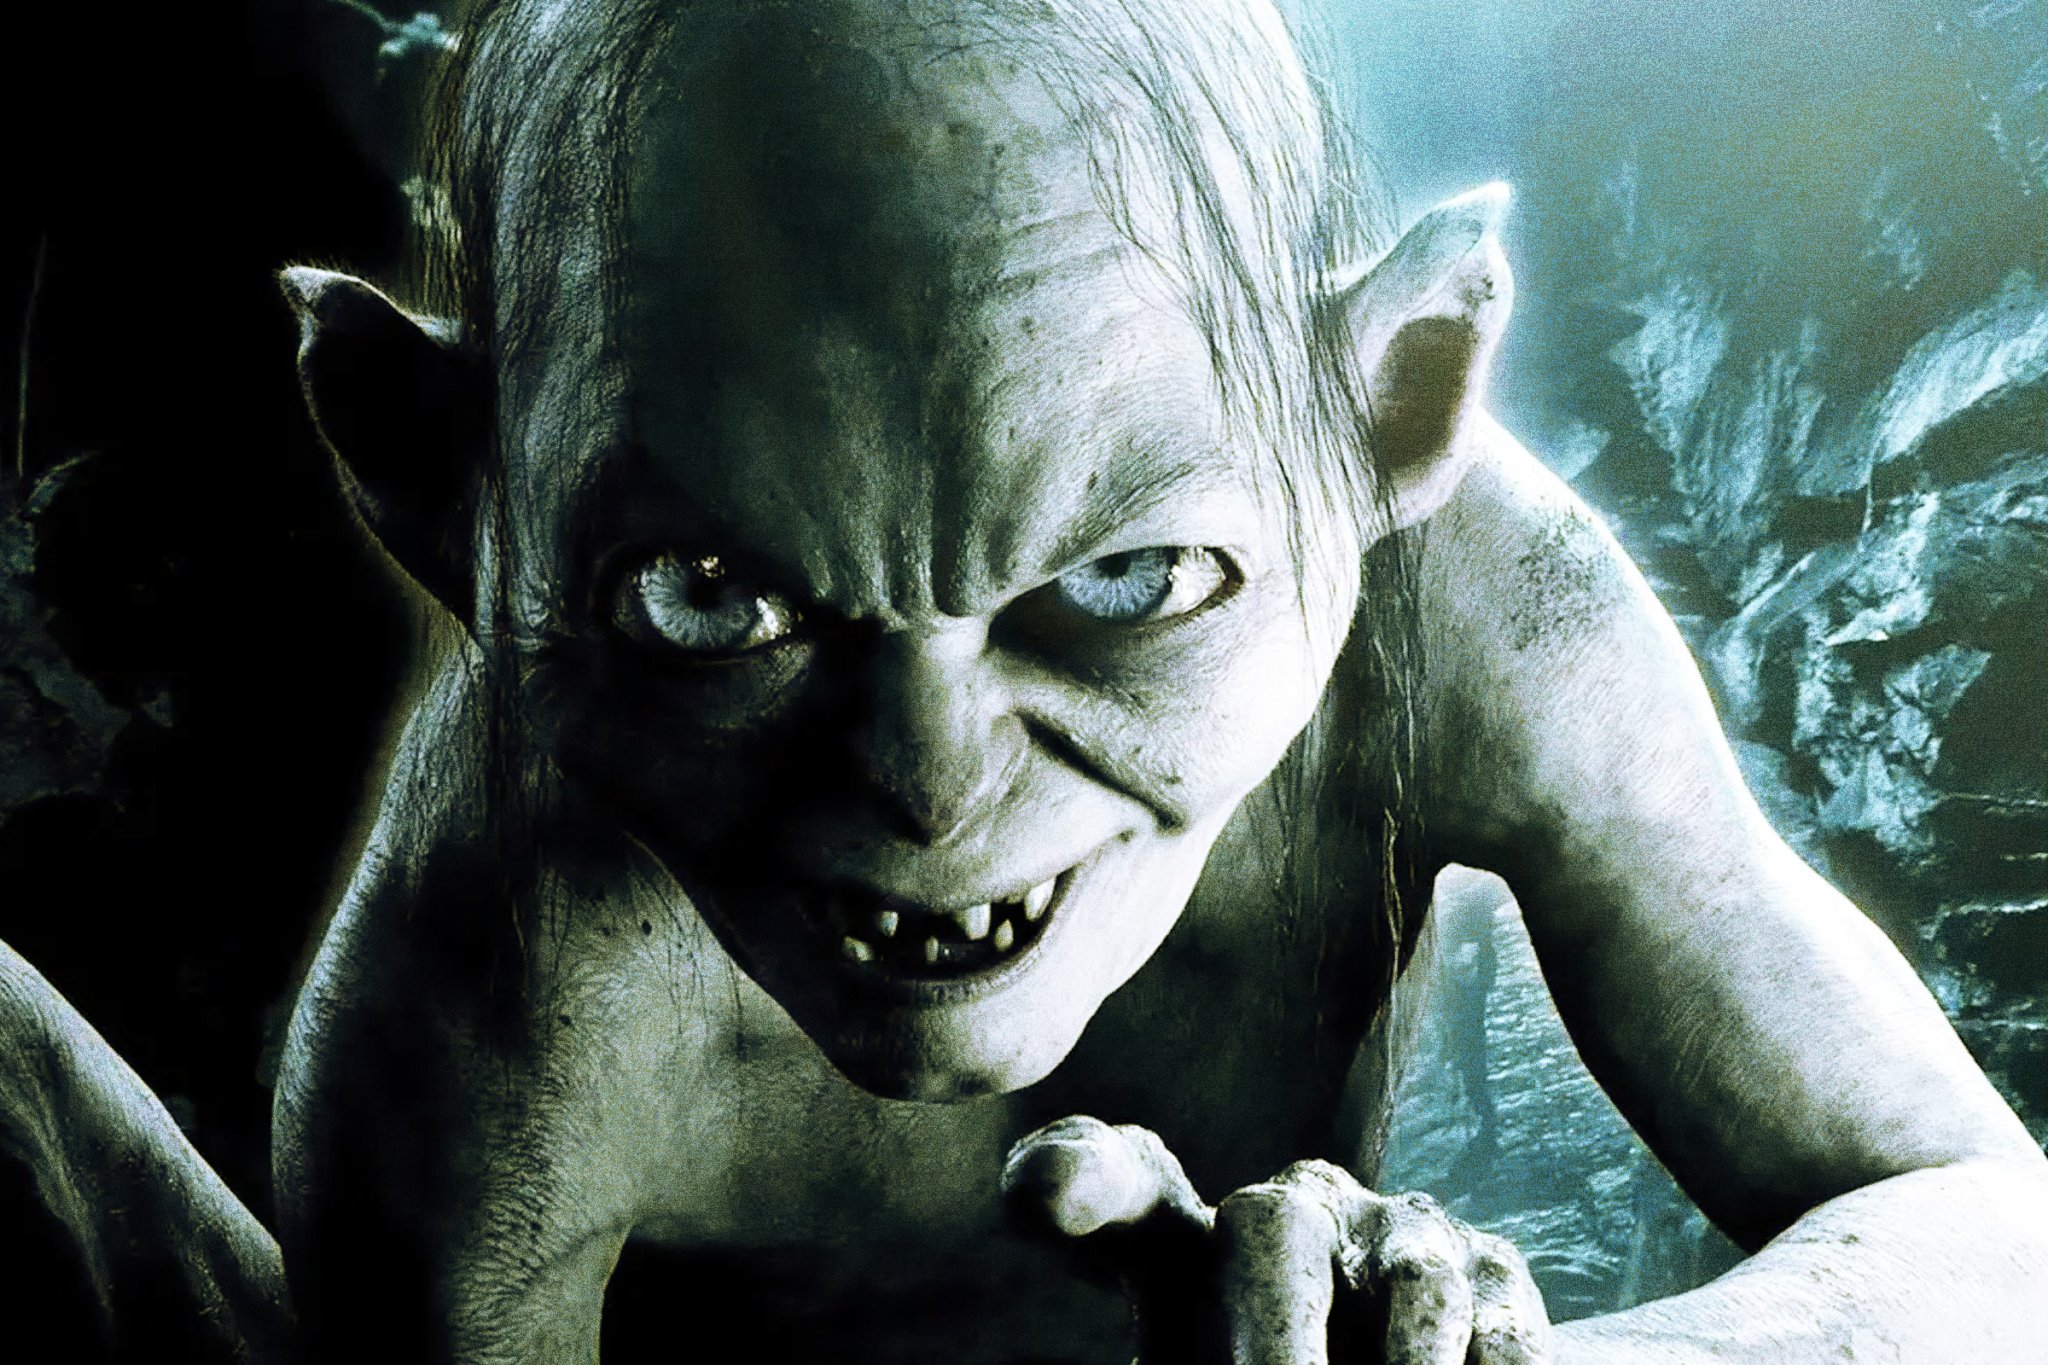
“The Lord of the Rings: The Hunt for Gollum,” will de-age actors using AI, the actor and director Andy Serkis confirmed to Variety.

“There’s a little bit of de-aging for some of the characters and machine learning is part of the process,” Serkis, who is both directing the new film and reprising his famous role as Gollum, told Variety.

AI is an incredibly contentious topic in Hollywood. Some studios, like A24, have leaned into generative AI. Others in the industry, from actors to directors and writers, have lambasted the tech, with many fearing that AI will be used to replace industry jobs or simply result in lower-quality work. As the tension between the pro-AI and anti-AI — or perhaps AI-resigned — factions deepen, the industry and its leaders, Serkis included, are publicly grappling with the technology and what it means for a key creative industry.

In addition to Serkis, returning actors from past films include Elijah Wood as Frodo, Ian McKellen as Gandalf, and Lee Pace as Thranduil — all of whom are markedly older than when the original “Lord of the Rings” trilogy and the prequel franchise “The Hobbit” were filmed. Beyond de-aging, though, Serkis said that “at present,” there are no other plans to use AI in the making of the new movie.

“We’re not creating AI shots in our movie, every shot is created in a traditional way,” said Serkis. “One of the things actually that I really wanted to do with this film was to bring back all of the great filmmaking skills, from miniatures to prosthetics and marry them up, because that’s my taste.”

Serkis didn’t nix the idea of using AI altogether. He noted that Peter Jackson, who famously directed the previous live-action movies in the celebrated franchise, worked with the software engineer Stephen Regelous to develop the AI-powered special effects software known as MASSIVE back in the early 2000s.

“When you think about it, in the original ‘Lord of the Rings’ films, Peter created MASSIVE, which was a program which allowed thousands of orcs to all have their own individual mindset,” said Serkis. “So that is a brilliant example of an incredible use of AI.”

He added that AI can be a “valuable” creative tool “as long as it’s not exploitative and as long as it’s not harming anybody or defaming anybody or telling mistruths.”

“When it becomes exploitative and people are not remunerated for the work that they’ve done, or it’s used in nefarious, or mean-spirited or pornographic ways, then of course, that’s terrible and we’ve only brought it upon ourselves,” he added. “I’ve said this before and I mean it — we are the parents of AI, and we have to be good parents and teach AI well. And if we teach AI well, then it can help us across many industries.”

As The Tab noted, many Lord of the Rings fans responded positively, drawing a line between machine learning-infused virtual effects software and generative AI tools that churn out text, audio, and imagery.

“AI is perfect for de-aging,” wrote one commenter. “It should get a complete and utter free pass for that. Having an artist sit and de-age someone must be a horrific chore. Let them work on something fun instead.”

“Every single VFX tool these days uses AI for some part of the processing,” added another. “This isn’t generative AI.”

Other famous filmmakers’ AI stances, meanwhile, haven’t received the same warm reception from fans.

More on AI and movies: Film Community Aghast as Martin Scorsese Extolls AI Startup, Says He Now Uses AI for Storyboards

The post “The Lord of the Rings: The Hunt for Gollum” Will Use AI to De-Age Actors appeared first on Futurism.
  •  

Top Meta Exec Describes Controversial Facial Recognition Feature in Detail After the Company Claimed It Didn’t Exist

Meta executives claimed that a controversial facial recognition feature didn’t “exist.” Fast forward a few weeks later, and they’re describing the feature in public — and in detail.

In June, a Wired investigation revealed that Meta had quietly infused unreleased facial recognition tech into its “AI Glasses,” the tech giant’s chatbot and camera-equipped smart glasses. While the feature, dubbed NameTag, was inaccessible to consumers, it was designed to register faces encountered by Meta glasses wearers “into unique biometric signatures, commonly known as faceprints, and check each one against faceprints stored on the user’s phone,” according to the magazine.

It’s safe to say that Meta executives were furious after Wired published its investigation. After all, the company has a long track record of data privacy violations. The revelation that its “pervert glasses,” as some have taken to calling Meta’s controversial smart glasses, could soon be using facial recognition tech — not unlike the eyewear being used by Immigration and Customs Enforcement (ICE) agents — fueled an existing PR disaster.

Andy Stone, the tech giant’s spokesperson and VP of communications, declared on X that Wired’s reporting was “intellectually dishonest” and “advocacy-driven click bait.” What’s more, according to Stone, NameTag was fully nonexistent.

“Here’s a thing: Wired reports Meta didn’t answer several questions about how this will work,” Stone added in a follow-up post. “How could we? The feature doesn’t exist!”

In response to Stone, another Meta executive, chief technology officer Andrew “Boz” Bosworth, jumped in.

“Incredibly misleading from Wired,” he wrote. “Absolutely dishonest.”

Yet despite company leaders reassuring us that the feature doesn’t exist, Bosworth discussed it in detail during an interview with The Atlantic CEO and podcaster Nick Thompson. Bosworth’s comments in the interview, which was published last week, seemingly contradicted his fellow executives, revealing that the feature did indeed exist.

NameTag, Bosworth told Thompson, would be “encrypted locally to your device,” and would catalog people who smart glasses wearers “met in person, with your glasses on, who introduced themselves, or you said, ‘okay, this is David, remember this person.'”

This information is “only available to you, when you are wearing your glasses,” Bosworth added. He emphasized that the data captured by NameTag wouldn’t be stored in a centralized database.

“This is a person you’ve met before. Here’s their name. They’re right in front of you. That’s… what we call a NameTags feature,” said Bosworth. “I think people get confused because they hear face recognition and they think, ‘oh, there’s a central face database that everyone’s being scanned constantly into.’ It’s not that.”

In addition to supporting blind or low-vision smart glasses wearers, said Bosworth, NameTag could solve what Meta calls “the cocktail party problem,” saving wearers from any awkwardness that may arise when encountering people at parties who they’re sure they’ve met before, but can’t quite place.

“It’s a very universally human problem,” Bosworth said. “Nearly every human I talk to, no matter what their status of their vision or their memory, understands that this is a problem that would help them feel more comfortable in social situations if they had it.”

To be clear, Wired never suggested that the facial recognition feature it uncovered was being used to build a “central face database” by way of Meta’s smart glasses. Indeed, in line with what Bosworth said in the podcast appearance, Wired reported that “code discreetly added to Meta’s AI app over multiple updates this year shows that the feature, internally called ‘NameTag,’ identifies people captured by the glasses’ camera and, when activated, alerts the wearer when it recognizes someone.” The story also repeatedly noted that the feature was unreleased and inaccessible to glasses wearers.

When journalists and others called out the contradiction between Meta’s past and recent statements, Stone — the comms executive who said that Wired couldn’t answer questions about the feature because it “doesn’t exist” — jumped back in the comments section.

“We have said for months we’re exploring such features, even as nothing has shipped to consumers,” the spokesperson said in response to a post by The Intercept journalist Sam Biddle. “No secret there despite the conspiratorial thinking.”

There’s a big difference between a feature not existing and a feature that exists — if still unfinished — and has yet to be released. Meta appears to be arguing that if a feature remains inaccessible to consumers, it’s technically nonexistent, even if the company has gone as far as to issue multiple updates inserting code for the feature into products that are already in consumers’ hands. (Meta quietly deleted the NameTag code after its existence was made public.)

During the podcast interview, Bosworth took care to emphasize that Meta is considering the privacy implications of a facial recognition-powered feature like NameTag. He noted that it’s likely illegal in states like Illinois and Texas, and that it “has to be done in a way that people feel comfortable.”

Meanwhile, Meta continues to fight an ongoing consumer harm lawsuit, prompted by an investigation by a pair of Swedish newspapers. The publications found that Meta collected recordings by smart glasses wearers and passed them along to human data labelers, despite promising consumers that their recordings would be stored only on their devices.

“Designed for privacy,” reads a webpage for Meta’s smart glasses, “controlled by you.”

More on Meta’s smart glasses: Meta Furious Over Bombshell Smart Glasses Revelation

The post Top Meta Exec Describes Controversial Facial Recognition Feature in Detail After the Company Claimed It Didn’t Exist appeared first on Futurism.

  •  

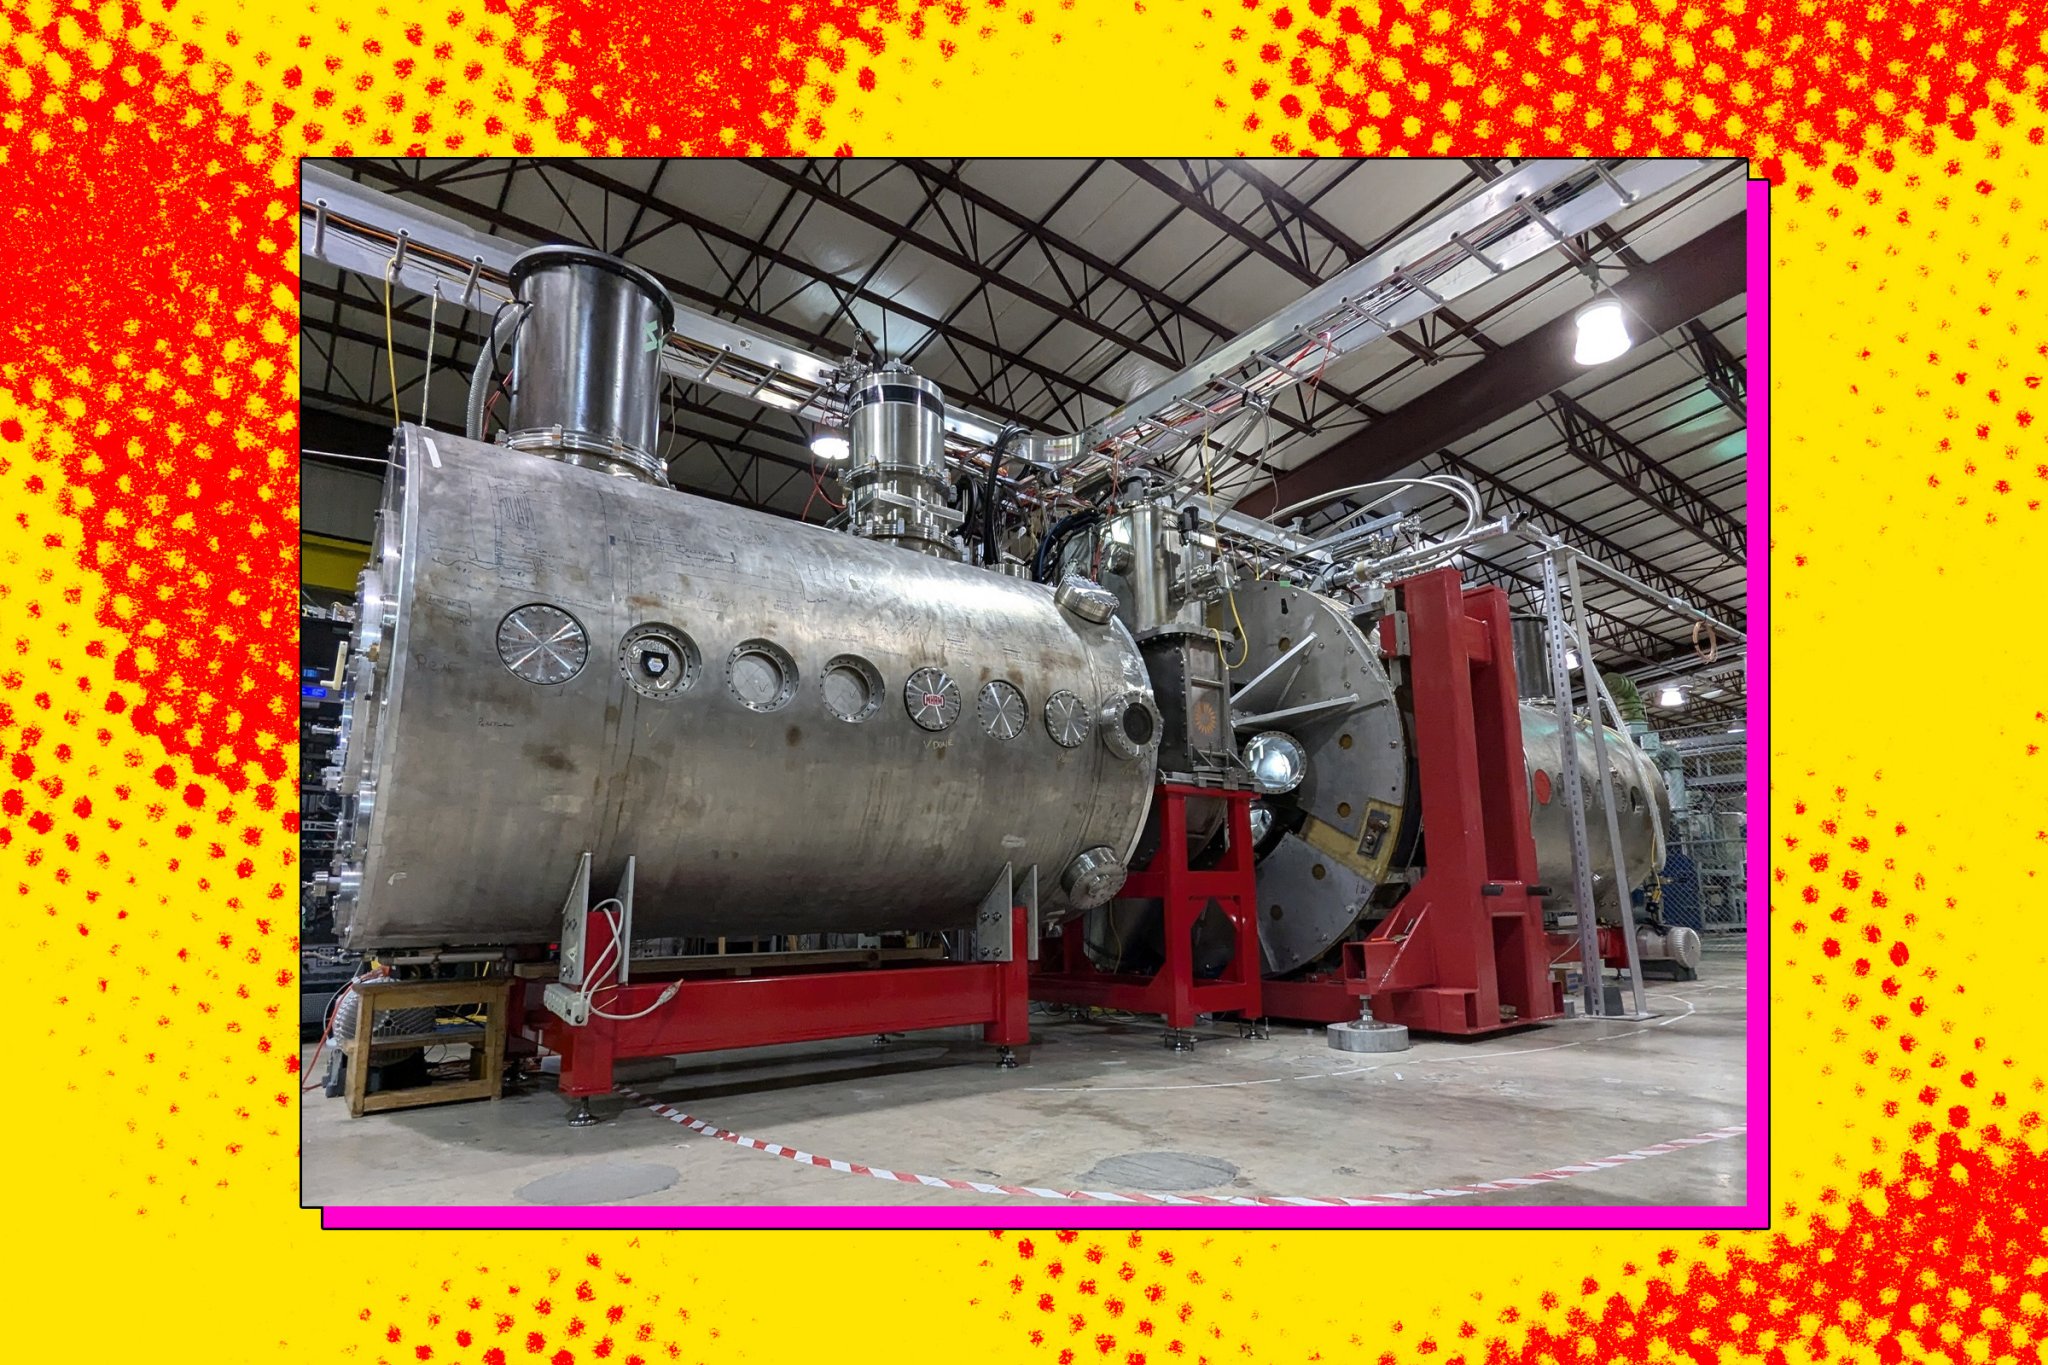
Decrepit Oscar Mayer Hot Dog Factory Is Getting a Major Fusion Reactor Facelift

Unsure what to do with your rancid old hot dog factory? Apparently, the answer is simple: turn it into a fusion reactor facility.

As TechCrunch reports, a company called Realta Fusion is building a fusion reactor inside an old Oscar Mayer hot dog factory in Wisconsin. The refurbished facility is called Forge, and according to Realta cofounder and CEO Kieran Furlong, it’s due to begin operations by 2029 to test whether fusion reactors can actually make a profit by generating more electricity than they require.

“From sausages to fusion,” Furlong told TechCrunch, touting Realta as Wisconsin’s nuclear “state champion.”

The company chose the site because of its “ample” access to power and its proximity to the startup’s existing headquarters.

Per TechCrunch, Realta recently demonstrated that it could generate electricity using a fusion device dubbed Wisconsin HTS Axisymmetric Mirror, or WHAM for short, a successful experiment that the startup claimed as the first of its kind.

Put simply, nuclear reactors replicate the process our Sun uses to generate energy by fusing atoms together under extreme conditions. Realta’s WHAM uses a novel process called direct energy conversion (DEC), which extracts electricity from charged particles emitted by plasma. That sets it aside from other fusion reactor designs that capture heat to spin turbines and generate electricity.

Despite early promising results — scientists only recently started showing that fusion reactors can indeed generate a surplus of energy — we’re still far from proving that it’s a scalable and renewable source of electricity.

But that hasn’t stopped a flourishing cottage industry of fusion startups from trying. With backing from some of the most influential names in tech, from OpenAI’s Sam Altman to Microsoft founder Bill Gates, companies are promising a safer alternative to conventional nuclear fission reactors that can’t experience catastrophic meltdowns.

Even old hot dog factories are fair game as firms like Realta pursue the idea. Besides, we think that it’s only natural that Realta works on turning some old Oscar Mayer Weinermobiles into fusion-powered cars.

More on nuclear fusion: There’s a Glaring Safety Problem With Nuclear Energy Startups

The post Decrepit Oscar Mayer Hot Dog Factory Is Getting a Major Fusion Reactor Facelift appeared first on Futurism.

  •  

Meta Patents Technology to Detect Your Mood by Constantly Analyzing Your Tone of Voice

Meta patented AI tech that constantly analyzes your voice and surroundings in order to detect your emotional state. Finally, exactly what we were all asking for: Meta being granted constant access to our offline lives.

As first caught by Patentlyze, a patent published on July 2 describes a system that records all the user’s “audible communications” and combines it with “contextual factors” like “time of day, location, user activity, or digital interaction.” Audio may be “transcribed, and an emotional-state machine learning model may interpret verbal and nonverbal cues to determine emotional indicators.”

In other words, the system listens to you and everything you do, combines it with other data, and feeds it all to a mood-predicting AI.

“The system increases the precision and reliability of emotional inference by aligning multimodal sensor inputs on synchronized timelines, which creates a novel data structure that supports richer emotional analysis,” reads the patent. “These combined features deliver a technical improvement in automated audio interpretation, enabling continuous emotional monitoring on everyday devices.”

According to the patent, the goal of this extraordinarily intrusive system would be to better tailor users’ workouts to their emotional state, as “personal trainers cannot provide the level of precision in guidance, such as correcting a pose and/or body movement,” as well as Meta’s imagined device could.

It’s not surprising to see Meta pitch this kind of surveillance technology as a fitness device. Health-tracking wearables have become wildly popular, despite the extraordinary amount of physical data about individual consumers they collect and store.

The key difference in Meta’s case, is that rather than crunch biological metrics, it’s an AI-powered fly-on-the-wall attempting to measure a person’s emotional state by listening in on the world around them, and possibly then connecting that information to all other available data.

“The AI assistant may listen to a user(s) at predefined times to hear various types of communication, such as sighs, laughter, and/or the tone(s) of a voice(s),” reads the patent. “The AI assistant may use these inputs to quantify the user’s emotional state or generate other insights about the user.”

The patent also discusses connecting audio inputs to information like when a user takes their medicine, proposing that “the AI assistant may take multiple inputs in addition to audio inputs (e.g., of a user’s voice) to provide a summary of emotional trends based on various inputs (e.g., a happier emotional state associated with a particular time of day or at a time when medication is taken, etc.)”

It’s worth noting that fellow tech giant Amazon tried and failed to market a similar system. In 2020, the company launched the Halo Band, a fitness band with a built-in microphone that was designed to listen in on users and conduct what Amazon described as a “tone of voice analysis.” Following public backlash in 2021, Amazon nuked the microphones when it launched a next-generation version of the band. It discontinued the product line altogether in 2023.

Whether we’ll ever see Meta attempt to launch a similar mood-tracking device is unclear. In a statement to 404 Media, a Meta spokesperson said that “like other companies, patents at Meta are often filed to disclose concepts that may or may not be implemented, and a granted patent does not guarantee that Meta has pursued or will pursue the technology described.”

The existence of the patent, though, shows that such a device is certainly on Meta’s mind — and is yet another Meta-made product that stands to strengthen the bridge between our online and offline worlds.

More on Meta products: The Backlash Is So Strong That People With “Pervert Glasses” Are Afraid to Use Them in Public

The post Meta Patents Technology to Detect Your Mood by Constantly Analyzing Your Tone of Voice appeared first on Futurism.

  •  

Hackers Expose How AI Music App Suno Stole Decades Worth of Copyrighted Music

A hack revealed in detail how AI music generating app Suno scraped millions of songs, likely including copyrighted ones, from across the web to feed into its AI model, 404 Media reports.

Suno, which is currently embroiled in multiple ongoing copyright lawsuits, has already admitted in response to legal action that it used “essentially all music files of reasonable quality that are accessible on the open internet” to train its music-generating AI.

According to 404, the hack shed light on how that copyrighted music was obtained and funneled into datasets, with Suno pulling music and lyrics from sites including YouTube Music, Genius, and Deezer, in addition to stock music libraries like Jamendo, Freesound, Pond5, and the International Music Score Library Project (IMSLP).

Source code obtained by the hacker also pointed to the staggering scale at which Suno has swallowed up music from across the web. For instance, one file, titled “youtube_music,” contained “2,013,545 music clips,” while another file noted that Suno’s AI datasets held “113,879 hours of youtube_music.” Altogether, the file appears to host hundreds of thousands of hours of music.

The hacker, who goes by the pseudonym ellie.191, also claimed to 404 that they’d also been able to view sensitive Suno user data, including Stripe payment information.

In a statement, Suno told 404 that “as we have stated in public filings and disclosures, Suno’s AI models have been trained on publicly available music files and related metadata accessible on third-party websites on the open Internet.”

The company also insisted that its “goal has always been to help people create original new music, not replicate someone else’s.” That’s despite tests extensively showing how Suno can easily replicate published music, including the work of well-known artists.

More on Suno: CEO of Song-Generating AI App Says People “Don’t Enjoy” Making Music With Instruments

The post Hackers Expose How AI Music App Suno Stole Decades Worth of Copyrighted Music appeared first on Futurism.

  •  

Elon Musk’s xAI, Which is Being Sued Over AI-Generated Sexual Deepfakes, Sues Grok User Over AI-Generated Sexual Deepfakes

Elon Musk’s xAI is suing a man for using its flagship chatbot, Grok, to create nonconsensual sexual deepfakes of women and children.

The Grok user, a 67-year-old in South Carolina named Terry Wayne Harwood, was arrested in March on multiple counts of sexual exploitation of a minor. According to the allegations, Harwood possessed and distributed child sexual abuse material, or CSAM. Filed earlier this week in Texas, xAI’s lawsuit accuses Harwood of using Grok to do just that, per Reuters. He apparently used two different Grok accounts, according to the lawsuit, and though xAI claims that Grok refused some of Harwood’s requests, he was able to tailor prompts to sidestep Grok’s safety guardrails and create the disturbing imagery.

The lawsuit follows a massive deepfake scandal that unfolded over the winter, as X users realized that Grok — which had been updated with a new photo and video-editing feature — could be used to quickly and easily alter images to artificially undress real people and depict them in sexual positions.

As Futurism reported, some of these images depicted real women in sexually violent and degrading scenarios. Some of the nonconsensual deepfakes depicted minors. The Center for Countering Digital Hate estimated that during an 11-day period, Grok “generated an estimated 3 million sexualized images, including 23,000 of children.”

Now, as it sues one of its users for the creation of illegal content, xAI is fighting multiple lawsuits over Grok-generated CSAM. In March, teenagers in Tennessee sued the company in a proposed class action, alleging that Grok had been used to create deepfakes of them and more than a dozen other minors. Just last week, the suit was amended to include allegations that a man used Grok to generate more than 7,000 sexual deepfakes of his stepdaughter. The amended complaint alleges that the man’s prompts largely went unflagged by Grok’s guardrails.

In another high-profile case, the former conservative influencer (and mother to one of Musk’s many children) Ashley St. Clair sued xAI after she was aggressively targeted by sexualized deepfakes, including one depicting her as a minor.

Law enforcement professionals and child online safety experts say that AI has led to an overwhelming and disorienting new flood of CSAM, as Bloomberg detailed in a devastating report earlier this year. It’s also created a host of new challenges for those attempting to find and arrest child predators, as AI has made it more difficult for investigators to determine whether a child depicted in abuse material is real or AI-generated.

In its latest lawsuit, xAI accuses Harwood of engaging in a “calculated scheme to weaponize Plaintiff’s ⁠tool ​for criminal ends, exposing real victims to profound ​and lasting harm, while exposing Plaintiff to significant legal risk and reputational damage.”

xAI — which is now owned by SpaceX and has since been renamed to SpaceXAI — also alleges that it “enforces its rules ​against violators through account suspensions, account terminations, and by reporting suspected child sexual abuse ‌material ⁠to the National Center for Missing and Exploited Children,” or NCMEC. It also claims that xAI “has suspended 52,222 accounts and made 73,604 reports to NCMEC in 2026, resulting in (at least) 244 arrests.”

But despite its best efforts, it’s clear that the startup still has a serious deepfake problem. If a user is engaging in deeply disturbing criminal activity using a company’s service, it’s reasonable for a company to hold them to account. But suing users doesn’t fix a chatbot’s failing guardrails, facilitating their crimes.

More on Grok and deepfakes: Grok Linked to Sickening Crime in Lawsuit That Puts SpaceX in Crosshairs

The post Elon Musk’s xAI, Which is Being Sued Over AI-Generated Sexual Deepfakes, Sues Grok User Over AI-Generated Sexual Deepfakes appeared first on Futurism.

  •  

Terrified Tech Execs Are Traveling With Armed Bodyguards as AI Backlash Grows

Public backlash to AI is intensifying — and transforming into real-world attempts at physical violence. Industry leaders are fearing for their lives.

Leading AI companies and their top executives are beefing up security, the Wall Street Journal reports, as escalating anti-AI industry sentiment is culminating in threats and attempts of violence against the people and ventures building leading AI models. Some executives are even traveling with armed guards, while others have taken to keeping a lower public profile.

“Tech CEOs, a few years ago, definitely did not have security,” Dakota Dominguez, an executive at the Silicon Valley-based security firm JPT Security, told the WSJ. “A lot of tech companies now are incorporating that into their budgets.”

Earlier this year, the AI industry was shaken when a 20-year-old anti-AI activist named Daniel Moreno-Gama, armed with a gun and a Molotov cocktail, unsuccessfully tried to firebomb the home of OpenAI CEO Sam Altman. No one was injured, but the high-profile incident followed a string of violent threats and at least one OpenAI lockdown.

OpenAI isn’t alone. Per the WSJ, around the time that Altman’s home was targeted, OpenAI rival Anthropic faced a close call when a man snuck into its headquarters behind an employee carrying an envelope with an executive’s name on it. The man reportedly then told a guard that the executive was “going to be killed.” The man was stopped before anyone got hurt.

All in all, it’s easy to see why tech leaders are budgeting for beefed up security.

Not all anti-AI sentiment has manifested in attempted physical violence. Activists have also shut down data centers, taken down AI-powered surveillance cameras, and protested outside AI company headquarters. As the fight over AI data centers heats up, some polls have shown that AI is less popular with Americans than Immigration and Customs Enforcement. People fear that AI will result in mass layoffs, a further consolidation of wealth and power, or even a catastrophic apocalypse — outcomes that many leaders in the AI industry have issued warnings about.

“That’s why people are setting warehouses on fire,” a former Pinterest employee named Bonnie Kate Wolf, who was laid off during an AI-focused restructuring, told the WSJ. “You can’t go back to serfdom. It really feels like the people in power want to be kings. Historically, that doesn’t work out for kings.”

More on AI tensions: AI Billionaires Are Starting to Get Scared

The post Terrified Tech Execs Are Traveling With Armed Bodyguards as AI Backlash Grows appeared first on Futurism.

  •  
❌