❌

Reading view

I fixed a tractor using John Deere’s self-repair service. Farmers aren’t sold on it.

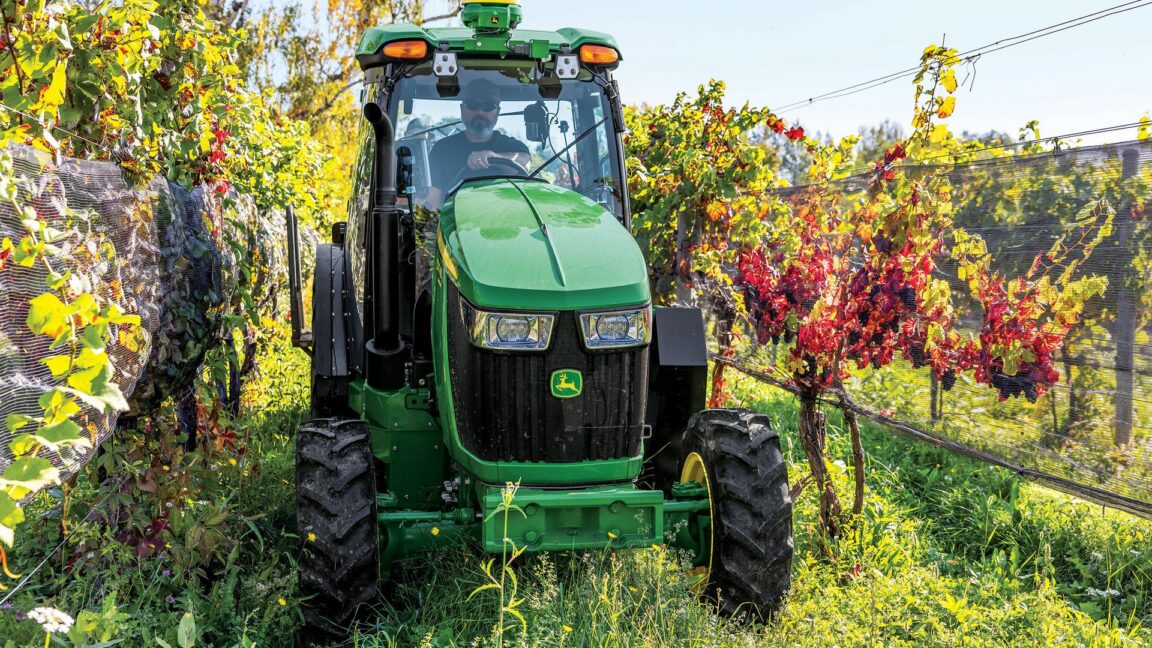
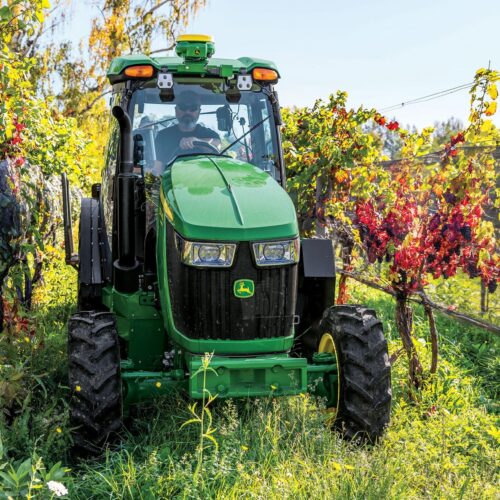
There is something wrong with the tractor. The water-in-fuel sensor, a small device embedded in the John Deere machine that monitors the integrity of its diesel engine, is disconnected. And I’ve got to fix it.

I’m not a mechanic or a farmer. I’m poking at a laptop at John Deere’s corporate office in Santa Clara, California. There’s a cable connecting the computer to a 5130ML tractor sitting on the grass nearby. A bright red notification sits on the screen, telling me something is wrong. I type in a question and the software pulls up instructions and a few images from the user manual that matches the serial number of the machine.
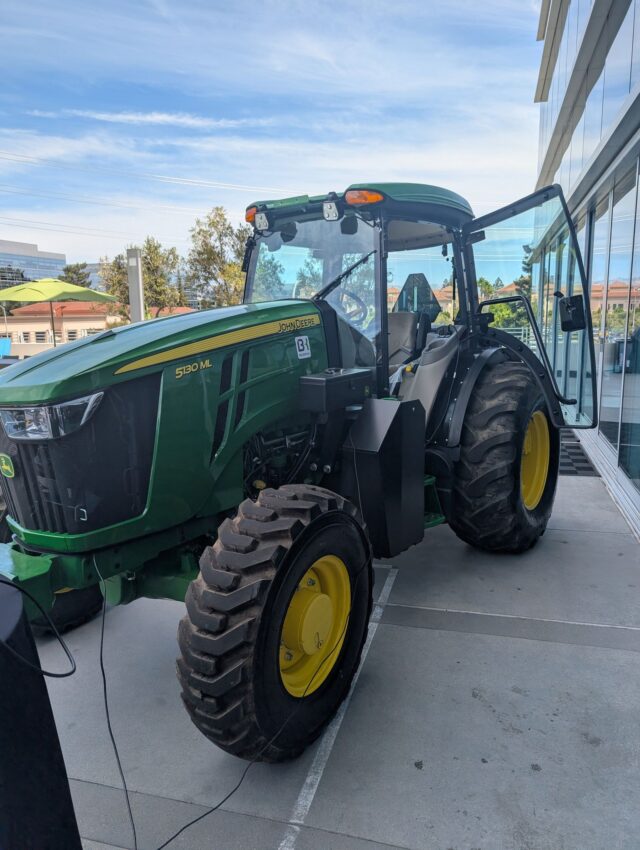
Credit: Boone Ashworth
Read full article

Comments

© John Deere

  •  

The Army just used a 20-kilowatt laser to take out three drones

This week, the US Army used a high-energy multipurpose laser to shoot down three drones near the US-Mexico border, which official reports claimed were “posing a physical threat to US military personnel and CBP partners,” referring to Customs and Border Patrol.

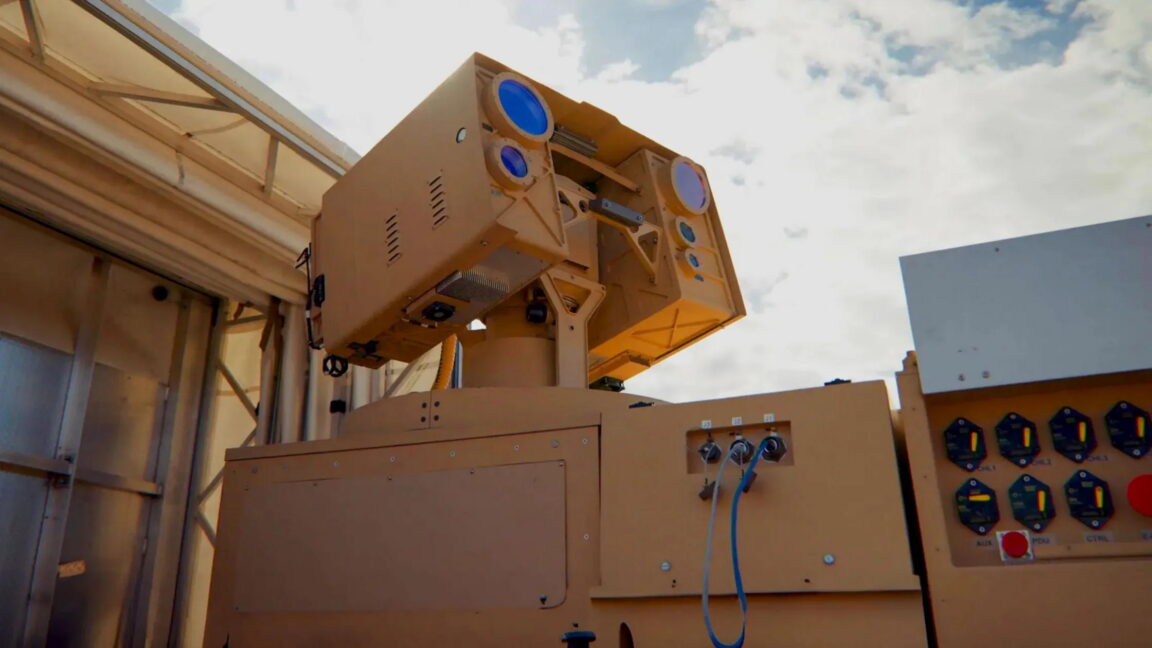
The operation took place between the night of August 25 and the early morning of August 26 in the vicinity of the Rio Grande Valley in Texas and was led by the Joint Task Force Southern Border (JTF-SB), which operates under US Northern Command. Authorities confirmed that, during the operation, agents used technology derived from the Army’s High-Energy Multipurpose Laser (AMP-HEL) system, a military program focused on implementing high-energy lasers for new defense capabilities.

Available information suggests that this initiative began in September 2025, when AeroVironment, a company specializing in defense technology, delivered the first two functional prototypes of these laser-based weapons to the US Armed Forces. Two new, improved systems were delivered as the program was expanded in December of the same year. According to the manufacturer, this particular platform, called the Locust Laser Weapon System, is designed to be mounted on military vehicles, as the Army has done with the versions it has received.

Read full article

Comments

© Aerovironment

  •  

Inside Meta’s push to put robots to work in data centers

Meta is testing robots that can plug in cables, reset servers, and handle other tasks inside its data centers, according to several current and former workers familiar with the projects. The ongoing effort, which has not been previously reported, may eventually allow Meta to operate its rapidly expanding data center footprint with fewer humans, keeping labor costs in check as its spending on AI infrastructure soars.

Meta is using robots and related hardware from several different vendors, including Watney Robotics, Kinova, and ABB, according to the same workers, who asked to remain anonymous because they weren’t authorized to speak to the media. Kinova and ABB declined to comment. Watney didn’t respond to requests for comment.

In one experiment, Meta is evaluating whether a Kinova Gen3 robotic arm could be used for power cycling or cutting off electricity to servers. The company is also testing a different robot to swap networking cables. One Meta data center worker estimates that if it’s successful, the bot could replace up to 80 percent of some people’s workloads. “We thought those of us performing the physical tasks were safe for a while, but not anymore,” says the worker. “It’s coming for us all, unfortunately.”

Read full article

Comments

© Getty Images

  •  

Reverse-lookup service exposed millions of photos of people’s faces

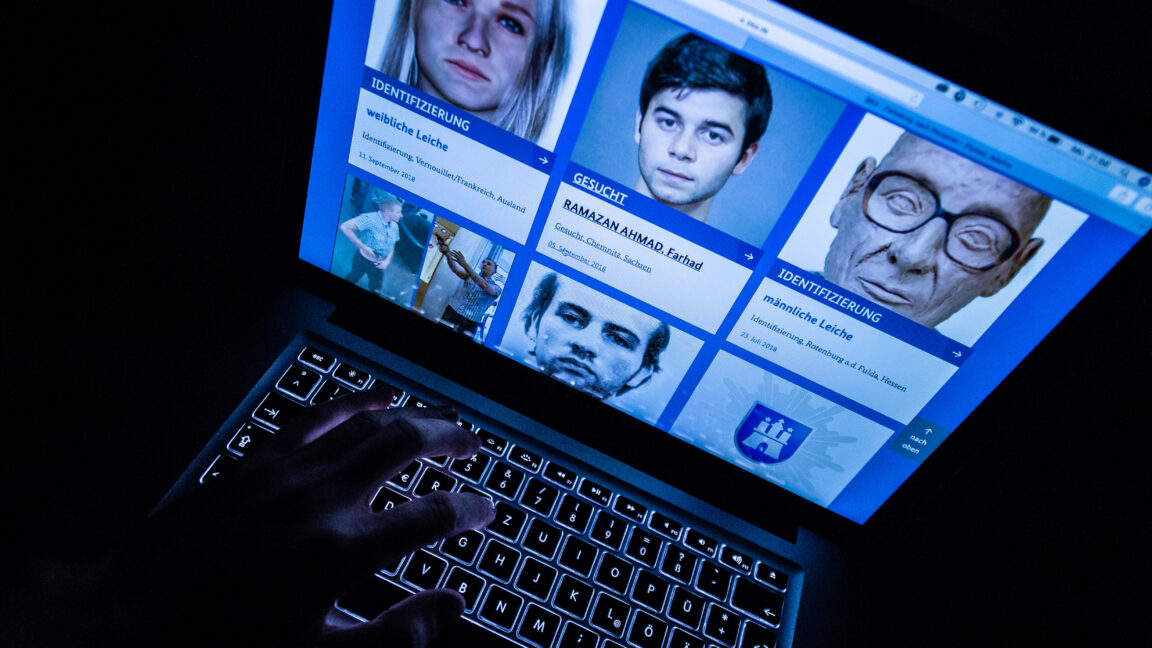
When someone uploads a photo to the people-search tool ClarityCheck, the website has a clear message: “Your reverse image search is private and secure.” New research, though, shows that the website left more than 9 million image files, including photographs of people’s faces, publicly exposed. And a second misconfiguration publicly exposed people’s email addresses and phone numbers.

Overall, according to findings from independent security researcher Jeremiah Fowler, the exposed ClarityCheck database contained roughly 450 GB of images, including what appeared to be profile images, screenshots, and other photographs of adults, teenagers, and children. All of the images were stored in an unsecured Amazon S3 bucket, with files in folders named “faces” and “profiles,” which could be accessed by anyone online through a URL included in the company’s publicly available website code.

ClarityCheck is one of a number of so-called people-finder tools that have appeared online in recent years. These websites broadly claim to be able to search the web, public records, and other databases to identify individuals. ClarityCheck’s website says it can run searches on phone numbers, email addresses, vehicle identification numbers, and names. Its photo-search page says it can help “identify anyone in a photo” and find social media profiles “in seconds.”

Read full article

Comments

© picture alliance / Contributor

  •  

"Dangerous" AI models are coming no matter what

Late last week, Anthropic took its new Claude Fable 5 and Mythos 5 AI models offline following a United States government export-control directive barring “any foreign national” from using the services. The company has been in talks with the White House since Friday but has yet to secure an agreement that would allow it to reinstate the offerings.

Since Mythos debuted in April, Anthropic has claimed—and warned—that the model has advanced capabilities for not only finding software vulnerabilities to help defenders patch them, but also figuring out ways to exploit them that could be used by bad actors. Anthropic itself noted this double-edged sword in its launch of Mythos 5 and Claude Fable 5. “A great deal of advanced usage of AI models is dual use: the same queries that are beneficial in the hands of cybersecurity professionals and biology researchers could be dangerous if available to malicious actors,” the company wrote in a blog post last week.

With this in mind, the company initially released a version called Mythos Preview to a select consortium as part of a working group known as Project Glasswing. Mythos 5 was also privately released to this group last week, while Claude Fable 5, which is a Mythos-grade model, was released to the general public with specific blocks on its ability to give responses to questions about biology and cybersecurity.

Read full article

Comments

© Samuel Axon

  •  

Cameras, sensors, and 3D body scans: All the tech helping eliminate blown calls

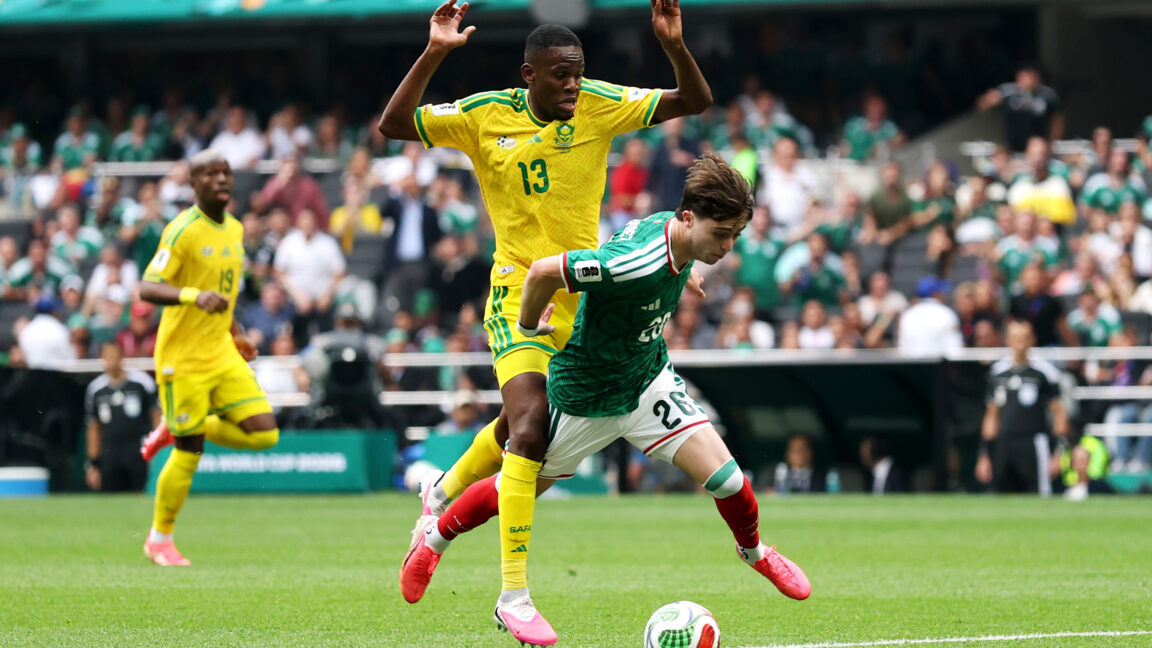
At the 2026 World Cup, the refs on the field and the officials on the sidelines will be able to use an abundance of tech to help call penalties, spot offside violations, and make other consequential decisions.

The video assistant referee system, known as VAR, and the semi-automated offside technology (SAOT) have been used in soccer for years. But the setup at this summer's World Cup represents some of the most advanced uses of adjudication tech to date—not just in soccer, but across all high-level sports.

During each match, the pitch will be awash in sensors, cameras, and new computer vision software. One especially notable advancement this year is the use of digital twins. Every player in the World Cup has had their body scanned by a computer. The digital twin of any athlete—which precisely matches their height, limb length, and shoe size—can be dropped into a virtual simulation of the game to determine their exact position relative to the ball, boundary lines, and other players. Officials can use all of this data to help spot infractions, determine penalties, and smooth out the edges of the beautiful game.

Read full article

Comments

© Luke Hales/Getty Images

  •  

One day after discovery, Meta pulls facial recognition code from its smart glasses

One day after WIRED revealed that Meta had quietly embedded an unreleased face-recognition system into an app installed on more than 50 million phones, the company removed it, according to a WIRED analysis of the latest version’s code.

The most recent version of Meta AI, a companion app for its line of smart glasses, strips out the unactivated software components that powered the system Meta internally called NameTag. The version published the day of WIRED’s report included several code libraries explicitly named for face recognition. Friday’s release includes none of them.

Andy Stone, Meta's vice president of communications, told WIRED on Monday that the feature is purely exploratory, adding: “No final decision has been made on what to do here, if anything.”

Read full article

Comments

© David Paul Morris/Bloomberg/Getty

  •  

A hacker group is poisoning open source code at an unprecedented scale

A so-called software supply chain attack, in which hackers corrupt a legitimate piece of software to hide their own malicious code, was once a relatively rare event but one that haunted the cybersecurity world with its insidious threat of turning any innocent application into a dangerous foothold in a victim’s network. Now one group of cybercriminals has turned that occasional nightmare into a near-weekly episode, corrupting hundreds of open source tools, extorting victims for profit, and sowing a new level of distrust in an entire ecosystem used to create the world’s software.

On Tuesday night, open source code platform GitHub announced that it had been breached by hackers in one such software supply chain attack: A GitHub developer had installed a “poisoned” extension for VSCode, a plug-in for a commonly used code editor that, like GitHub itself, is owned by Microsoft. As a result, the hackers behind the breach, an increasingly notorious group called TeamPCP, claim to have accessed around 4,000 of GitHub’s code repositories. GitHub’s statement confirmed that it had found at least 3,800 compromised repositories while noting that, based on its findings so far, they all contained GitHub’s own code, not that of customers.

“We are here today to advertise GitHub’s source code and internal orgs for sale,” TeamPCP wrote on BreachForums, a forum and marketplace for cybercriminals. “Everything for the main platform is there and I very am happy to send samples to interested buyers to verify absolute authenticity.”

Read full article

Comments

© NiseriN via Getty Images

  •  
❌